
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
100 results
CVE-2022-29072 preview

CVE-2022-29072

GitHubsentinelblue/cve-2022-29072

** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…

exploitationincident-responselog-analysis+3
8
4 years ago
amcache-evilhunter preview

amcache-evilhunter

GitHubcristianzsh/amcache-evilhunter

Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.

digital-forensicsforensicsincident-response+2
1147 days ago
zeek-quasarrat-detector preview

zeek-quasarrat-detector

GitHubcorelight/zeek-quasarrat-detector

Zeek detector for QuasarRat

anomaly-detectionintrusion-detectionmalware-analysis+2
31 year ago
trufflehog preview

trufflehog

GitHubtrufflesecurity/trufflehog

Find, verify, and analyze leaked credentials
cloud-securitycode-analysisdevsecops+6
28.3k11h 10m ago
sage preview

sage

GitHubgendigitalinc/sage

Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
ai-securitycode-analysisdefensive-tools+6
31019 days ago
CVE-2025-55182-Attack-Analysis preview

CVE-2025-55182-Attack-Analysis

GitHubngvcanh/cve-2025-55182-attack-analysis

Real-world attack analysis of CVE-2025-55182 (React2Shell) - React Server Components RCE vulnerability
educationforensicsincident-response+5
10 months ago
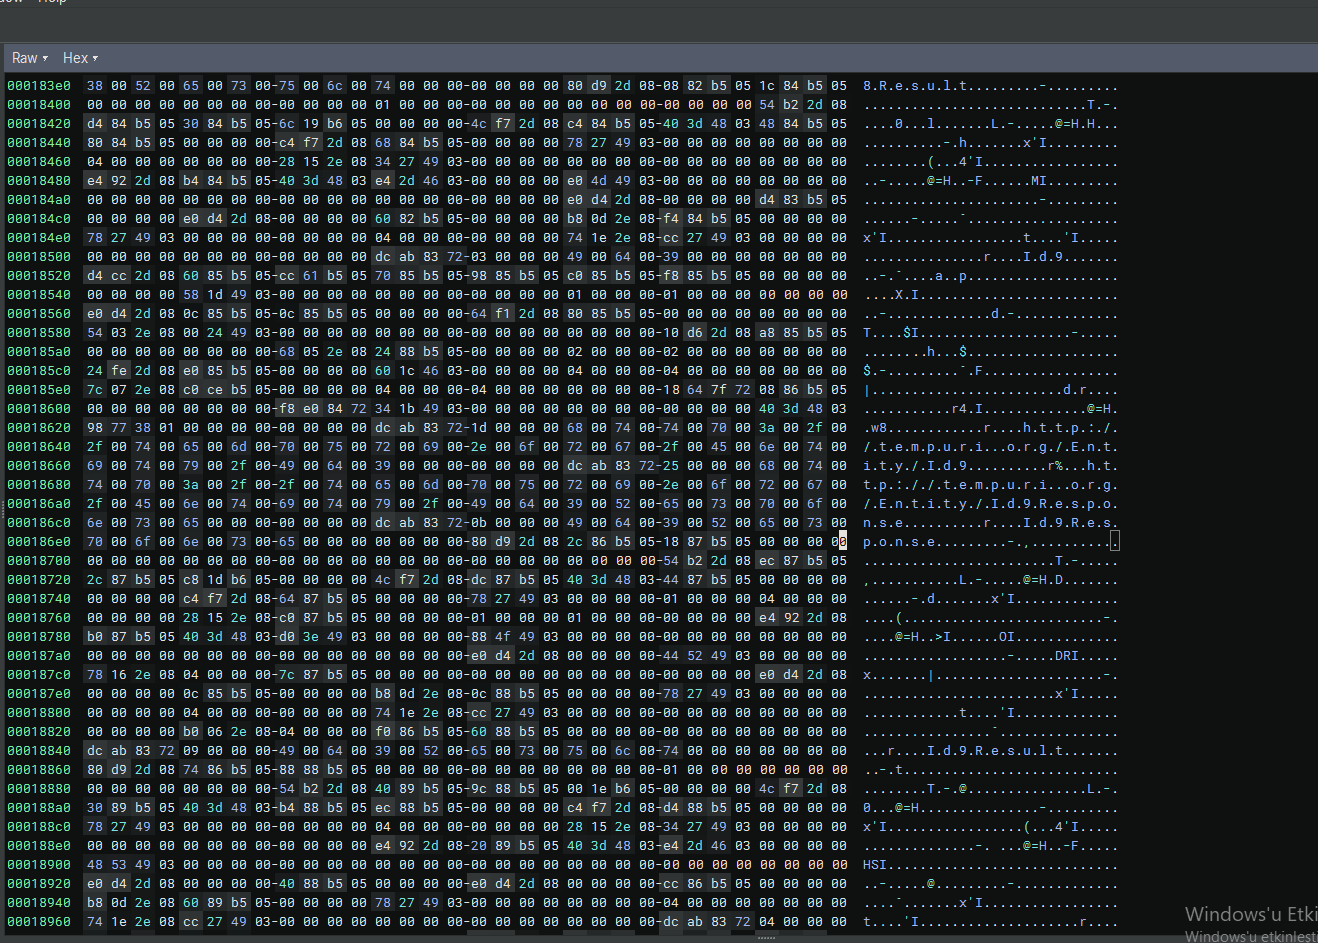
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
command-and-controldata-exfiltrationmalware-analysis+4
11 month ago
RemotePSpy preview

RemotePSpy

GitHubwithsecurelabs/remotepspy

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
defensive-toolsdigital-forensicsincident-response+3
196 years ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
command-and-controlcryptographydigital-forensics+7
1024 days ago
pingback preview

pingback

GitHubcorelight/pingback

A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
command-and-controlintrusion-detectionmalware-analysis+2
121 year ago
SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298 preview

SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298

GitHubabc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
command-and-controleducationemail-security+9
4 months ago
sigma-cli preview

sigma-cli

GitHubsigmahq/sigma-cli

The Sigma command line interface based on pySigma

defensive-toolsintrusion-detectionlog-analysis+2
2161 day ago
RCE-CVE-2017-0199-detection-analysis preview

RCE-CVE-2017-0199-detection-analysis

GitHubahmed-tarek22752/rce-cve-2017-0199-detection-analysis

This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…
command-and-controldigital-forensicseducation+8
21 month ago
Zero-Click-RCE-Incident-Response-CVE-2025-21298 preview

Zero-Click-RCE-Incident-Response-CVE-2025-21298

GitHubtarunbharathe/zero-click-rce-incident-response-cve-2025-21298

Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…

command-and-controldigital-forensicseducation+6
6 months ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

binary-analysiscommand-and-controldefensive-tools+6
1614 days ago
active_c2_ioc_public preview

active_c2_ioc_public

GitHubcarbonblack/active_c2_ioc_public

Active C2 IoCs
command-and-controlioc-managementthreat-intelligence
1003 years ago
PAN-OS-CVE-2024-3400-Command-Injection-Investigation preview

PAN-OS-CVE-2024-3400-Command-Injection-Investigation

GitHubzedocun/pan-os-cve-2024-3400-command-injection-investigation

Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
digital-forensicsincident-responselog-analysis+3
15 months ago
CVE-2026-73570 preview

CVE-2026-73570

GitHub0xblackash/cve-2026-73570

Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…

defensive-toolseducationemail-security+6
15 days ago
Previous123456Next