

ore_react2shell_scanner
 rapticore/ore_react2shell_scanner
CVE-2025-55182 (React2Shell) Scanner
exploitationpenetration-testingreconnaissance+4
2
rapticore/ore_react2shell_scannerCVE-2025-55182 (React2Shell) Scanner

 edu0x01/sr-71
An easy-to-use Python tool for performing subdomain enumeration, endpoint recognition, and more
 cujanovic/subdomain-bruteforce-list
Large wordlist (34M+ entries) for subdomain bruteforcing and DNS reconnaissance during penetration testing and attack surface discovery.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
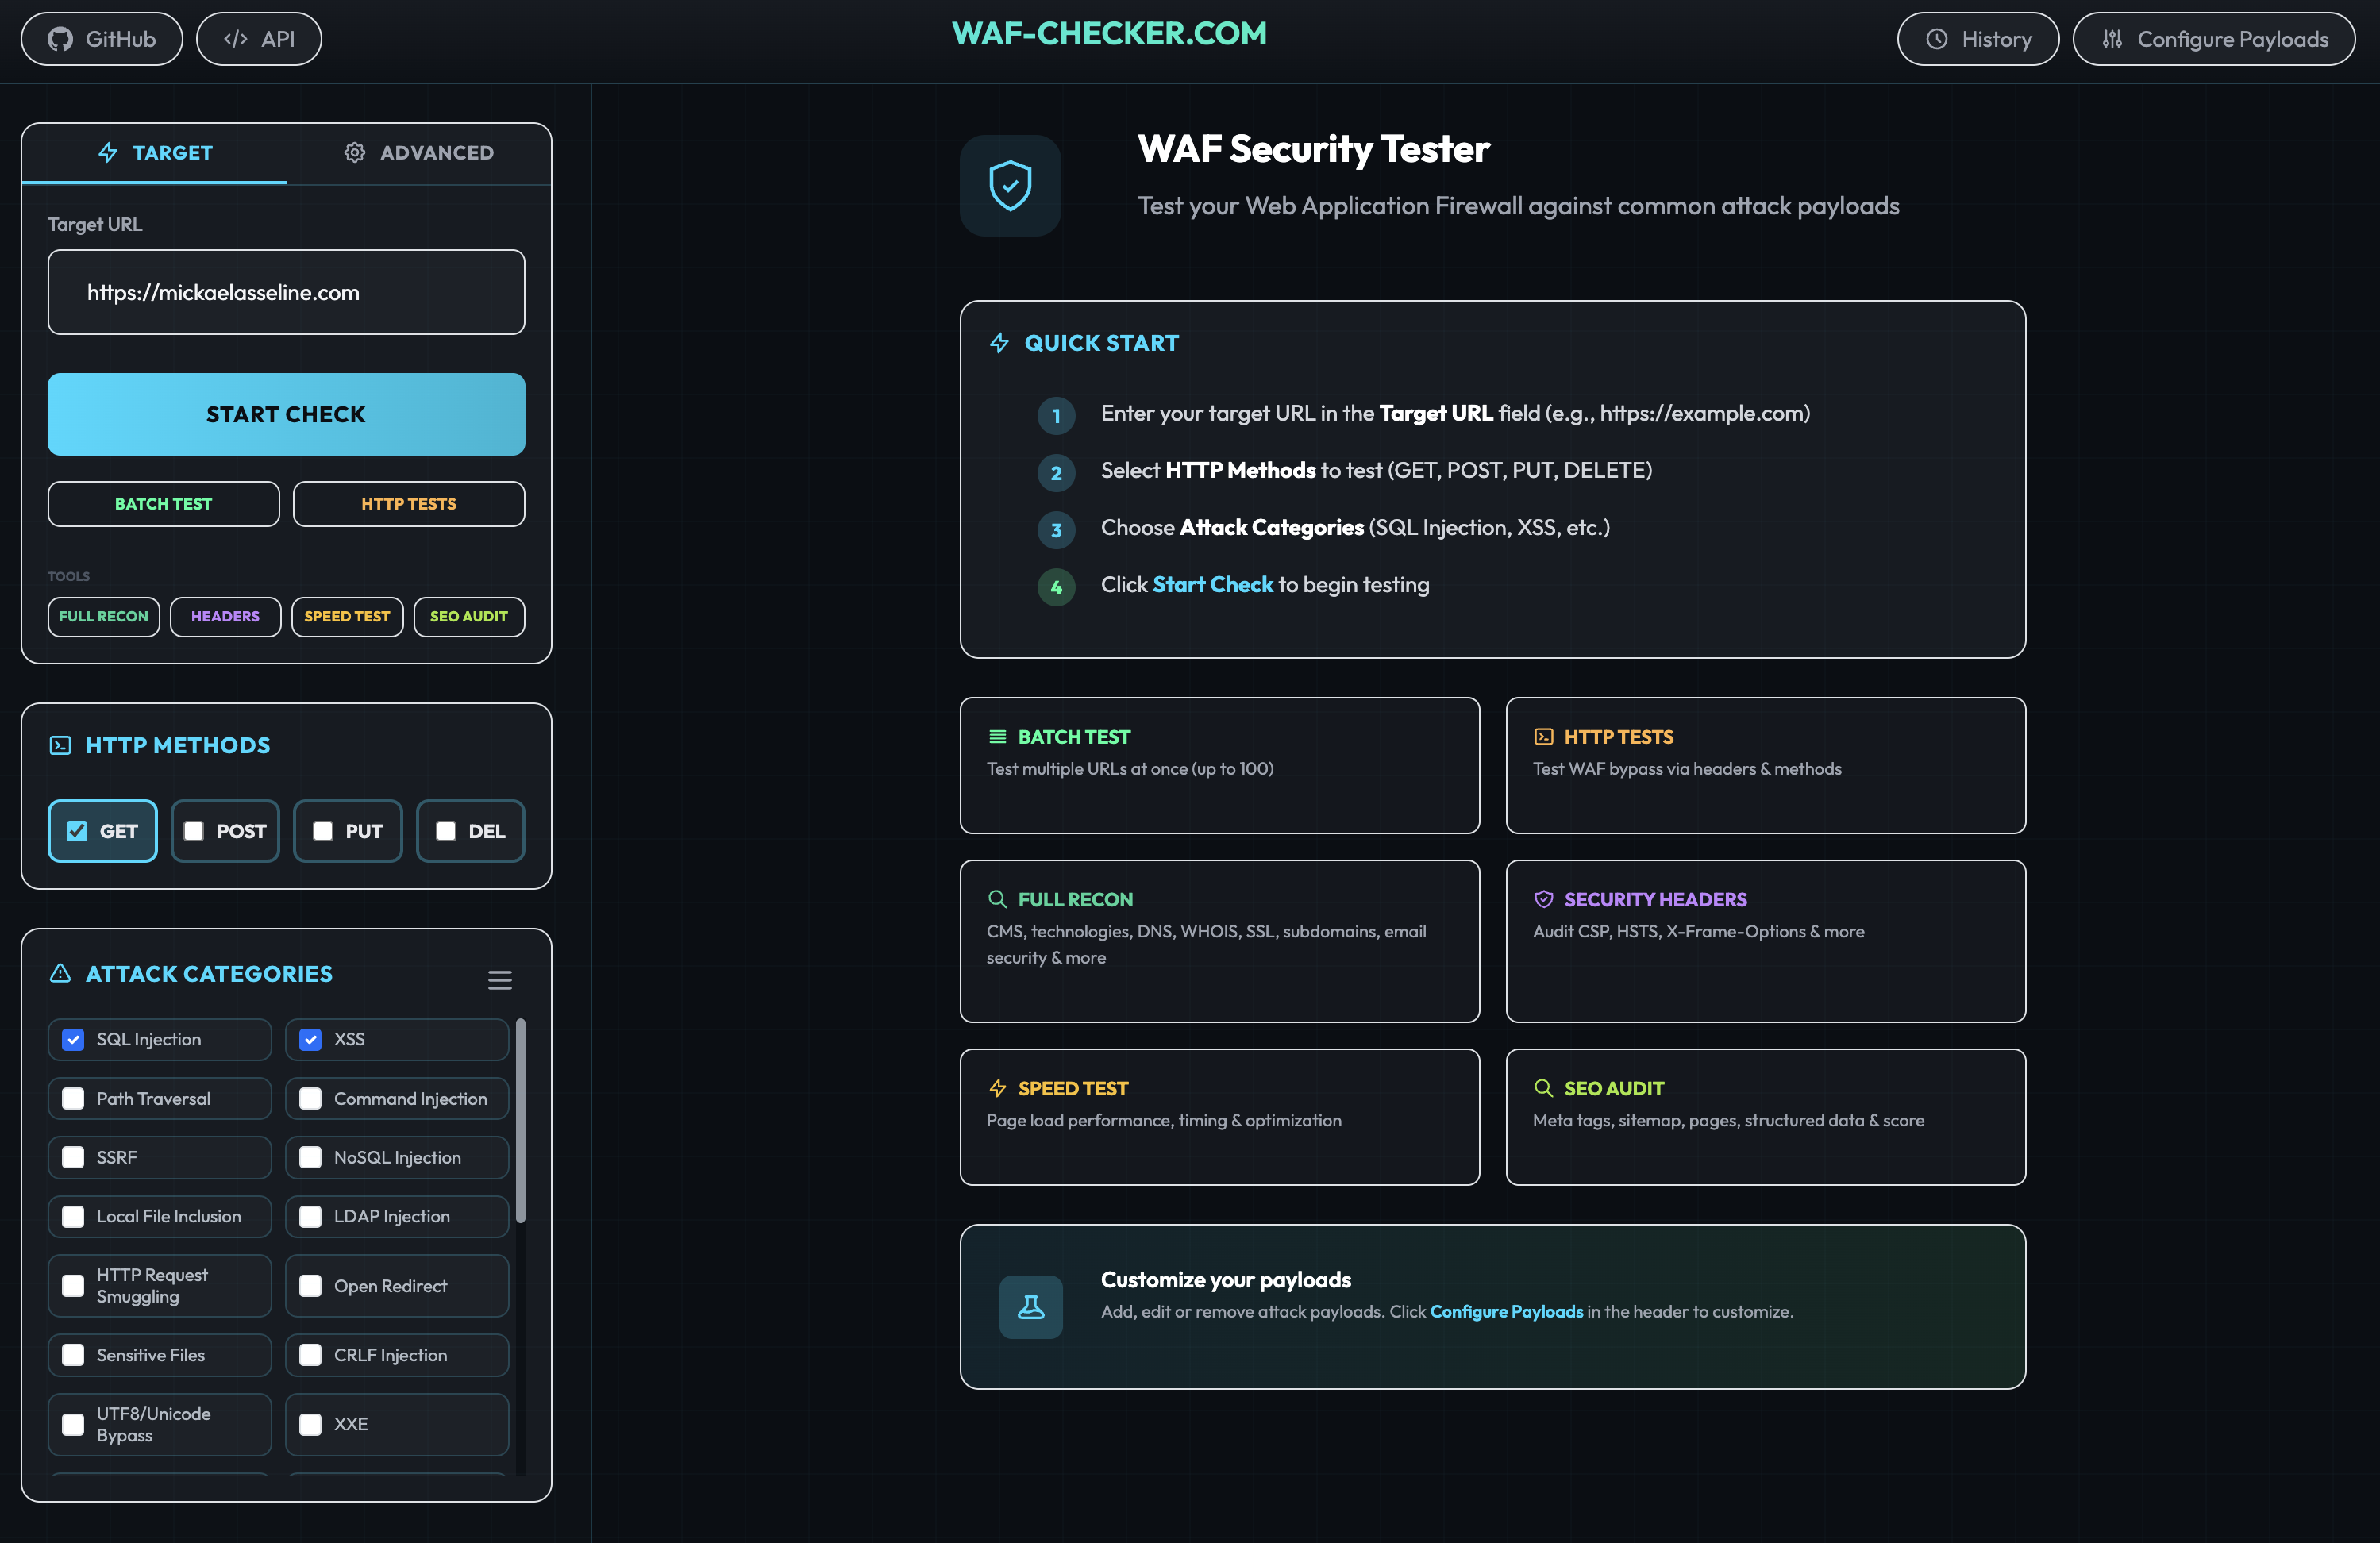 papamica/waf-checker
Tests your WAF with +160 payloads
 fundacio-i2cat/infohound
InfoHound is an OSINT to extract a large amount of data given a web domain name.
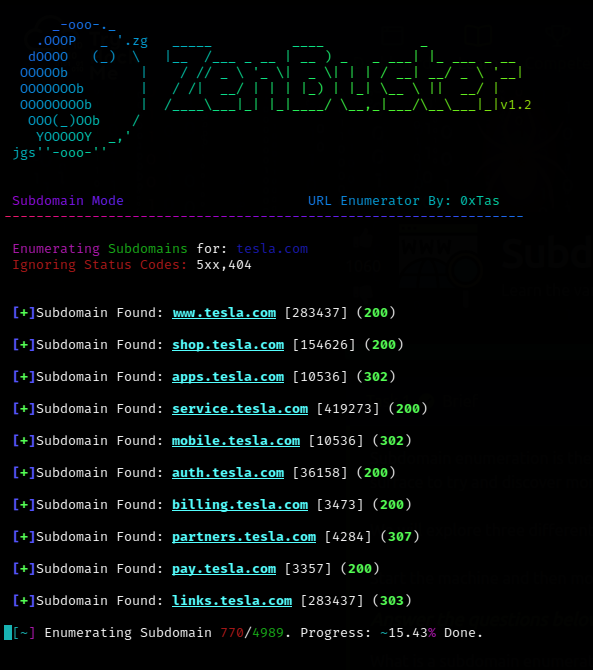 0xtas/zenbuster
Multi-threaded URL enumeration/content-discovery tool in Python.
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
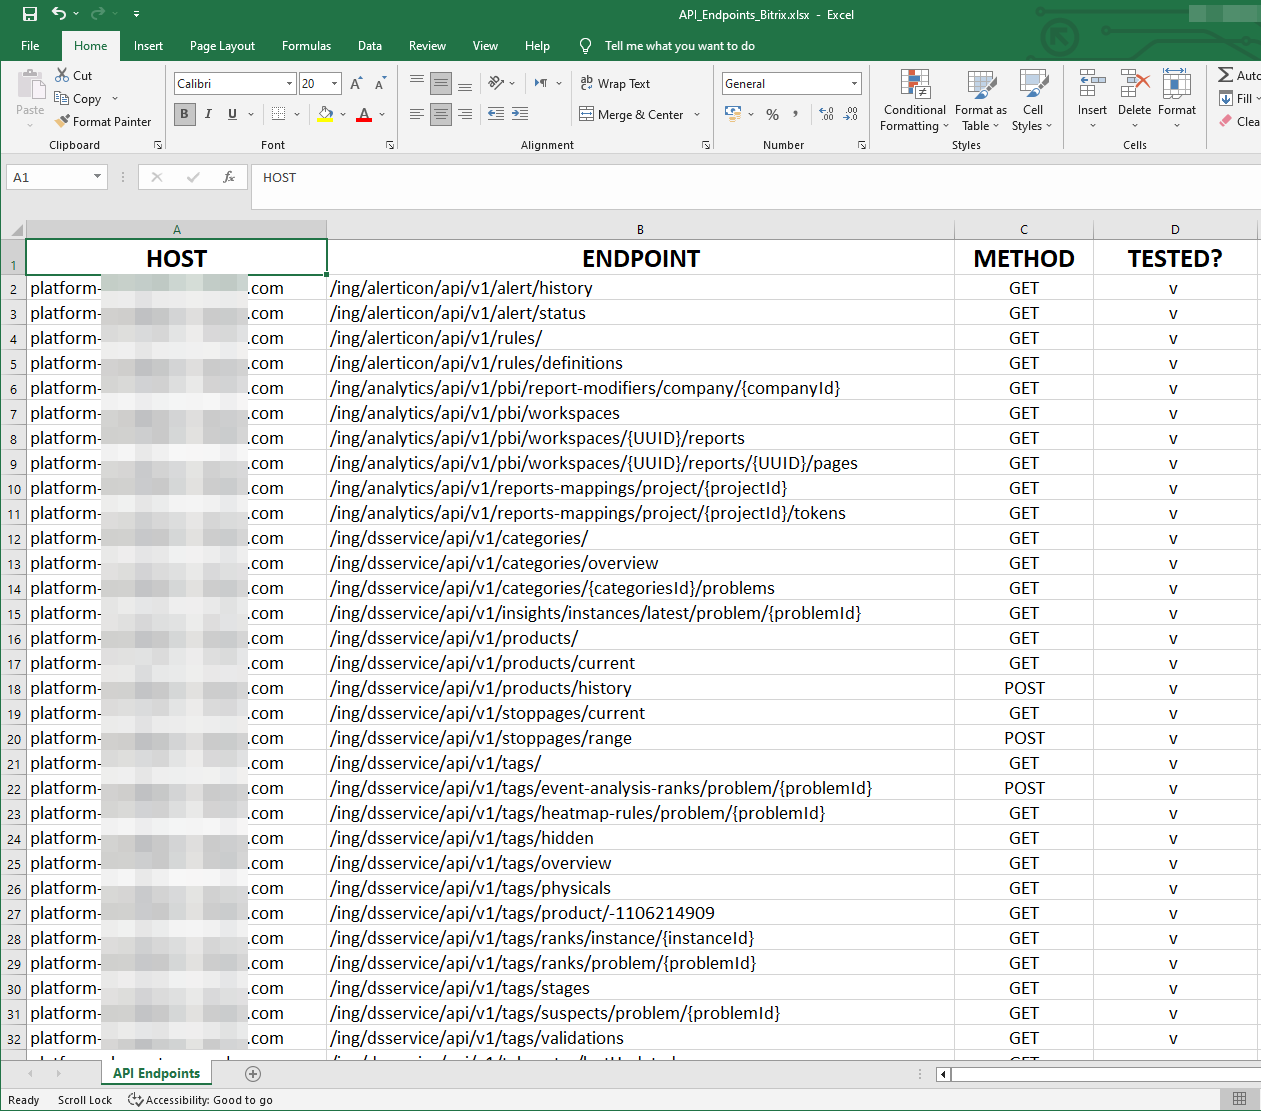 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 security-phoenix-demo/react2shell-scanner-cve-2025-55182
React2shell-web-scanner
 jan0x190/cve-2025-55182-simple-scanner-main
Multi-language scanner for CVE-2025-55182 RCE in Next.js React Server Components, with single/mass scanning modes and integrated bug bounty…