
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
SubMon — Yet another subdomain monitor. | Kitploit
Tools/GitHubGitHub/liuyc26/submon
ReconnaissanceScripting & AutomationInformation GatheringWeb SecuritySubdomain EnumerationDNS Analysis
GitHubliuyc26/submon

SubMon

Yet another subdomain monitor.

View Repository
1418 months agoNot yet reviewed
Share

SubMon

Some say bug bounty isn't just about finding bugs, but being the "first" to find them. I'm building this tool to notify hunters when new subdomains appear.
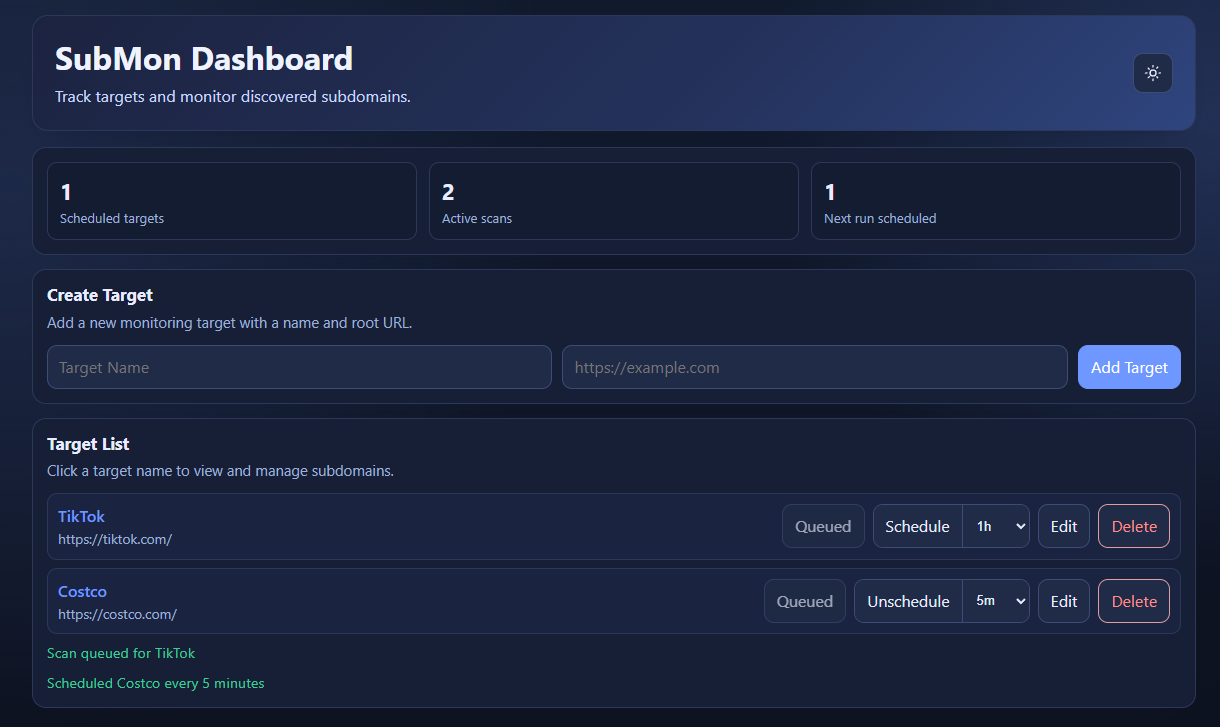
Features

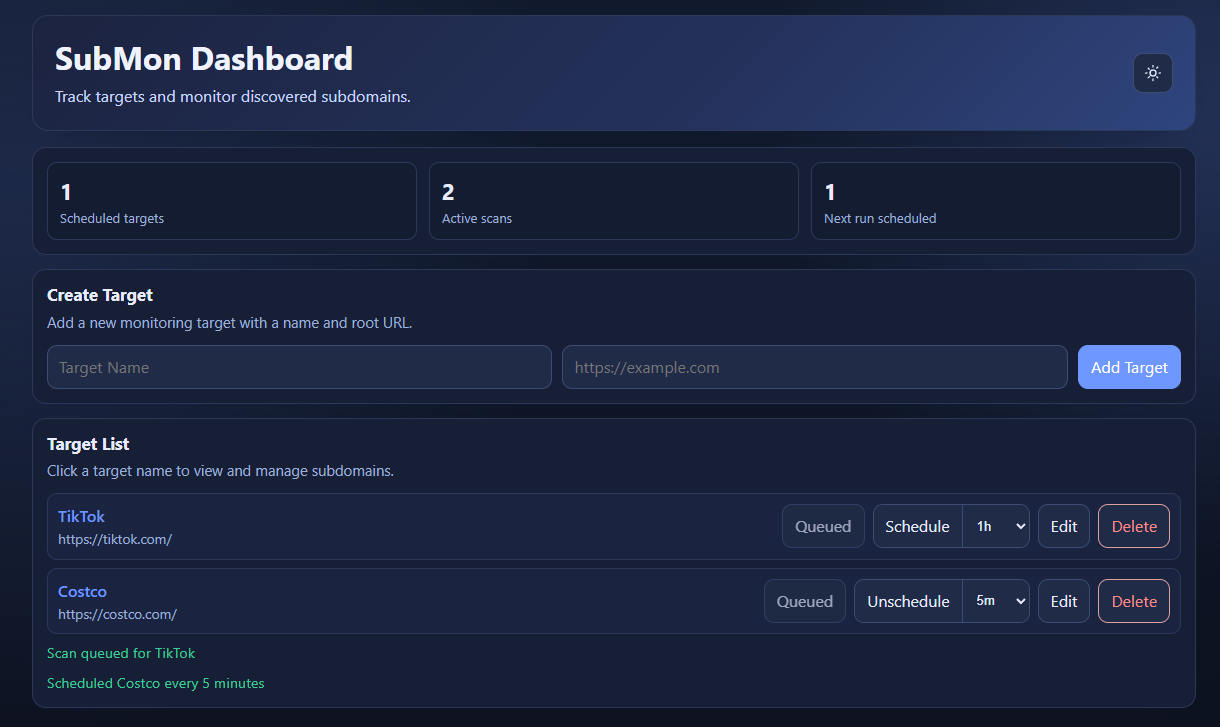
dashboard

  • You can add your favorite target: name + domain.
  • Then you can either click scan or schedule a scan.
  • When the scan finishes, you will get a discord alert.
  • If you set up the scheduler, you will get a discord notification every time it finds new subdomains.

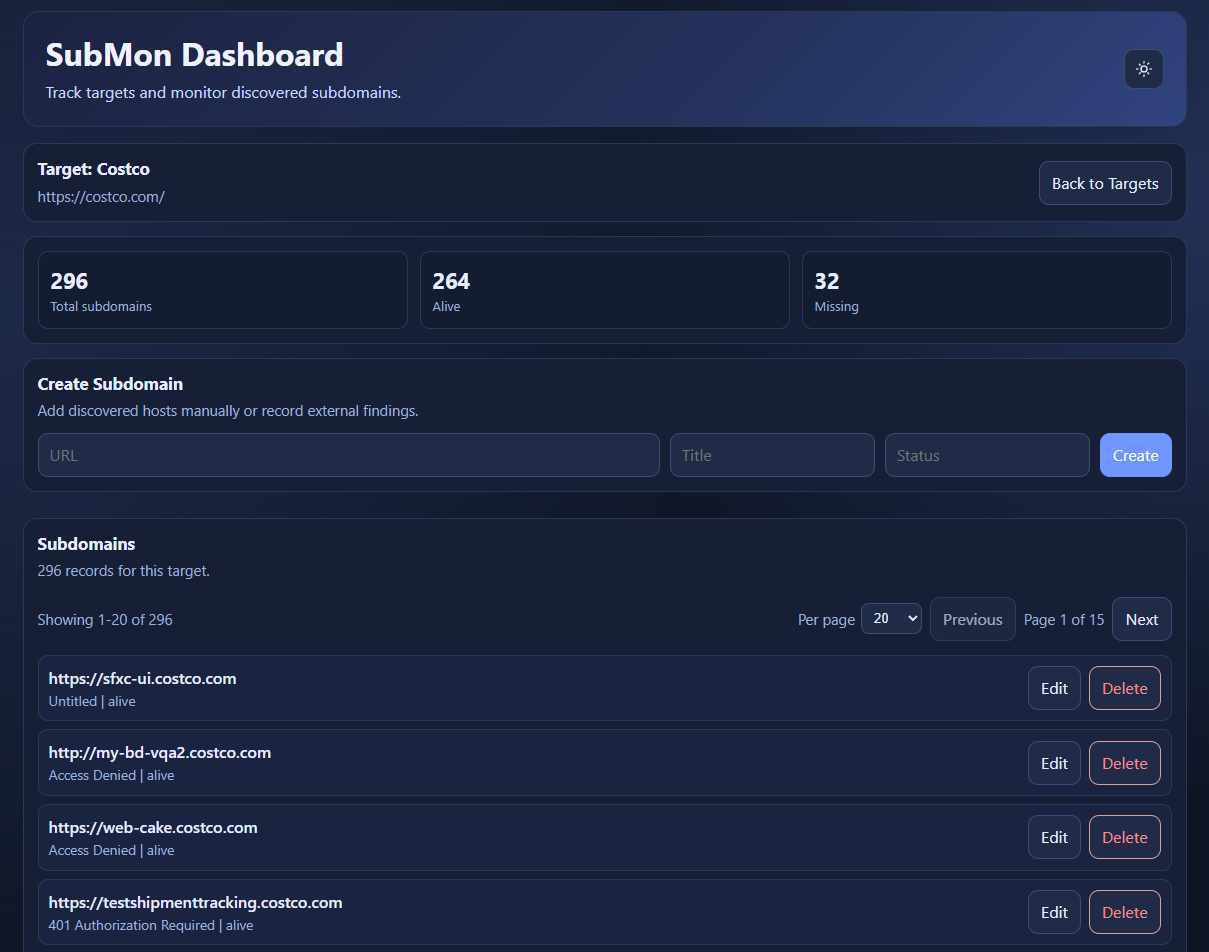
target page

  • Here you can see result from the last scan: which subdomain is new, which is missing.
  • You will also see the title of that subdomain, but it might not be accurate.

Tech Stack

Backend: FastAPI

  • ORM: SQLModel
  • Data validation: Pydantic
  • SQL DB: SQLite

Frontend: React

  • ViteVibe coding

Scanning Tools

  • subfinder
  • dnsx
  • httpx

Try It Yourself

  • Making A Discord Webhook

Manual Install

cd backend

# install tools
go install -v github.com/projectdiscovery/subfinder/v2/cmd/subfinder@latest
go install -v github.com/projectdiscovery/dnsx/cmd/dnsx@latest
go install -v github.com/projectdiscovery/httpx/cmd/httpx@latest

# add GOPATH/bin to PATH
export PATH=$PATH:$(go env GOPATH)/bin
# save the above command to `~/.bashrc`
source ~/.bashrc  # or ~/.zshrc
# optional env vars for backend
export DB_NAME="database.db"
export DISCORD_WEBHOOK_URL="YOUR-DISCORD-WEBHOOK"
# create a virtual env
python -m venv venv
source venv/bin/activate
pip install -r requirements.txt

# run fastapi service
python -m app.main

# run worker in a new terminal
python -m app.services.worker

# check Swagger doc
http://localhost:8000/docs

# check ReDoc
http://localhost:8000/redoc

cd frontend

# run frontend
npm i
npm install node
npm run dev

Docker Compose (recommended)

From the project root:

# optional: create env file and set Discord webhook for alerts
cp .env.example .env
# then edit .env and set DISCORD_WEBHOOK_URL

# build and start frontend + backend + worker
docker compose up --build -d

Open:

  • Frontend: http://localhost:5173
  • API docs: http://localhost:8000/docs
# stop services
docker compose down

Workflow

flowchart TD
    U[User / Frontend] -->|Scan Target| A[FastAPI Backend]
    U -->|Schedule Scan| A

    A -->|Create or update ScanRun = queued| DB[(SQLite)]
    W[Worker Loop] -->|Poll queued jobs + enqueue due schedules| DB
    W -->|Pick next queued ScanRun| S[Scanner Pipeline]

    S --> SF[subfinder]
    SF --> DX[dnsx]
    DX --> HX[httpx]
    HX --> D[Diff with existing subdomains]

    D -->|Insert new subdomain| DB
    D -->|Mark missing subdomain| DB
    D -->|Send new findings| DIS[Discord Webhook]

    S -->|success / failed| W
    W -->|Update ScanRun status| DB
  1. Frontend triggers scan or schedule endpoints.
  2. API stores state in ScanRun (queued, running, success, failed).
  3. Worker loops through queued and scheduled jobs.
  4. Scanner runs subfinder -> dnsx -> httpx, diffs results, updates DB, and sends Discord alerts for new subdomains.



  • Release notes
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    591
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    481
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    389
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    332
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    255
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    247

Explore all tools

Browse our collection of tools

View all tools →