TriSuElla-AIDLCA-Framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…

Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.

Vulnerability Assessment Scanner with Report Generation

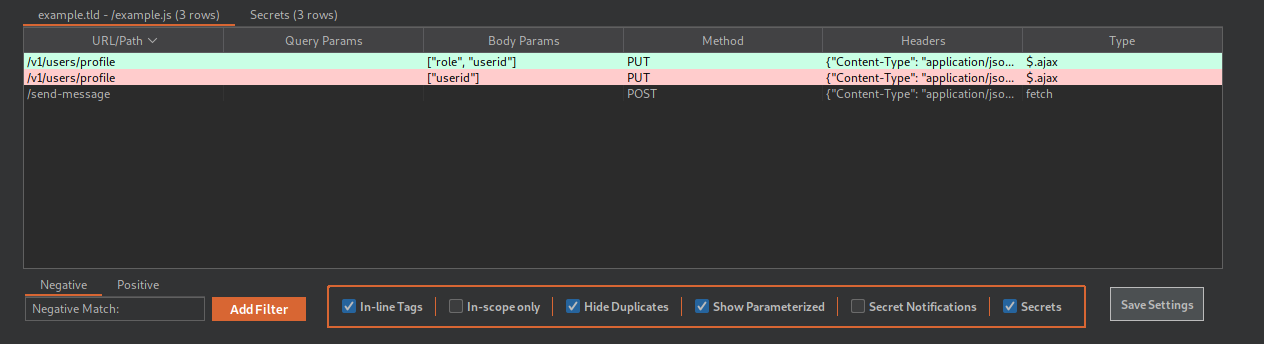
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice

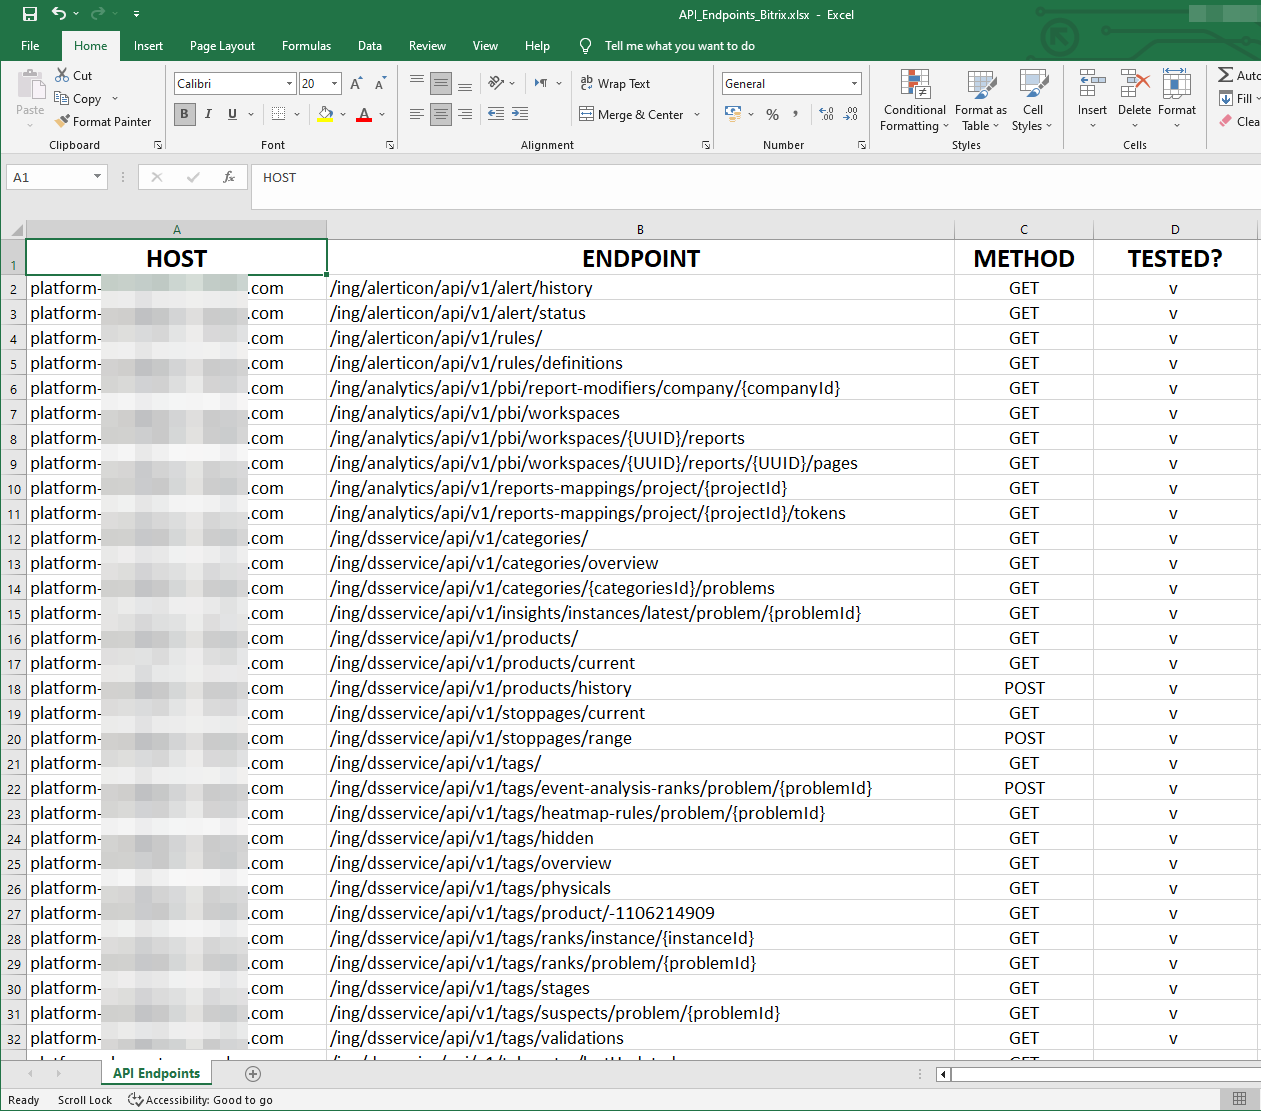
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.

Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…

Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.

OWASP Secure Agent Playbook Project

High-performance open-source security scanner combining SAST, SCA, Secret Detection, and IaC analysis, built for developers and CI/CD pipelines,…

Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.

Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.

Self-service pentest platform that only scans domains whose ownership is proven, and re-checks that proof at scan time. OWASP, TLS, DNS and port…

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…