

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
61 results
yakit preview

yakit

GitHubyaklang/yakit

All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…

command-and-controlexploit-frameworksfuzzing+9
7.8k
19h 2m ago
Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis preview

Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis

GitHubkaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

binary-analysiscommand-and-controldata-exfiltration+7
13 days ago
skills preview

skills

GitHubspecterops/skills

Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…

command-and-controleducationexploitation+9
70315 days ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
1617 days ago
Project-Onyx preview

Project-Onyx

GitHubx-3306/project-onyx

Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…

ai-securitycommand-and-controlcryptography+6
11921 days ago
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis preview

StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

GitHubkaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
command-and-controldata-exfiltrationdigital-forensics+7
324 days ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
command-and-controlcryptographydigital-forensics+7
1027 days ago
DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis preview

DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis

GitHubkaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis

Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
command-and-controldata-exfiltrationdigital-forensics+4
471 month ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

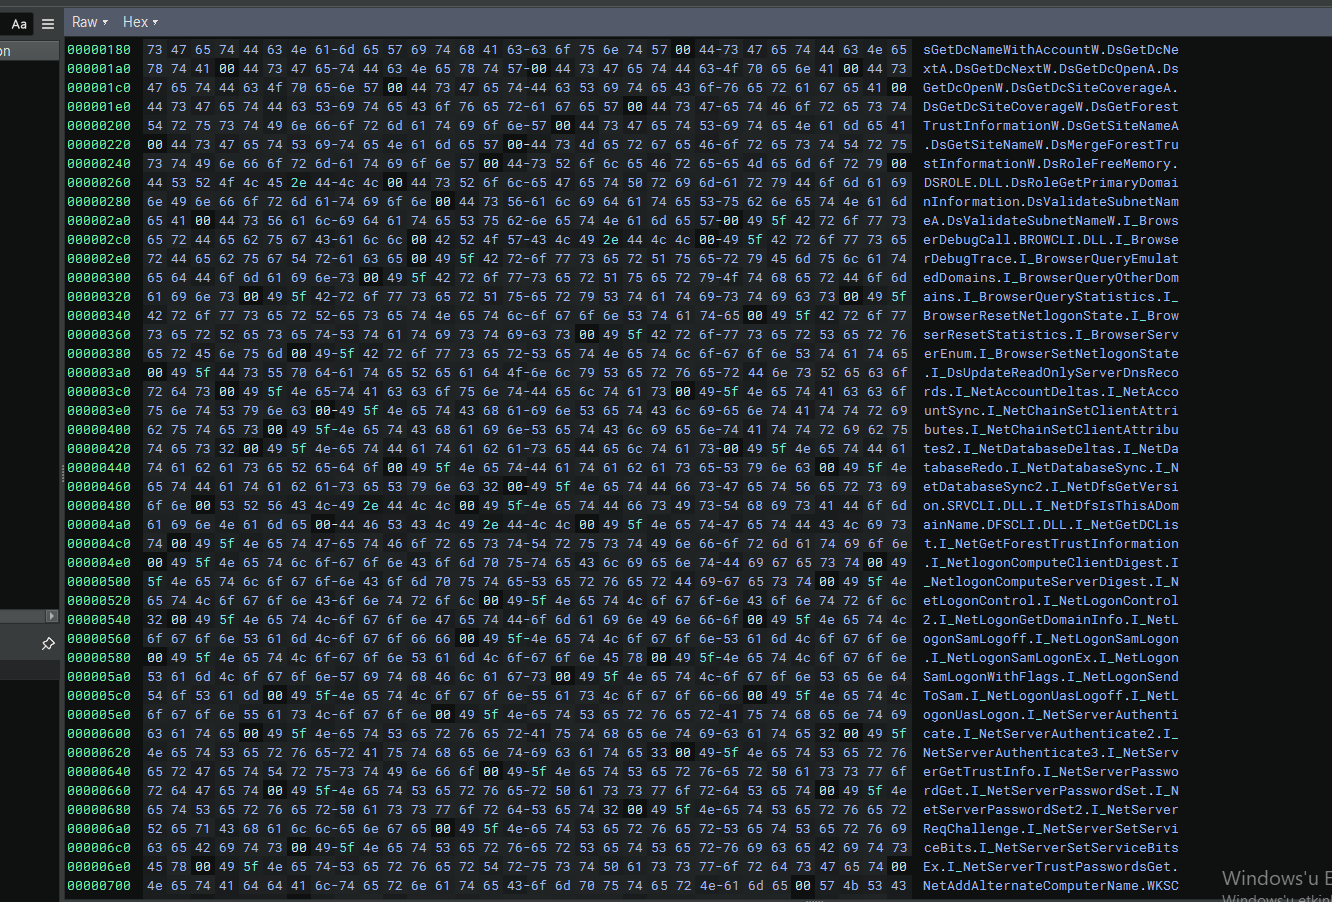
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
binary-analysiscommand-and-controldata-exfiltration+4
111 month ago
AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis preview

AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis

GitHubkaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis

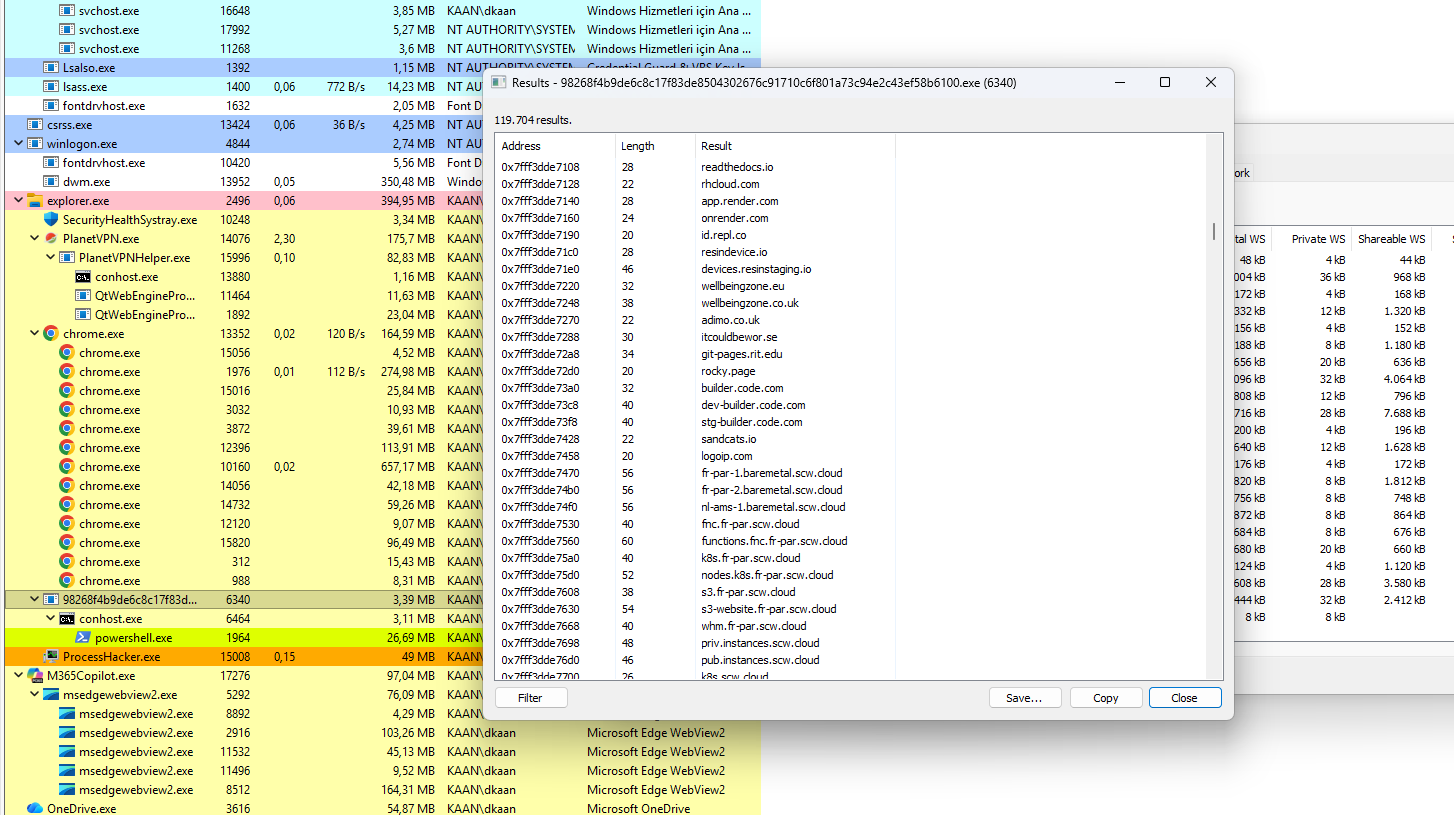
Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
binary-analysiscommand-and-controldata-exfiltration+2
31 month ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

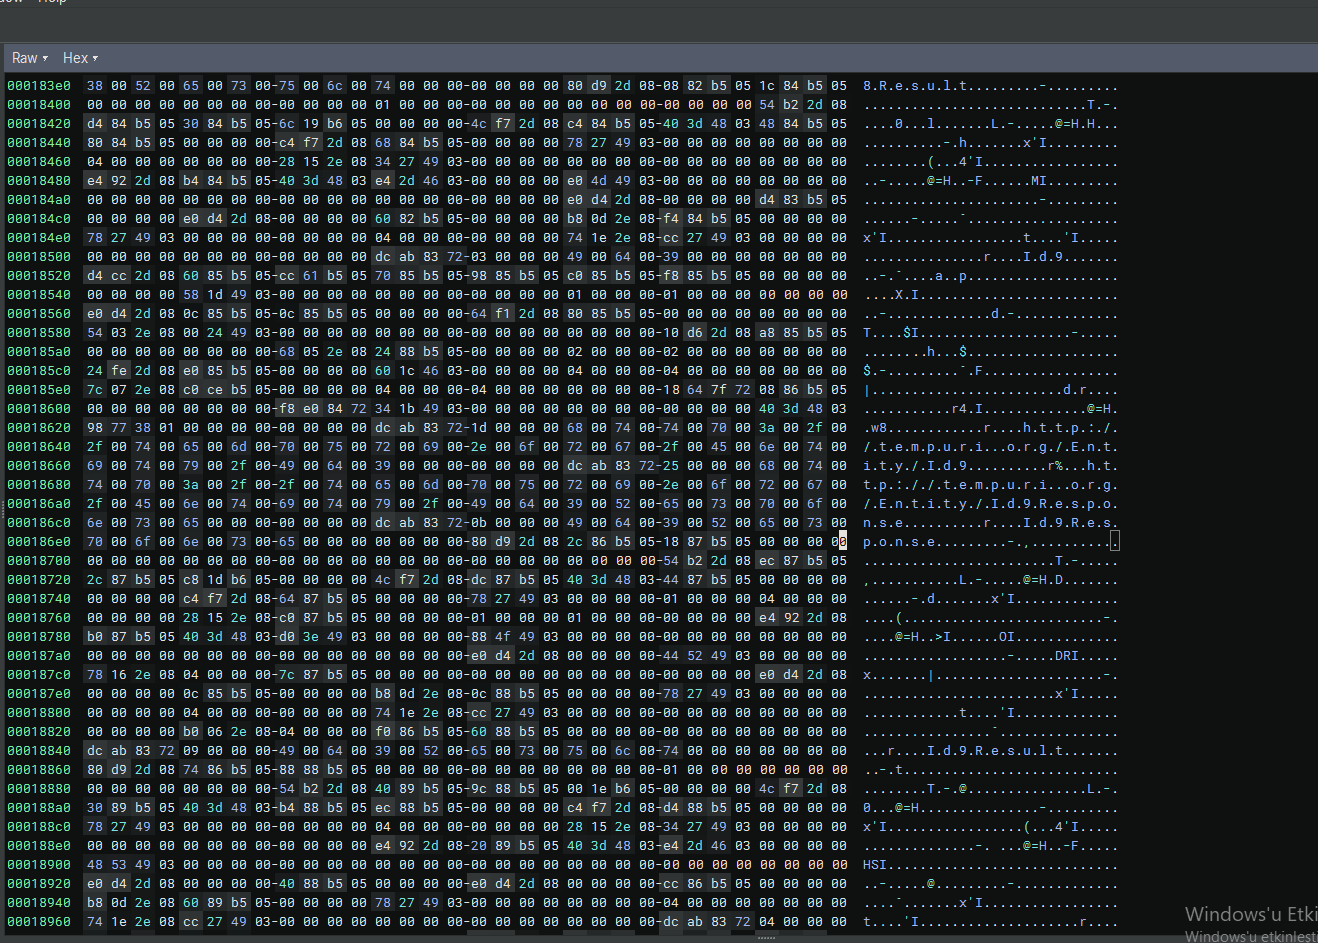
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
binary-analysiscommand-and-controldata-exfiltration+6
51 month ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

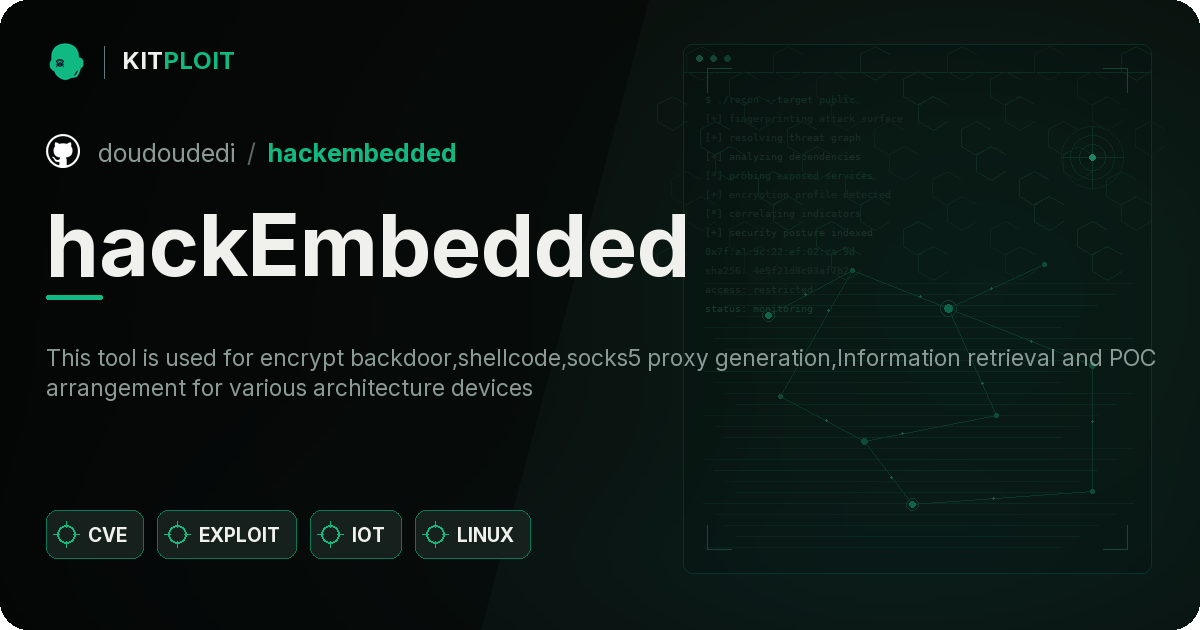
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
command-and-controldata-exfiltrationmalware-analysis+4
11 month ago
hackEmbedded preview

hackEmbedded

GitHubdoudoudedi/hackembedded

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
command-and-controlembedded-systems-securityencryption-decryption-tools+8
2062 months ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
binary-analysiscommand-and-controleducation+6
52 months ago
IKEV2-POC preview

IKEV2-POC

GitHubepsilonpointori/ikev2-poc

IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
binary-exploitationcommand-and-controlexploit-frameworks+3
63 months ago
hedgehog-tools preview

hedgehog-tools

GitHubstruppigel/hedgehog-tools

Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
binary-analysisdynamic-analysis-sandboxingforensics+4
1443 months ago
CVE-2021-4045 preview

CVE-2021-4045

GitHubkaleth4/cve-2021-4045

Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
command-and-controlembedded-systems-securityexploitation+6
3 months ago
SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298 preview

SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298

GitHubabc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough

command-and-controleducationemail-security+9
4 months ago
Previous1234Next