subdomain-bruteforce-list

Large wordlist (34M+ entries) for subdomain bruteforcing and DNS reconnaissance during penetration testing and attack surface discovery.

Large wordlist (34M+ entries) for subdomain bruteforcing and DNS reconnaissance during penetration testing and attack surface discovery.

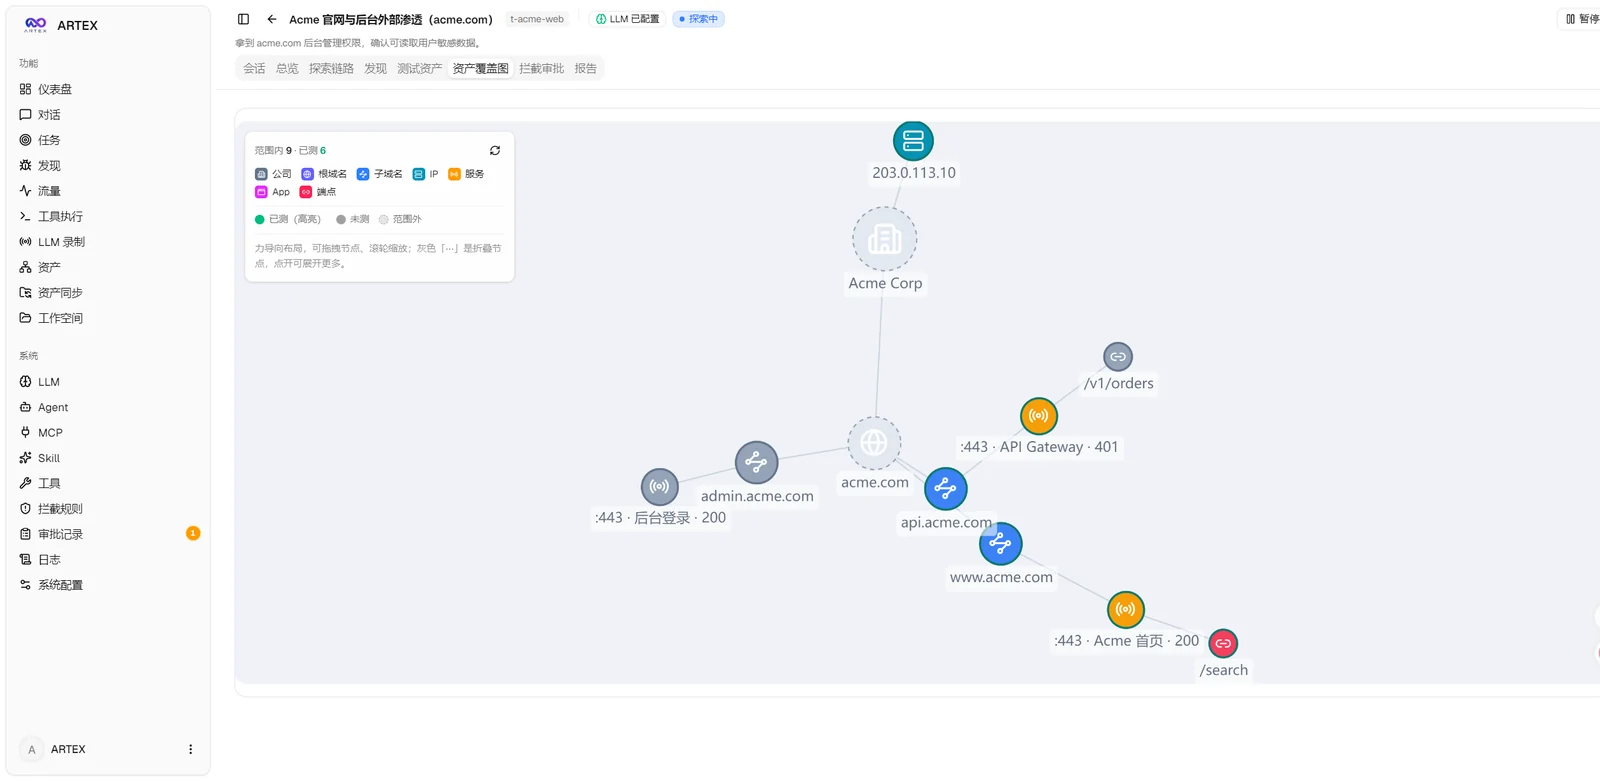
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…

🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install

Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…

Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…

Rust CLI that probes HTTP methods (including WebDAV and DeltaV verbs) against a target URL to surface verb tampering, access-control bypasses, and…

High fidelity scanner for php2shell (CVE-2026-109618 and CVE-2026-109619)

Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…

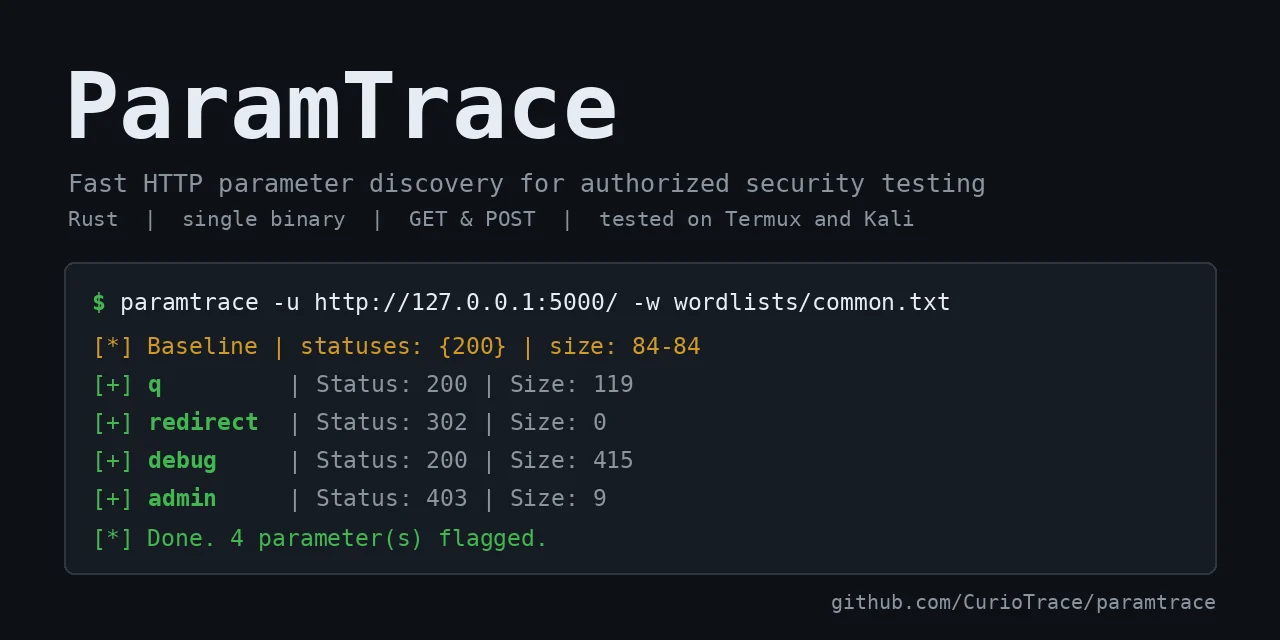
Fast HTTP parameter discovery for authorized security testing

Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…

Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…

SNMP enumeration tool that queries SNMPv1/v2c hosts to extract system information, TCP connections, and write access for penetration testing and…

Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…

Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.

The one shot API attacker tool - finds the API url from the given root simulate the automated attacks

Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…

Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…