Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-36842-Backdooring-Oncord-Android-Sterio- — CVE-2024-36842, Creating Persistent Backdoor on Oncord+ android/ios car infotaiment using malicious script! | Kitploit
Tools/GitHubGitHub/abbiy/cve-2024-36842-backdooring-oncord-android-sterio-
Android SecurityEmbedded Systems SecurityPersistence MechanismsVulnerability AnalysisExploitationPost-ExploitationPenetration TestingHardware Security
Share
GitHub
abbiy/cve-2024-36842-backdooring-oncord-android-sterio-

CVE-2024-36842-Backdooring-Oncord-Android-Sterio-

CVE-2024-36842, Creating Persistent Backdoor on Oncord+ android/ios car infotaiment using malicious script!

View Repository
5341 year agoNot yet reviewed

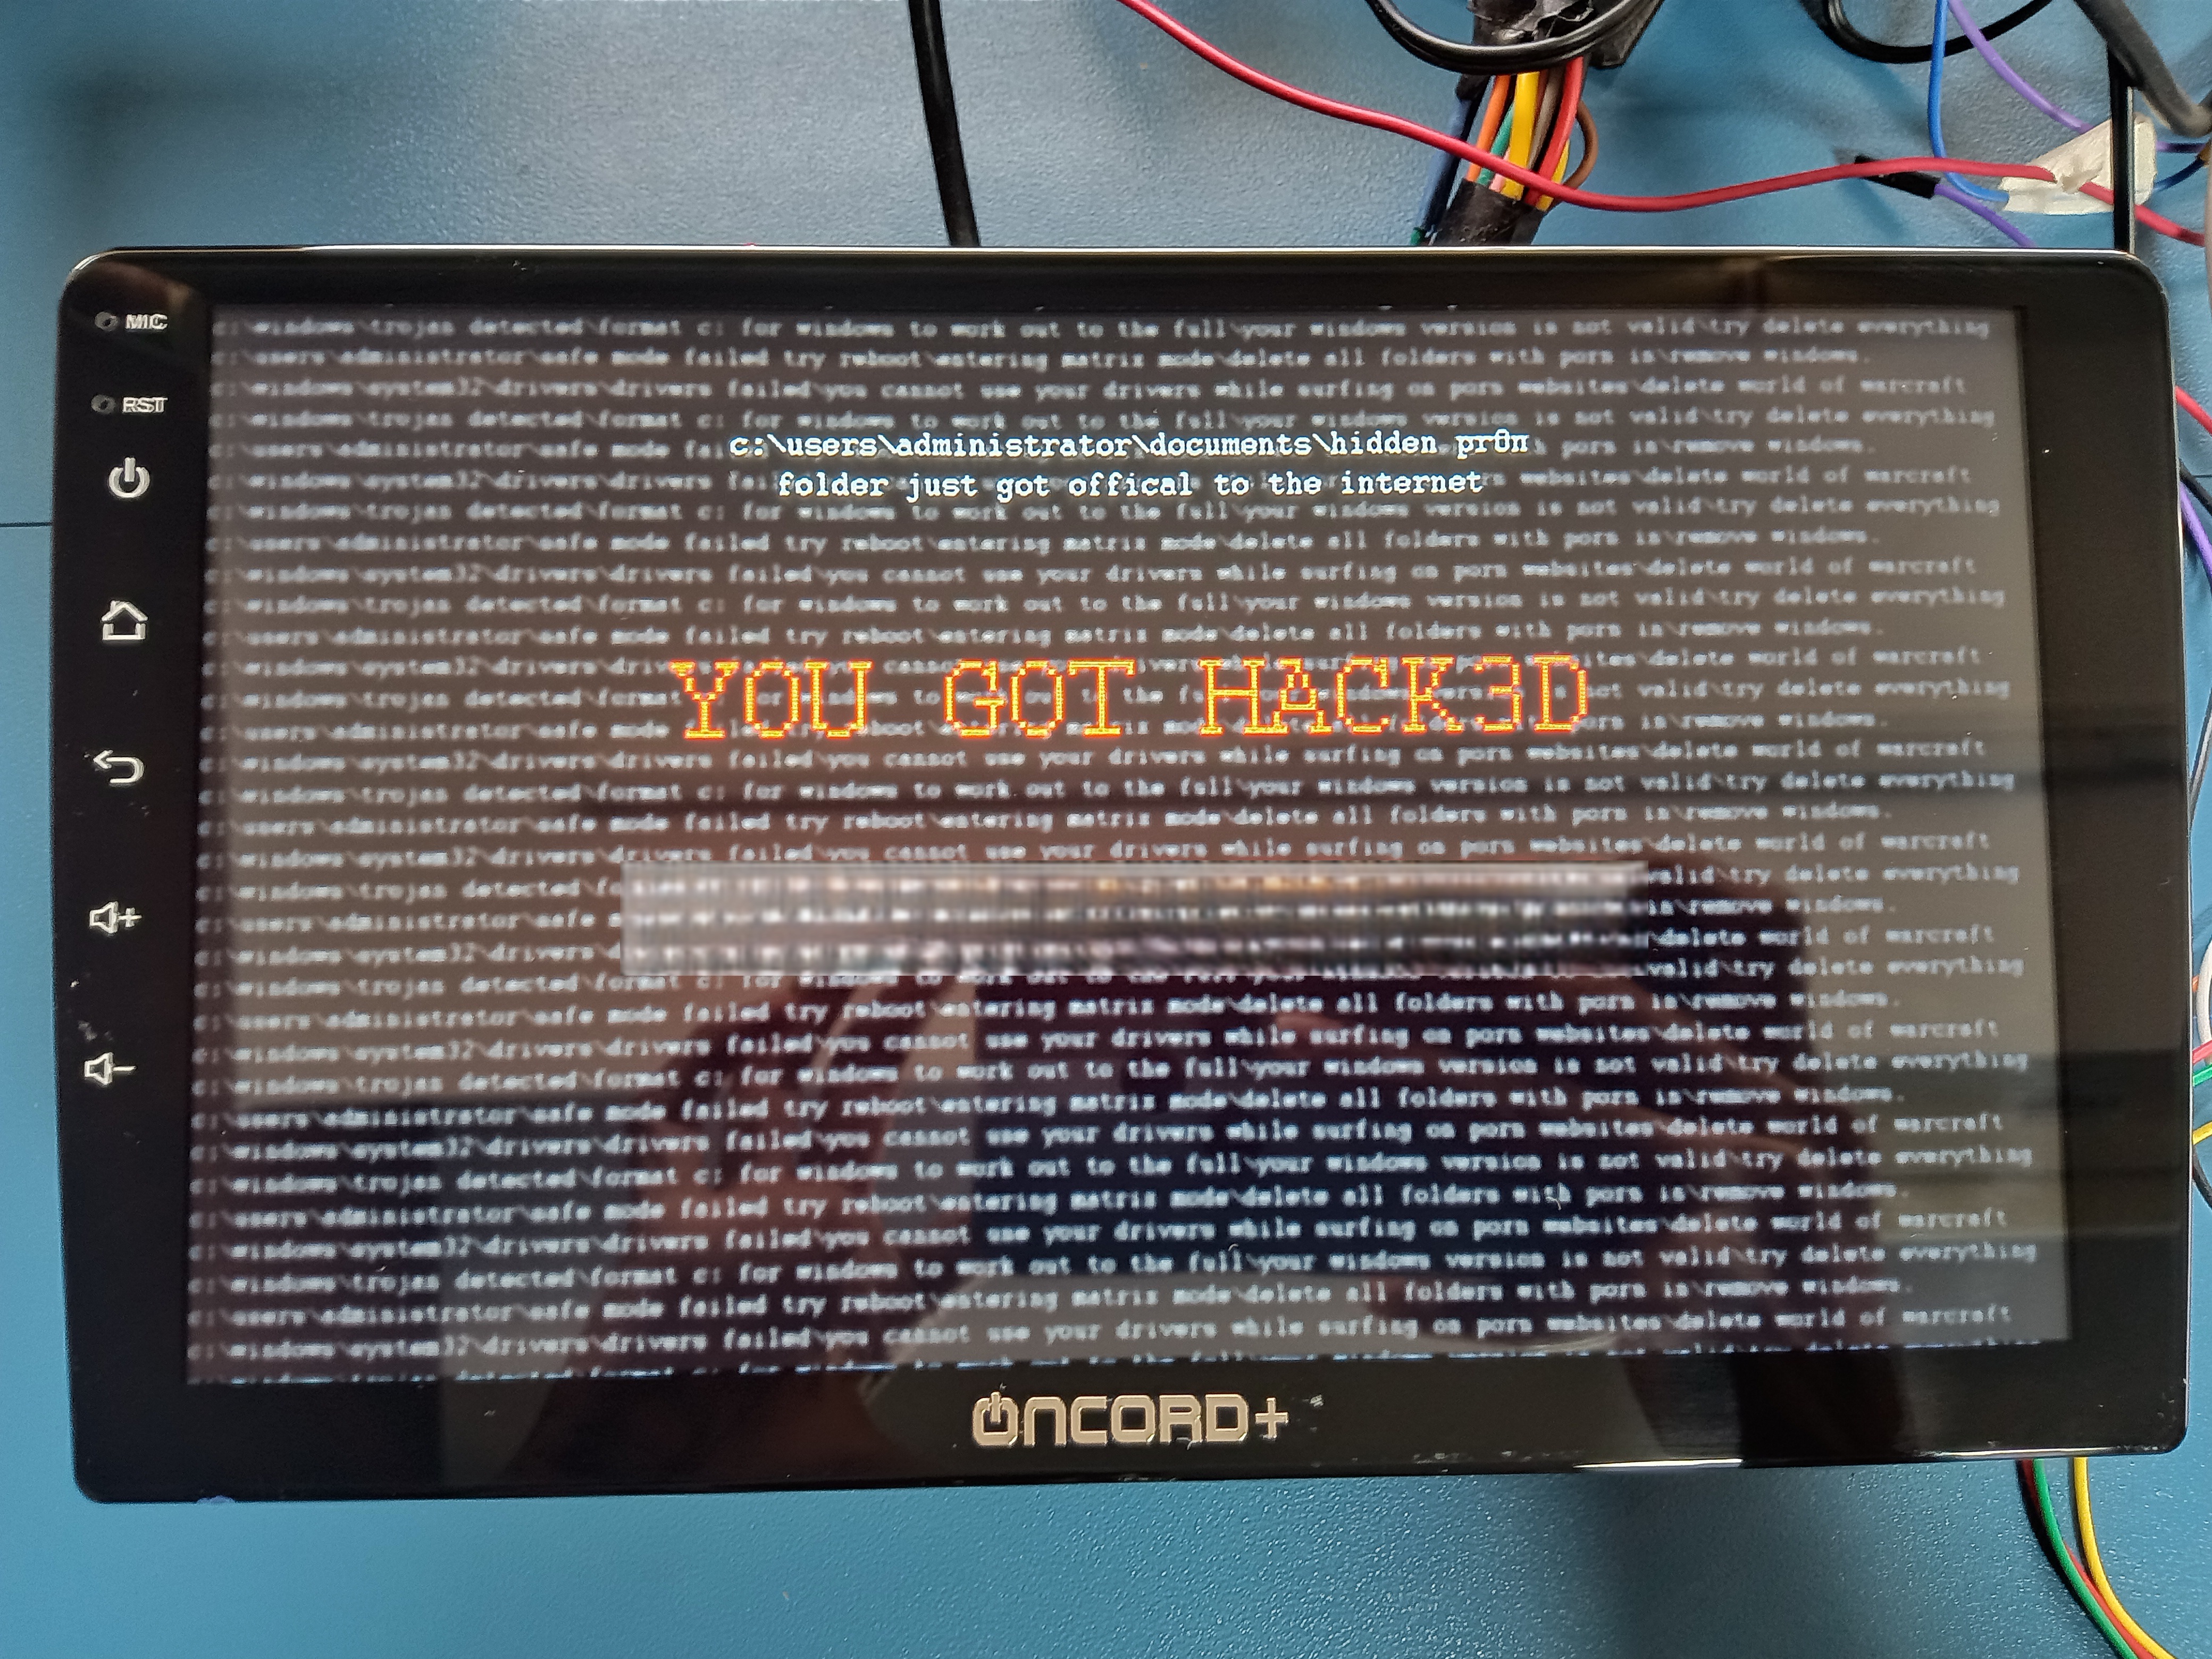
# CVE-2024-36842 Backdooring-Oncord+ Android-Sterio We have conducted vulnerablity assessment on one of the most selling after marrket car infotainment unit. Creating Persistent Backdoor on Oncord+ android/ios car infotainment unit using malicious script!

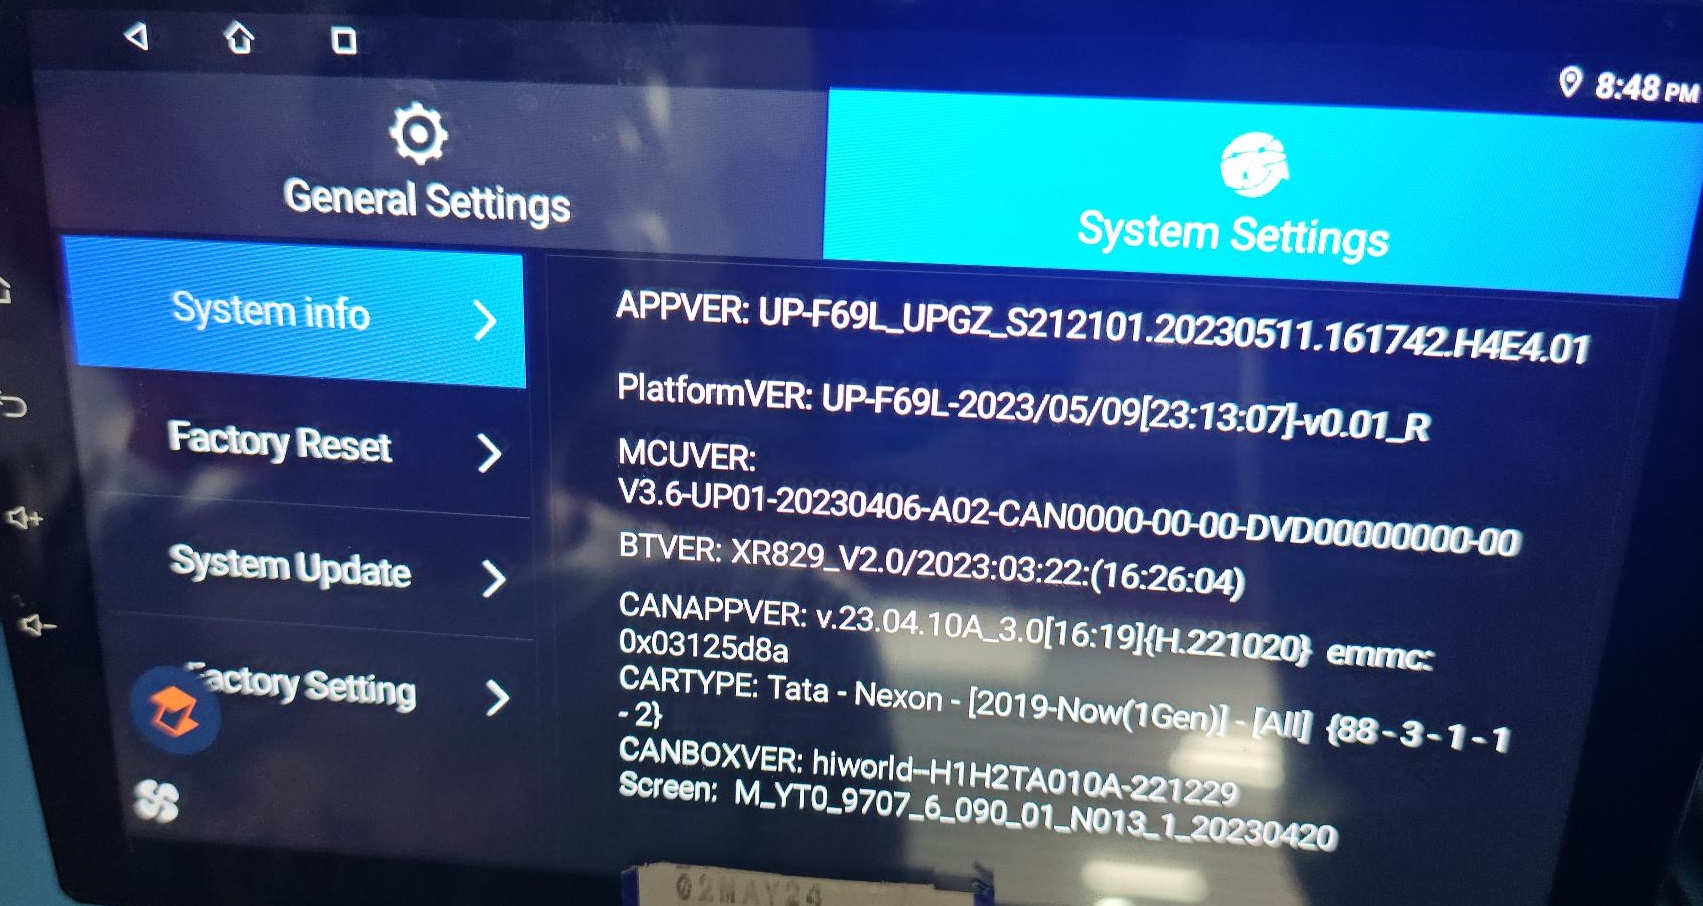
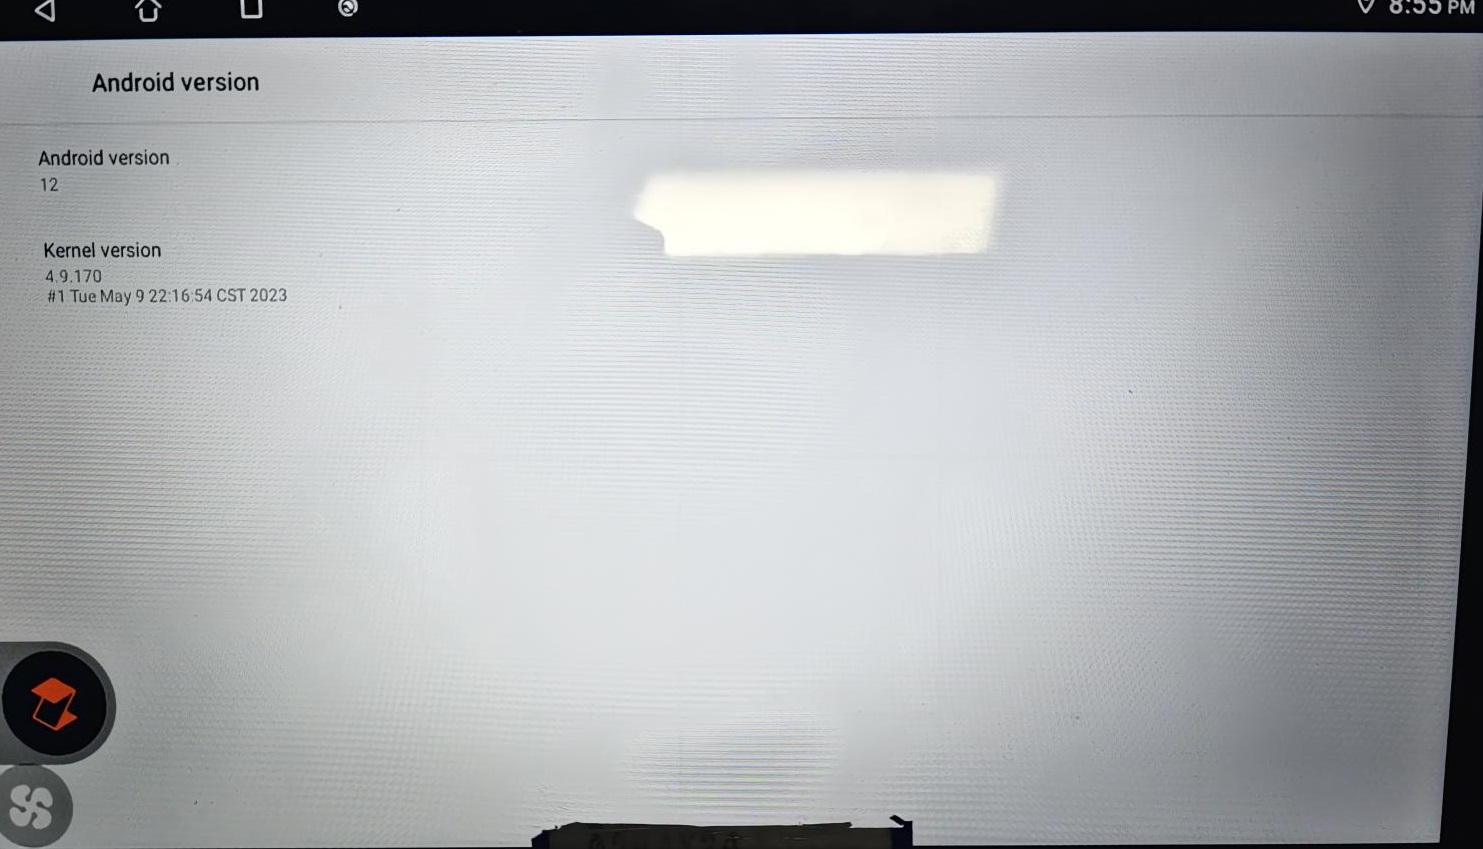
About Device: **Android version : 12

Kernel Version : 4.9.170

Model : TS17/Powered by Allwinner

Serial number : 0x03125dBa ** 329246011-7ce996ac-7cb4-4b84-92e7-cae389960646
shared image(2)

shared image(6)

shared image(5)

shared image(3)

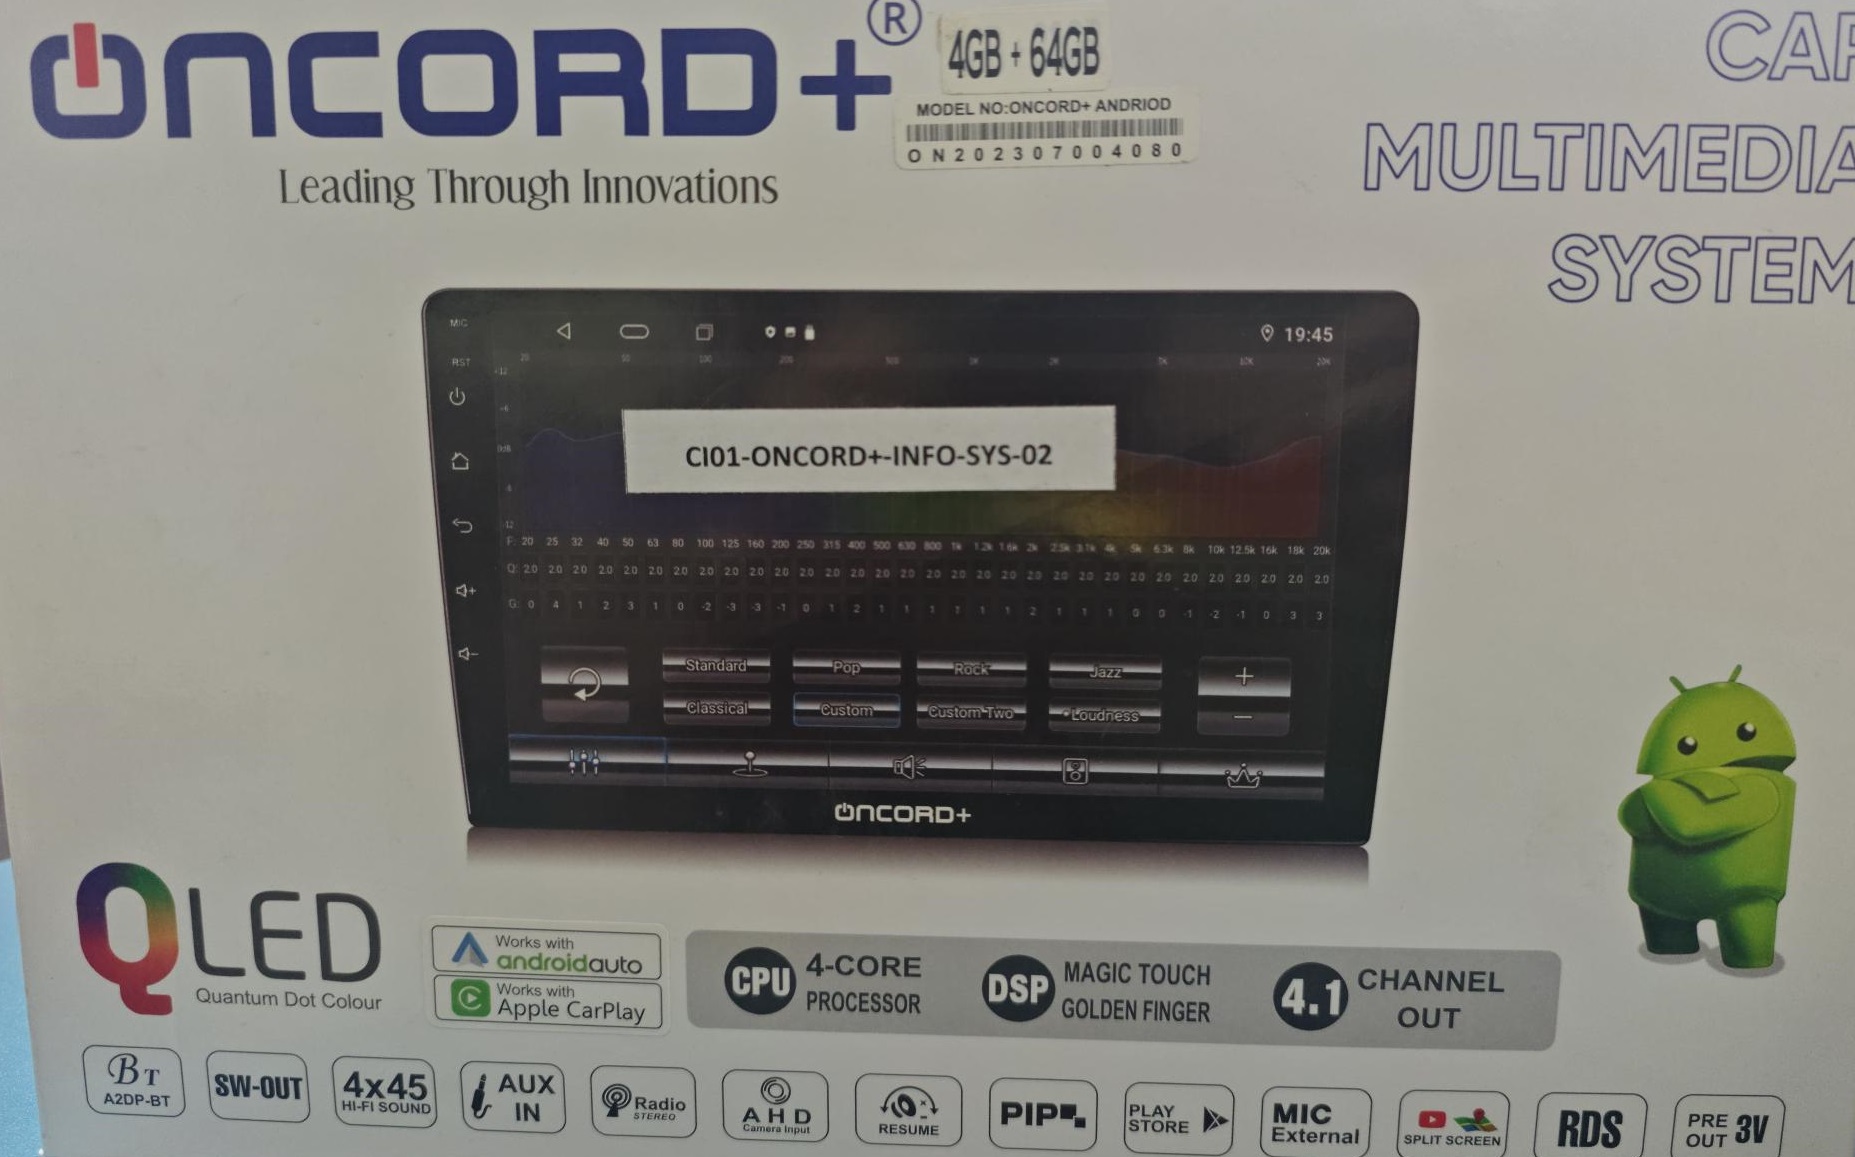
oncord

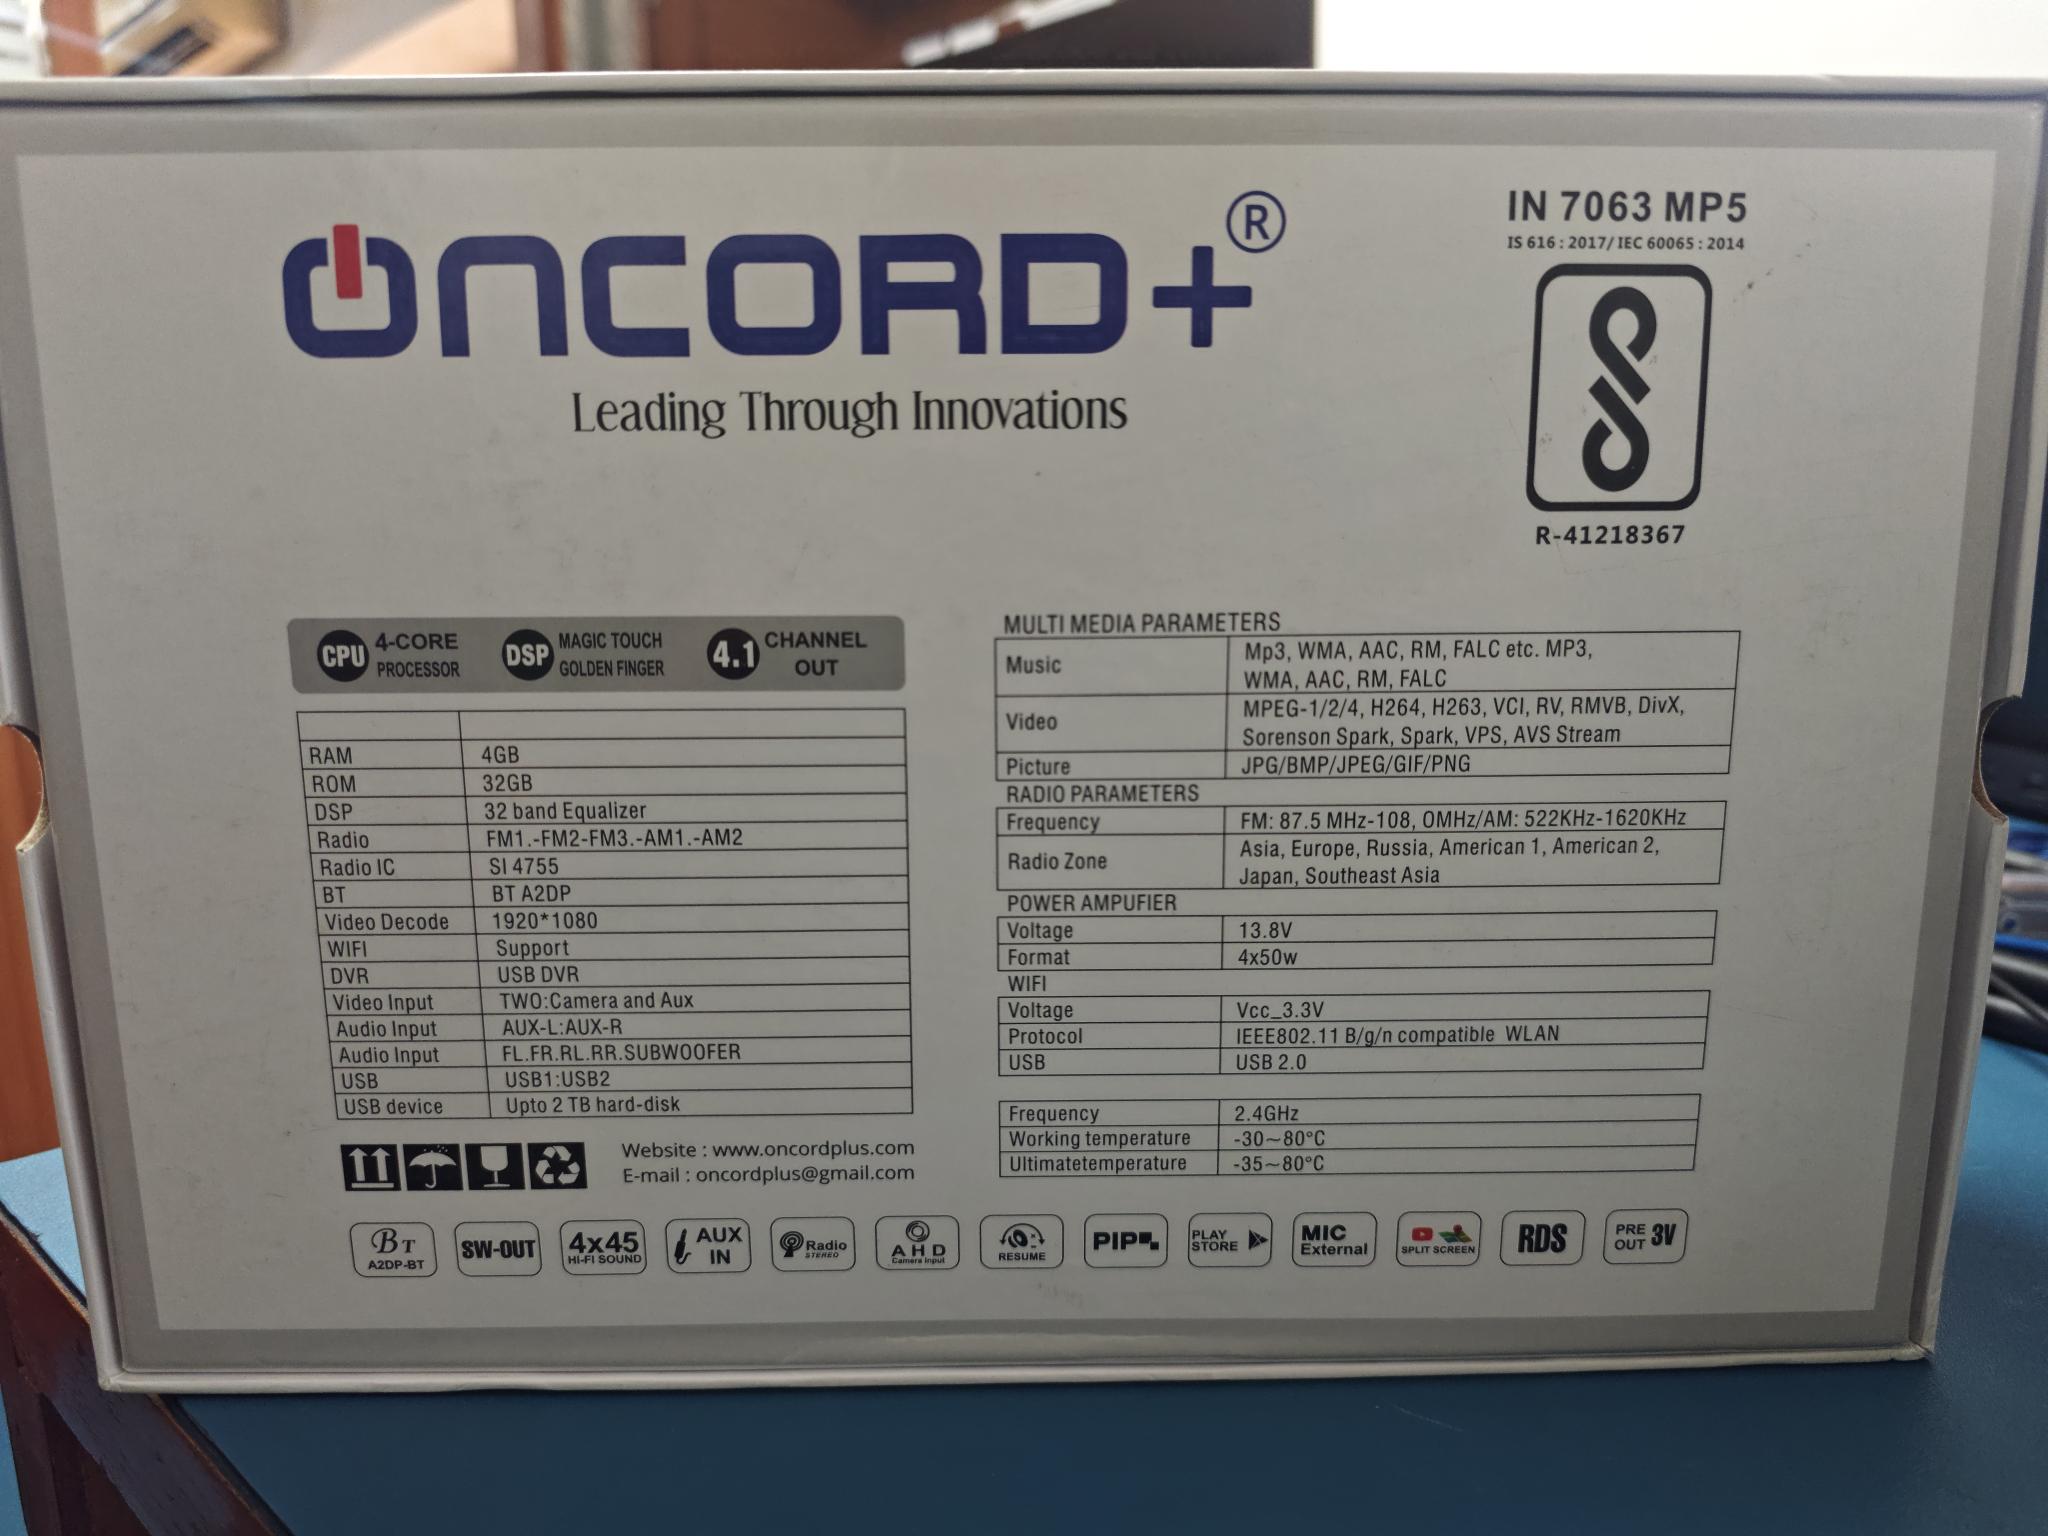
Android sterio unit by Oncord+ provides excellent performance and maintenance system based on cutting-edge technology. It is most available after market android unit fro cars in India and other countries.
images

** _Vulnerability ID Vulnerability Severity CVSS Score

NW-VUL-01 Gaining Root access of the Infotainment Unit by exploiting ADB port HIGH - 8.4

HW-VUL-02 Gaining Root access through UART Port – Improper Access Control MEDIUM - 6.4_ **

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    989
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    576
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    315

Explore all tools

Browse our collection of tools

View all tools →