Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
PoC-Deployer-System — Quick tool for utilizing CVE-2024-31317 on Android | Kitploit

Tools/GitHubGitHub/wqry085/poc-deployer-system
Android SecurityPrivilege EscalationPayload GenerationExploitationPost-ExploitationPenetration TestingMobile SecurityRemote Access Tool
GitHubwqry085/poc-deployer-system

PoC-Deployer-System

Quick tool for utilizing CVE-2024-31317 on Android

View Repository
7410539 months agoReviewed by Kitploit
Share

PoC-Deployer-System

License: MIT Android

A visualization tool based on CVE-2024-31317 for Zygote injection, integrating remote terminal and file transfer capabilities.

Binder-CLI - Access system services via binder

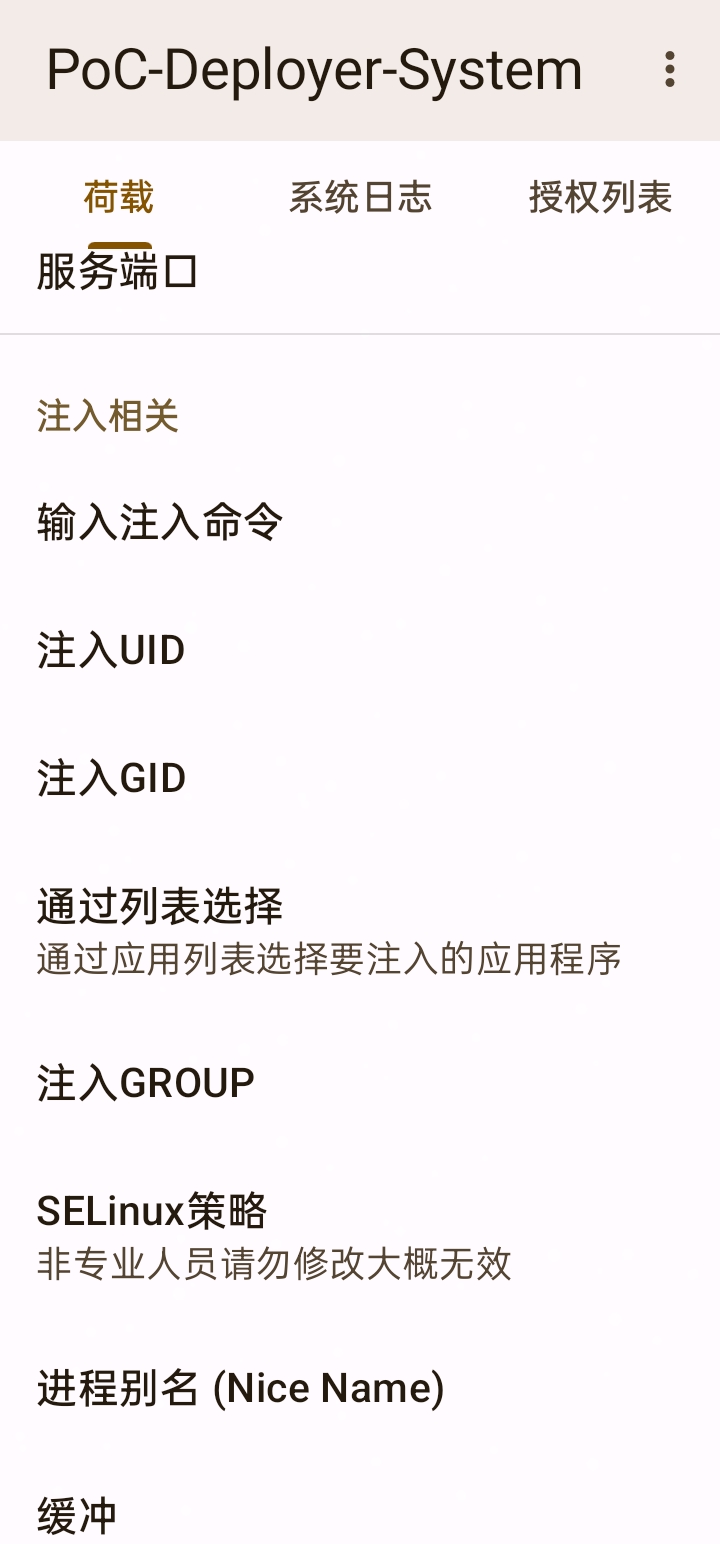
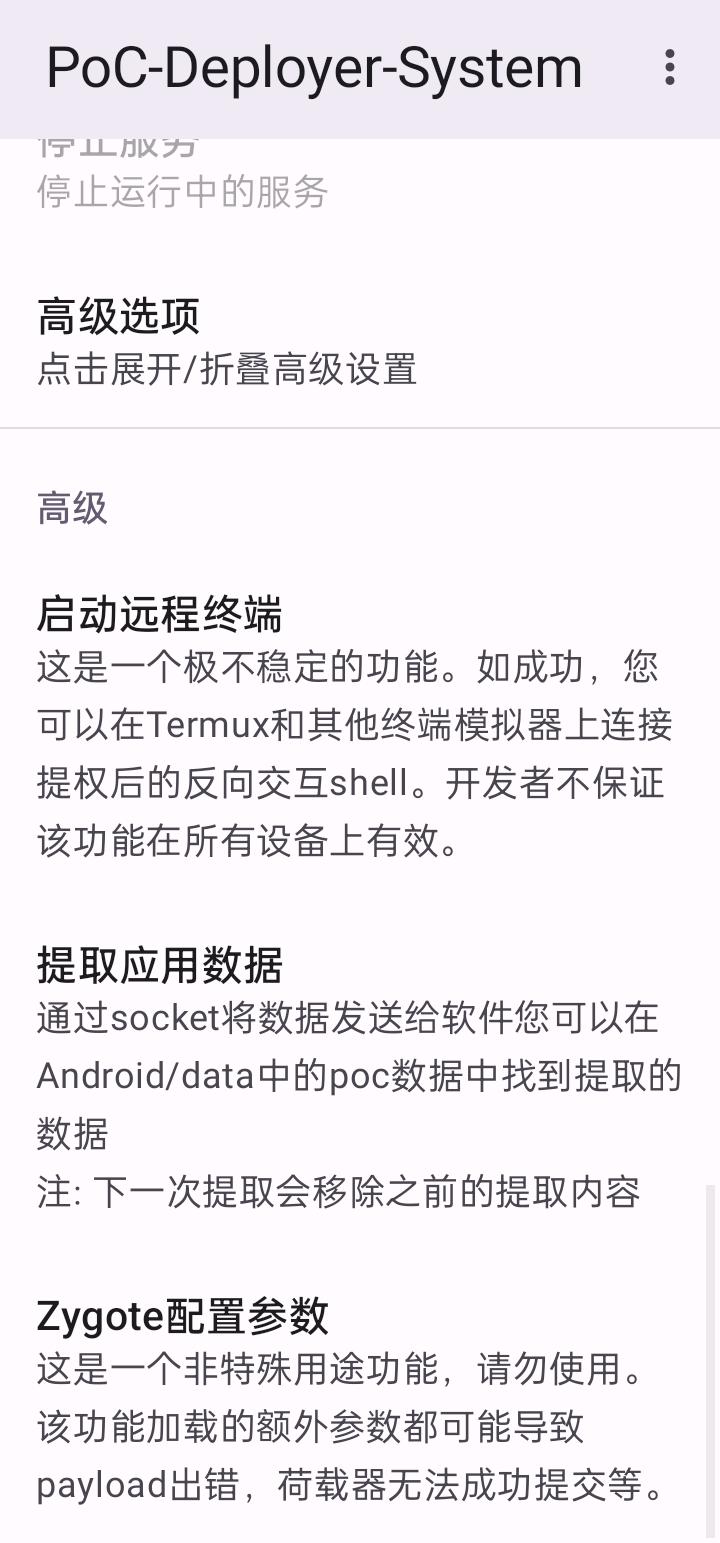
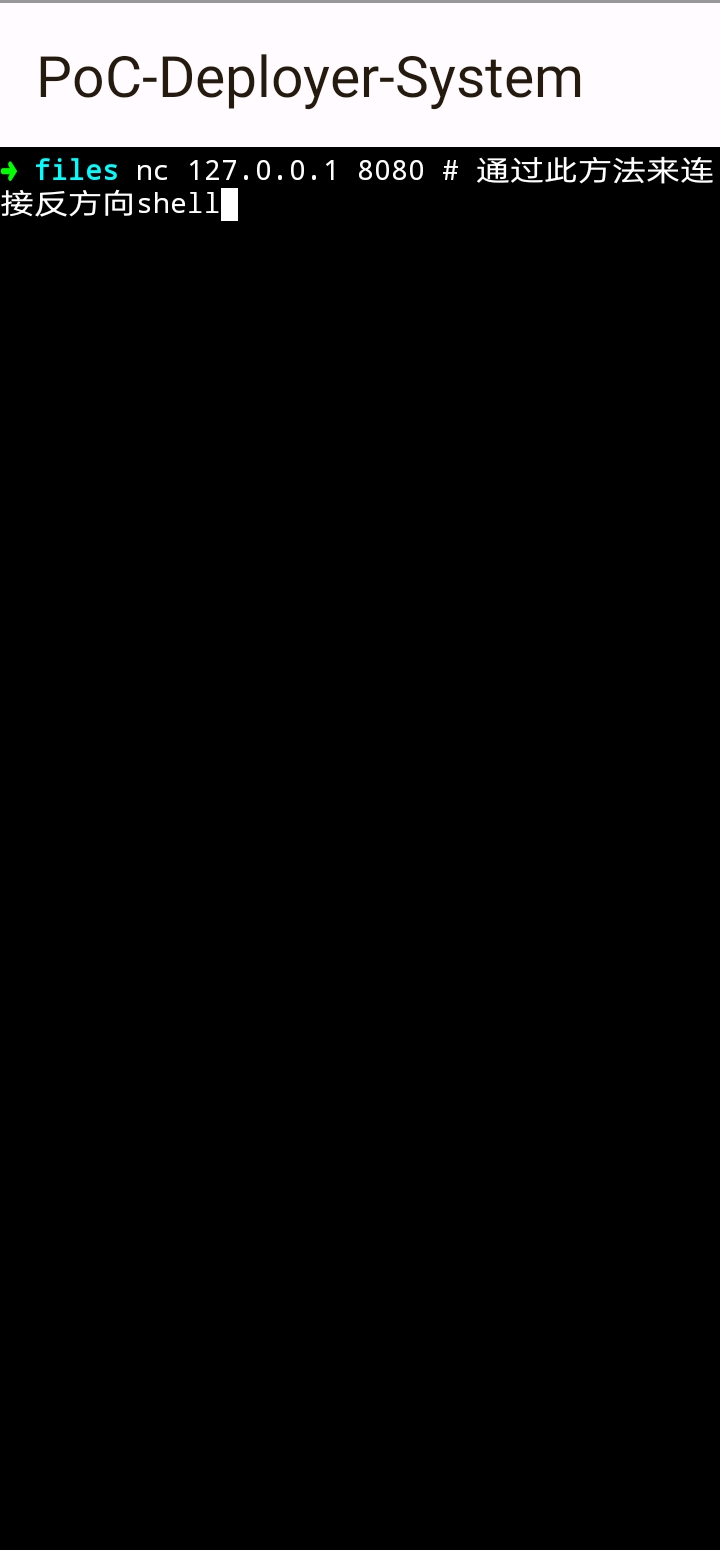
Screenshots

UID/GID InjectionAdvanced FeaturesReverse Shell
injectionadvancedshell

Quick Start

Requirements

  • Android 9-13, security patch before 2024.6
  • Shizuku activated
  • Disable vendor restrictions on special devices (MIUI/ColorOS/OriginOS)

Usage

  1. Install and activate Shizuku
  2. Install app, grant Shizuku permission
  3. Configure target parameters (UID/GID/SELinux context)
  4. Start remote terminal (reverse shell)
  5. Connect to reverse shell:
stty raw -echo; nc 127.0.0.1 8080; stty sane

Features

FeatureDescription
Zygote Injectionvia hidden_api_blacklist_exemptions
Remote TerminalFull PTY, window resize support
App Data Transfer50-100 MB/s transfer speed
Access ControlUID whitelist

Ports

PortPurposeAuthentication
8080Local reverse shellLocal + UID whitelist
8081Control interfaceMD5 key
56423File接收Local

Control Commands (Port 8081)

EXEC <cmd>       - Execute command
STATUS           - System status
POLICY_ADD <uid> - Add to whitelist
POLICY_LIST      - List whitelist
SEND_APP_DIR     - Send app directory

Troubleshooting

# Check process
ps -A | grep zYg0te
# Check ports
netstat -tlnp | grep 56423
# View logs
logcat -s FolderReceiver:*

Disclaimer

For security research only. Illegal use is prohibited. Users assume all responsibility.

Credits

https://github.com/Webldix

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    546
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    477
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    377
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    324
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    269
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    252

Explore all tools

Browse our collection of tools

View all tools →