

waf-bypass
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
api-security-testingpenetration-testingvulnerability-scanners+2
1.5k
nemesida-waf/waf-bypassAutomated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
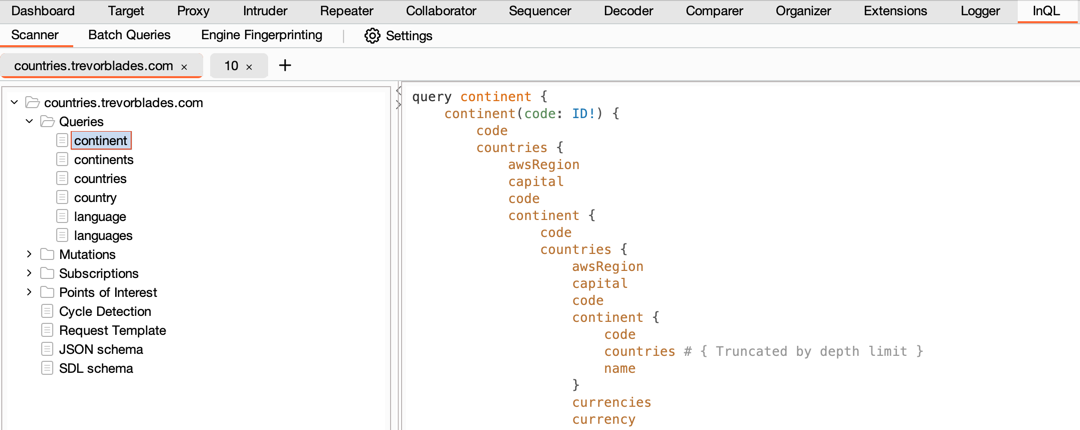 doyensec/inql
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
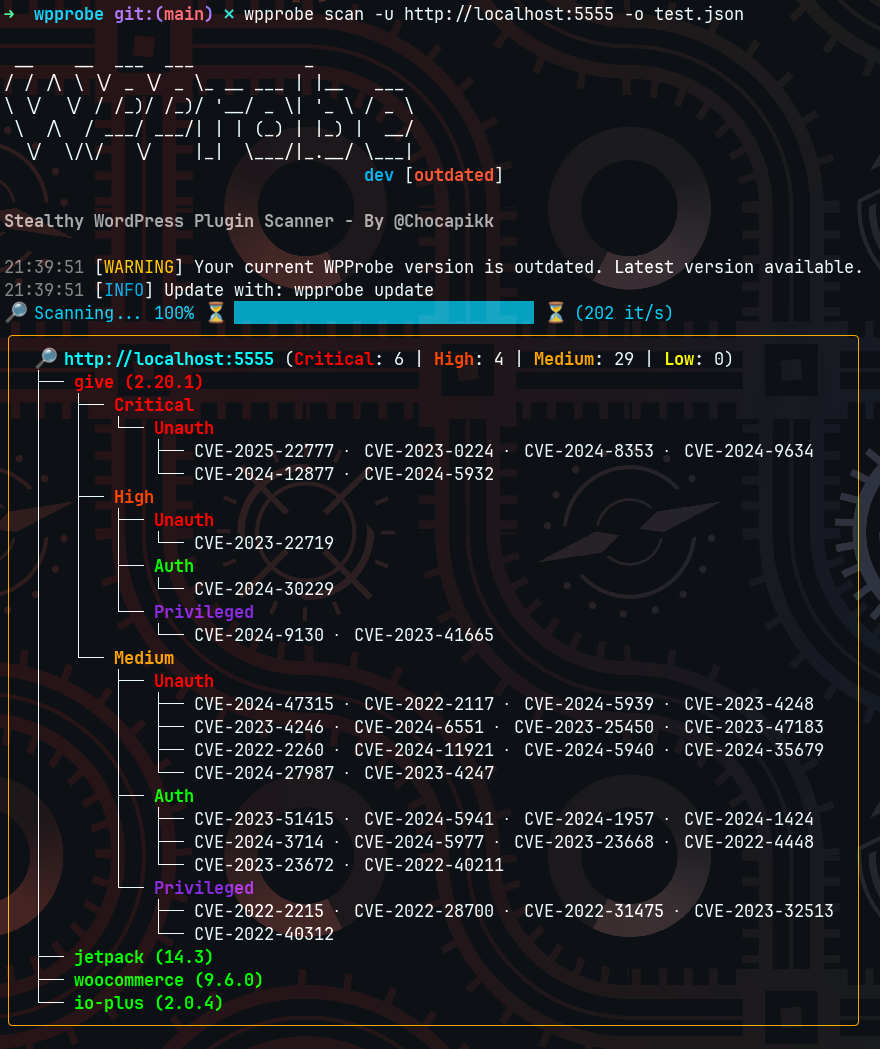 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
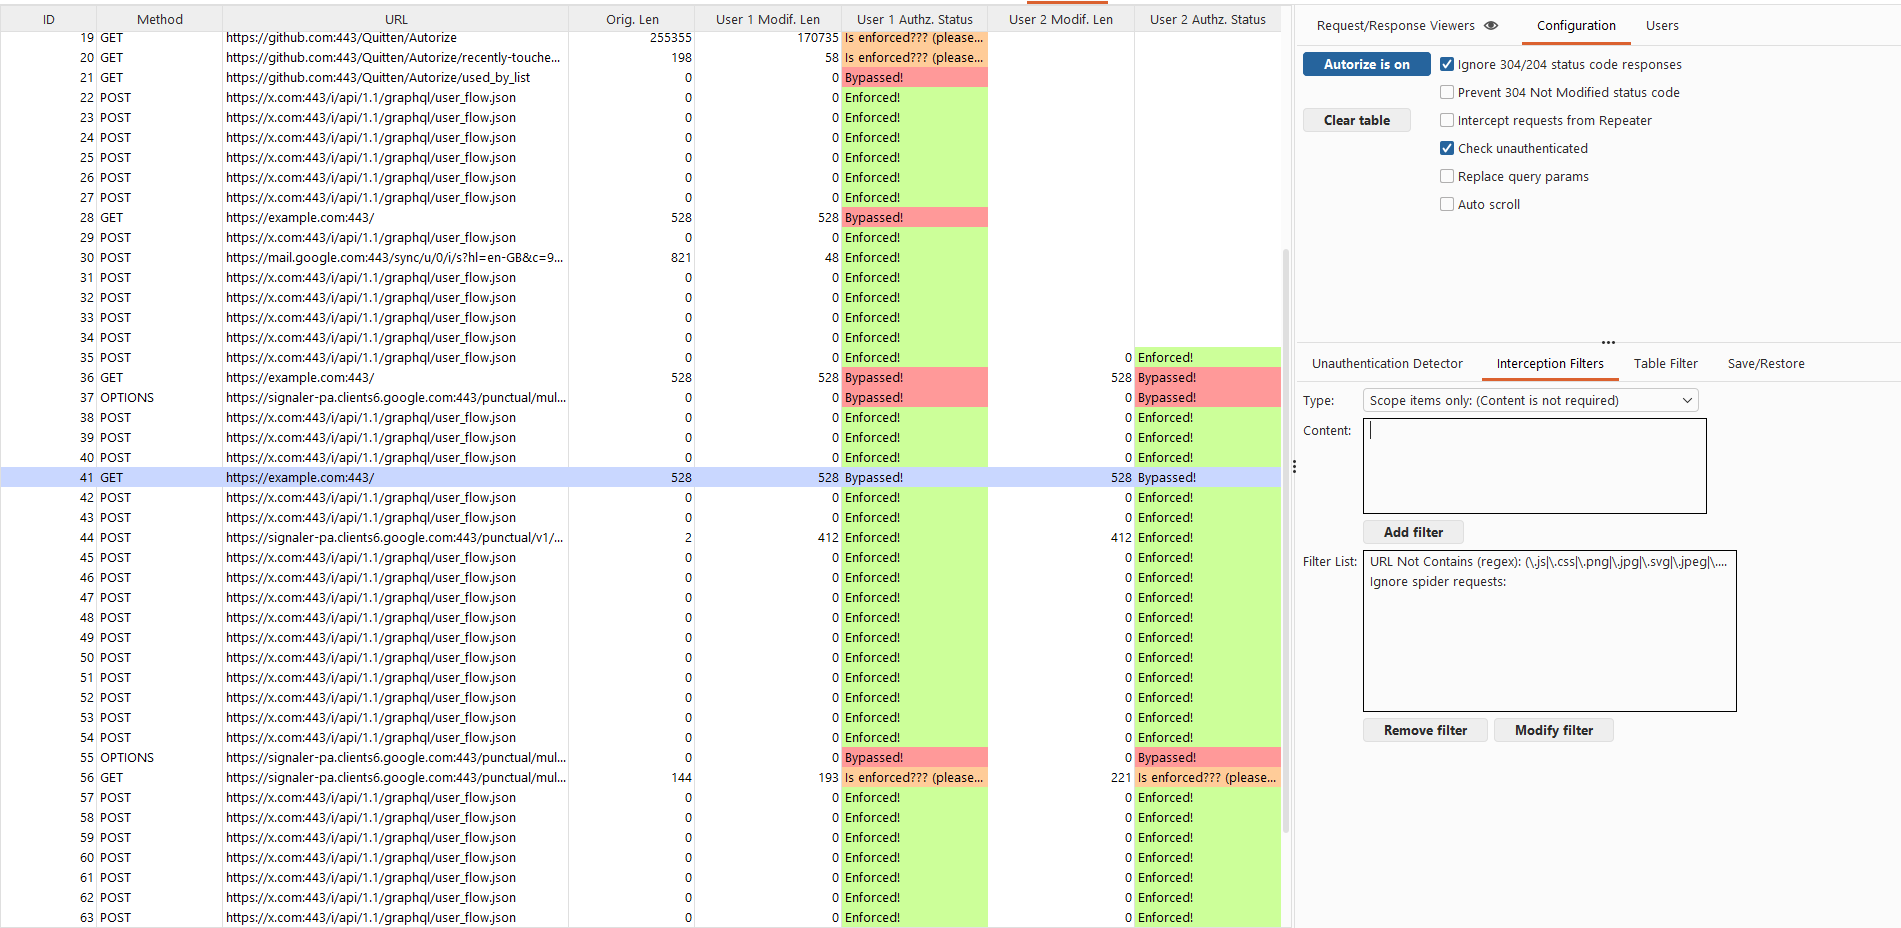 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
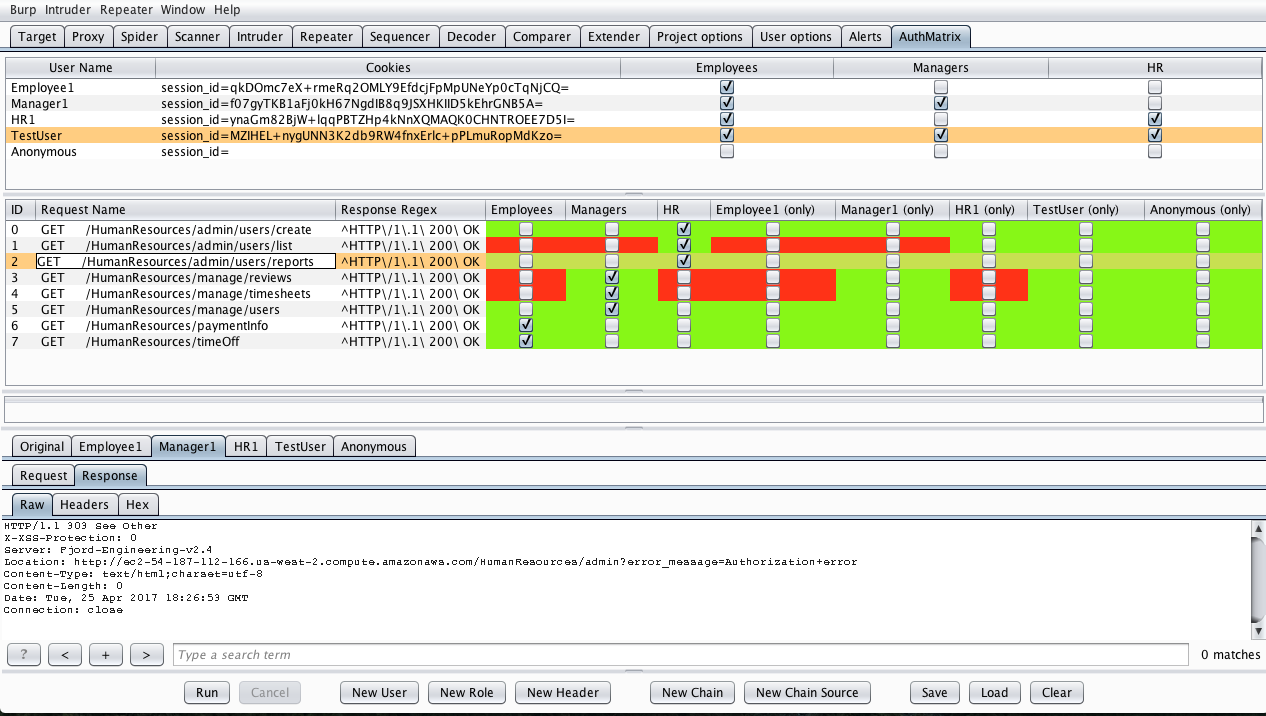 securityinnovation/authmatrix
AuthMatrix is a Burp Suite extension that provides a simple way to test authorization in web applications and web services.
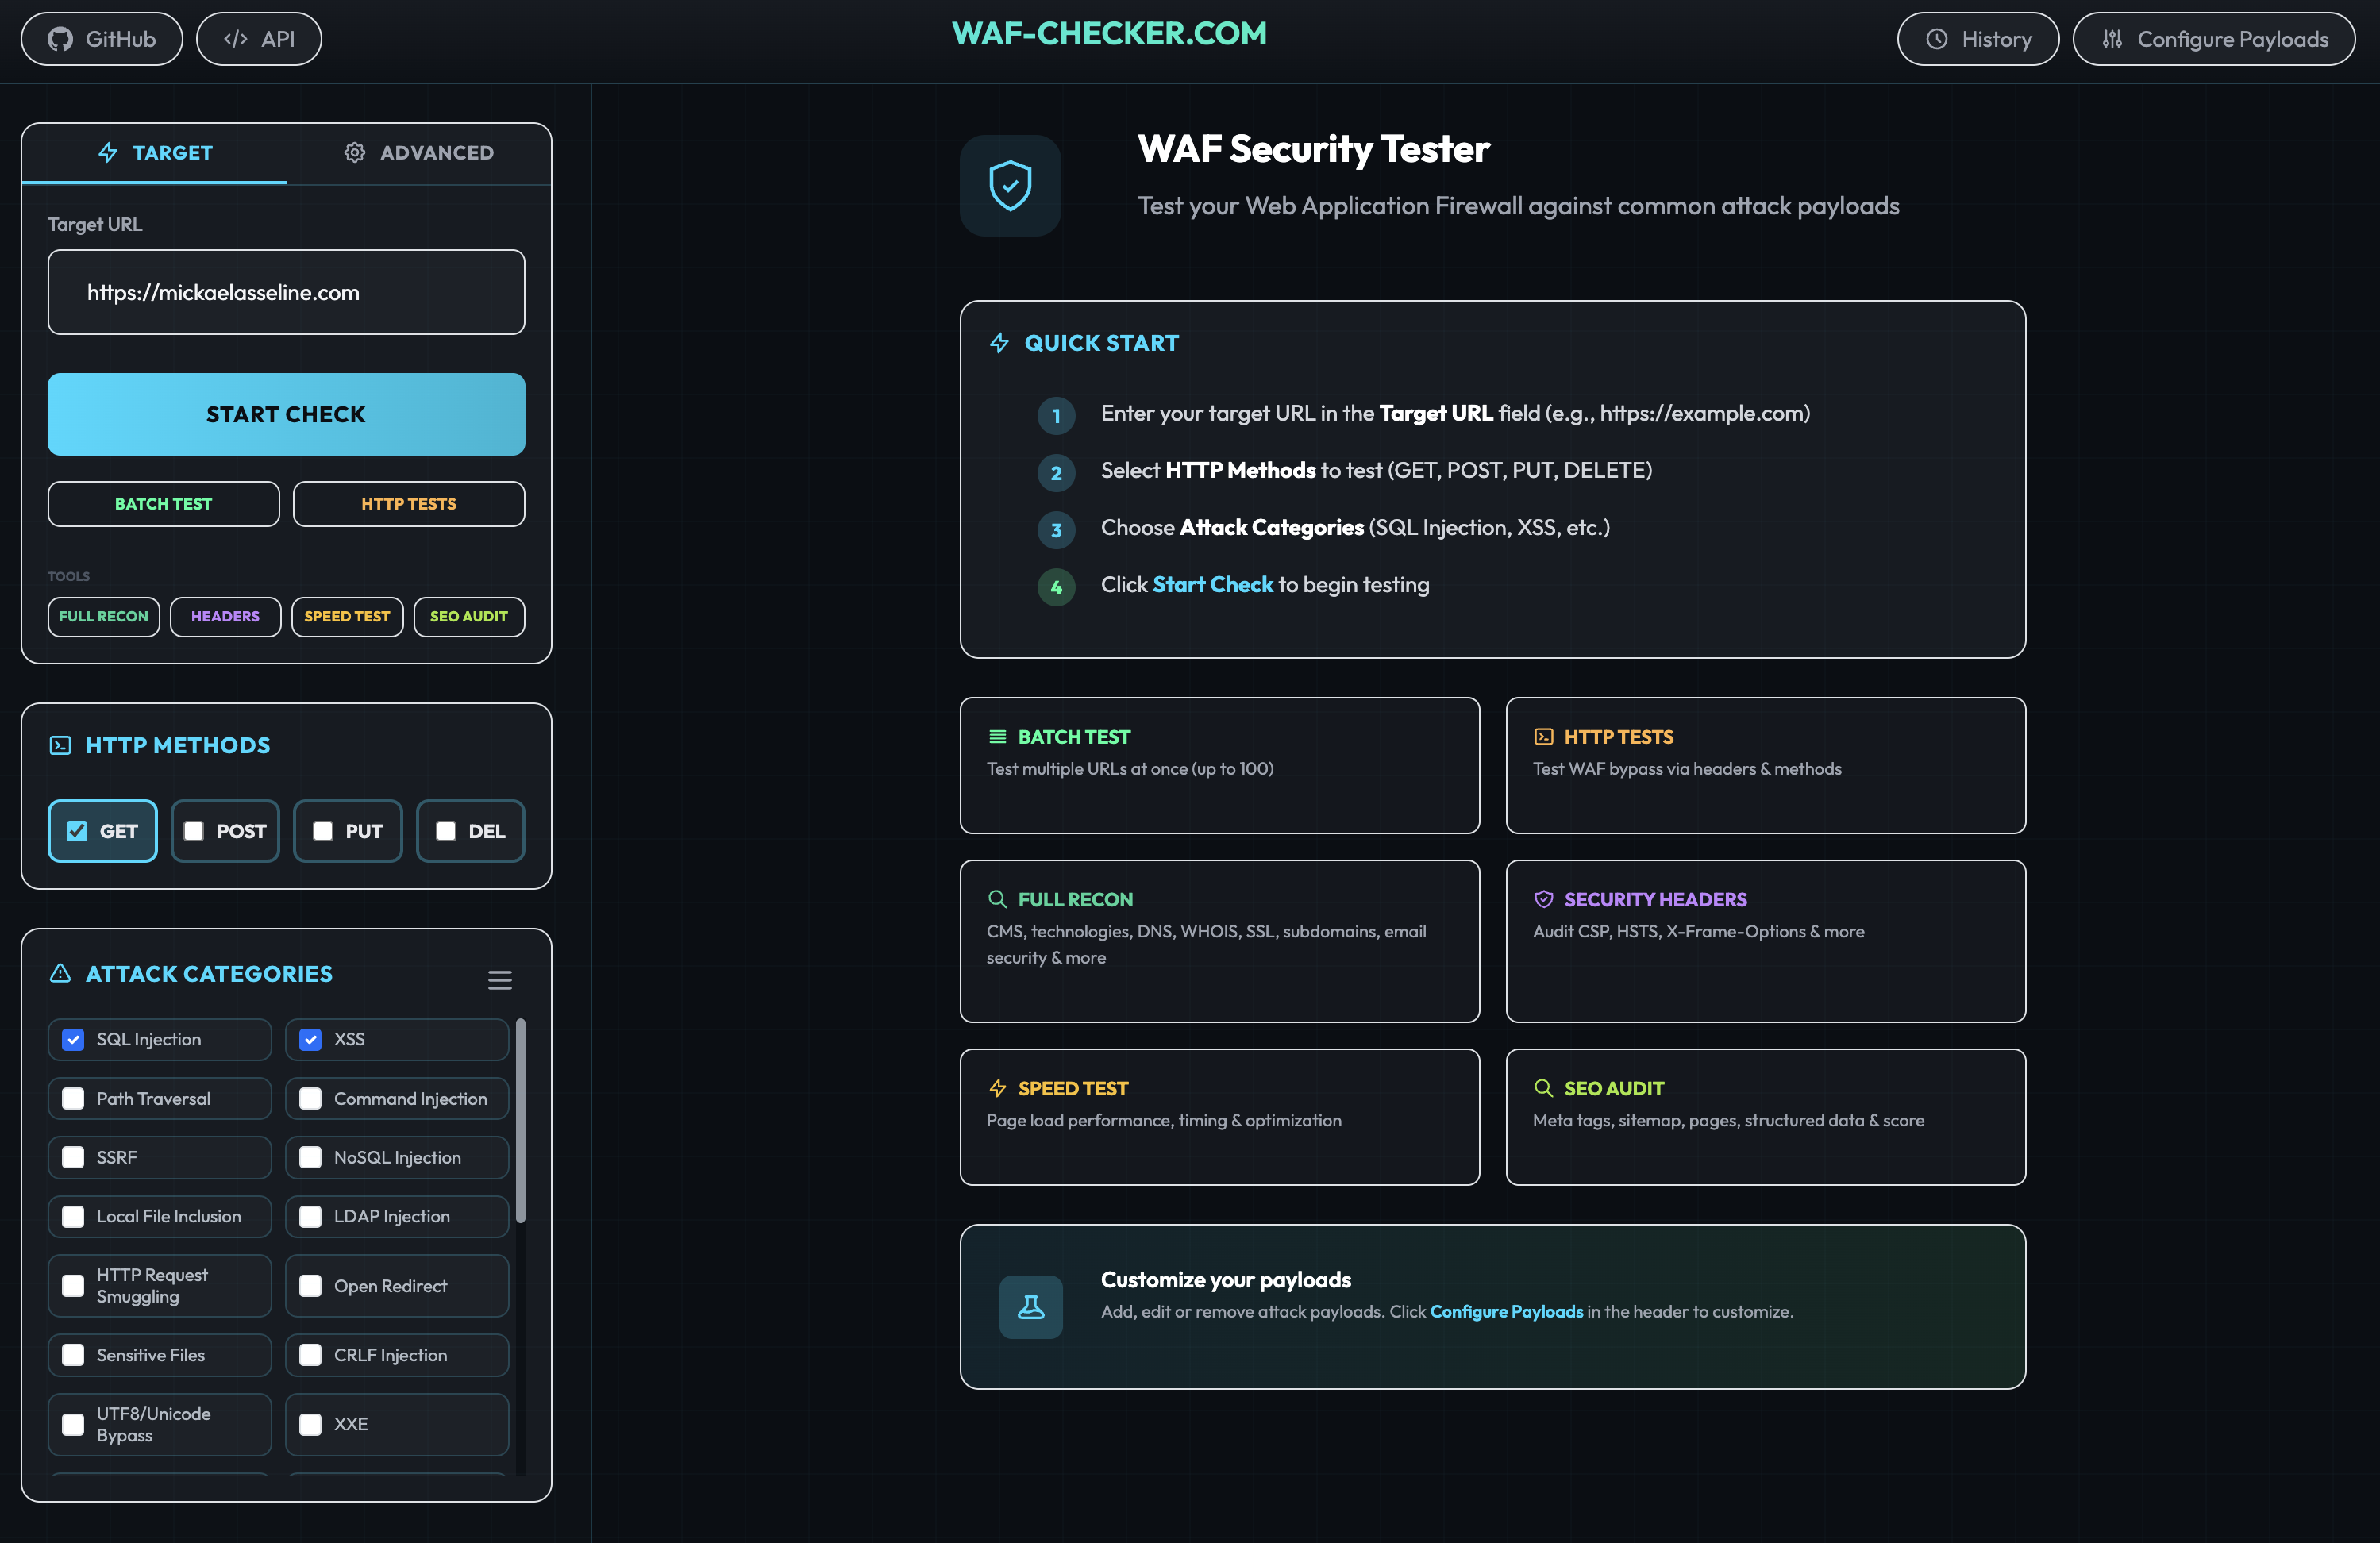 papamica/waf-checker
Tests your WAF with +160 payloads
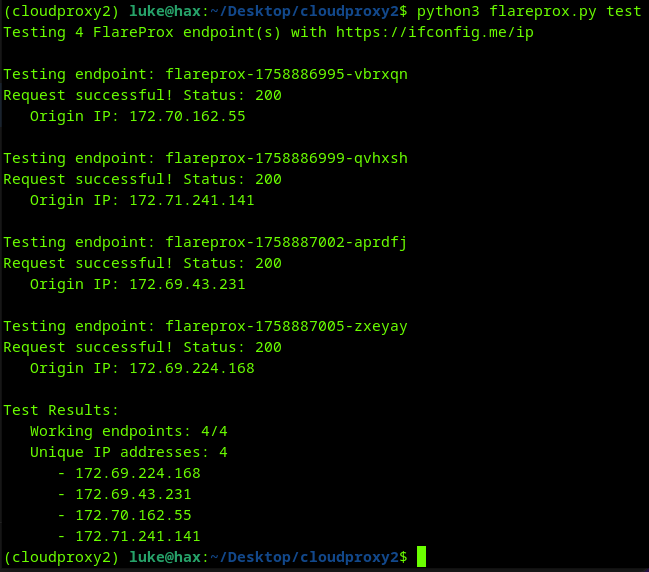 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
 ethicalhackingplayground/ssrf-king
SSRF plugin for burp Automates SSRF Detection in all of the Request

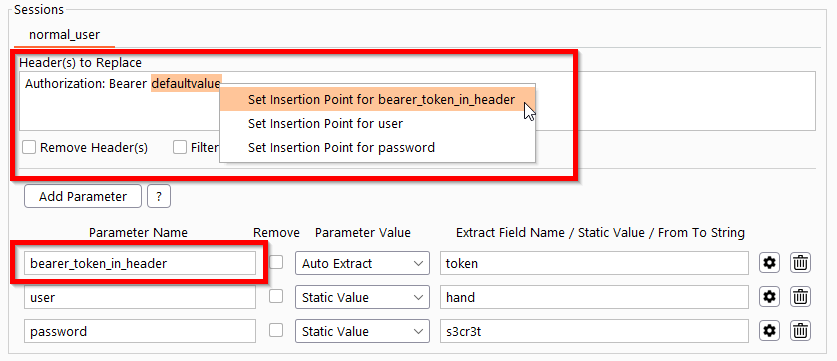 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
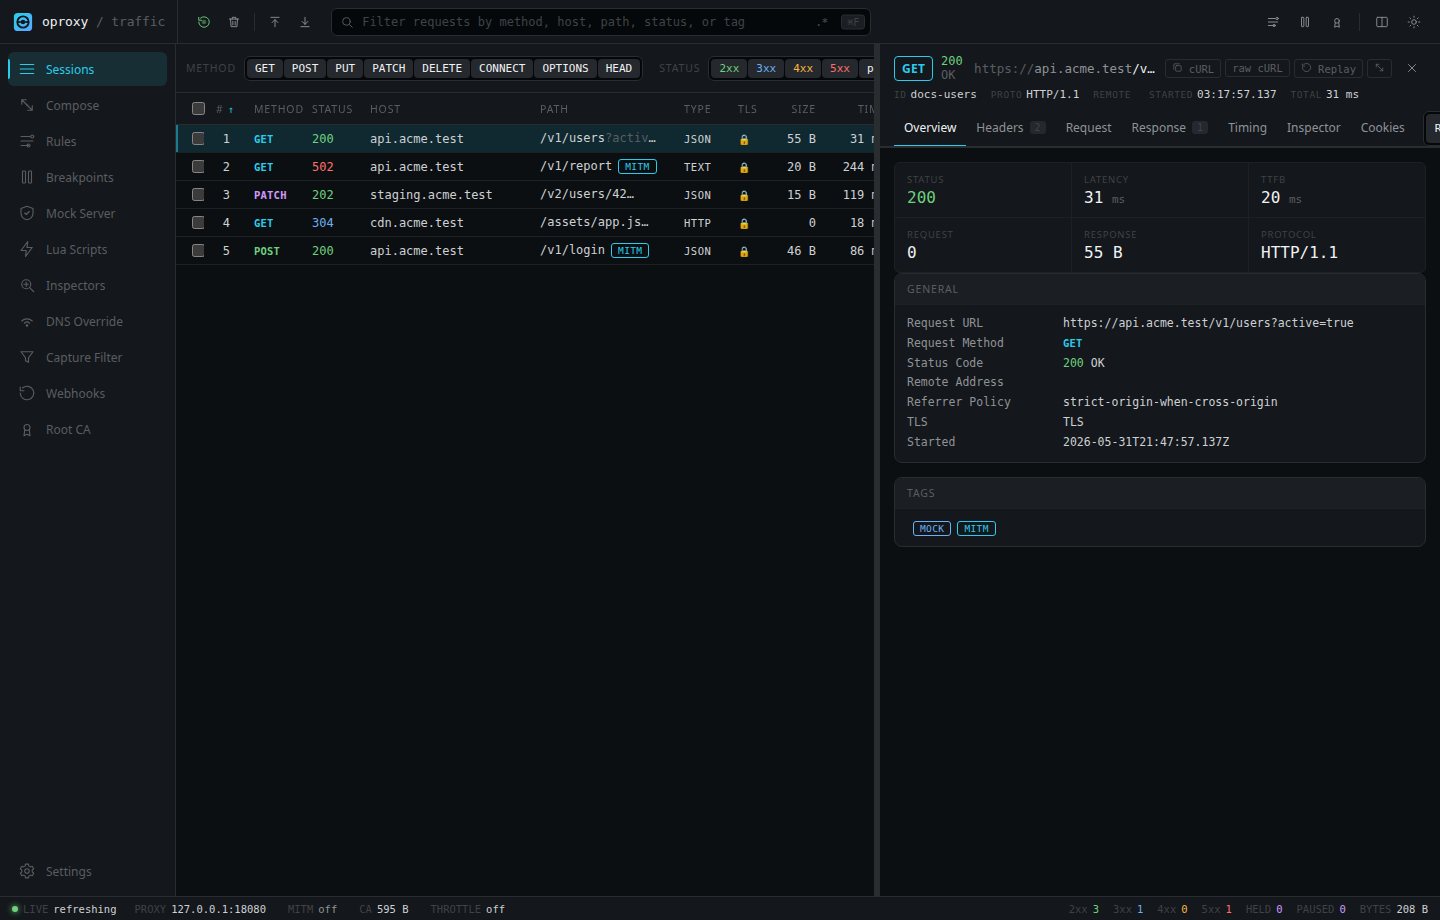 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 assetnote/batchql
GraphQL security auditing script with a focus on performing batch GraphQL queries and mutations
 compasssecurity/samlraider
SAML2 Burp Extension