
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tiredful-API — An intentionally designed broken web application based on REST API. | Kitploit

Tools/GitHubGitHub/payatu/tiredful-api
Web Application ExploitationAPI Security TestingPenetration TestingLearning & EducationLabs & Practice
GitHubpayatu/tiredful-api

Tiredful-API

An intentionally designed broken web application based on REST API.

View Repository
583146766 years agoReviewed by Kitploit
Share

What is Tiredful API?

Tiredful API is intentionally designed broken app. The aim of this web app is to teach developers, QA or security professionals about flaws present in webservices (REST API) due to insecure coding practice.
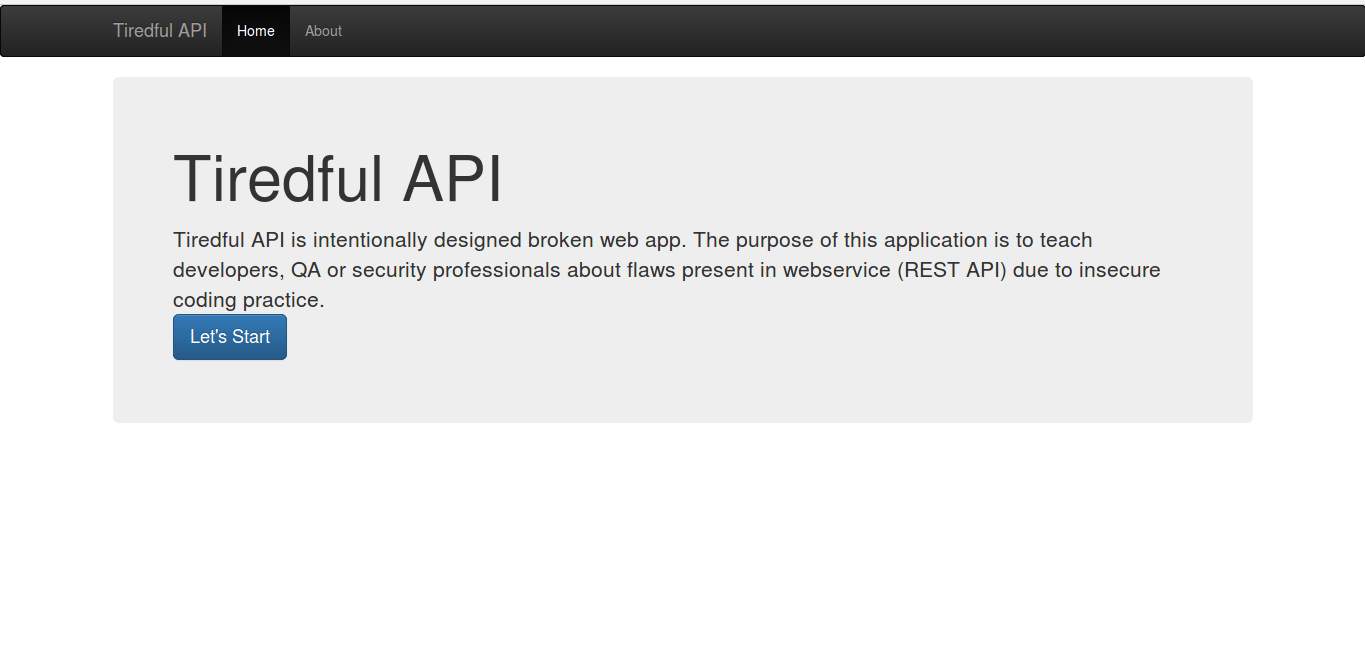
Tiredful API image

Who can use Tiredful API?

  • Web developers
  • Web Pentesters
  • Security Professionals
  • Student

What is included in Tiredful API?

I tried to cover most of the vulnerabilities, I am sure that we have missed some vulnerabilities.Please ping me if you know any good vulnerability that should be included. For now I have included following vulnerabilities.

  • Information Disclosure
  • Insecure Direct Object Reference
  • Access Control
  • Throttling
  • SQL Injection (SQLite)
  • Cross Site Scripting.

You can see solution here

Can I contribute?

Yes, you can help by sending us the details of vulnerabilities that we can implement in future versions of Tiredful API. Please mail us at info[at]payatu.com with subject "Tiredful API Scenario".

Where can I get Tiredful API?

Source can be downloaded from link.

How to run Tiredful API?

Tiredful API is developed using Django Framework and Django Rest Framework, so for running the web server user needs execute following command.

  • Navigate to the source folder and locate manage.py file.
  • Then execute python manage.py runserver.
  • If static files are not getting load, then execute above command with insecure flag i.e. python manage.py runserver --insecure If you are facing any issue starting the web server please refer django documentation admin or django documentation tutorial. Please ping me if you are still not able to run development server.

Note: It is recommended to use required libraries with the version specified in the requirements.txt. Please refer this more details

Docker Container

You can run Tiredful via Docker. Simply execute:

docker build -t tiredful .
docker run -p 8000:8000 --name tiredful -it tiredful

Browse to http://localhost:8000/ and you are all set. Use CTRL-C to shut down the server.

Added new JWT based scenarios. Updated repository available at repo

Python3 Compatible Code

Tiredful API Python3

Feedback and Bug Reports.

We would love to hear from you about your experience with Tiredful API. Please send us an email on info [at] payatu [dot] com or siddharth [dot] bezalwar [at] gmail [dot] com with Subject "Tiredful API Issue" based on what you want to share. Please include the below in your email.

  • Operating system with version.
  • Django Framework used.
  • Steps to replicate issue.

Author

Siddharth Bezalwar

@fattu_medjai | siddharth [dot] bezalwar [at] gmail [dot] com

About Payatu

Payatu is a boutique security testing company with specialization in:

  • IoT Security
  • Mobile Security
  • Cloud security
  • Web Security We also organize two International Security Conferences

nullcon International Security Conference - http://nullcon.net hardwear.io Hardware Security Conference - http://hardwear.io Website: http://payatu.com Email: info (at) payatu dot com


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    500
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    466
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    339
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    317
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    294

Explore all tools

Browse our collection of tools

View all tools →




