

mimikatz
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
authenticationexploitationlateral-movement+5
2.6k
parrotsec/mimikatzTool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 mohuihui/antispy
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
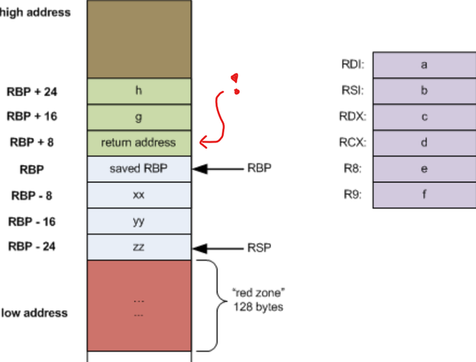 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 vah13/extracttvpasswords
tool to extract passwords from TeamViewer memory using Frida
 netspi/sshkey-grab
Grab ssh keys from ssh-agent
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 anvilsecure/ulexecve
Executes arbitrary ELF binaries directly from memory on Linux without touching disk, enabling stealthy red-teaming and anti-forensic operations via a…
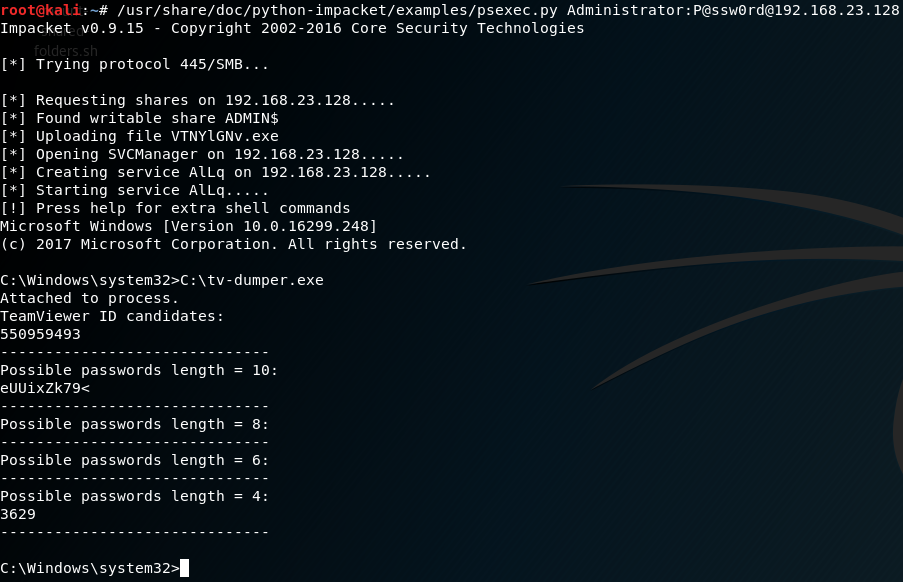 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
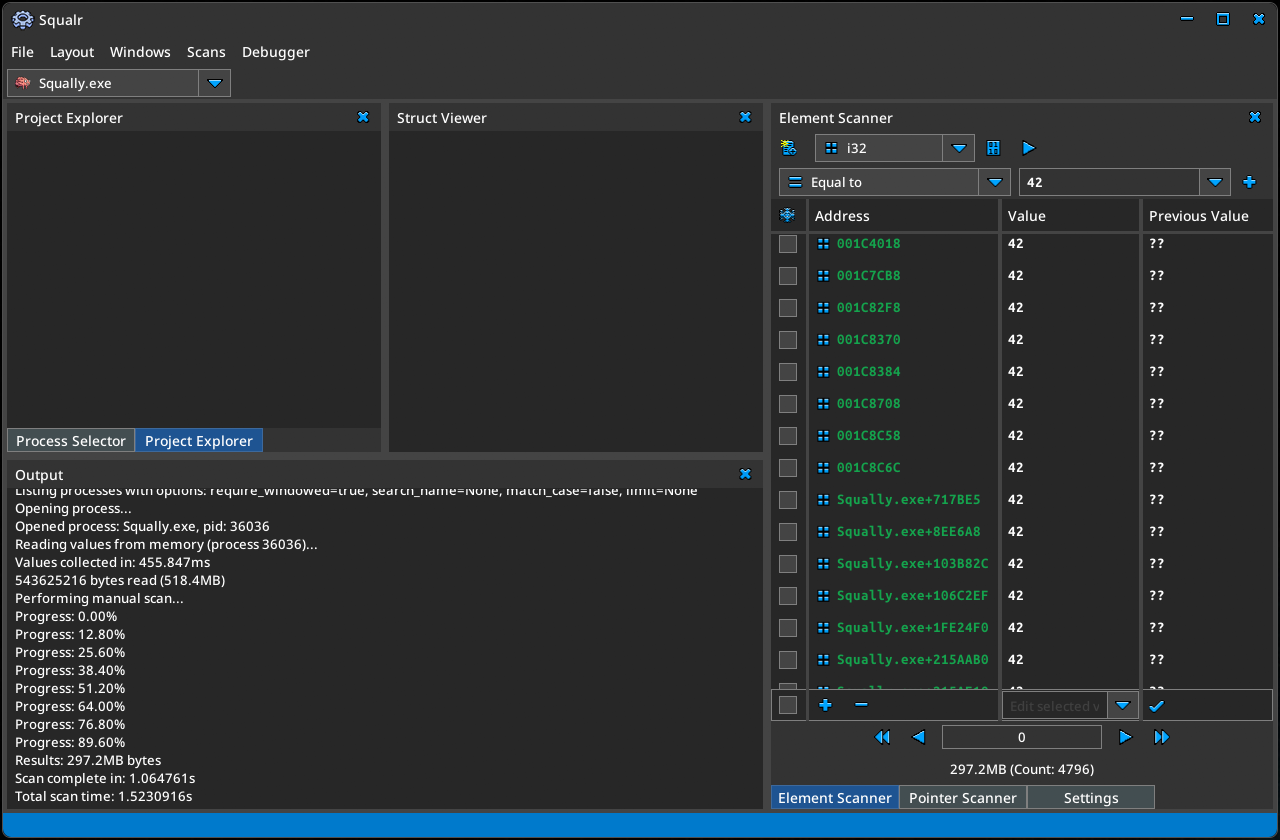 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 andreafortuna/autotimeliner
Automagically extract forensic timeline from volatile memory dump
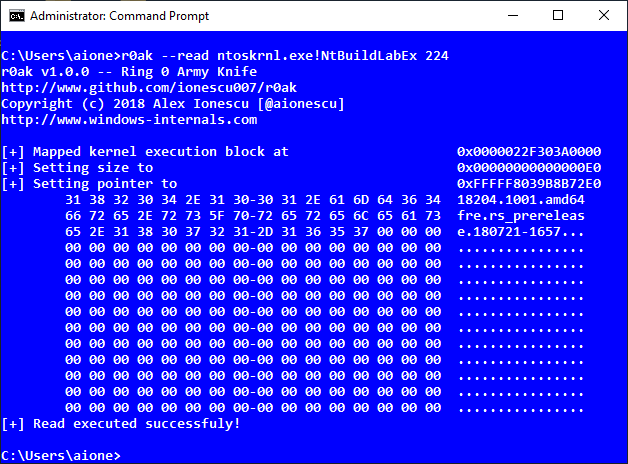 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…