Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
IronPE — Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure for educational research. | Kitploit
Tools/GitHubGitHub/iss4cf0ng/ironpe
Memory ForensicsExploitationReverse EngineeringShellcodeBinary AnalysisLearning & EducationPayload DevelopmentBinary Exploitation
GitHubiss4cf0ng/ironpe

IronPE

Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure for educational research.

12419438 months agoReviewed by Kitploit
Share
View Repository
Website

IronPE - Minimal Windows PE manual loader written in Rust.

Rust PE Loader / Manual Mapping Implementation

status language license Release

IronPE is a minimal Windows PE manual loader written in Rust for both x86 and x64 PE files.

This project is a Rust reimplementation of my previous project dotNetPELoader, which implemented a manual PE loader in C#.

The goal of IronPE is to explore how Windows loads Portable Executables internally and to demonstrate how this process can be implemented in Rust.


Waaaahhhhhhh!

If you find this project useful or informative, a ⭐ would be appreciated!

Disclaimer

This project is intended for educational and research purposes only.

It is designed to help understand:

  • Windows PE internals
  • Manual loading techniques
  • Reverse engineering concepts

Features

  • Manual PE loading
  • Section mapping
  • Base relocations
  • Import resolution
  • Execute PE from memory
  • x86 and x64 PE support

Background

This project was inspired by my previous implementation:

  • dotNetPELoader (C#)

In that project, I implemented a PE loader using .NET and WinAPI.
IronPE rewrites the same concept in Rust, which provides better memory safety while still allowing low-level Windows API access.

The purpose of this project is educational, to better understand:

  • PE file structure
  • Windows loader behavior
  • Manual PE mapping techniques

How It Works

IronPE performs the following steps to execute a PE file from memory:

  1. Read PE file into memory
  2. Parse PE headers
  3. Allocate memory using VirtualAlloc
  4. Copy PE headers and sections
  5. Apply base relocations
  6. Resolve imports using LoadLibrary and GetProcAddress
  7. Transfer execution to the Original Entry Point (OEP)

This process mimics the behavior of the Windows PE loader.

An x64 PE cannot be loaded by an x86 loader, and vice versa.

Build

Requirements:

  • Rust (cargo, rustc)
  • Windows

Build the project:

cd IronPE
build.bat

Usage

IronPE.exe --coffee
IronPE.exe --x86 <x86_pe_file>
IronPE.exe --x64 <x64_pe_file>

Example:

IronPE.exe --x86 Win32\mimikatz.exe
IronPE.exe --x64 x64\mimikatz.exe
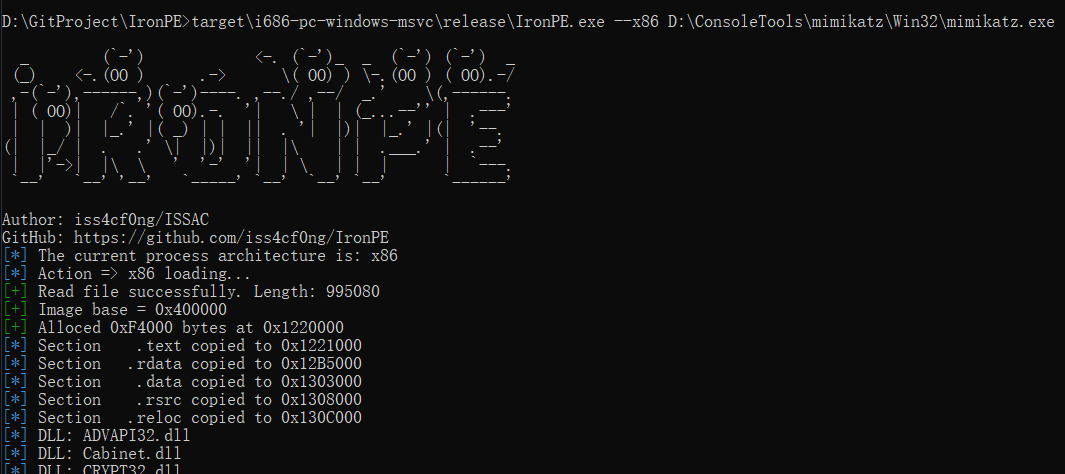
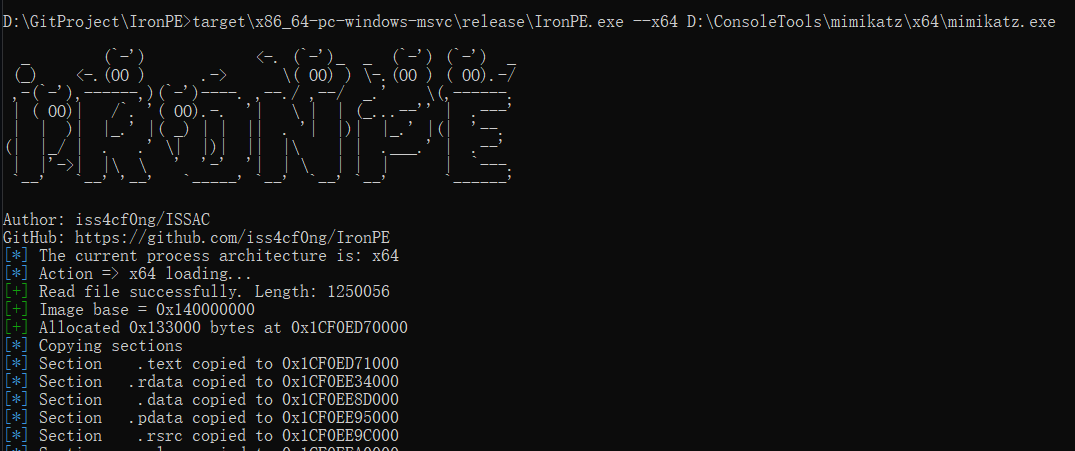
Demo (Running mimikatz)

x86


x64


Unmatched Loader and PE Architecture (Error)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →