
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/idov31/etwleakkernel
ReconnaissanceMemory ForensicsExploitationInformation GatheringBinary Exploitation
GitHubidov31/etwleakkernel

EtwLeakKernel

Leaking kernel addresses from ETW consumers. Requires Administrator privileges.

View Repository
9410331 year agoReviewed by Kitploit
Share

EtwLeakKernel

This repository contains a PoC for a program that utilizes ETW to leak kernel memory addresses. It does so by creating a consumer (could be to almost any provider as almost all of them leak kernel addresses) and requesting a stack trace from it. Once the stack trace is received, it is parsed to extract the kernel memory addresses. Since Microsoft do not consider administrator to kernel as a security boundary, this situation won't change any time soon. Might be useful in some exploitation scenarios (e.g. wanting to leak the kernel base address if you know that an ETW provider leaks a kernel address which is in a certain offset from the kernel base address or any other interesting address for that matter) or just as a party trick.

Bare in mind that administrative privileges are required to start consuming from ETW providers. If there is already a program that consumes ETW events that normal user has access to the trace, the normal user will be able to leak kernel addresses as well. It does not provide any leak of actual kernel data, just kernel addresses (unless in maybe an extreme edge cases).
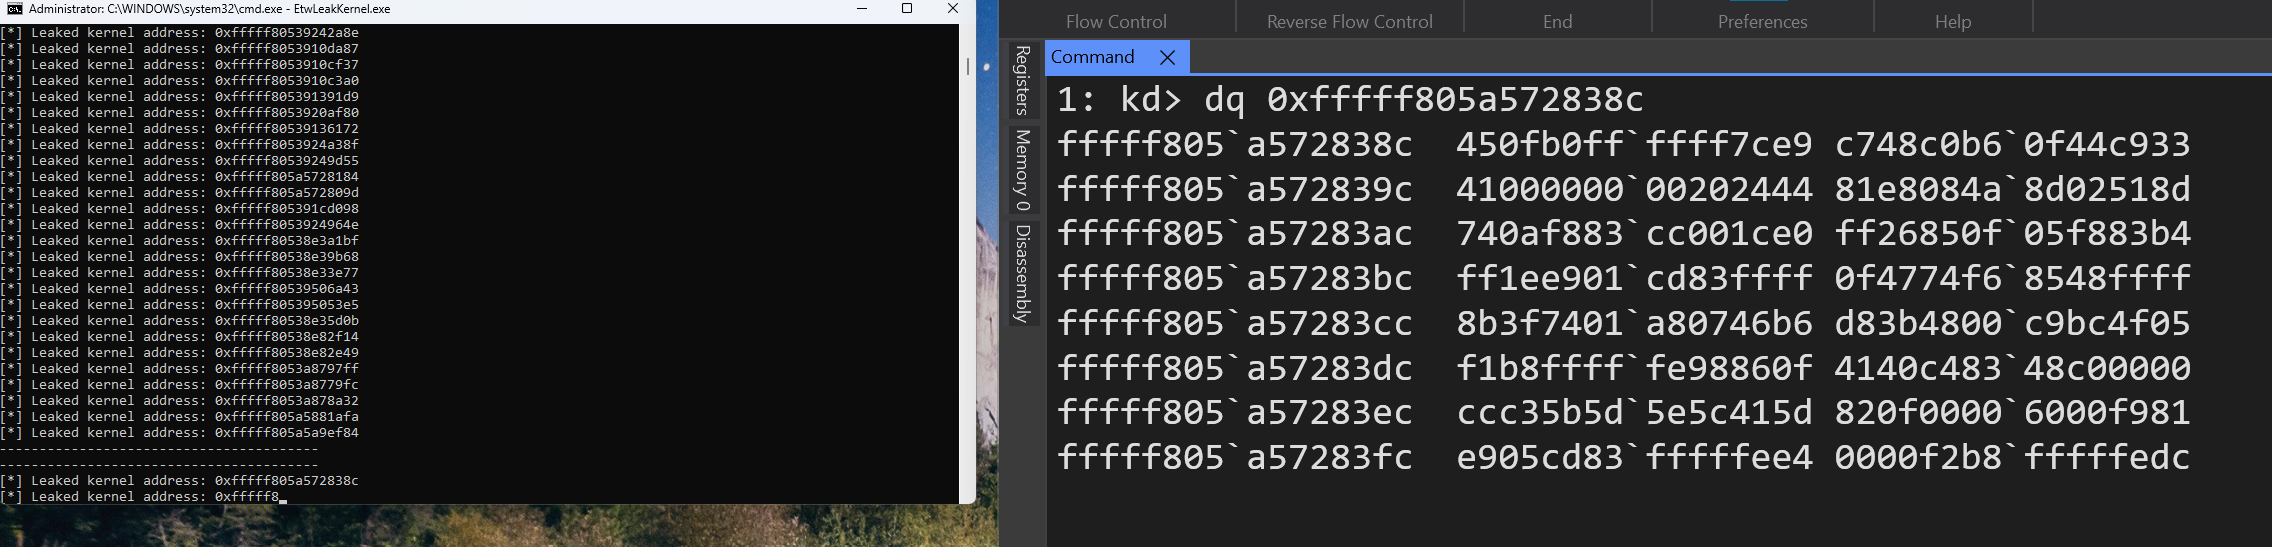
poc

Usage

You can see an example of how to use in EtwLeakKernel. You can also use any other ETW consumer and request the stack, in this example it is using Microsoft-Windows-Kernel-Network.

Setup

Requirements

  • VS 2022

Cloning

git clone https://github.com/Idov31/EtwLeakKernel --recursive

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →





