Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
wmi-static-spoofer — Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking | Kitploit

Tools/GitHubGitHub/alex3434/wmi-static-spoofer
Privilege EscalationMemory ForensicsPersistence MechanismsExploitationHardware HackingHardware SecurityHardware & IoT Security
GitHubalex3434/wmi-static-spoofer

wmi-static-spoofer

Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking

View Repository
508139927 years agoReviewed by Kitploit
Share

wmi-static-spoofer

Motivation:

The initial motivation is bypassing HWID detection methods used by intrusive software like anti-cheats, etc. or licensing restrictions implemented in software. The concept is not new but other solutions require a loaded driver at all times and a kernel hook with possible instabilities. This project only uses direct memory manipulation and makes it possible to fake the serials without hooking a function or having a loaded kernel module at all times.

Description:

Fakes the serialnumber for HDDs/diskdrives from kernelmode without hooking anything. The driver can be fully unloaded after changing the serialnumber.

  • It's more like a PoC, there are many things to optimise
  • It generates a random serial with a fixed length that can be changed in the main.h file
  • The offsets for the spoofer can also be changed in the main.h file
  • This does NOT counter all the ways for getting the serialnumber! I will make a writeup on that later.
  • It also changes the registry entries to the faked serial via a internal kernel function

Pictures:

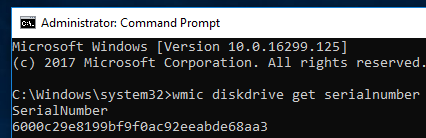
Before:

After:

Supported/Testing:

Only tested on Windows 10 16299.125
For testing purposes add: disk.EnableUUID="true" to your VMware .vmx file to enable serialnumbers


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →