Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
149 results
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
11.9k5 days ago
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
19026 days ago
chisel preview

chisel

GitHubjpillora/chisel

Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…

command-and-controldata-exfiltrationgeneral-purpose-utilities+8
16.6k24 days ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k17 days ago
awesome-pentest preview

awesome-pentest

GitHubenaqx/awesome-pentest

A collection of awesome penetration testing resources and tools
cloud-securityctfcurated-resources+10
27.3k2 months ago
Hollow preview

Hollow

GitHubchaelsoo/hollow

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
binary-exploitationencryption-decryption-toolsexploitation+7
1022 months ago
OffensiveRust preview

OffensiveRust

GitHubtrickster0/offensiverust

Rust Weaponization for Red Team Engagements.
binary-exploitationcommand-and-controleducation+9
3.0k3 years ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
2.6k4 years ago
OSRipper preview

OSRipper

GitHubnoahoksuz/osripper

AV evading cross platform Backdoor and Crypter Framework with a integrated lightweight webUI
command-and-controleducationexploit-frameworks+5
3337 months ago
mora-hwbp preview

mora-hwbp

GitHubdovughs/mora-hwbp

Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).

adversarial-attackdebuggersdefensive-tools+3
182 days ago
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
command-and-controldatabase-securitydata-exfiltration+20
39.1k1 day ago
IfritProxy preview

IfritProxy

GitHub0tsystemspublicrepos/ifritproxy

IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate…

ai-securitydefensive-toolsids-ips-evasion+7
18 months ago
DcRat preview
Archived

DcRat

GitHubqwqdanchun/dcrat

A simple remote tool in C#.
command-and-controldata-exfiltrationids-ips-evasion+9
1.0k4 years ago
CyberDefense-Lab preview

CyberDefense-Lab

GitHubumidguluzada/cyberdefense-lab

A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
educationids-ips-evasionintrusion-detection+5
61 month ago
ExtensionSpoofer preview

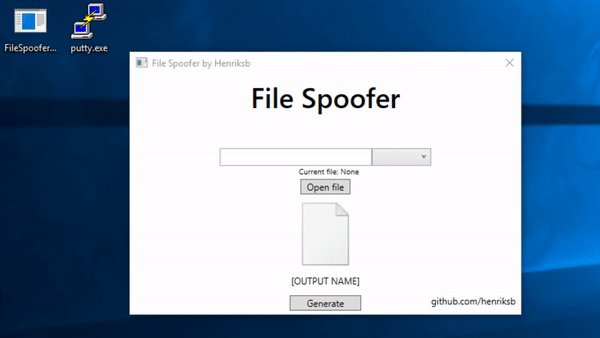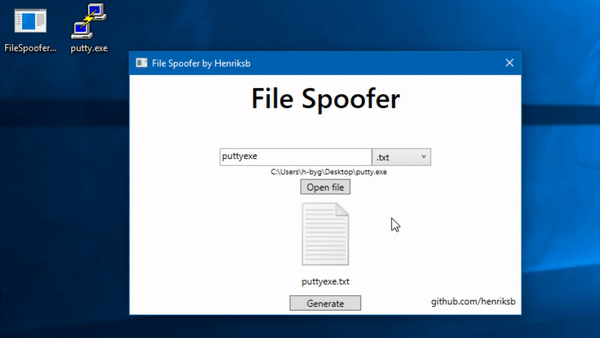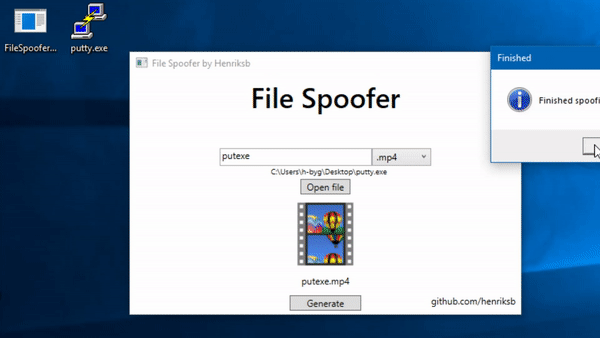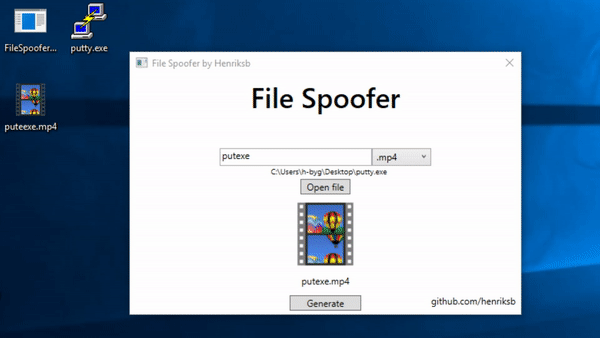
ExtensionSpoofer

GitHubhenriksb/extensionspoofer

Spoof file icons and extensions in Windows

ids-ips-evasionimpersonation-toolsmalware-analysis+3
1871 month ago
voidsyscall preview

voidsyscall

GitHubvoidsecsoftwares/voidsyscall

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
5714 days ago
thorse preview

thorse

GitHubpushpenderindia/thorse

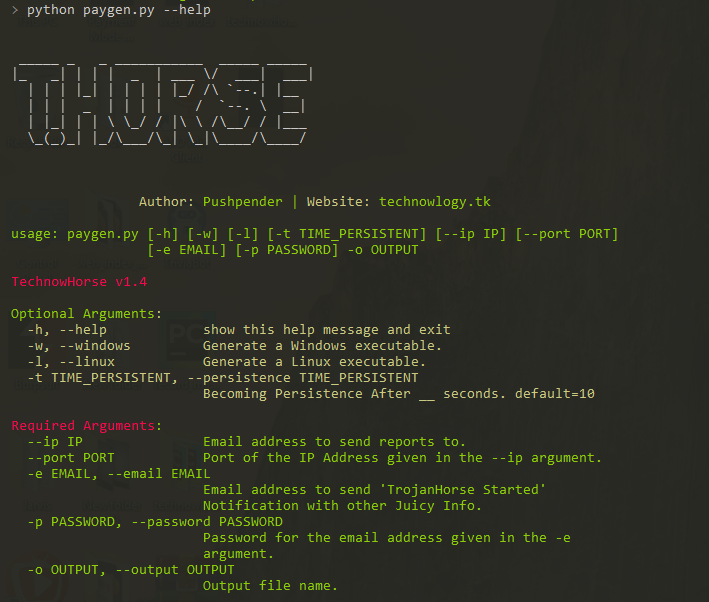
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
anti-botcommand-and-controlexploit-frameworks+6
6143 years ago
Nodejs-Tracer preview

Nodejs-Tracer

GitHubcheckpointsw/nodejs-tracer

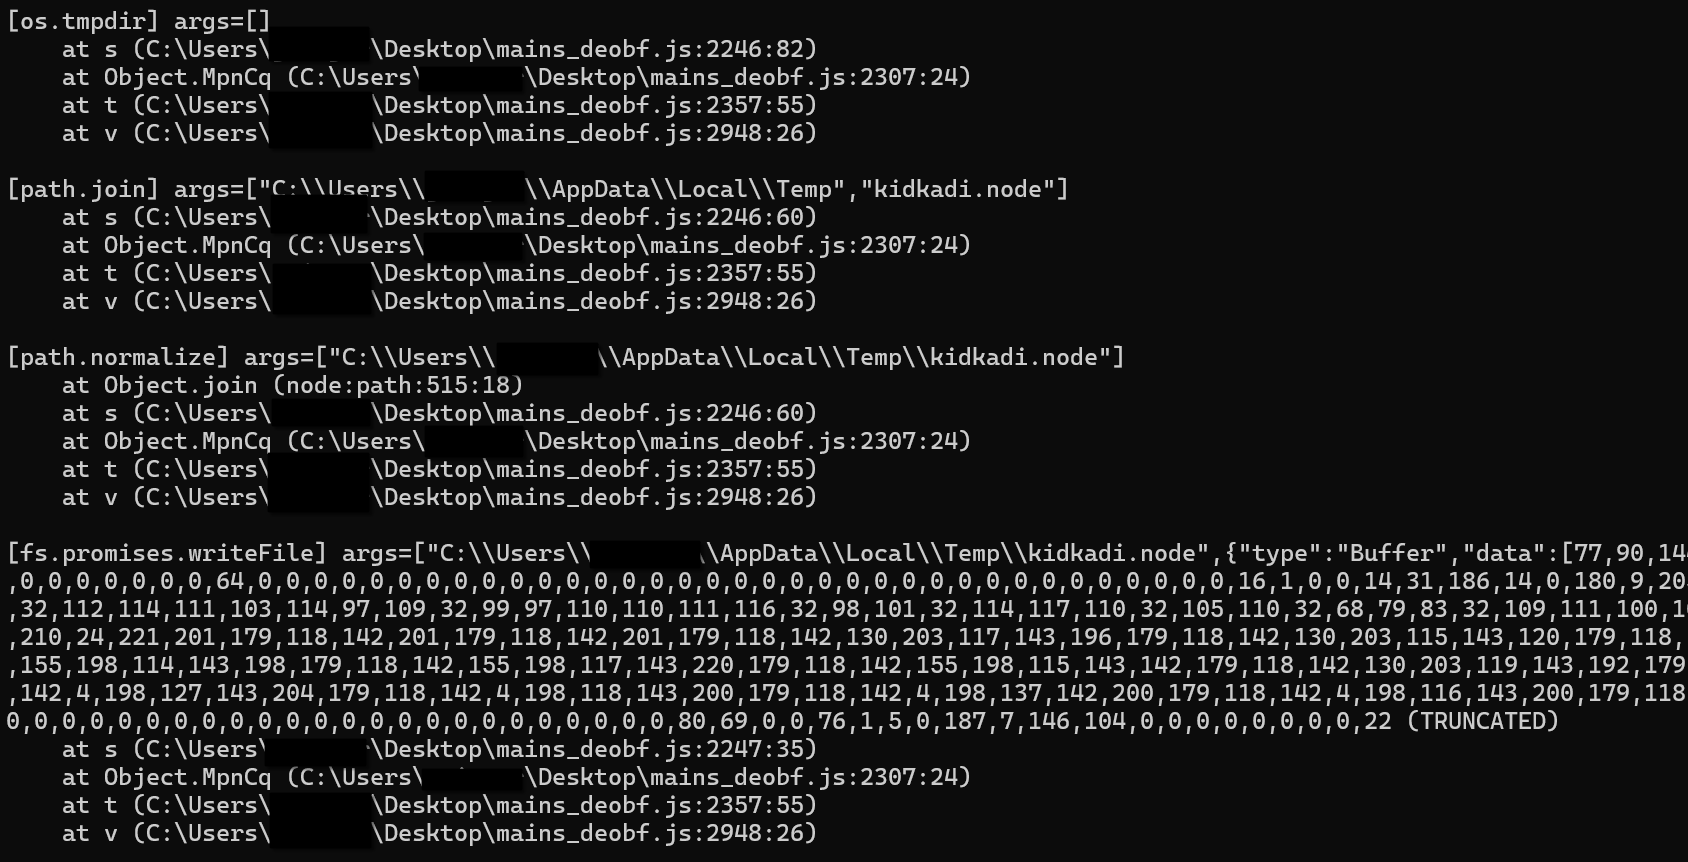
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…

anti-botdynamic-analysis-sandboxingids-ips-evasion+3
818 months ago
Previous12…9Next