 0tsystemspublicrepos/ifritproxy

IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate traffic is forwarded to backend; malicious traffic receives a customized AI-generated honeypot response that mimics the requested resource with fabricated data, deceiving attackers into wasting time on it.
Turn attackers into intelligence sources with adaptive honeypot responses

📦 Quick Start • ✨ Features • 🔄 How It Works • 📚 Docs • 🔌 API
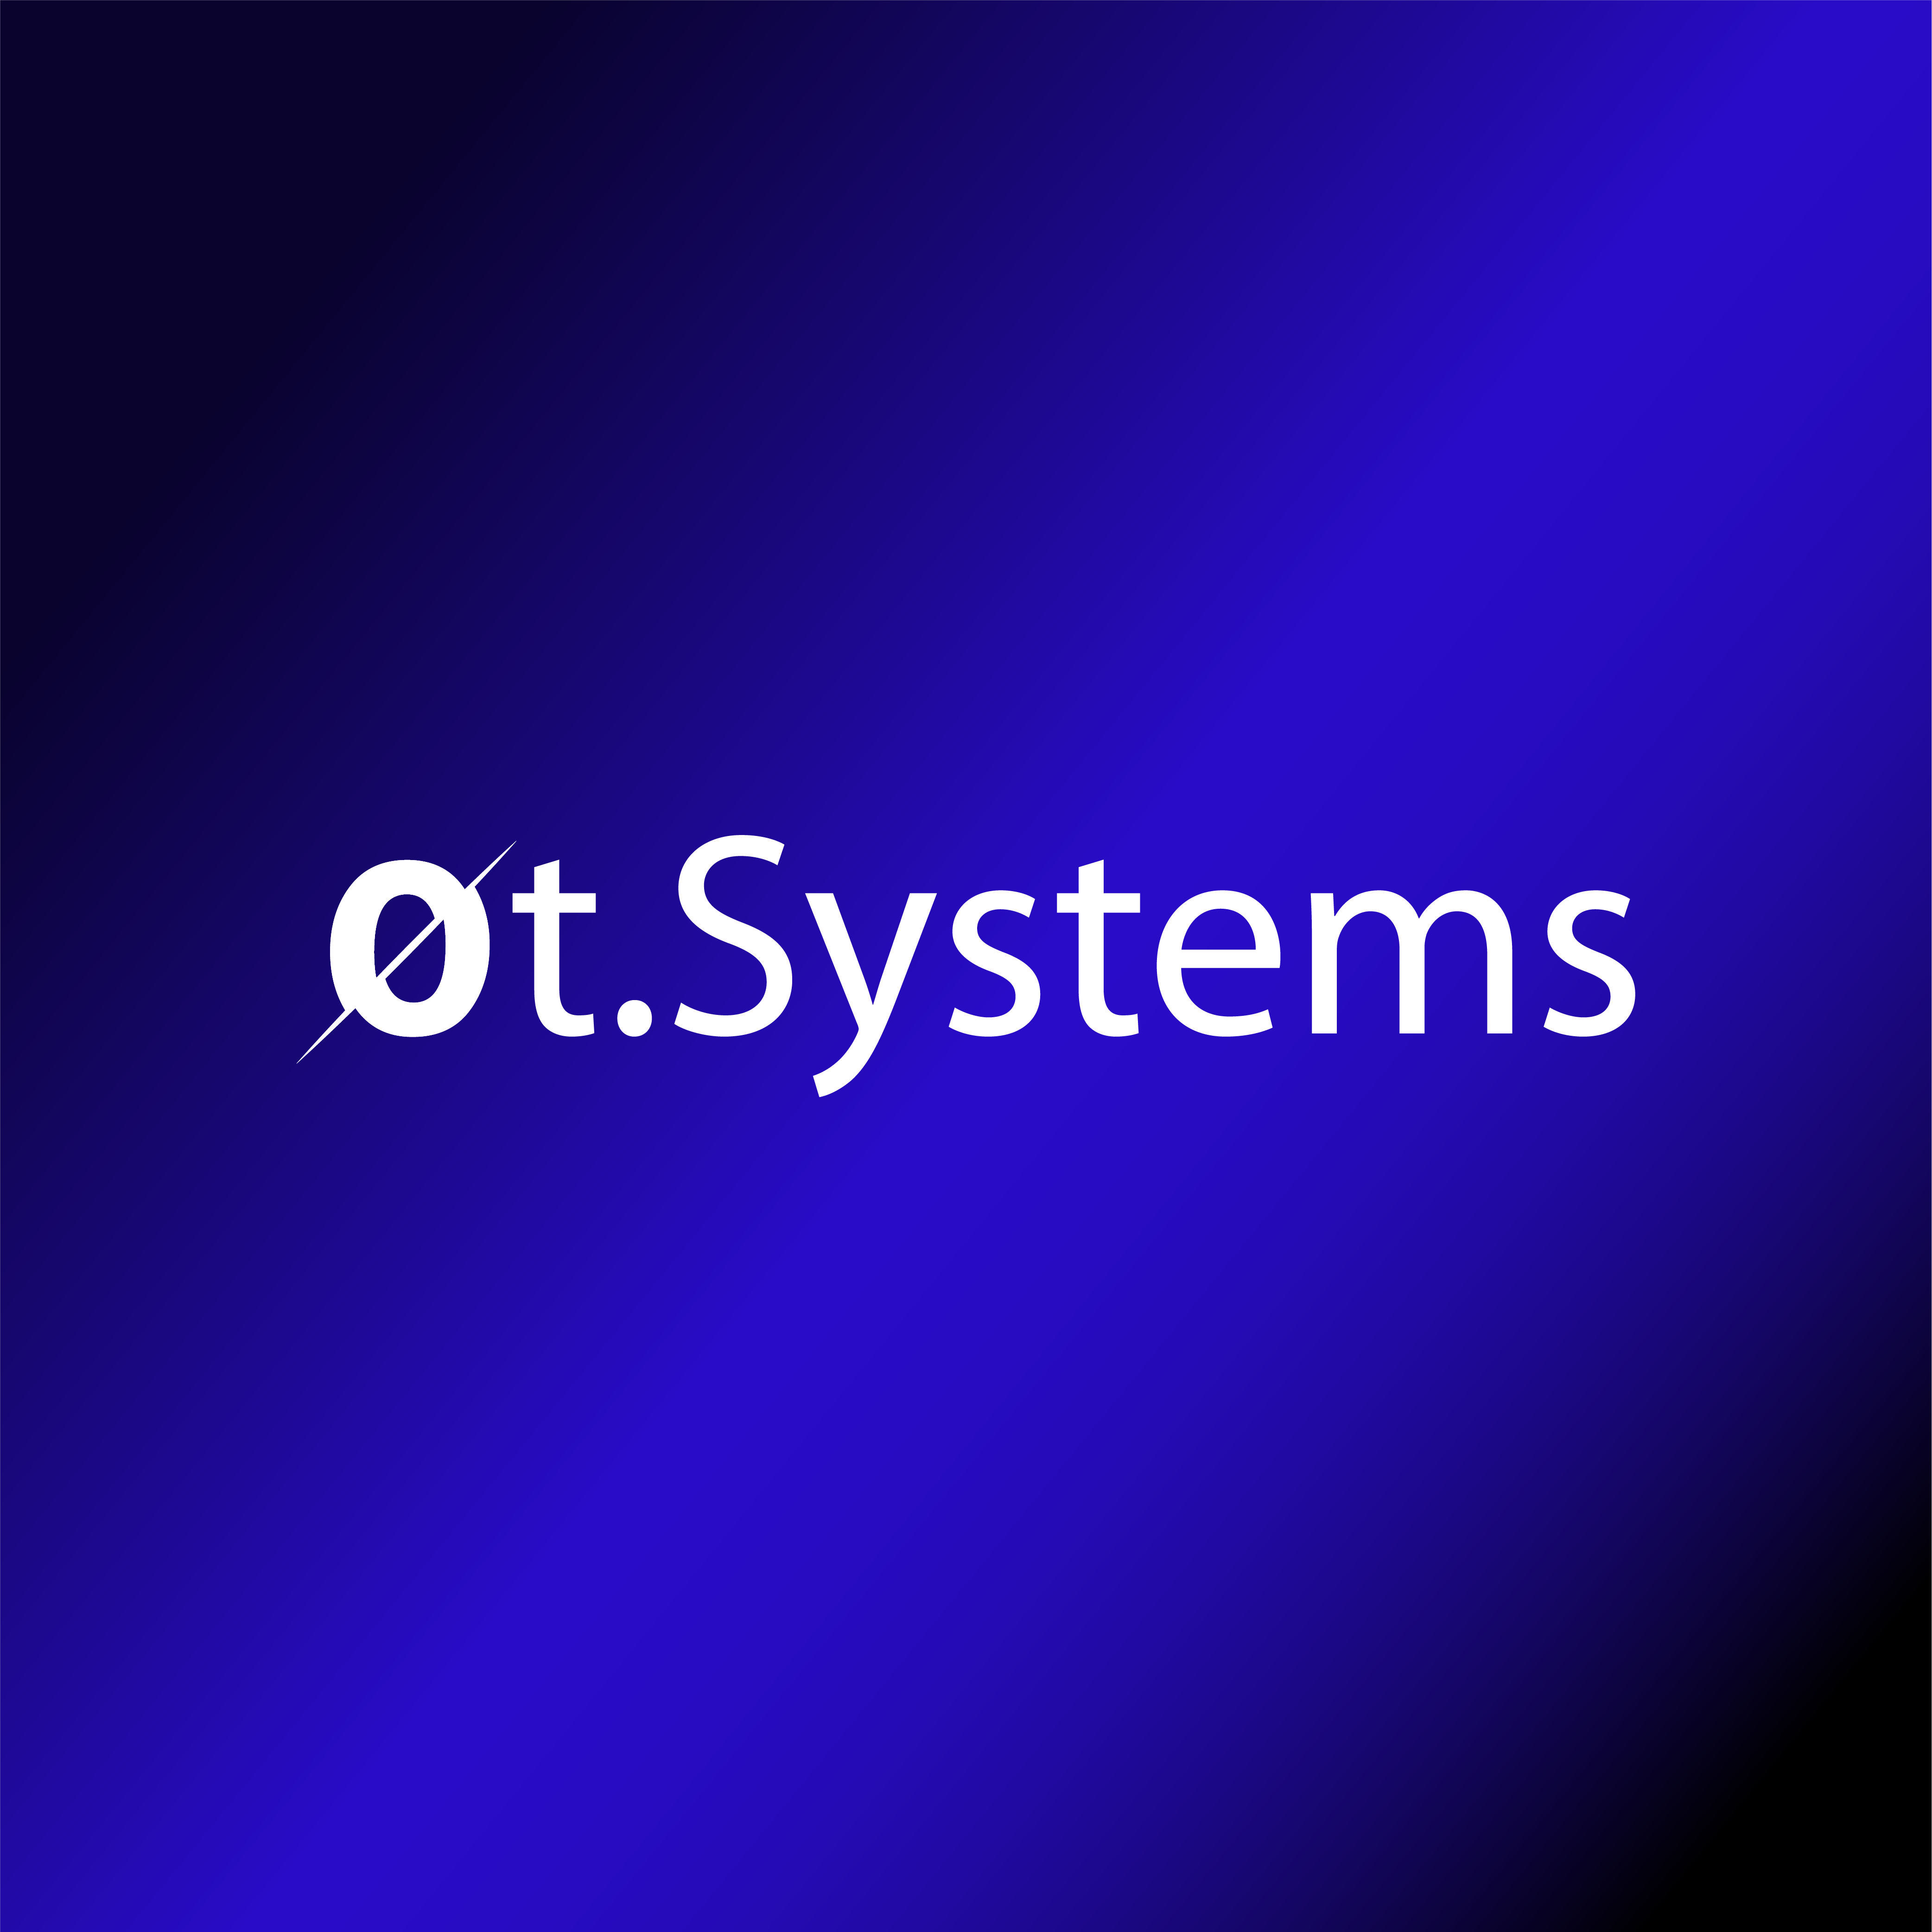
IFRIT is an intelligent reverse proxy that sits between the internet and your applications, analyzing every request in real-time. Legitimate traffic flows through seamlessly. Malicious traffic? It gets served AI-generated honeypot responses that waste attackers' time while you gather intelligence.
graph TB
    subgraph Internet
        A[👤 Attacker]
        L[✅ Legitimate User]
    end

    subgraph "IFRIT Proxy Layer"
        B[🛡️ IFRIT Proxy]

        subgraph "AI Detection Engine"
            C1[🤖 Claude Sonnet 4]
            C2[🤖 Gemini 2.0 Flash]
        end

        subgraph "Threat Intelligence"
            D1[📊 AbuseIPDB]
            D2[🦠 VirusTotal]
            D3[🌍 IPInfo]
        end
    end

    subgraph Backend
        E[🎯 Your Application]
    end

    subgraph "Attacker Receives"
        F[🍯 Fake Data<br/>Honeypot Response]
    end

    subgraph "User Receives"
        G[📦 Real Data<br/>Protected]
    end

    A -->|Malicious Request| B
    L -->|Normal Request| B

    B --> C1
    B --> C2

    B --> D1
    B --> D2
    B --> D3

    B -->|Attack Detected| F
    B -->|Legitimate| E
    E -->|Response| G

    F -.->|Wasted Time| A
    G -->|Secure Access| L

    style A fill:#ff6b6b,stroke:#c92a2a,stroke-width:2px,color:#fff
    style L fill:#51cf66,stroke:#2f9e44,stroke-width:2px,color:#fff
    style B fill:#4c6ef5,stroke:#364fc7,stroke-width:3px,color:#fff
    style C1 fill:#845ef7,stroke:#5f3dc4,stroke-width:2px,color:#fff
    style C2 fill:#845ef7,stroke:#5f3dc4,stroke-width:2px,color:#fff
    style D1 fill:#ff922b,stroke:#e8590c,stroke-width:2px,color:#fff
    style D2 fill:#ff922b,stroke:#e8590c,stroke-width:2px,color:#fff
    style D3 fill:#ff922b,stroke:#e8590c,stroke-width:2px,color:#fff
    style E fill:#20c997,stroke:#12b886,stroke-width:2px,color:#fff
    style F fill:#fa5252,stroke:#c92a2a,stroke-width:2px,color:#fff
    style G fill:#51cf66,stroke:#2f9e44,stroke-width:2px,color:#fff
Simplified flow:
Get up and running in under 2 minutes
|
macOS (Apple Silicon) |
Linux (x64) |
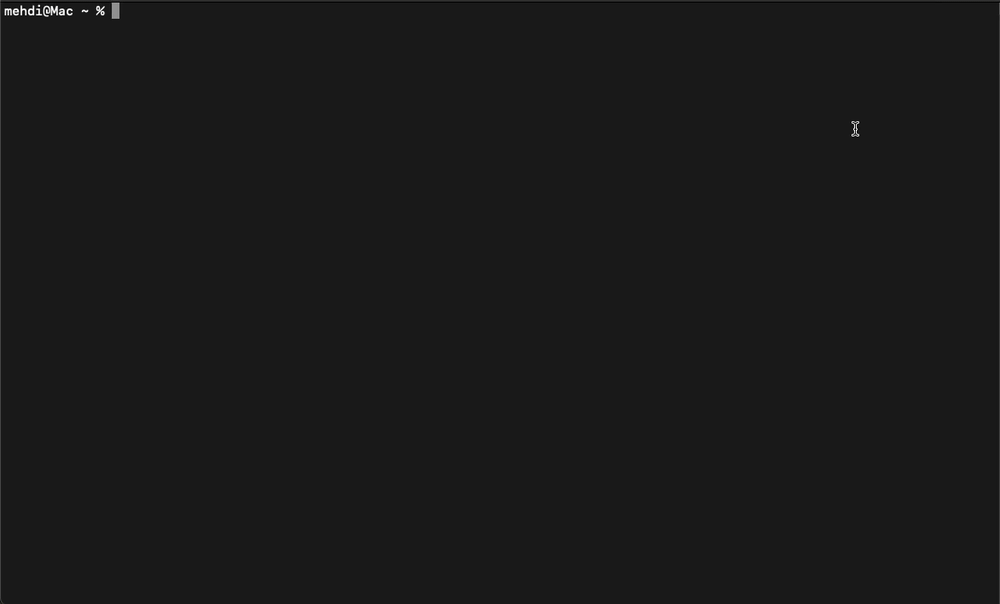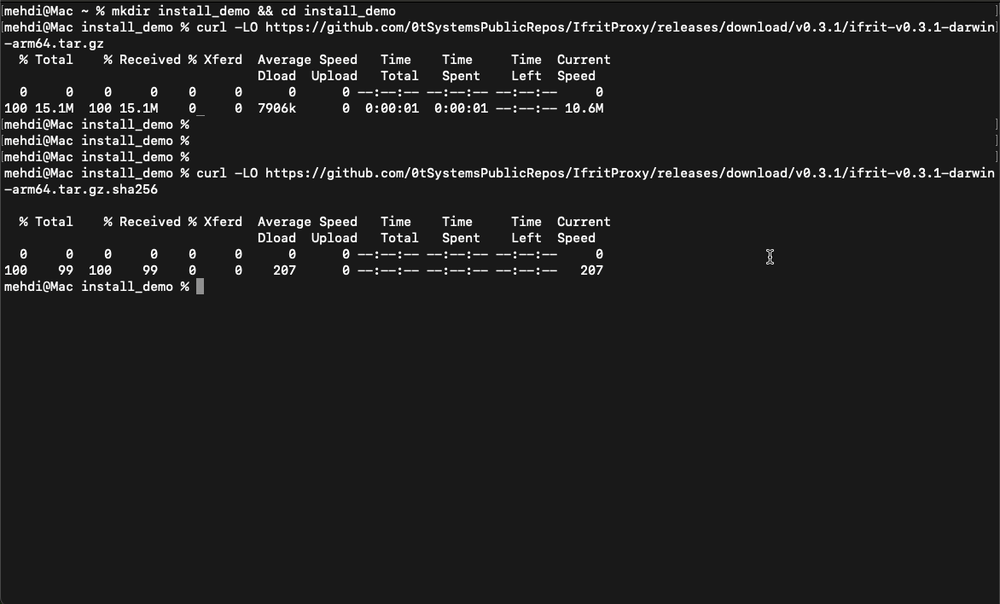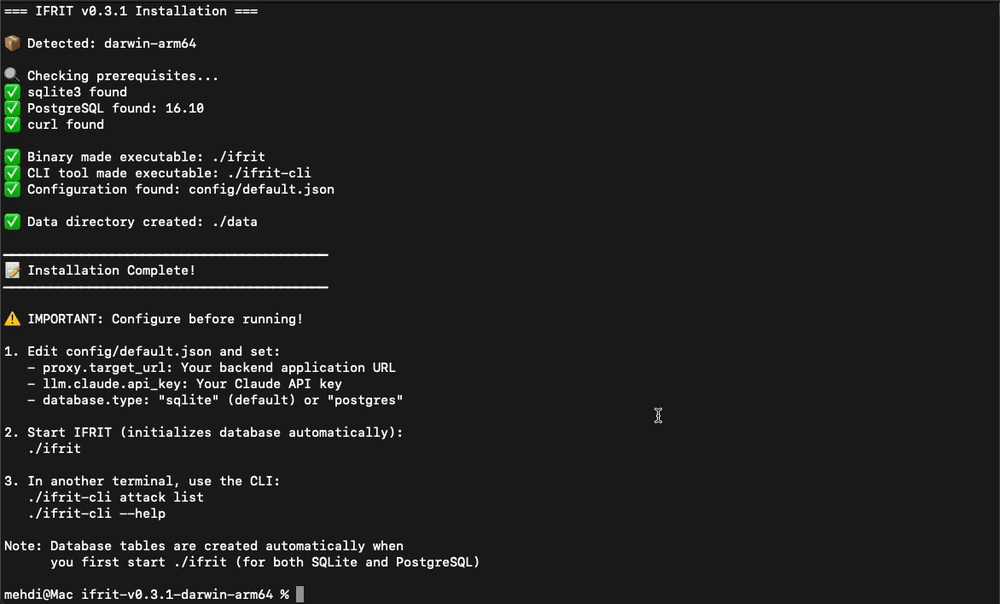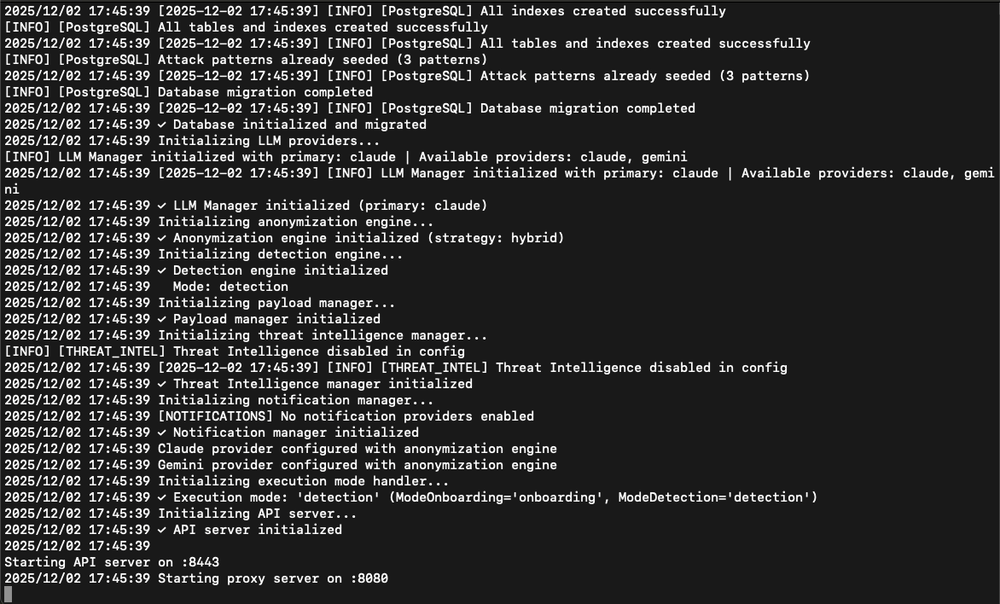
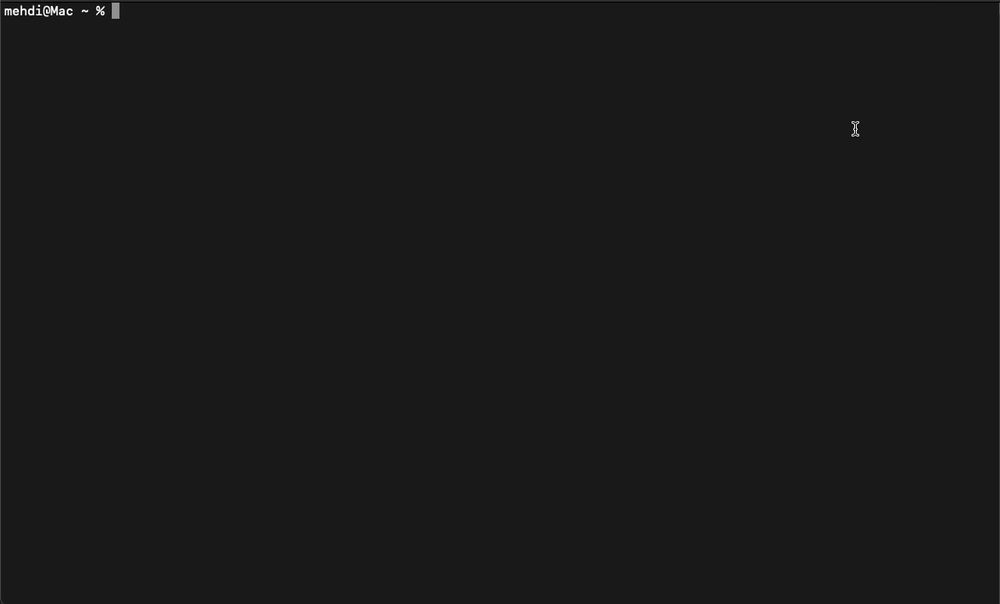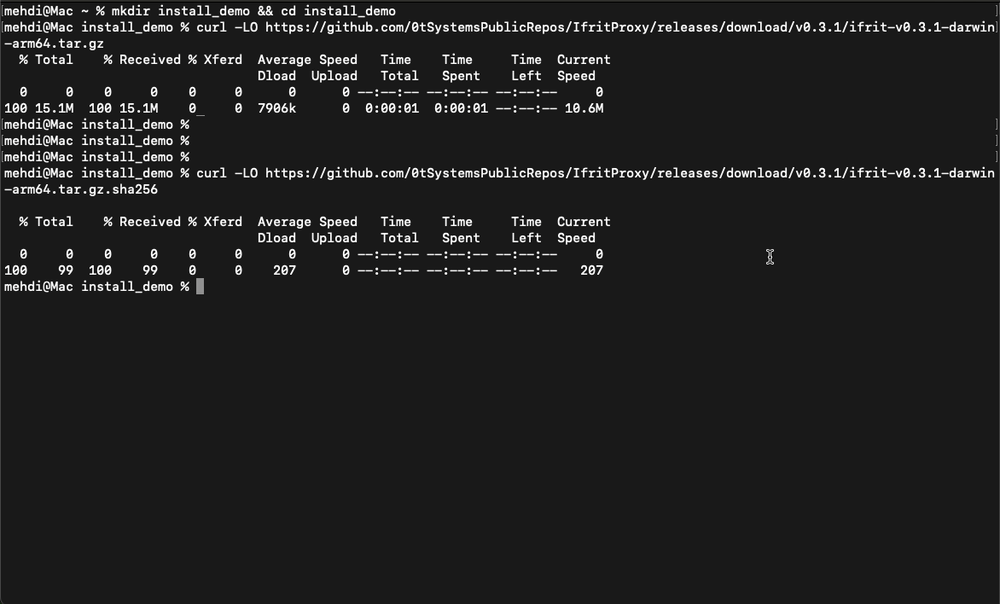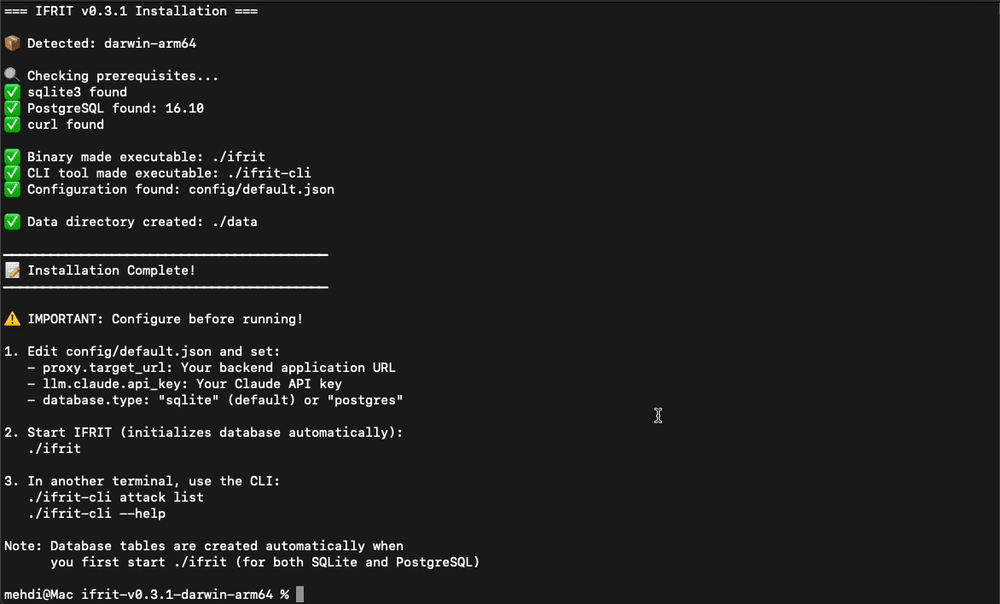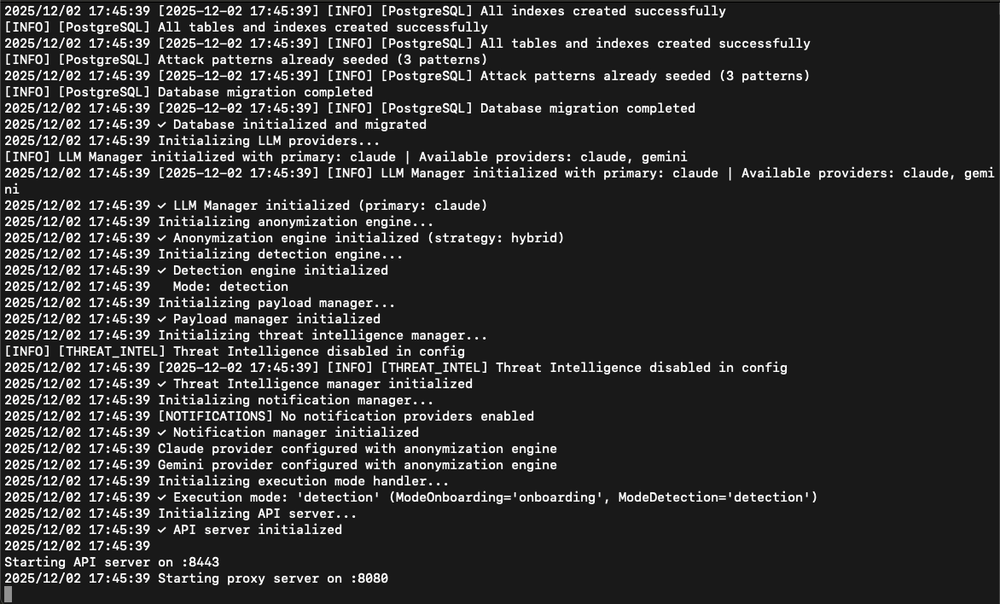
Installation in action - it's really that simple!
# 1. Copy template
cp config/default.json.example config/default.json

# 2. Add your API keys
nano config/default.json  # or use your favorite editor
Minimal configuration to get started:
{
  "llm": {
    "provider": "claude",  // 👈 Choose: "claude" or "gemini"
    "claude": {
      "api_key": "sk-ant-..."  // 🔑 Get from console.anthropic.com
    }
  },
  "proxy": {
    "listen_port": 8080,
    "backend_url": "http://localhost:3000"  // 🎯 Your app
  }
}
Build the source code or Install from the available binaries
# Build the binary
go build -o ifrit ./cmd/ifrit
(optional: build ifrit-cli as well)

# Start IFRIT (runs in background)
./ifrit &

# 🎉 You're protected! Access dashboard:
open http://localhost:8443
That's it! IFRIT is now protecting your application.
🧠 Multi-AI IntelligenceChoose your AI provider or let IFRIT auto-fallback:
|
🗄️ Production-Grade StorageDatabase flexibility for any scale:
|
🎭 Adaptive Deception EngineIntelligent honeypot responses that learn:
Example: SQL injection gets fake user database, path traversal gets fake file listings. |
🔍 Threat Intelligence HubReal-time enrichment from multiple sources:
|
📢 Smart Alert SystemMulti-channel notifications with zero fatigue: |