Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
ExtensionSpoofer — Spoof file icons and extensions in Windows | Kitploit

Tools/GitHubGitHub/henriksb/extensionspoofer
Phishing ToolsIDS/IPS EvasionImpersonation ToolsMalware AnalysisSocial EngineeringPayload Development
GitHubhenriksb/extensionspoofer

ExtensionSpoofer

Spoof file icons and extensions in Windows

View Repository
187641113 months agoReviewed by Kitploit
Share

ExtensionSpoofer

ExtensionSpoofer is a Visual Basic .NET desktop app that demonstrates how file names and icons can be visually manipulated on Windows while the underlying executable file type remains unchanged.

It uses the Unicode Right-to-Left Override character (U+202E) to reverse displayed characters in part of the file name and can swap the executable icon to match a chosen spoofed extension.

How it works (example)

Original file name:

test_application[RIGHT_TO_LEFT_OVERRIDE]gnp.exe

Displayed in Explorer as:

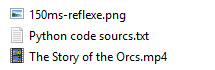
test_applicationexe.png

The file still executes as an executable format.

Supported source executable extensions

  • .exe
  • .scr
  • .com

Note: .com icon replacement is not always supported by the Windows shell.

Usage

  1. Download the precompiled executable from the latest release.
  2. Place the executable next to the Win10Icons folder (or choose a custom icon folder at startup).
  3. Open an executable file.
  4. Enter a file name, choose source extension and spoof extension.
  5. Generate the spoofed file name.

Icon requirements

  • Icon files must be valid .ico files.
  • Renaming .png, .jpg, or other formats to .ico is not sufficient.
  • Each icon file should be named after the target display extension (for example pdf.ico, txt.ico).

Educational use and safety notice

This project is intended for education and awareness: for example, showing students why file names and icons alone are not trustworthy security indicators.

Always use responsibly and only in authorized environments.
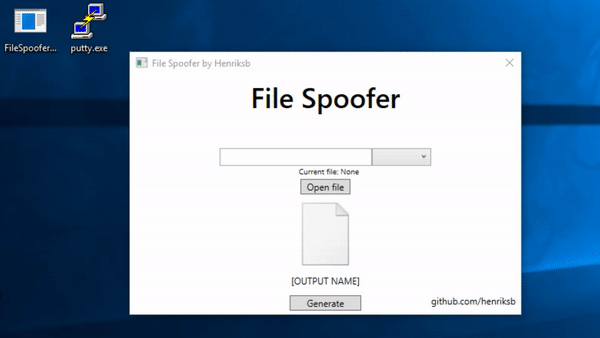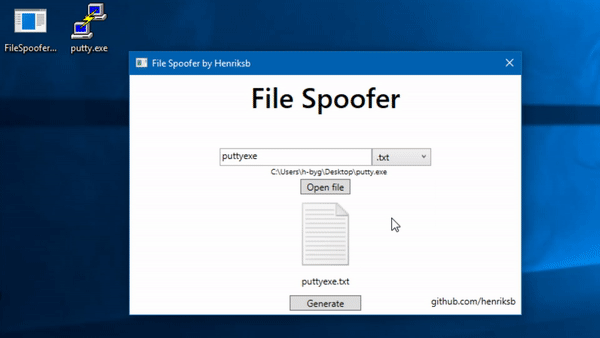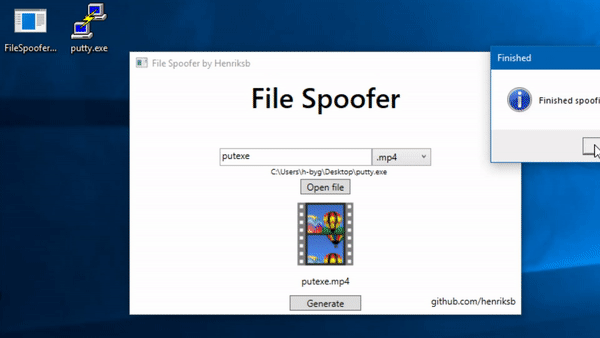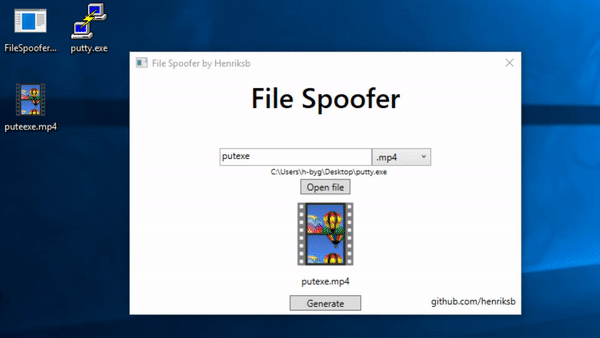
Screenshots

Usage animation Spoofed file examples

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →