

akca
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
248
akha-security/akcaEvidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer
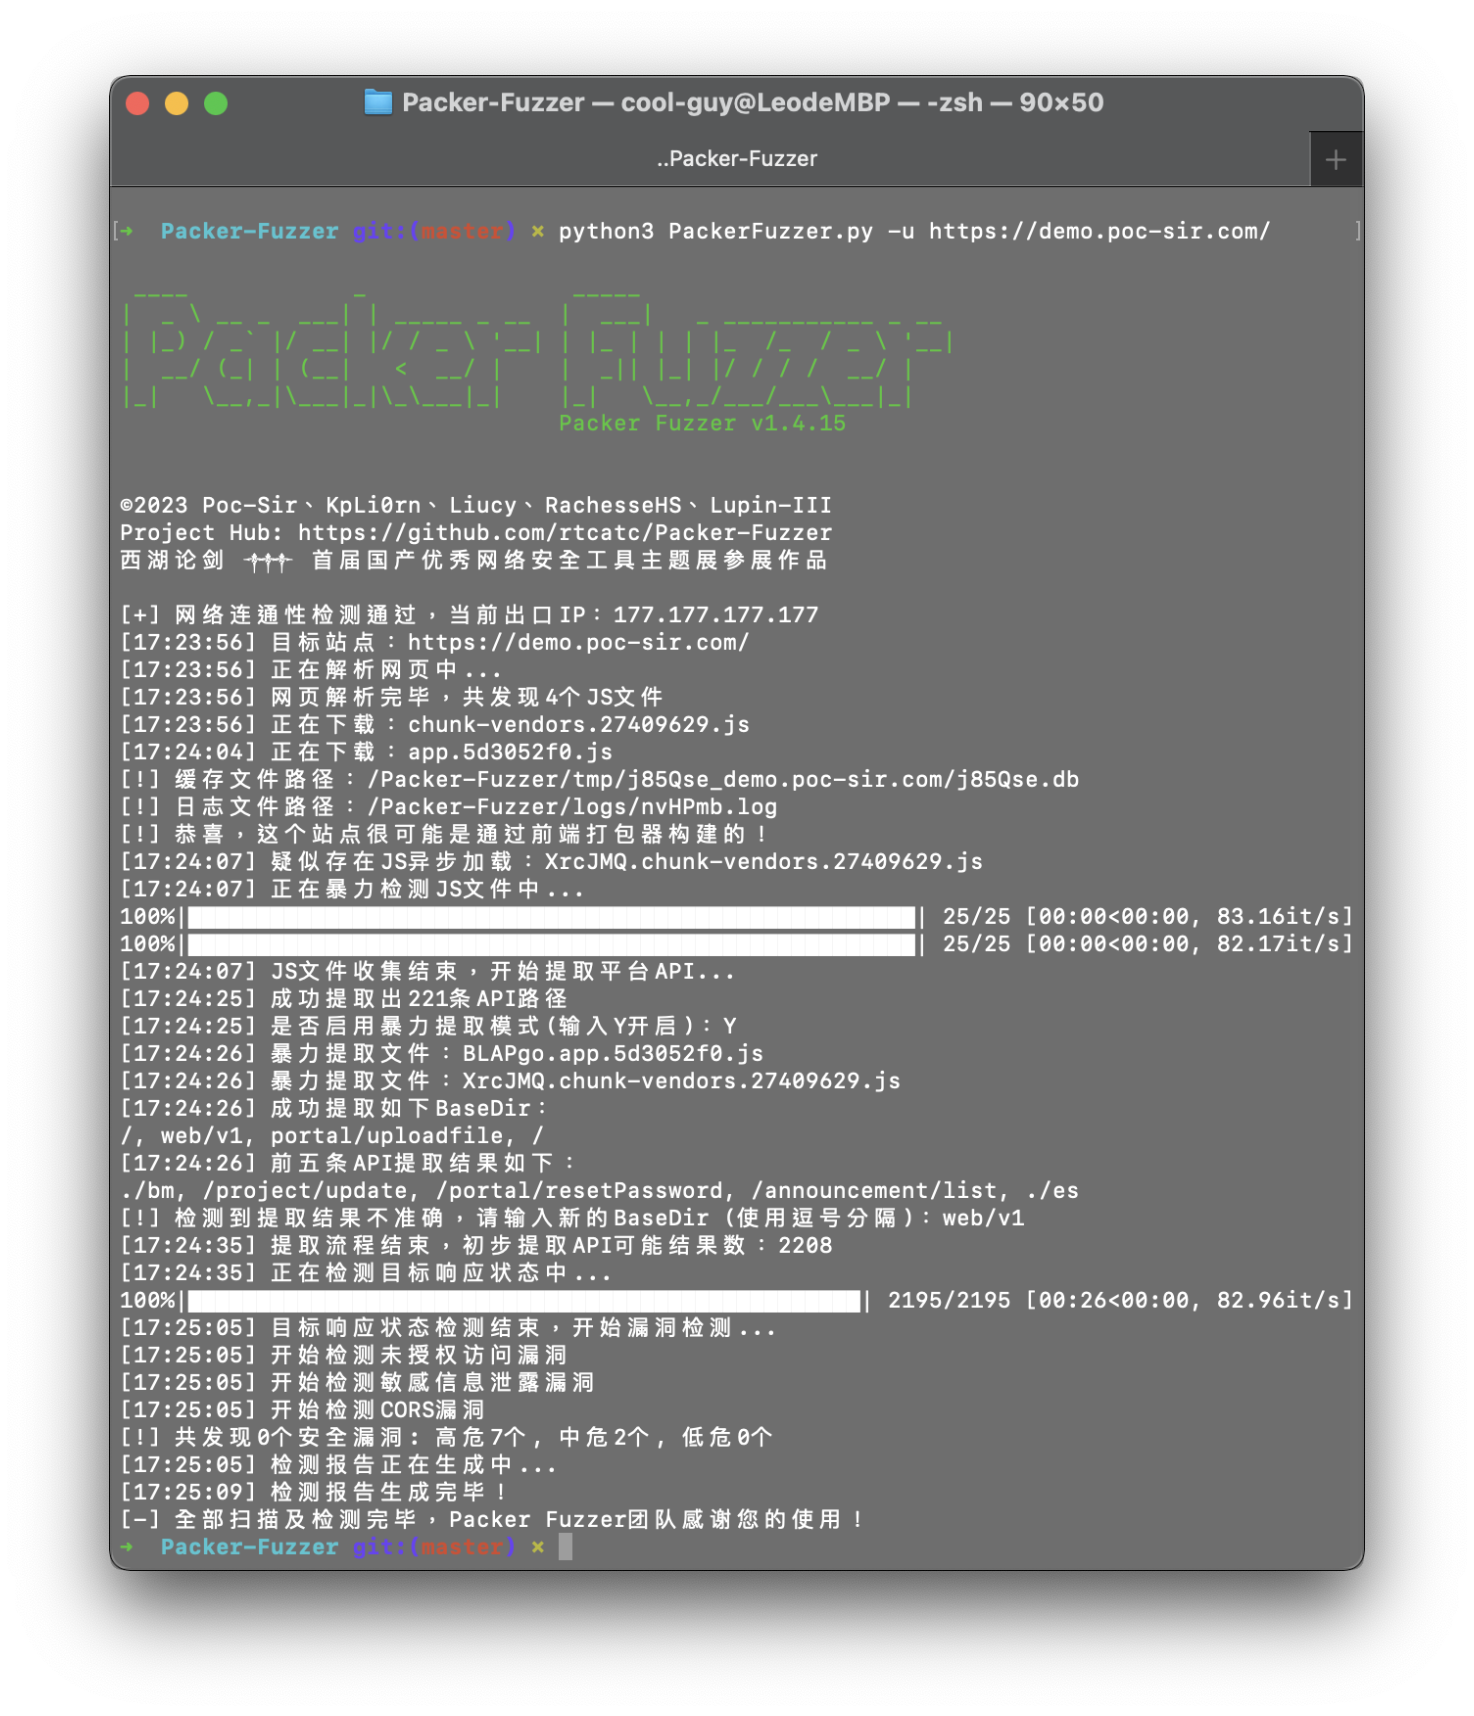 rtcatc/packer-fuzzer
Packer Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
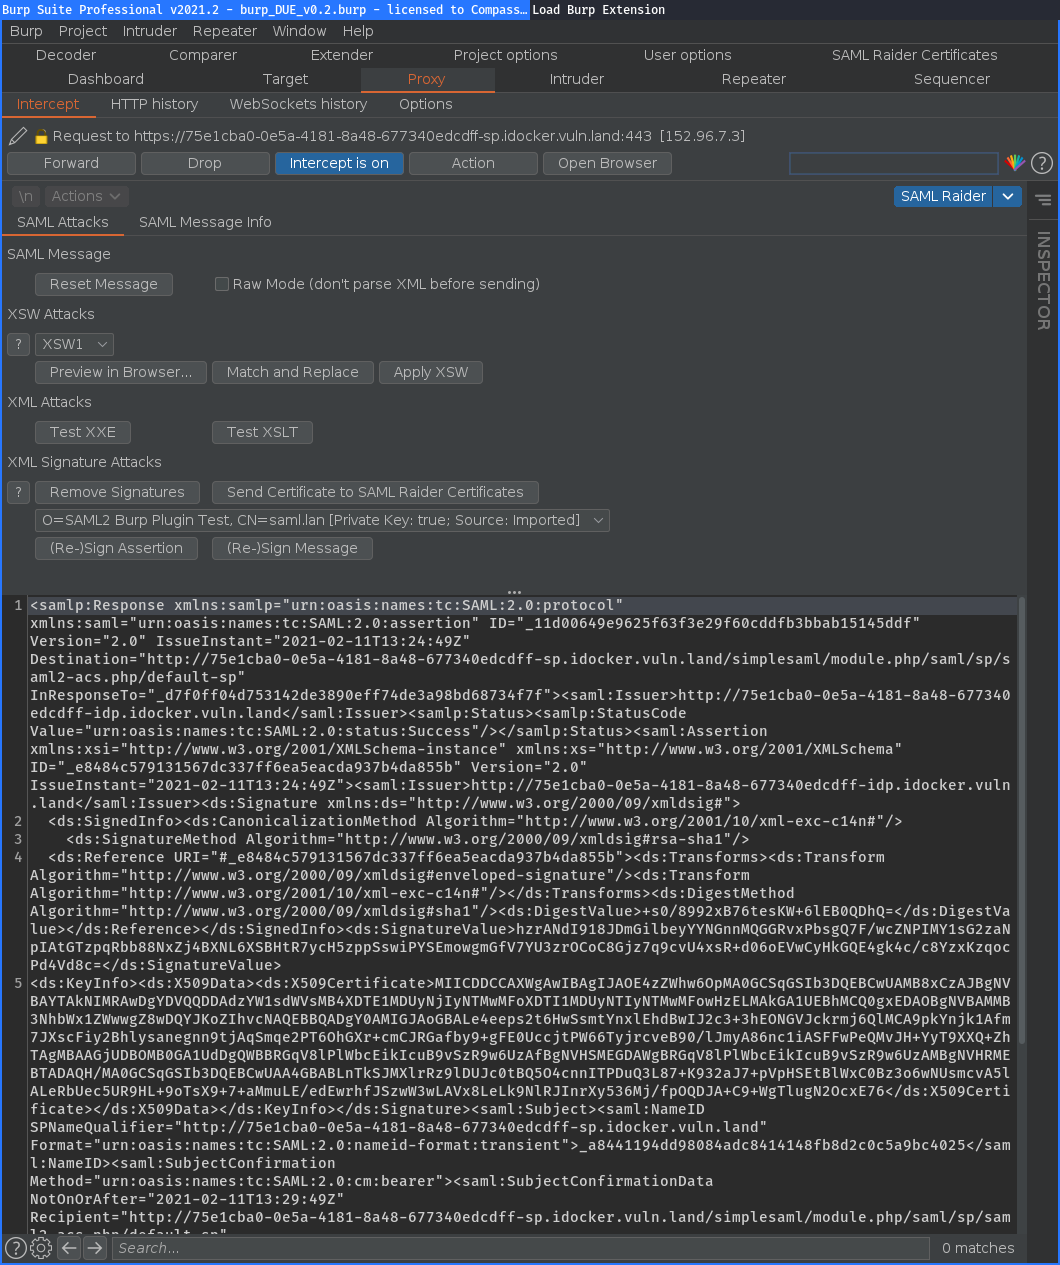 compasssecurity/samlraider
SAML2 Burp Extension
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
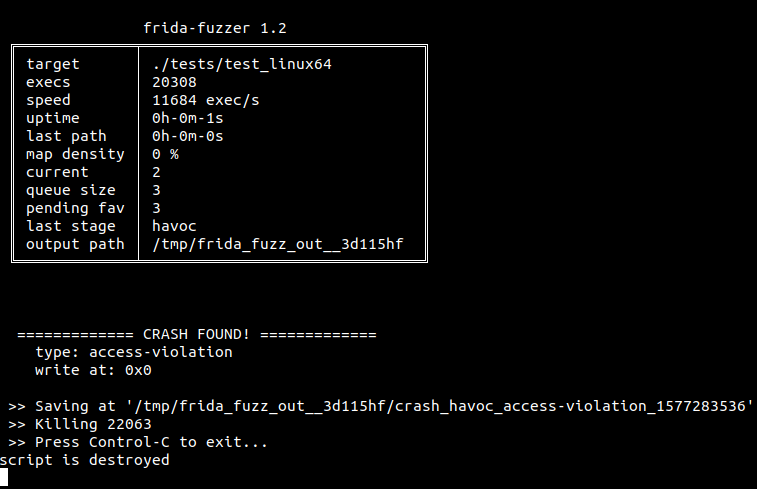 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.