

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
64 results
disrobe preview

disrobe

GitHub1-3-7/disrobe

Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…

android-securitybinary-analysisfirmware-analysis+4
168
12 days ago
kunglao-agent preview

kunglao-agent

GitHubamd2g2zz/kunglao-agent

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
ai-assisted-reversingandroid-securitybinary-analysis+8
5614 days ago
firmware-reverse-engineering preview

firmware-reverse-engineering

GitHuborbitcurve/firmware-reverse-engineering

Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…
binary-analysiscurated-resourcesdynamic-analysis-sandboxing+5
23121 days ago
Xiaomi-C200-Firmware-Analysis preview

Xiaomi-C200-Firmware-Analysis

GitHubh3xdum/xiaomi-c200-firmware-analysis

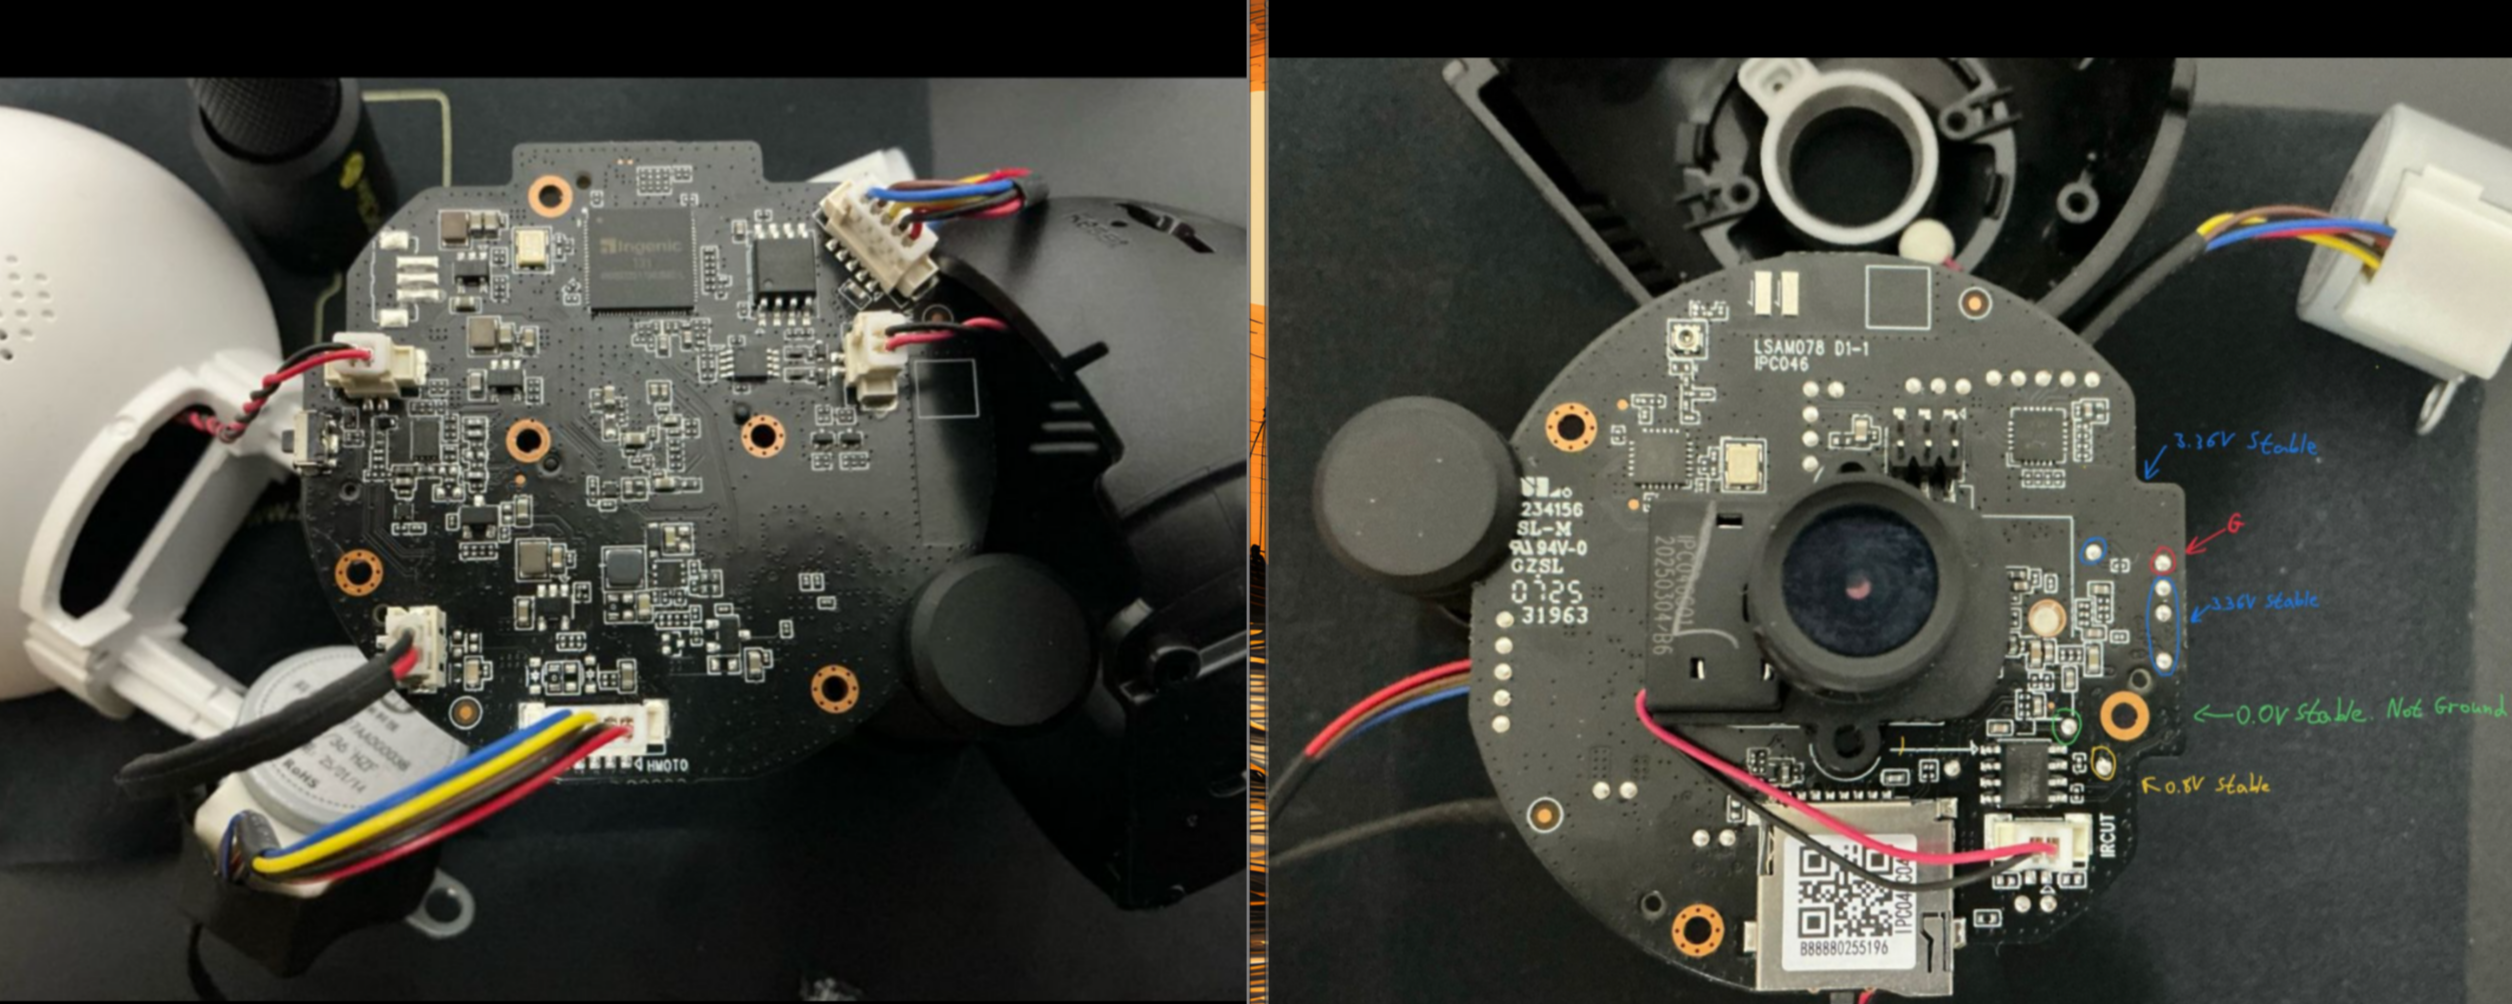
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
1110 months ago
Android-Projector-C2-Malware preview

Android-Projector-C2-Malware

GitHubkavan00/android-projector-c2-malware

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

android-securitycommand-and-controldigital-forensics+9
181 month ago
badbox-h713-projector preview

badbox-h713-projector

GitHubflorentineprinzessinzusachsen/badbox-h713-projector

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
android-securitydigital-forensicsembedded-systems-security+8
31 month ago
unblob preview

unblob

GitHubonekey-sec/unblob

Extract files from any kind of container formats

binary-analysisdata-recoveryembedded-systems-security+3
2.5k9h 31m ago
spidump preview

spidump

GitHubwrongbaud/spidump

Tool for reconstructing SPI flash images via logic analyzer captures
digital-forensicsembedded-systems-securityfirmware-analysis+7
91 month ago
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k8 days ago
Philips-PM-5139-5138A-5136-Firmware-Project preview

Philips-PM-5139-5138A-5136-Firmware-Project

GitHubdoctormord/philips-pm-5139-5138a-5136-firmware-project

Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…
binary-analysisdynamic-analysis-sandboxingeducation+6
41 month ago
mousejack preview

mousejack

GitHubbastilleresearch/mousejack

Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
exploitationfirmware-analysishardware-iot-security+3
1.4k10 years ago
sass-king preview

sass-king

GitHubflorianmattana/sass-king

Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.
binary-analysiscode-analysiscurated-resources+8
3175 months ago
polypyus preview

polypyus

GitHubseemoo-lab/polypyus

Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…

binary-analysisembedded-systems-securityfirmware-analysis+1
2325 years ago
Barzakh preview

Barzakh

GitHubyasindce1998/barzakh

Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.

defensive-toolsembedded-systems-securityfirmware-analysis+6
1520 days ago
xtride preview

xtride

GitHubpr0me/xtride

N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…

binary-analysisdebuggerseducation+5
264 months ago
build.prop preview

build.prop

GitHubpixel-props/build.prop

Bash script to build your own system.prop

android-securityfirmware-analysismobile-security+1
2901 month ago
qemu preview

qemu

GitHubqemu/qemu

Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…

embedded-systems-securityfirmware-analysisgeneral-purpose-utilities+2
13.4k13h 21m ago
CVE-2026-43499_HW-CLT-AL01 preview

CVE-2026-43499_HW-CLT-AL01

GitHubzychen027/cve-2026-43499_hw-clt-al01

Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.

android-securitybinary-exploitationexploitation+4
2 months ago
Previous1234Next