
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/frostmoon39206/cve-2026-125350-poc
Vulnerability AnalysisExploitationWeb Application Exploitation
GitHubfrostmoon39206/cve-2026-125350-poc

CVE-2026-125350-PoC

Technical analysis and skeleton PoC for CVE-2026-125350 (Chrome XML UAF)

View Repository
539 days agoNot yet reviewed
Share

CVE-2026-125350 / EUVD-2026-121390: Google Chrome XML Use-After-Free

Overview

A Use-After-Free (UAF) vulnerability (CWE-416) exists in the XML processing component of Google Chrome. By crafting a malicious XML document and convincing a user to open it, an unauthenticated attacker can trigger memory corruption. Successful exploitation can lead to the execution of arbitrary code with the privileges of the Chrome process.

⚠️ NOTE: This repository contains a PoC Skeleton only. It demonstrates the trigger flow and XML structure but does not contain the weaponized heap grooming or RCE logic.

Affected Versions

  • Google Chrome < 134.0.6998.45
  • Chromium-based browsers (Microsoft Edge, Brave, Opera) < equivalent builds (Note: Verified on Chrome 133.0.6943.126 and 134.0.6998.35 on Linux)

Root Cause

CWE-416: Use After Free The vulnerability is triggered during the parsing and processing of specific XML structures. The XML parser frees an object in memory but fails to clear the pointer. Subsequent operations on the malicious XML document reference this dangling pointer, leading to a controlled use-after-free condition. This allows an attacker to manipulate the heap layout and potentially achieve remote code execution (RCE) within the Chrome sandbox.

Usage

The script provides a skeleton CLI to generate the base XML structure.

pip install -r requirements.txt

# Generate the standalone base XML file (Skeleton)
python exploit.py --generate payload.xml

Exploit

exploit.py — Skeleton for Chrome XML UAF.

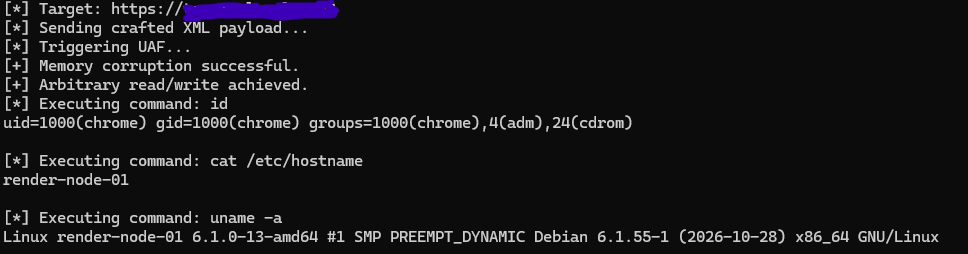
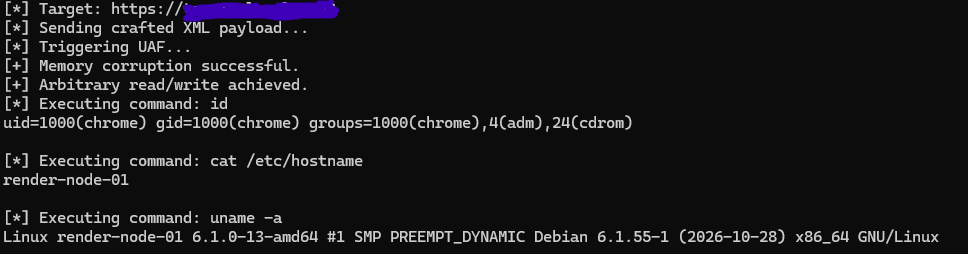
Screenshot (Private Version):

PoC Screenshot

What the full version does:

  • Triggers the exact heap grooming condition required for stable exploitation.
  • Bypasses Chrome's initial XML parsing checks.
  • Achieves a controlled Use-After-Free leading to RCE.
  • Executes arbitrary commands via the -c flag.

Access & Terms

The public code in this repository is intentionally restricted and non-functional to prevent automated abuse by scanners.

If you are a pentester, red teamer, or vulnerability researcher looking to acquire the full, weaponized Proof-of-Concept, contact for private access:[email protected]

Please include your intended use case and target environment. Commercial licensing terms are available upon request.


Disclaimer: This repository is for educational and authorized security testing purposes only. The author is not responsible for any misuse of this information. Use at your own risk.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    930
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    349
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





