
CVE-2022-23808
 dipakpanchal05/cve-2022-23808
Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…
exploitationpenetration-testingred-teaming+3
dipakpanchal05/cve-2022-23808Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…
 stmcyber/rmitaste
Java RMI security testing tool for detecting, enumerating, and exploiting insecure RMI services using ysoserial deserialization gadgets to achieve…
 rekter0/exploits
Collection of Python-based exploit scripts for penetration testing, covering multiple vulnerability types and exploitation techniques.
 exploits-forsale/cve-2024-26218
Proof-of-concept exploit for CVE-2024-26218, demonstrating a specific vulnerability for security research and testing.
 mistymntncop/cve-2025-5419
Proof-of-concept exploit for CVE-2025-5419, demonstrating a critical vulnerability with a JavaScript-based implementation for security testing and…
 secengjeff/rapidresetclient
Tool for testing mitigations and exposure to Rapid Reset DDoS (CVE-2023-44487)
 exploits-forsale/cve-2024-21345
Proof-of-concept exploit for CVE-2024-21345, demonstrating a specific vulnerability with functional code for security testing and validation.
 mistymntncop/cve-2023-2033
JavaScript exploit targeting CVE-2023-2033 for proof-of-concept testing and vulnerability validation in web applications.
 exploitblizzard/windows-privilege-escalation-cve-2021-1732
C++ exploit for CVE-2021-1732 targeting Windows privilege escalation on Win10 1803-20H2 and Server 2019/2004. Provides kernel-level elevation of…
 rogue-kdc/cve-2019-1253
Proof-of-concept exploit for CVE-2019-1253, a Windows privilege escalation vulnerability. Demonstrates exploitation technique for security research…
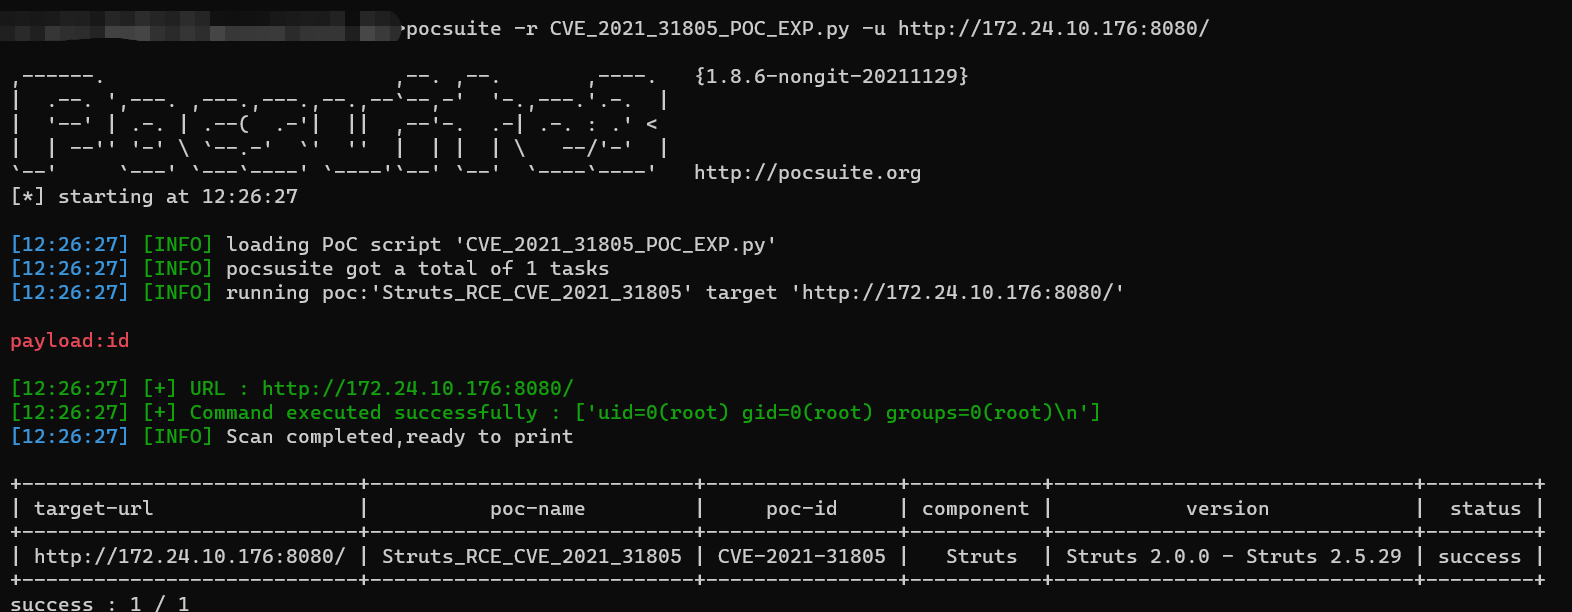 wrin9/cve-2021-31805
Python-based proof-of-concept and exploit for Apache Struts2 RCE (CVE-2021-31805), enabling command execution via OGNL injection. Includes POC and…
 luemmelsec/cve-2023-29357
C# proof-of-concept exploit for CVE-2023-29357 targeting SharePoint, with YARA detection rules and detailed usage instructions for security testing.
 zerodayevil/cve-2026-40369-exploit
Proof-of-concept exploit code targeting CVE-2026-40369, demonstrating the vulnerability for research and authorized security testing.
 convisolabs/cve-2022-24834
Generic heap overflow exploit for CVE-2022-24834 in Redis Lua cjson library, with auto gadget finder, symbol resolution, and reverse shell handler…
 holygu/cve-2023-42442
Go-based exploit for JumpServer unauthorized access vulnerability (CVE-2023-42442) with a single-command execution interface for penetration testing.
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…
 ghost-nemesis/cve-2021-20837-poc
Proof-of-concept exploit for CVE-2021-20837, a remote code execution vulnerability in MovableType CMS. Demonstrates exploitation technique for…
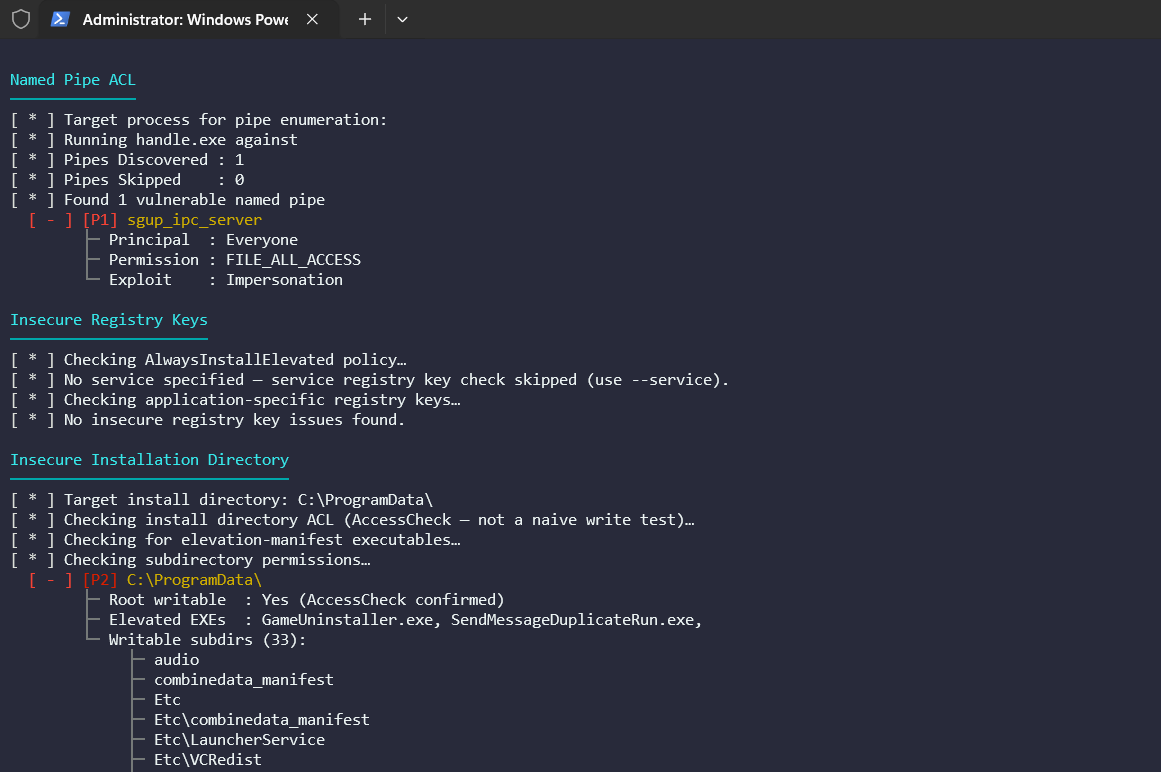 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…