
ftw
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
devsecopspenetration-testingvulnerability-scanners+2
142
coreruleset/ftwYAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
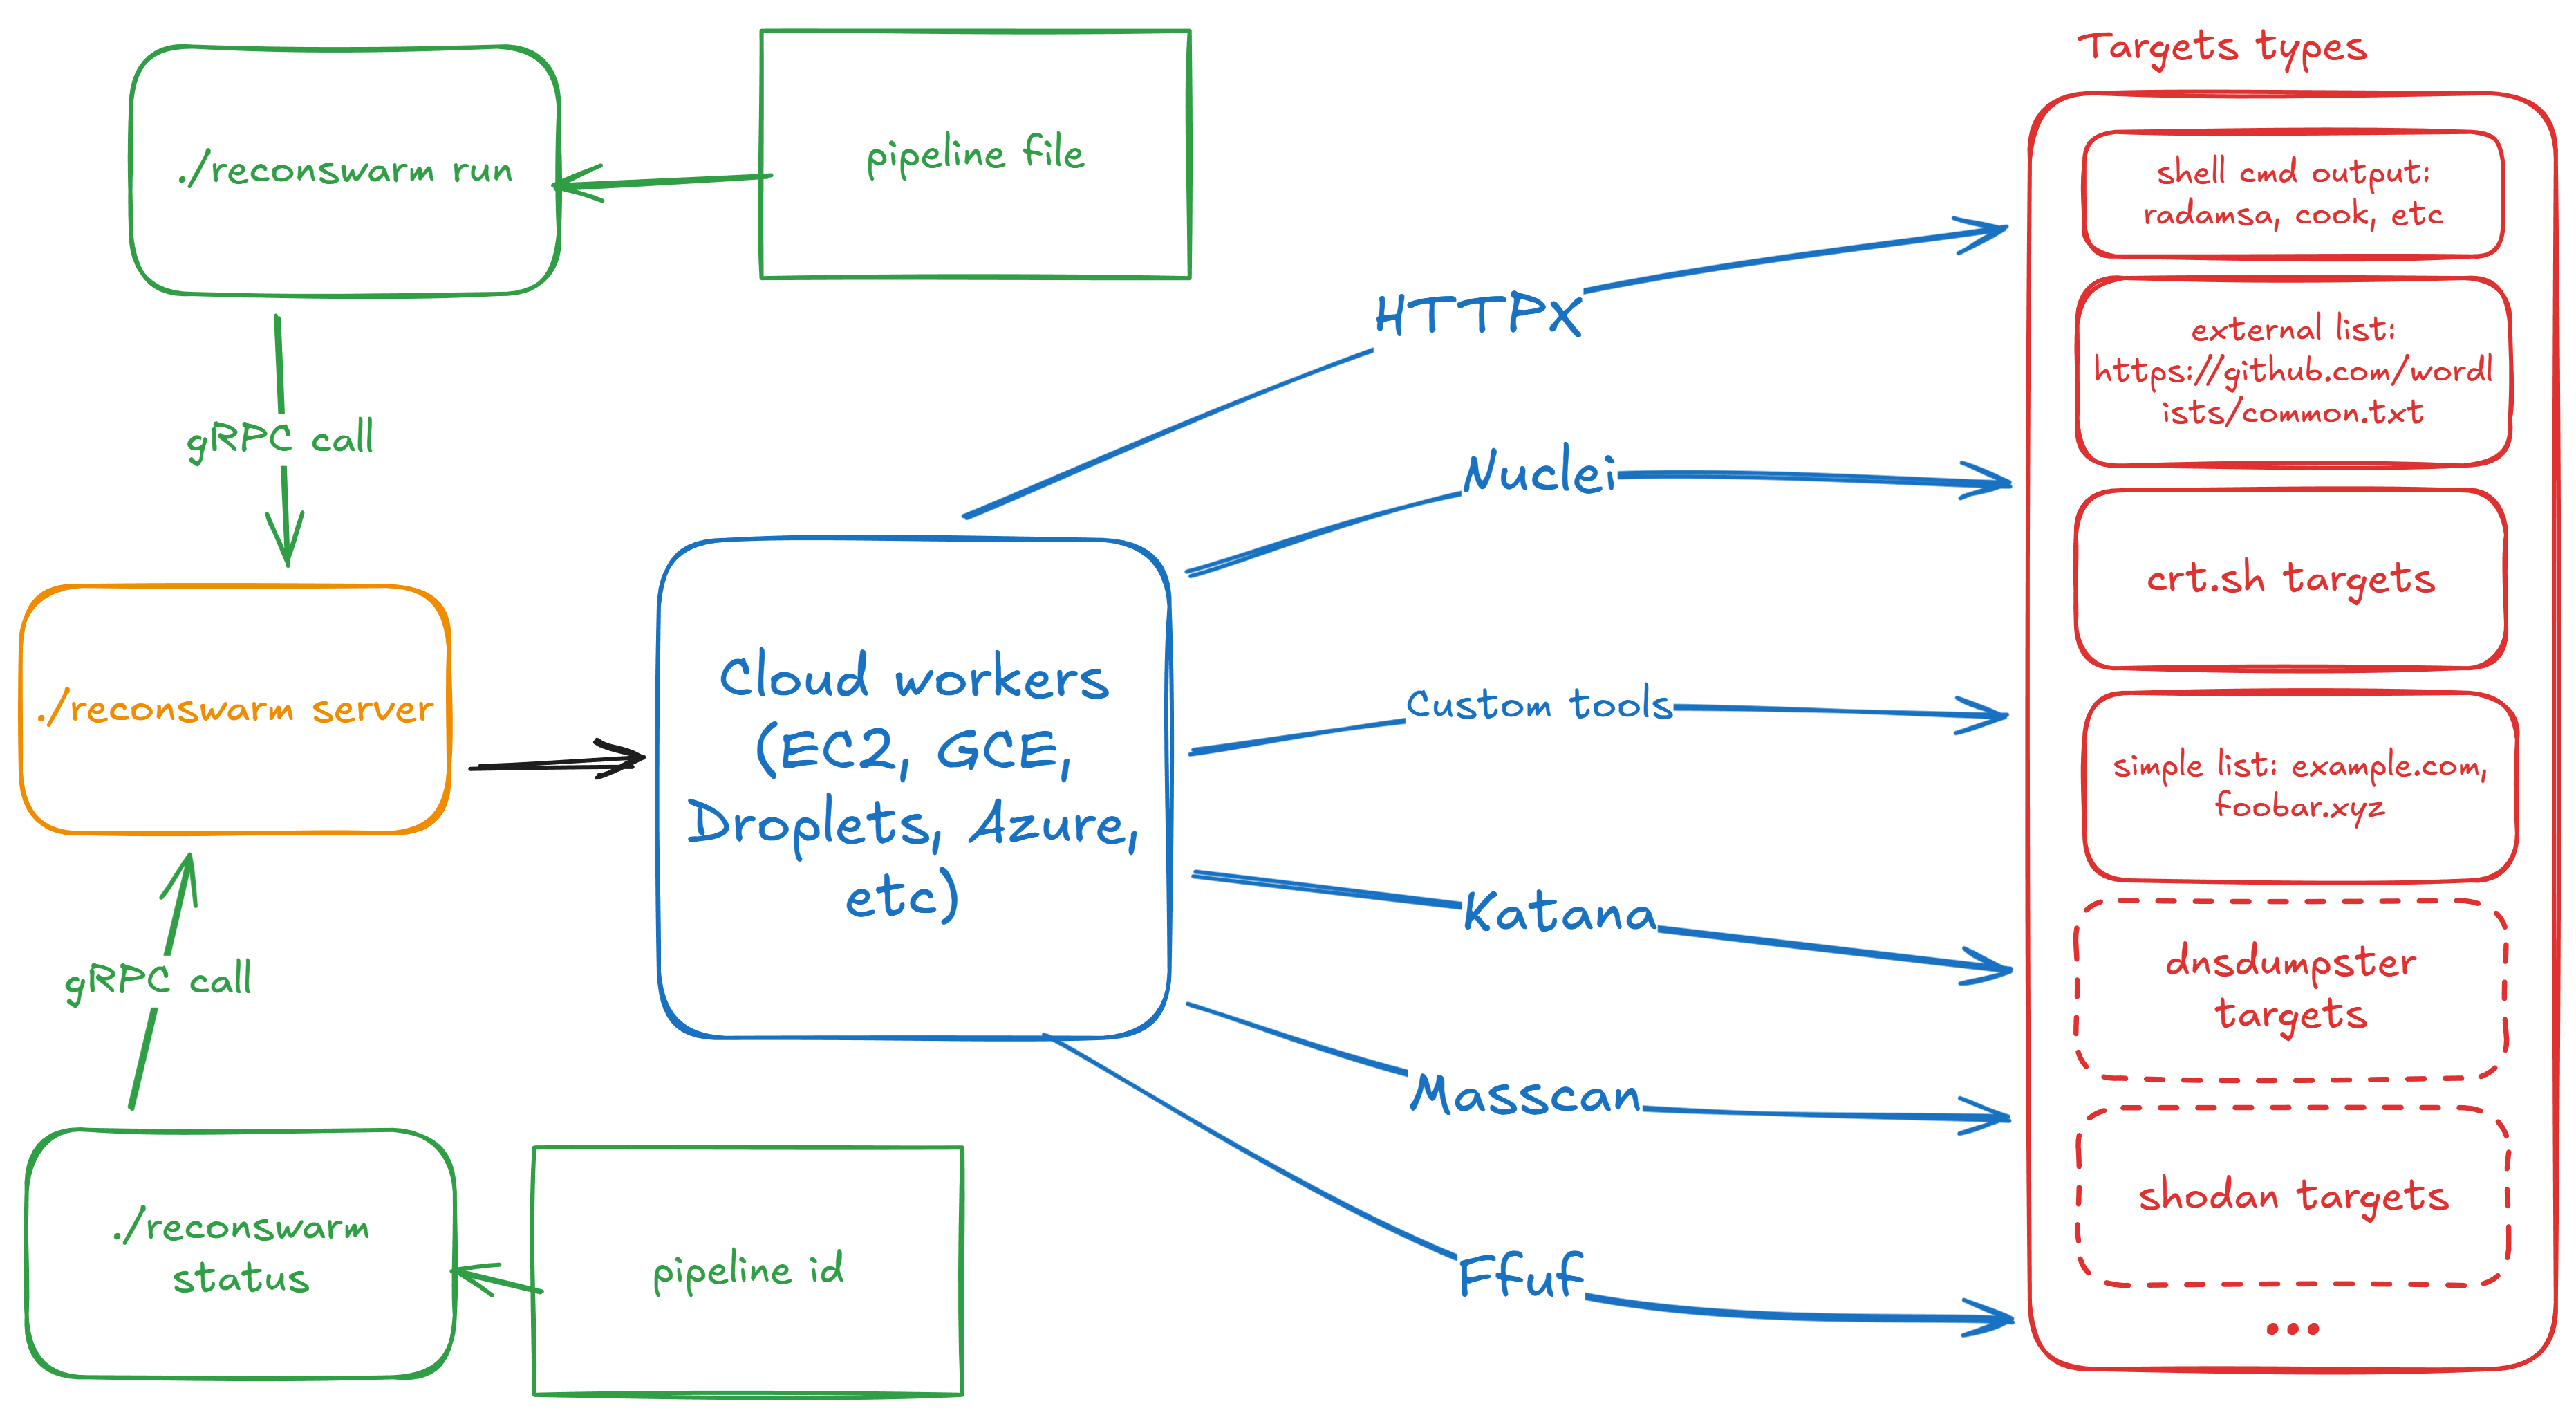 renatus-cartesius/reconswarm
Extend your recon with cloud power
 salesforce/vulnreport
Open-source pentesting management and automation platform by Salesforce Product Security
 defectdojo/django-defectdojo
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 reconmap/reconmap
Reconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from…
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
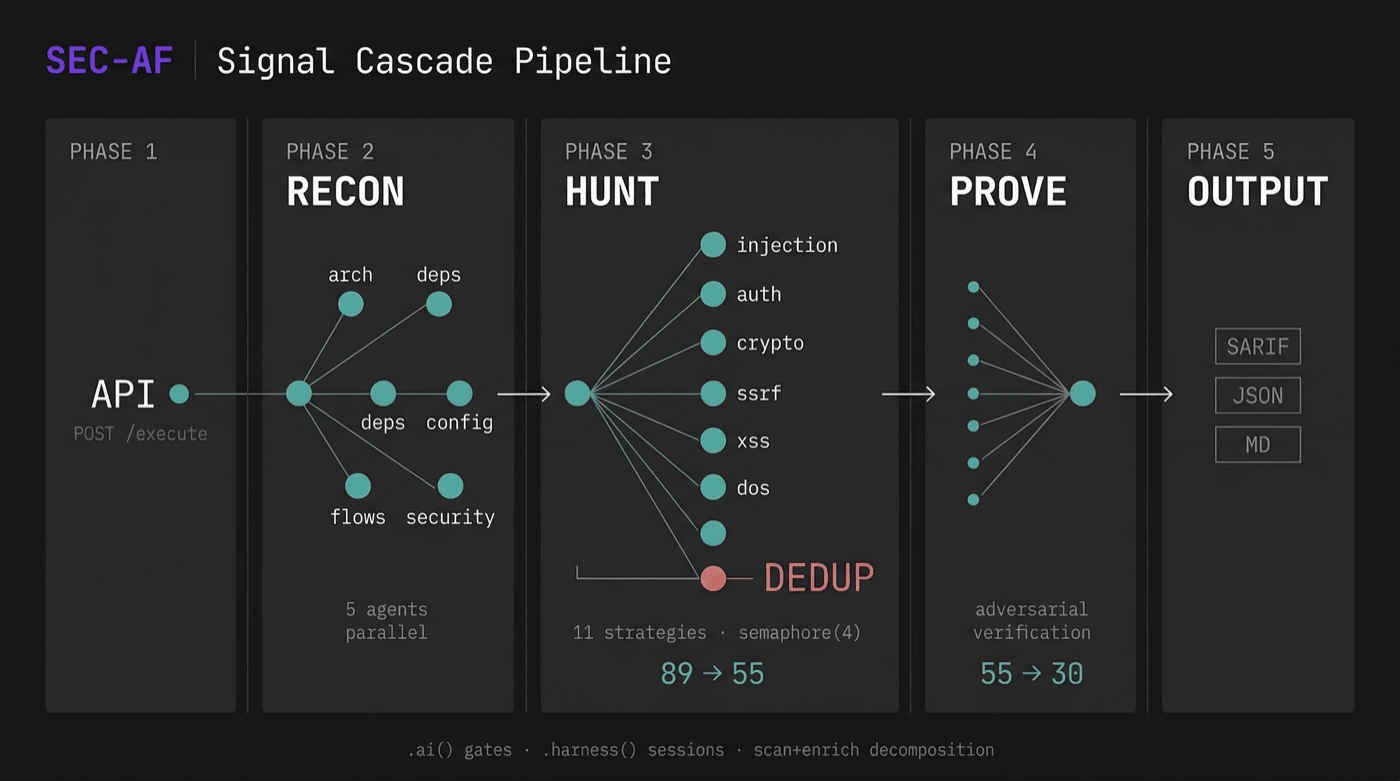 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 infobyte/faraday_plugins
Security tools report parsers for Faradaysec.com
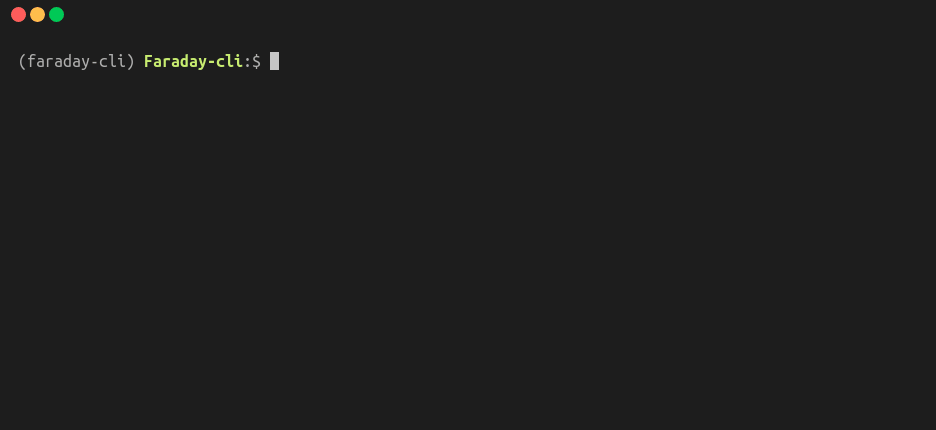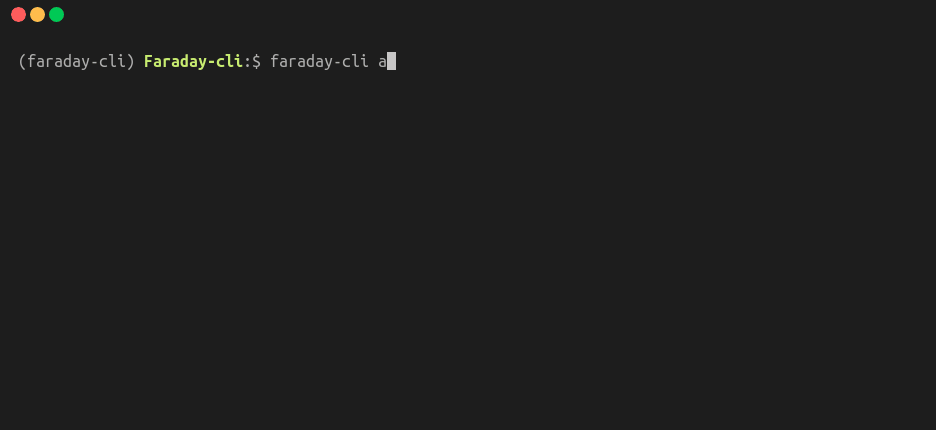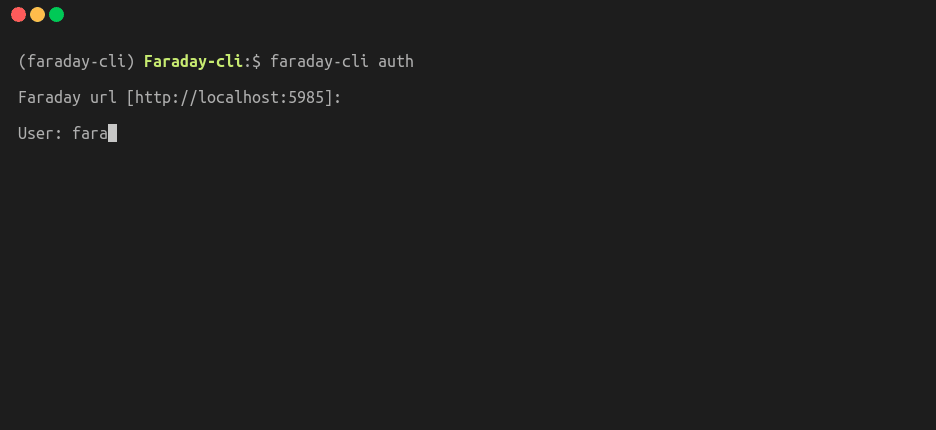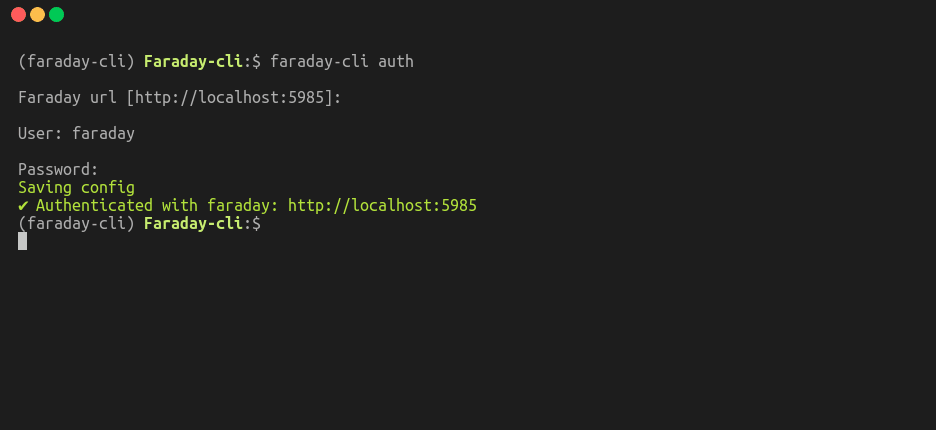 infobyte/faraday-cli
Faraday's Command Line Interface
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 adimahluf/rapidwebrecon
A high-performance automation tool designed to bridge the gap between technical web reconnaissance and executive reporting. Developed by **Adi…
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
 zanex360/cdt-samba-deploy
CDT Ansible playbook for deploying CVE-2017-7494 aka "SambaCry" to an Ubuntu box
 samjuk/cosmicsting-validator
CosmicSting (CVE-2024-34102) POC / Patch Validator