

BlobRunner
 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
debuggersmalware-analysisreverse-engineering+1
oalabs/blobrunnerQuickly debug shellcode extracted during malware analysis
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 hugsy/cfb
ProcMon-style IRP monitor for Windows drivers. Captures and logs I/O Request Packets via a kernel driver and user-land broker, outputting JSON for…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 x86-jtag-open-research/x86-jtag-information
Documents Intel and AMD x86 JTAG debugger hardware, connectors, probe software, and target platforms for low-level system debugging and firmware…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 packtpublishing/learning-linux-binary-analysis
Learning Linux Binary Analysis, published by Packt

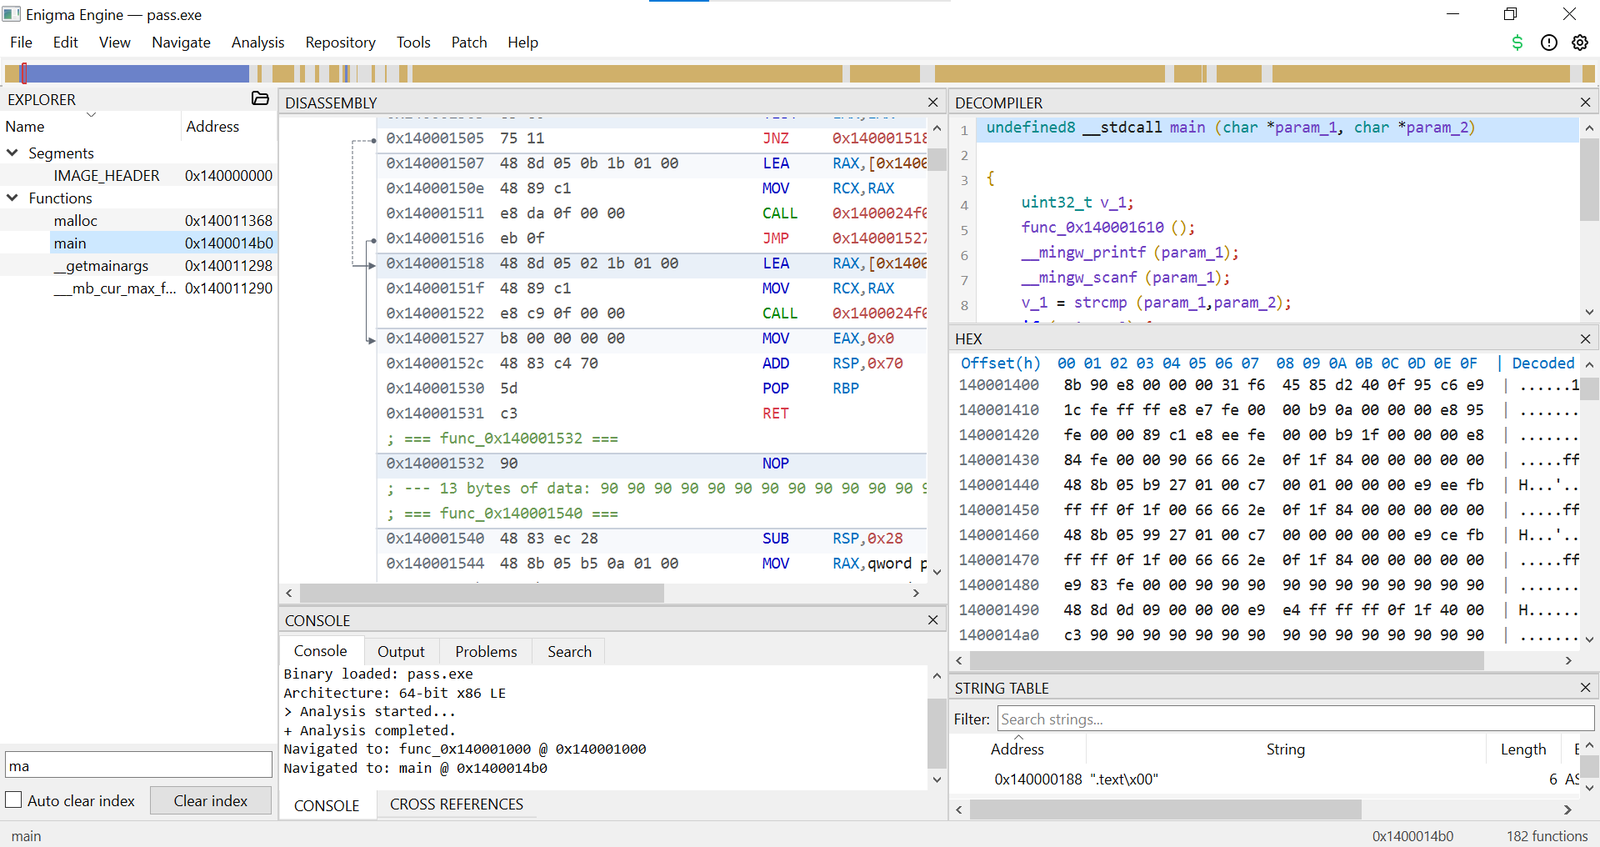 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 gengstah/windbg-mcp
An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
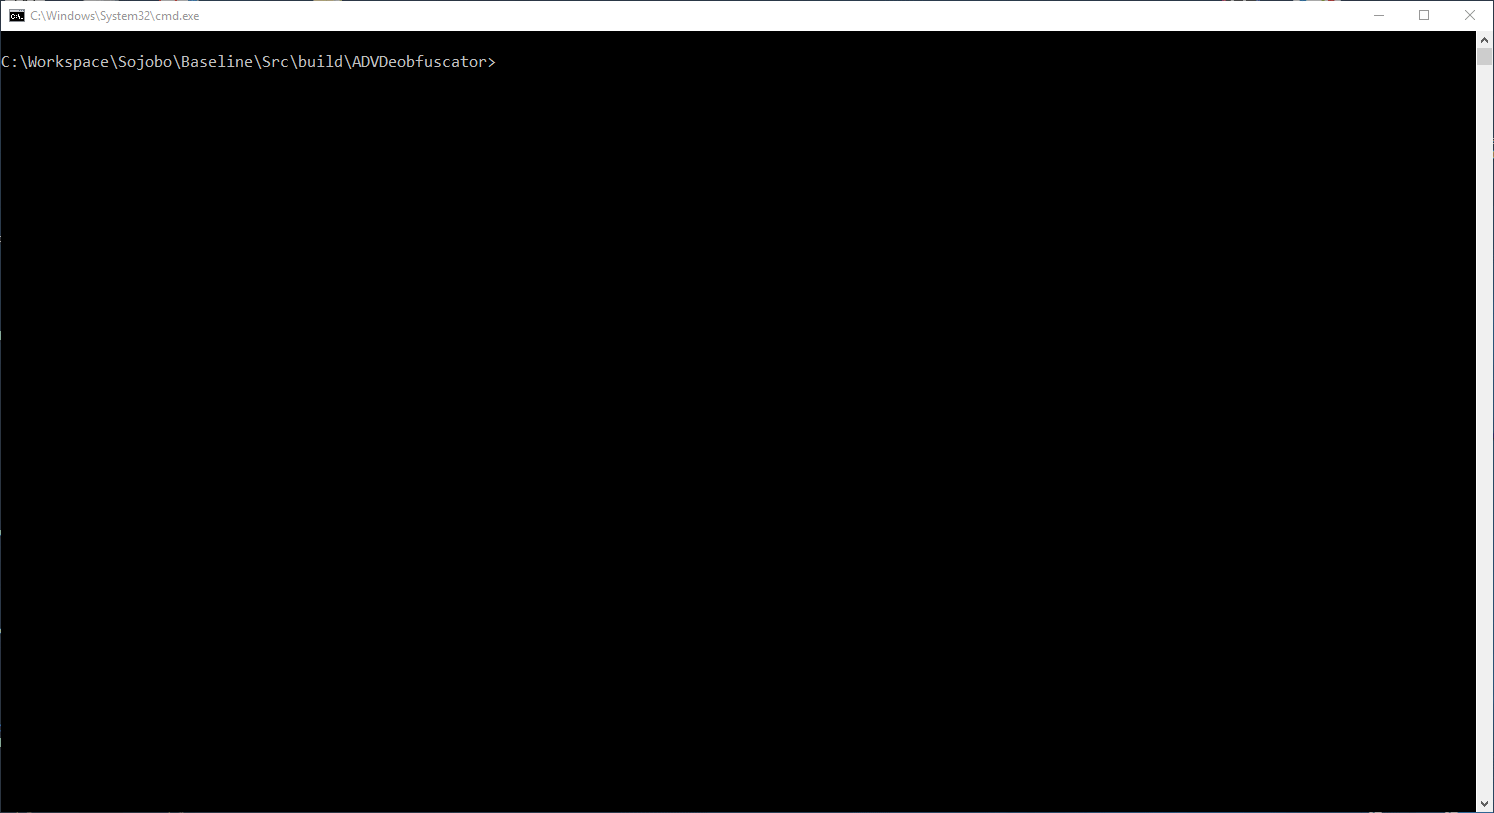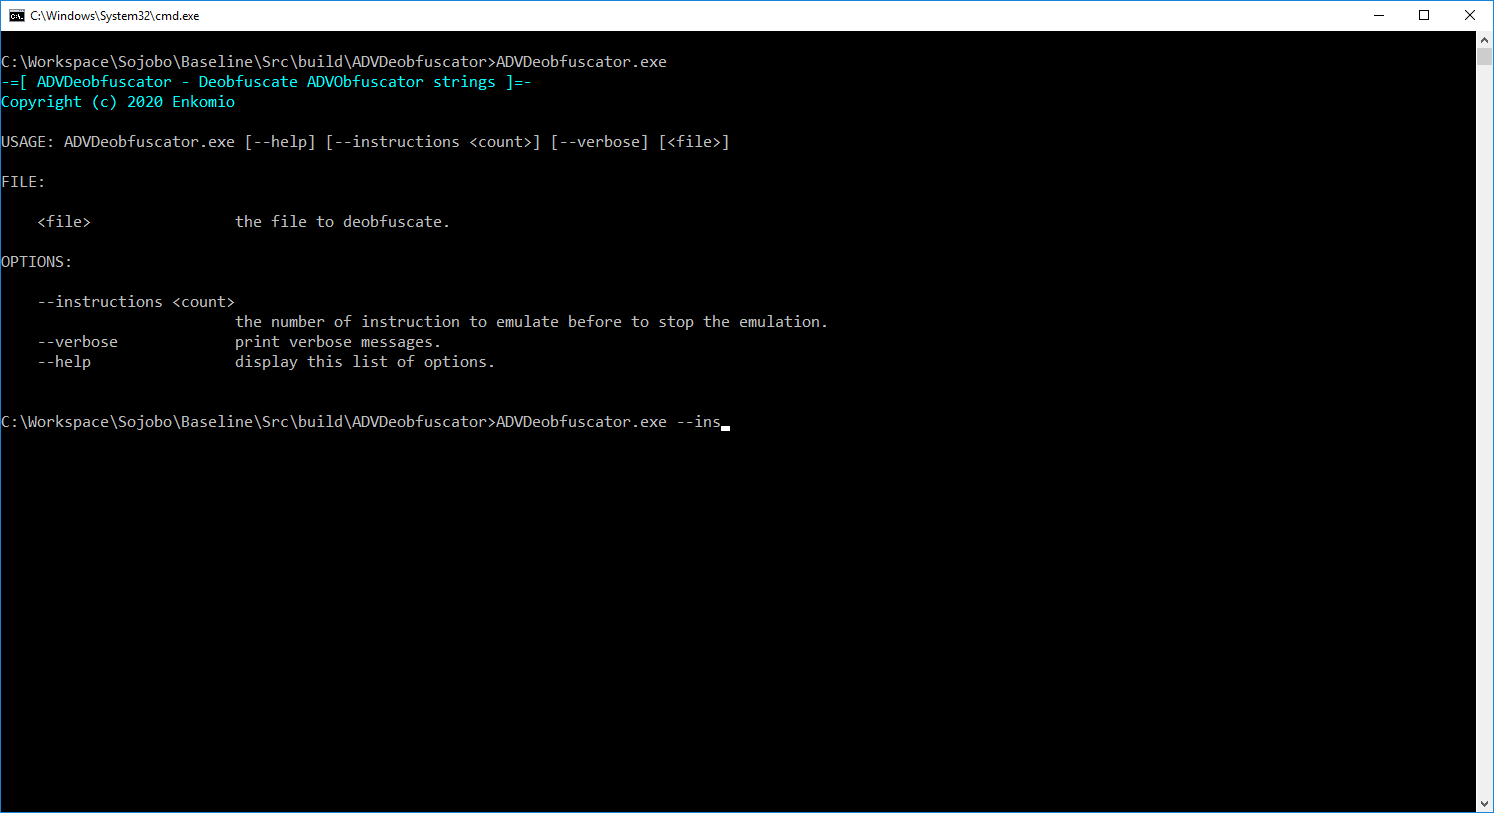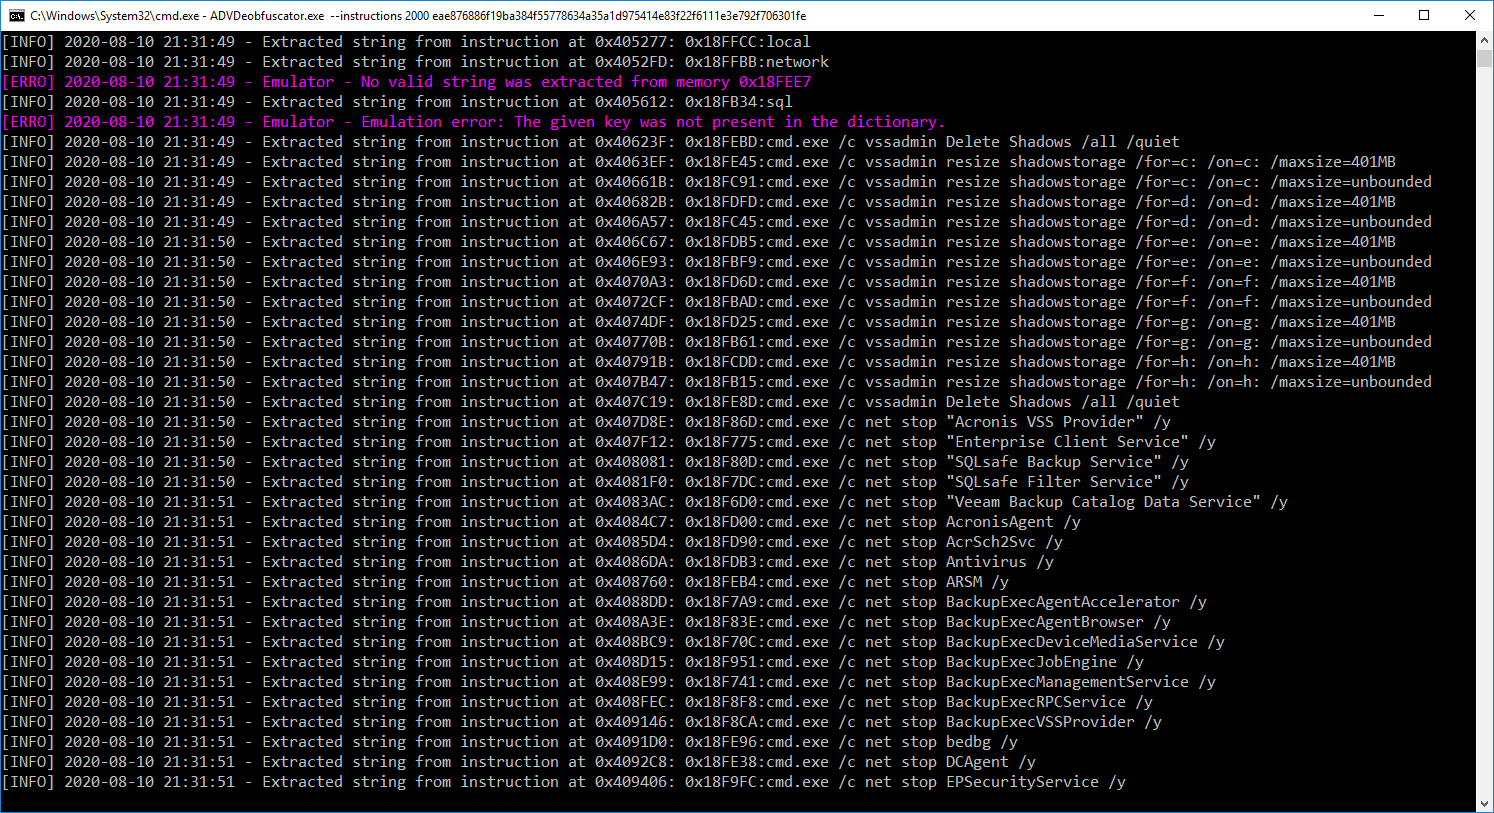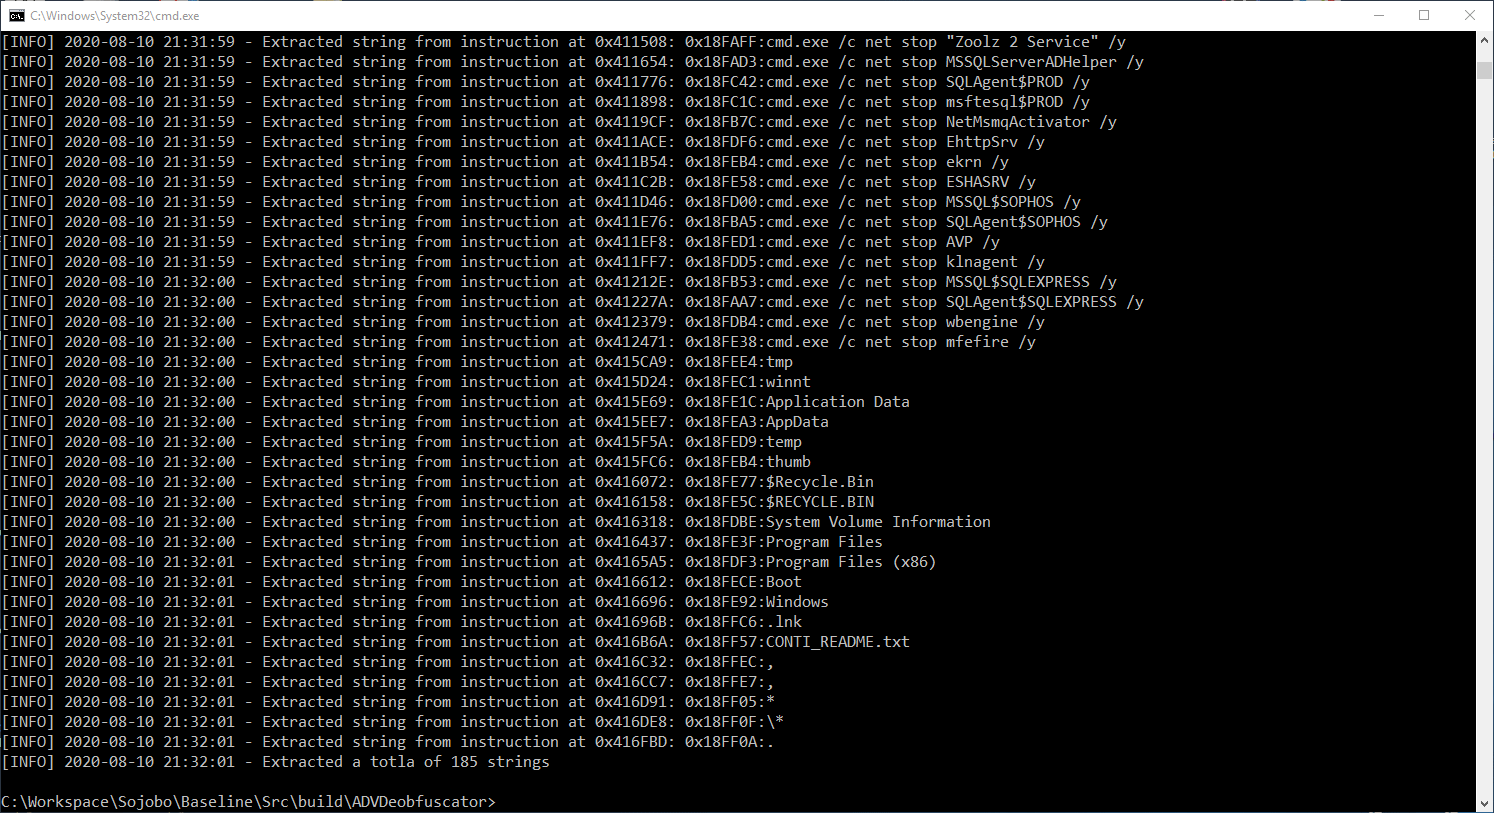 enkomio/sojobo
A binary analysis framework
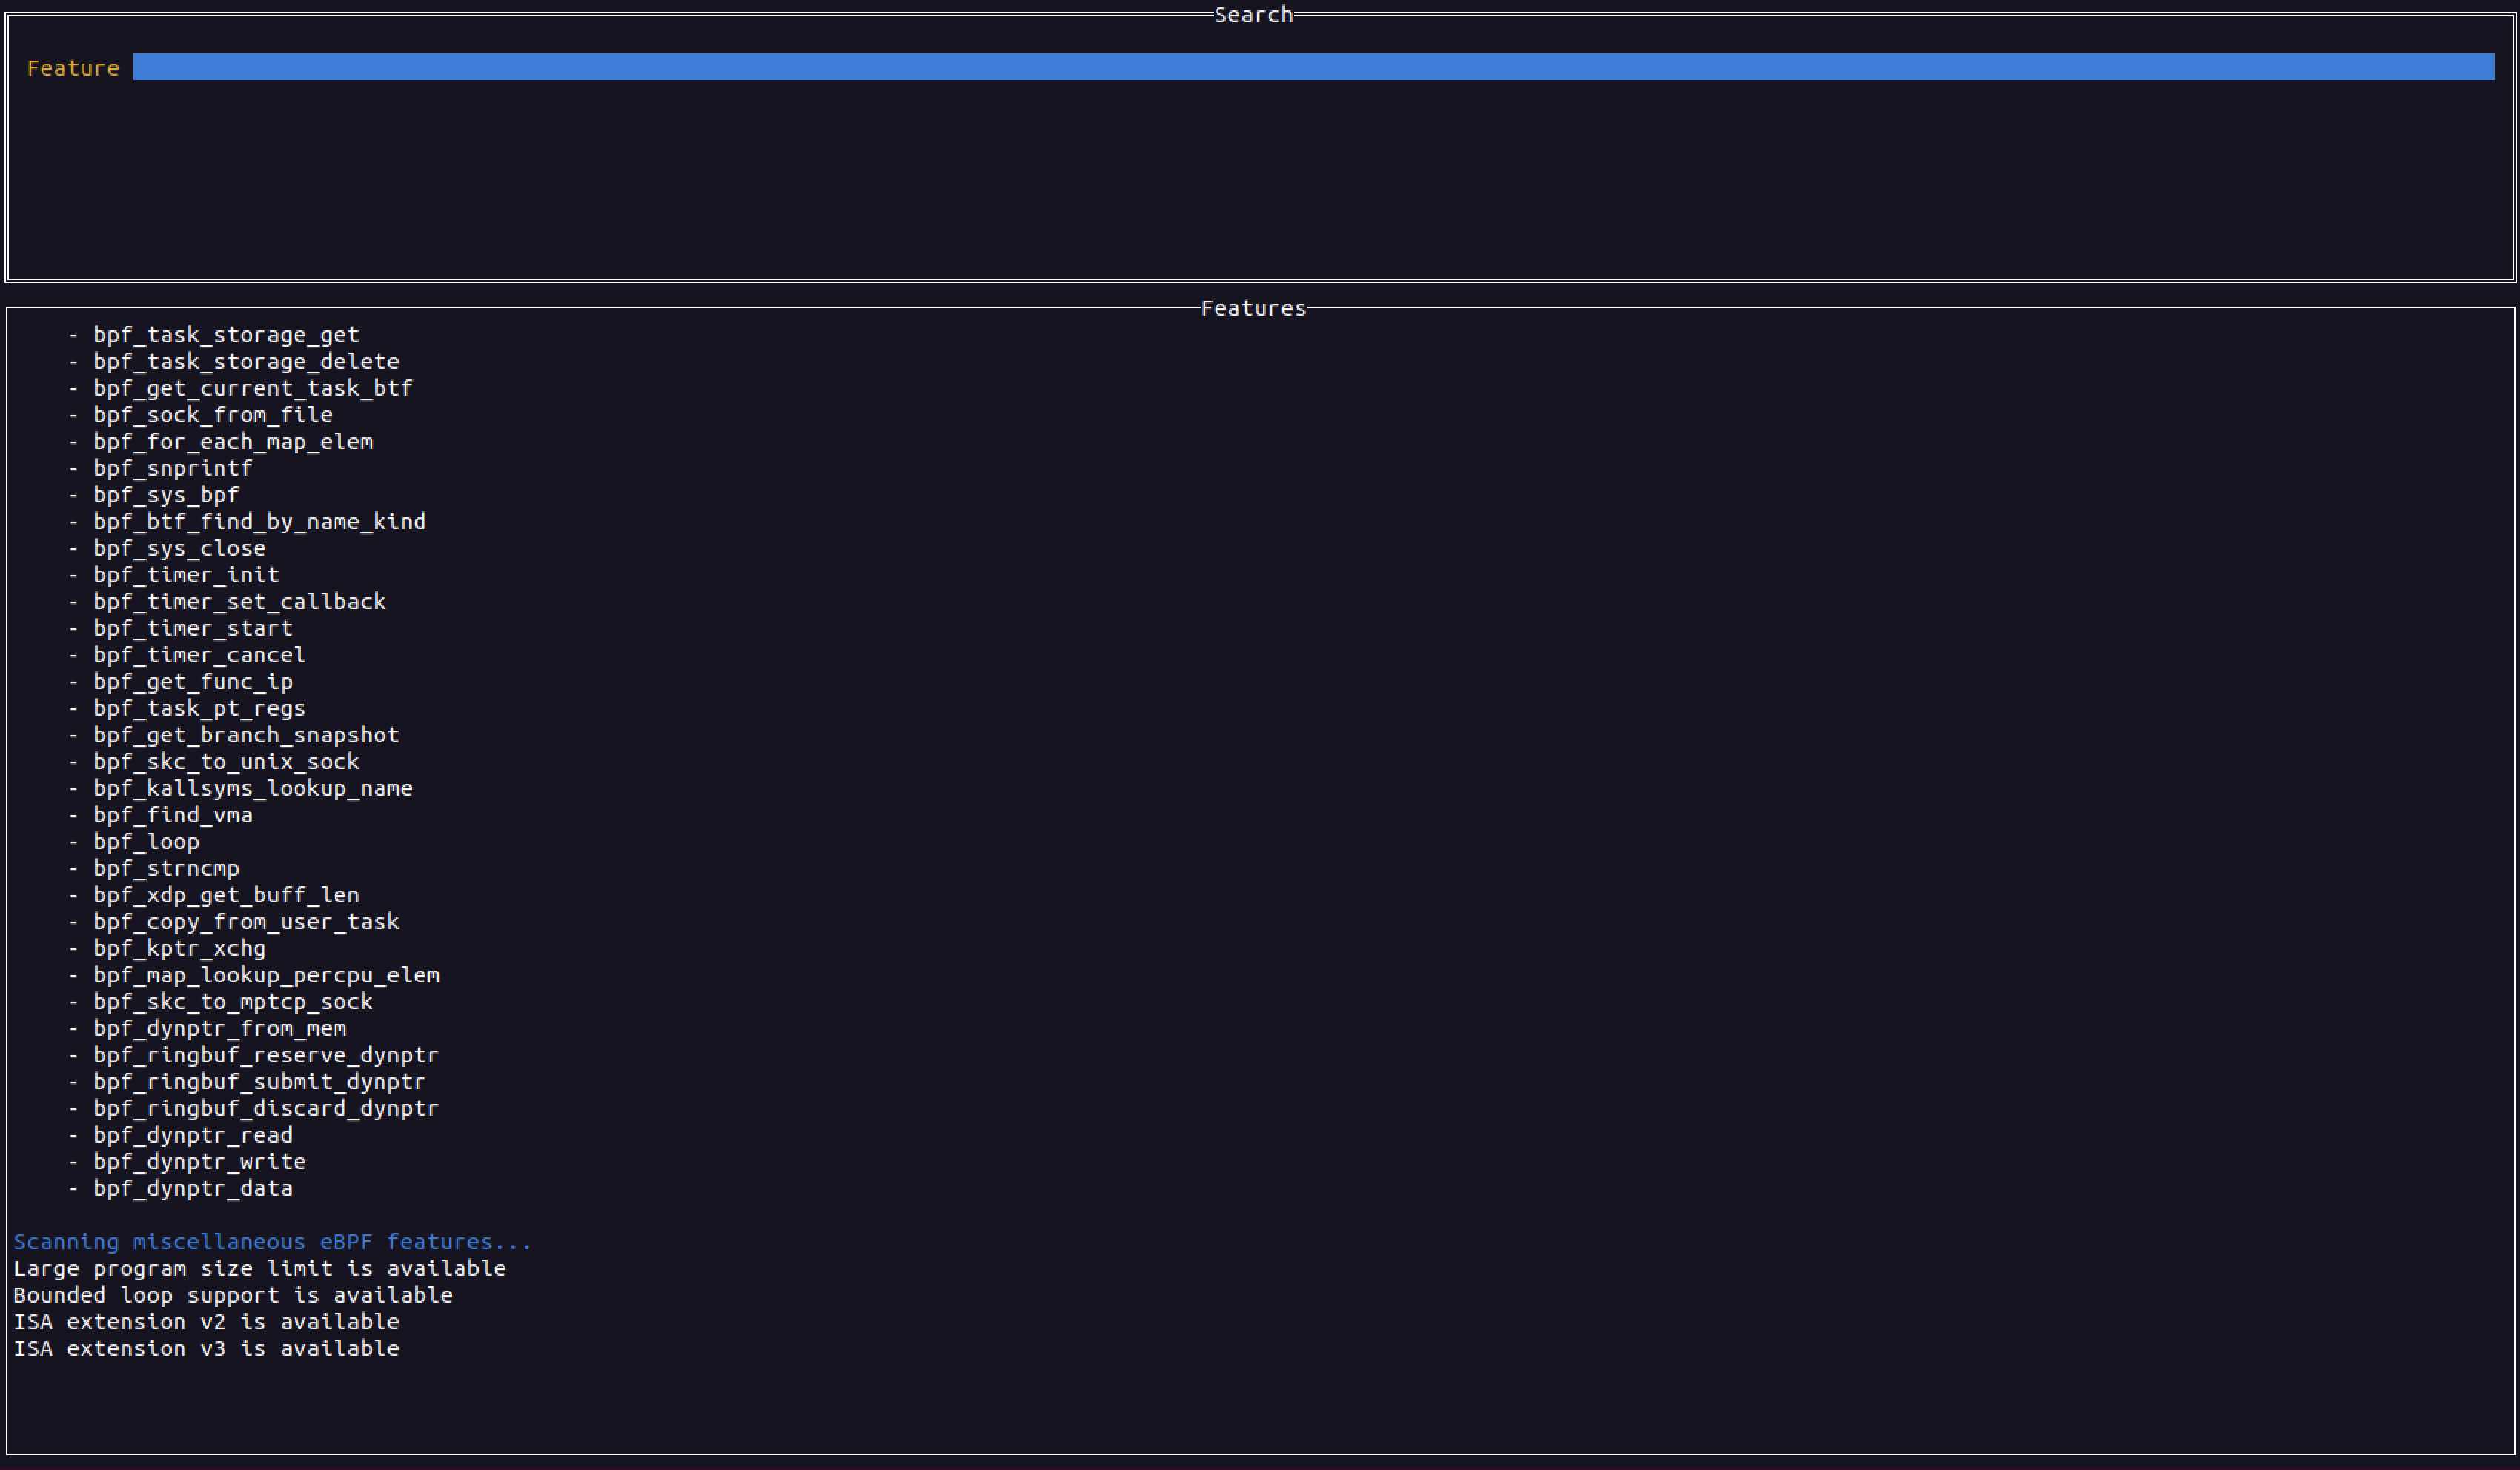 redcanaryco/ebpfmon
Terminal UI for real-time monitoring and inspection of eBPF programs and maps using bpftool, enabling live debugging and analysis of kernel-level…
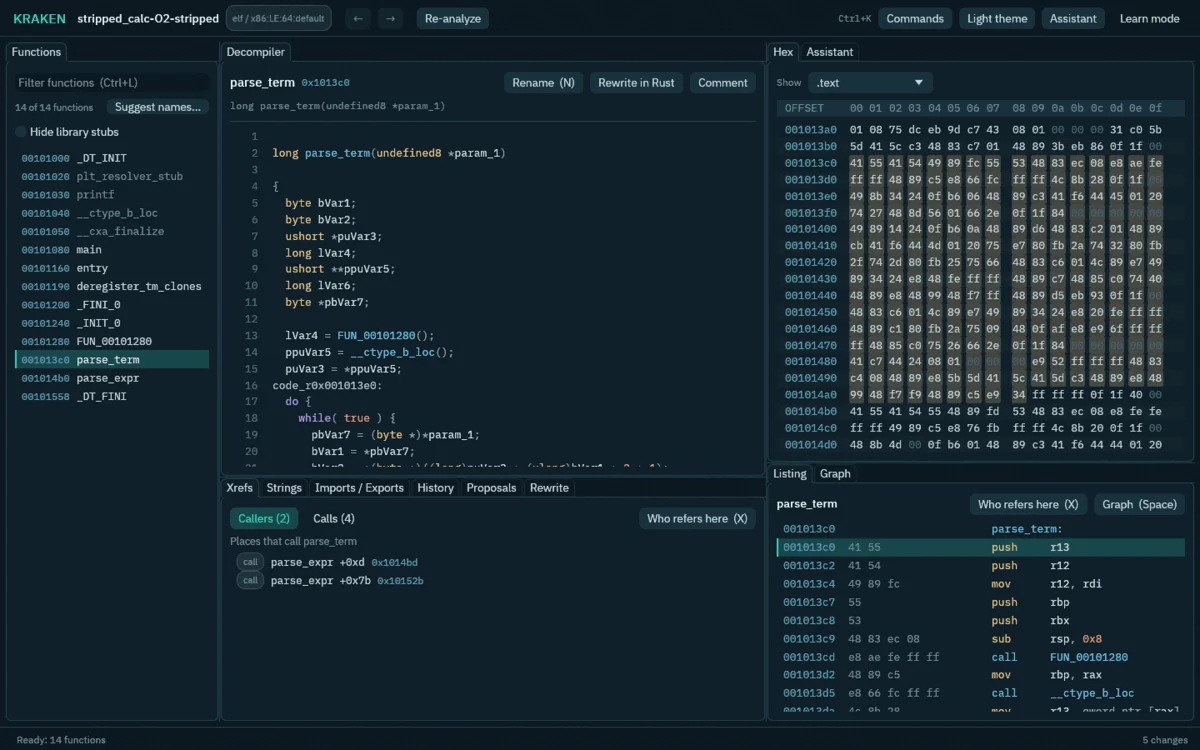 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
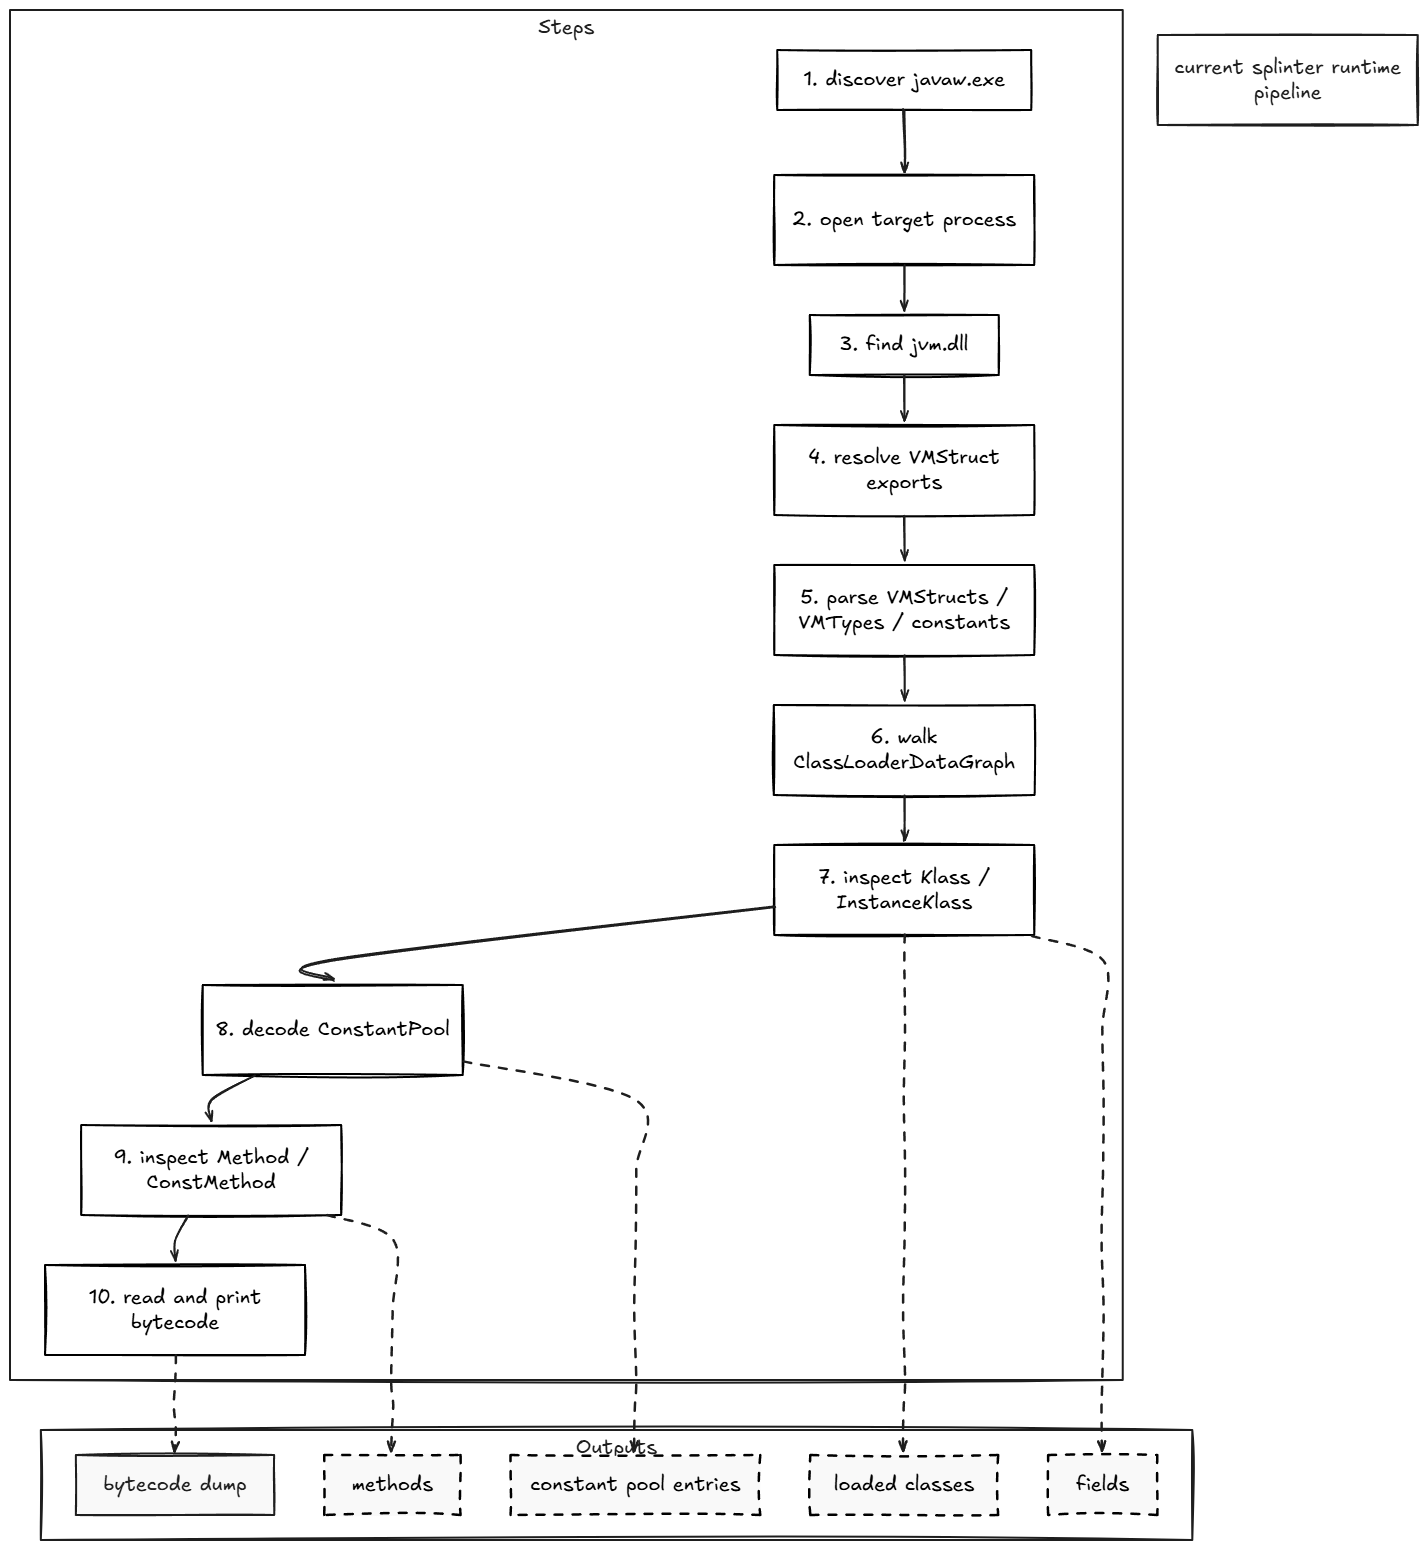 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode