
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/hugsy/cfb
Vulnerability AnalysisDebuggersFuzzing
GitHubhugsy/cfb

CFB

ProcMon-style IRP monitor for Windows drivers. Captures and logs I/O Request Packets via a kernel driver and user-land broker, outputting JSON for analysis and scripting.

View RepositoryWebsite
33568312 years agoReviewed by Kitploit
Share

logo

Build main Build dev Discord

What is it?

[!CAUTION] CFB is meant for research and debug purposes, it should never be used on production systems. Also BSoD may happen. You've been warned.

Canadian Furious Beaver is a ProcMon-style tool designed only for capturing IRPs sent to any Windows driver. It operates in 2 parts:

  1. the "Broker" combines both a user-land agent and a self-extractable driver (IrpMonitor.sys) that will install itself on the targeted system. After installing the driver, the broker will expose a TCP port listening (by default, on TCP/1337) and start collecting IRP from hooked drivers. The communication protocol was made to be simple by design (i.e. not secure) allowing any 3rd party tool to dump the driver IRPs from the same Broker easily (via simple JSON messages).

  2. the clients can connect to the broker, and will receive IRPs as a JSON message making it easy to view, or convert to another format.
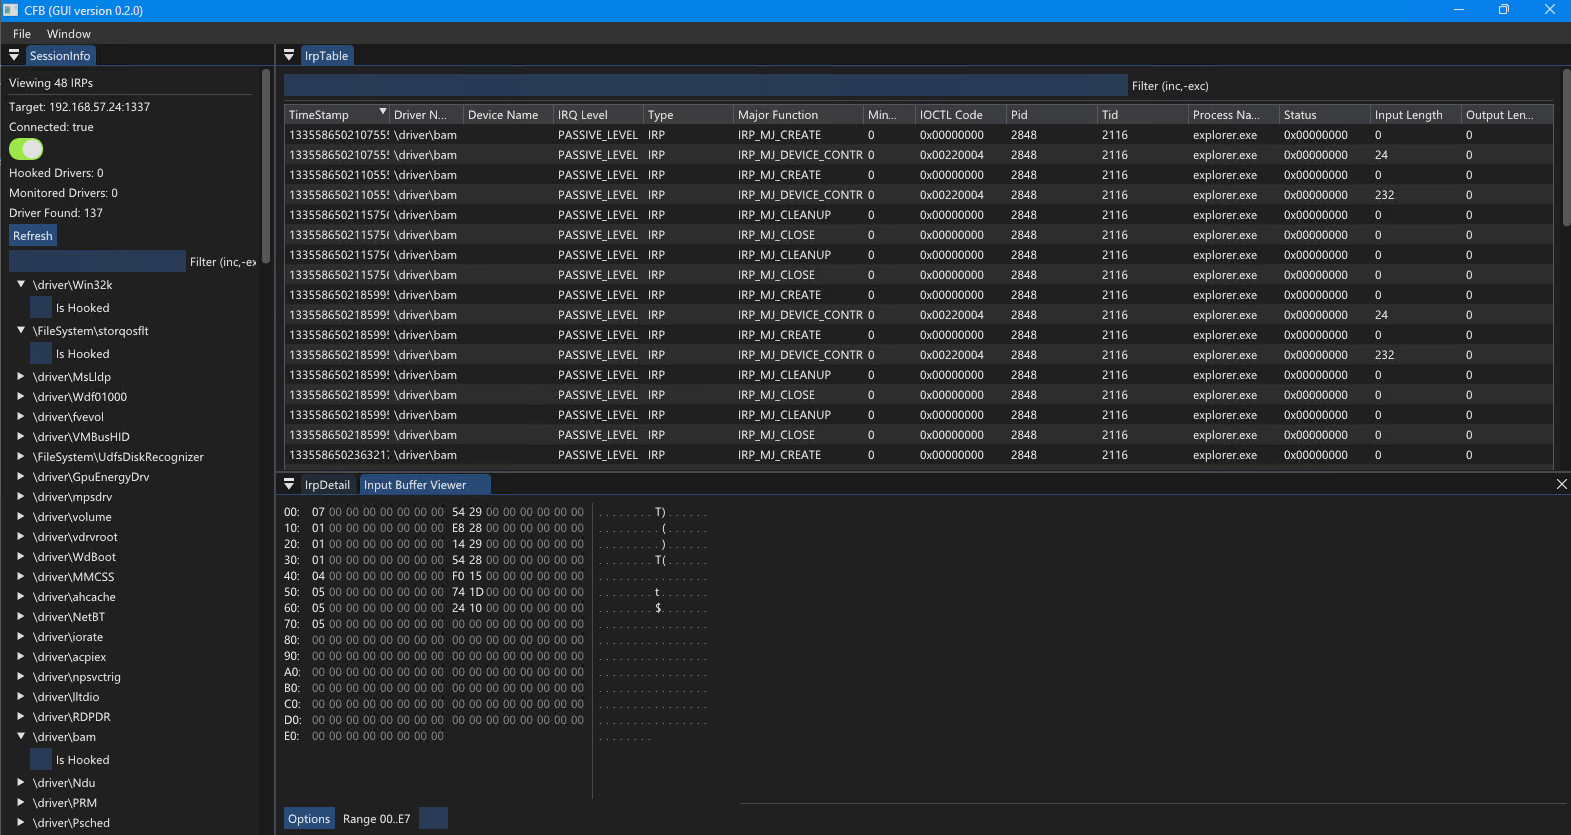
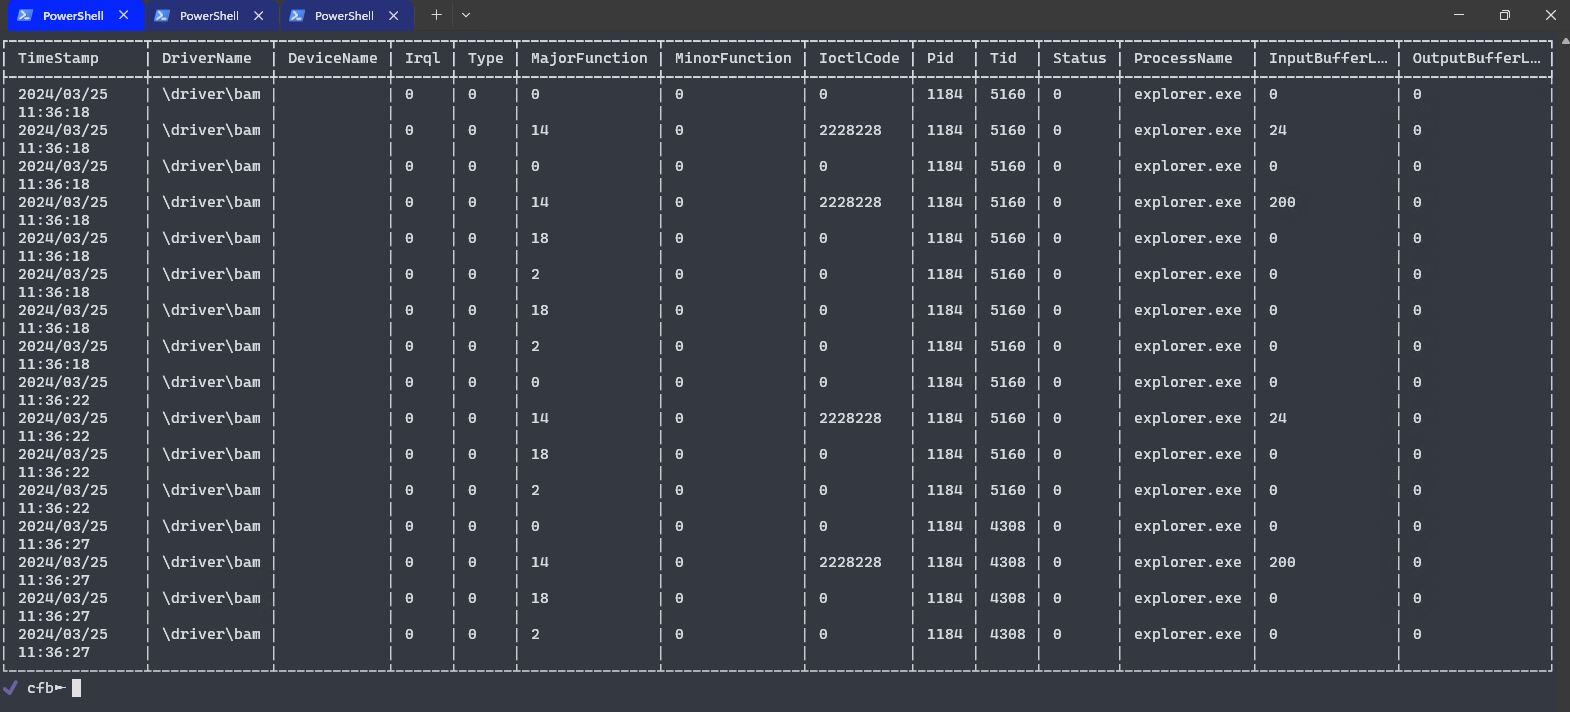
GUI

CLI

  1. IRPs (metadata, input/output buffers) can be stored to file on disk in the JSON format allowing for easy further scripting.

[!WARNING] Although the CFB driver (IrpMonitor.sys) should not violate patchguard, it however is only self-signed and so requires TestSigning enabled in the BCD

Why the name?

Because I had no idea for the name of this tool, so it was graciously generated by a script of mine.

Kudos

  • processhacker for their phnt header files
  • nlohmann for their json library
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →






