

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
splinter — Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode | Kitploit
Tools/GitHubGitHub/awrped/splinter
Dynamic Analysis (Sandboxing)Memory ForensicsDynamic Code Analysis (DAST)Reverse EngineeringDebuggersMalware AnalysisBinary Analysis
GitHubawrped/splinter

splinter

Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode

View Repository
80623 months agoReviewed by Kitploit
Share

splinter

splinter is a jvm analysis toolkit, allowing the user to view classes, methods, fields, constant pools and bytecode on runtime. this was made and tested on openjdk build 22.0.2+9-70

what is splinter?

usually, when you think of an analysis toolkit for the jvm, you would think it uses jni or jvmti, but not splinter!

splinter is actually external and has these capabilities right now:

  • can read hotspot vmstructs from a running process
  • can decode bytecode live over Method and ConstMethod

the long-term goal is for it to be a runtime jvm analysis toolkit for:
  • loaded class inspection
  • method and field inspection
  • constant-pool decoding
  • bytecode disassembly
  • class graph and metadata analysis

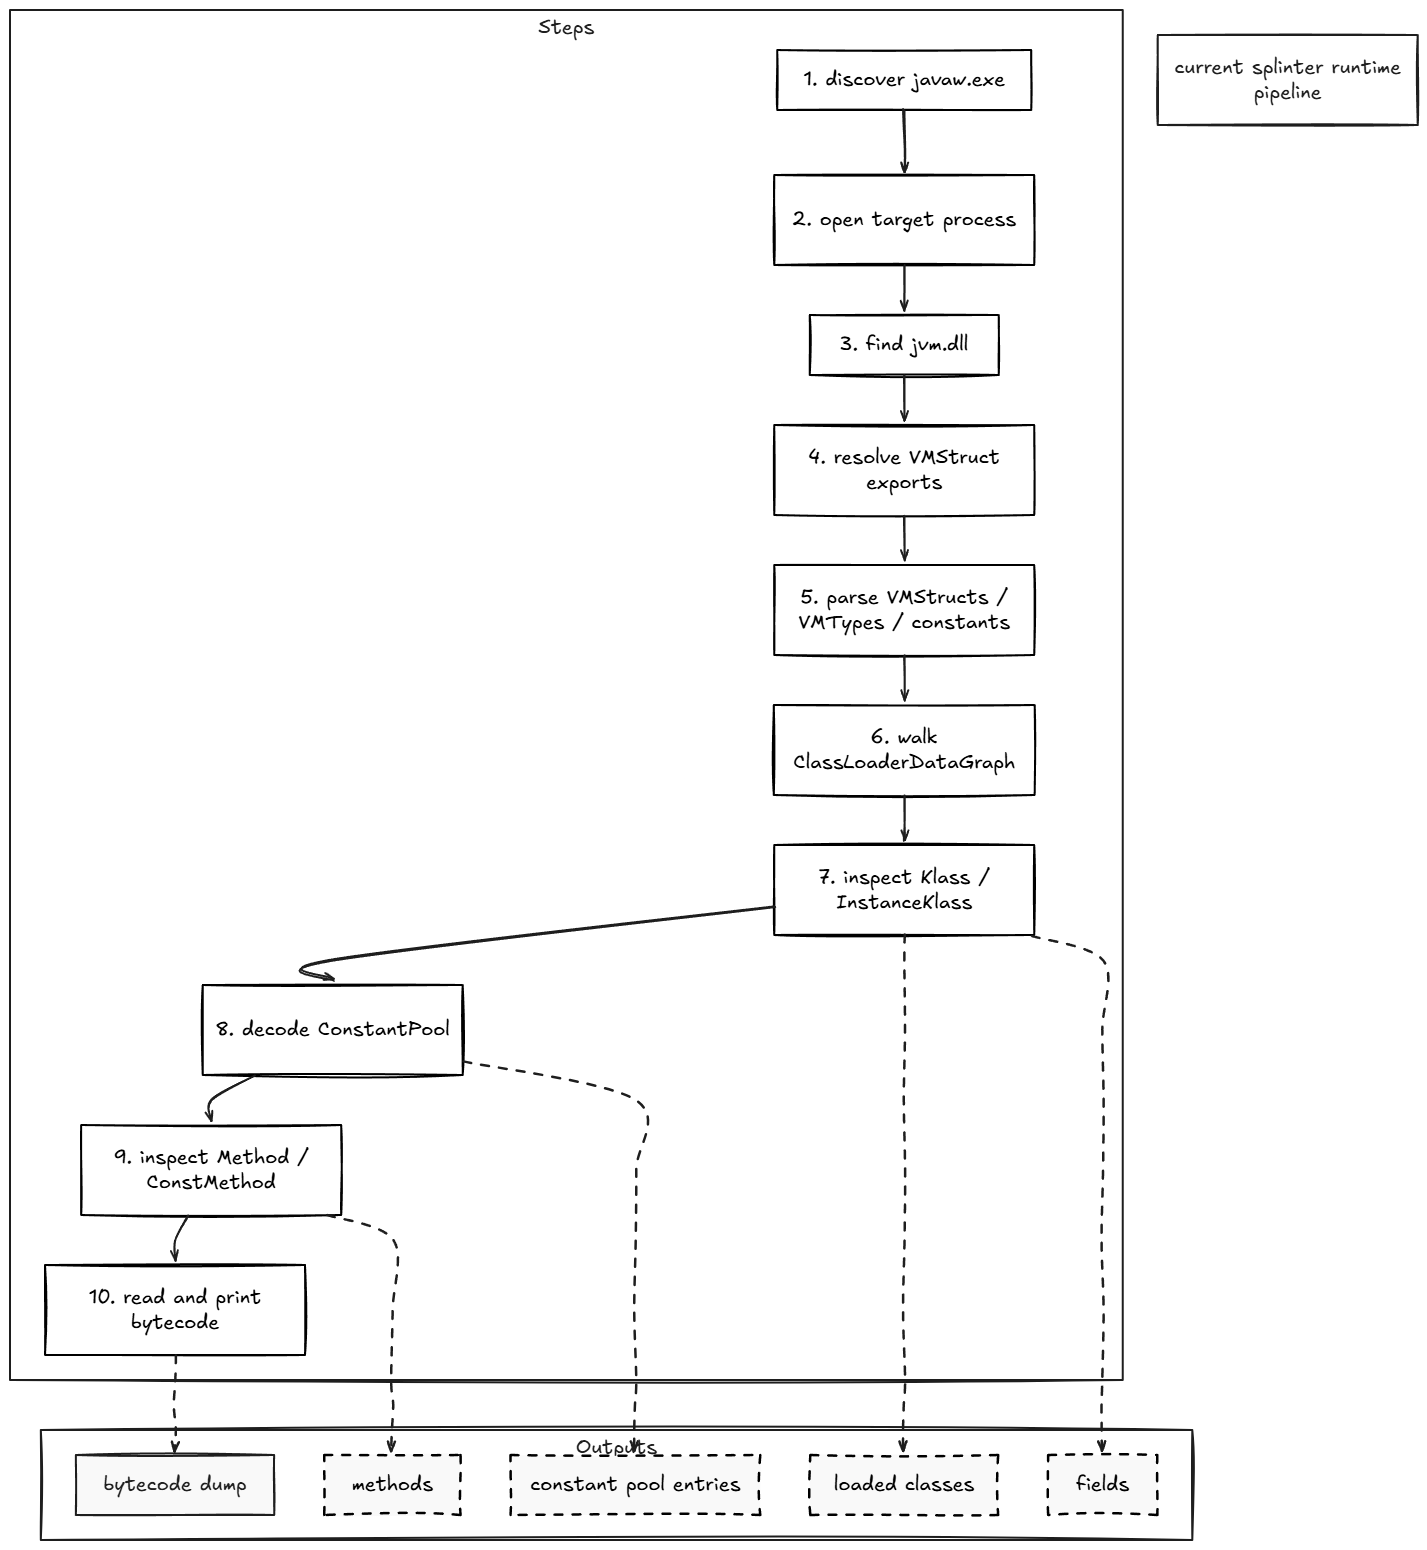
splinter current runtime pipeline

current state

the current code base is currently a foundation, but it still functions

as of writing this (3/11/2026), splinter can:

  • attach to a readable javaw.exe process automatically
  • locate jvm.dll in the target process
  • resolve HotSpot exported VMStruct tables from jvm.dll
  • parse:
    • VMStruct fields
    • VMTypes
    • HotSpot int constants
    • HotSpot long constants
  • list loaded klasses through ClassLoaderDataGraph
  • inspect Klass and InstanceKlass
  • decode constant-pool entries
  • decode HotSpot field streams from InstanceKlass::_fieldinfo_stream
  • inspect Method / ConstMethod
  • read live bytecodes
  • disassemble bytecode with HotSpot rewritten/runtime bytecode support

bytecode

one of the cooler parts of splinter is that it doesnt use classfile-format bytecode, it actually uses runtime bytecode instructions from the hotspots interpreter which is later read back to you as symbolic class/method/field references.

it matters because the hotspot actually tends to rewrite some instructions at runtime. we currently r handling:

  • invokedynamic encoded indexes
  • hotpsot fast bytecodes such as:
    • fast_iaccess_0
    • fast_igetfield
    • fast_aldc
    • invokehandle

splinter rewritten bytecode resolution

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →






