Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
CVE-2024-22120-RCE-with-gopher preview

CVE-2024-22120-RCE-with-gopher

GitHubispique/cve-2024-22120-rce-with-gopher

This is my exploit for CVE-2024-22120, which involves an SSRF vulnerability inside an XXE with a Gopher payload.
command-and-controlexploitationpenetration-testing+2
3
2 years ago
notionterm preview

notionterm

GitHubariary/notionterm

Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…


command-and-controlexploitationpayload-generation+3
1383 years ago
ultrasploiter preview

ultrasploiter

GitLabvqkro/ultrasploiter

A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
command-and-controlexploitationexploit-frameworks+9
6 days ago
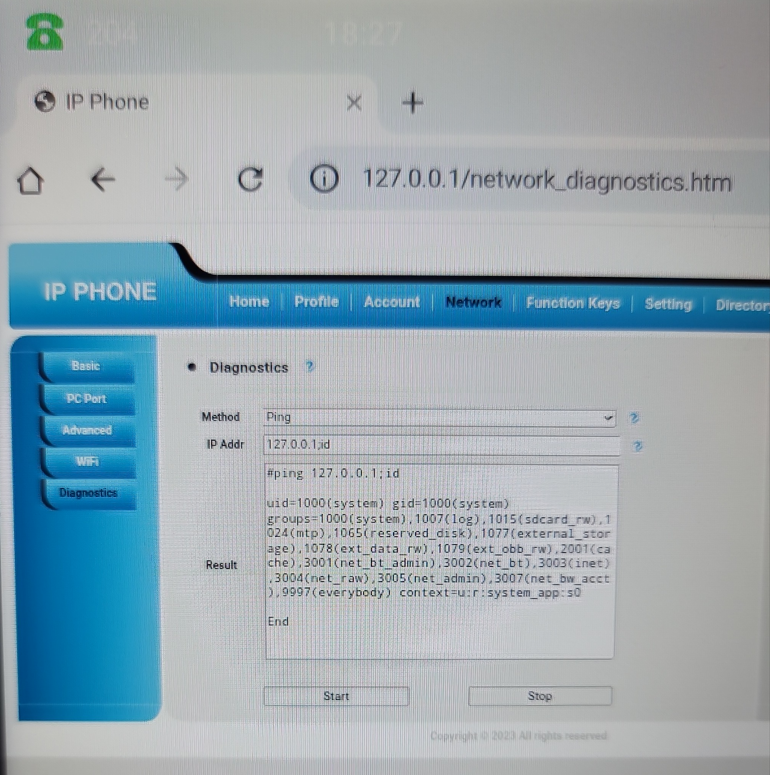
CVE-2025-57457 preview

CVE-2025-57457

GitHubrestdone/cve-2025-57457

Proof-of-concept for OS command injection in Curo UC300 IP phone admin panel, demonstrating arbitrary command execution via the IP Addr parameter.
command-and-controlexploitationpenetration-testing+2
1 year ago
refreshing-soap-exploit preview

refreshing-soap-exploit

GitHubrbowes-r7/refreshing-soap-exploit

A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
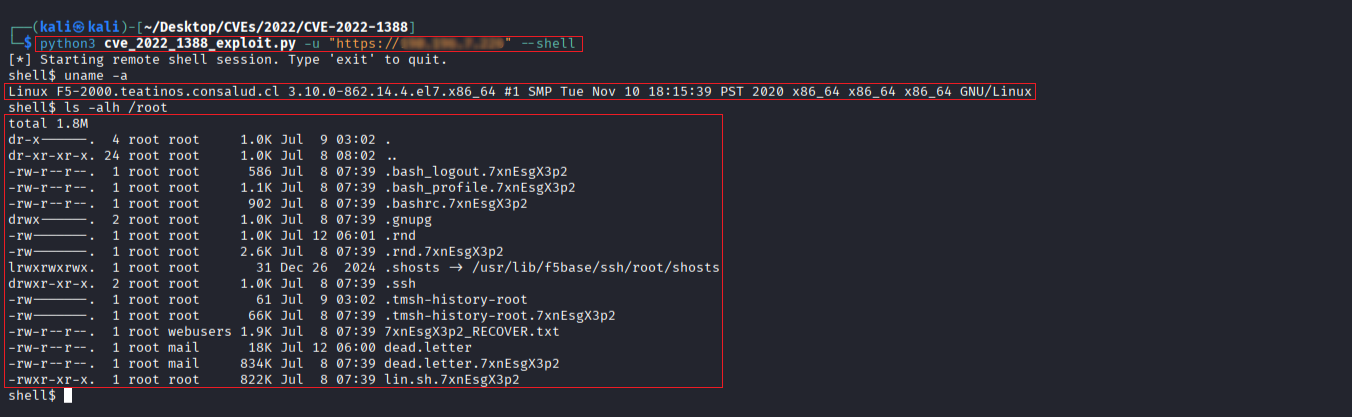
command-and-controlexploitationpayload-development+7
223 years ago
CVE-2022-1388 preview

CVE-2022-1388

GitHubr0otk3r/cve-2022-1388

Python exploit for CVE-2022-1388, an unauthenticated remote command execution vulnerability in F5 BIG-IP iControl REST. Supports single commands and…

command-and-controlexploitationpenetration-testing+3
1 year ago
BigFinger preview

BigFinger

GitHubcediegreyhat/bigfinger

CVE-2023-46747-RCE PoC

command-and-controlexploitationpenetration-testing+3
1 year ago
CVE-2020-5902 preview

CVE-2020-5902

GitHub0xblackash/cve-2020-5902

CVE-2020-5902

command-and-controlexploitationpenetration-testing+3
6 months ago
Cuteit preview

Cuteit

GitHubd4vinci/cuteit

IP obfuscator made to make a malicious ip a bit cuter
command-and-controlids-ips-evasionpayload-generation+4
5461 year ago
CVE-2021-4045 preview

CVE-2021-4045

GitHubhacefresko/cve-2021-4045

Exploit for command injection vulnerability found in uhttpd binary from TP-Link Tapo c200 IP camera

binary-analysiscommand-and-controlembedded-systems-security+6
1201 year ago
CVE-2022-1388-rs preview

CVE-2022-1388-rs

GitHubaancw/cve-2022-1388-rs

CVE-2022-1388 F5 BIG-IP iControl REST Auth Bypass RCE written in Rust

command-and-controlexploitationpenetration-testing+3
24 years ago
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis preview

StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

GitHubkaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

command-and-controldata-exfiltrationdigital-forensics+7
327 days ago
Nuclei-Template-Exploit-F5-BIG-IP-iControl-REST-Auth-Bypass-RCE-Command-Parameter preview

Nuclei-Template-Exploit-F5-BIG-IP-iControl-REST-Auth-Bypass-RCE-Command-Parameter

GitHubmrcl0wnlab/nuclei-template-exploit-f5-big-ip-icontrol-rest-auth-bypass-rce-command-parameter

CVE-2022-1388 is an authentication bypass vulnerability in the REST component of BIG-IP’s iControl API that was assigned a CVSSv3 score of…

command-and-controlexploitationpayload-generation+3
64 years ago
CVE-2022-1388 preview

CVE-2022-1388

GitHubwrin9/cve-2022-1388

Proof-of-concept and exploit for CVE-2022-1388, a remote command execution vulnerability in F5 BIG-IP, with command execution capability via pocsuite.
command-and-controlexploitationpenetration-testing+2
4 years ago
DblTekGoIPPwn preview

DblTekGoIPPwn

GitHubjacobmisirian/dbltekgoippwn

Tool to check if an IP of a DblTek GoIP is vulnerable to a challenge-response login system, send SMS messages from the system, execute remote…
command-and-controlexploitationpenetration-testing+2
646 years ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
command-and-controldata-exfiltrationmalware-analysis+4
11 month ago
MCPJam-Inspector-1.4.2-Remote-Code-Execution-CVE-2026-23744 preview

MCPJam-Inspector-1.4.2-Remote-Code-Execution-CVE-2026-23744

GitHubafifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744

Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.

command-and-controlexploitationpayload-generation+3
4 months ago
CVE-2022-46169 preview

CVE-2022-46169

GitHub0xn7y/cve-2022-46169

Exploit for CVE-2022-46169

authentication-authorizationcommand-and-controlexploitation+3
12 years ago
Previous1234Next