
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-57457 — Proof-of-concept for OS command injection in Curo UC300 IP phone admin panel, demonstrating arbitrary command execution via the IP Addr parameter. | Kitploit
Tools/GitHubGitHub/restdone/cve-2025-57457
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and Control
GitHubrestdone/cve-2025-57457

CVE-2025-57457

Proof-of-concept for OS command injection in Curo UC300 IP phone admin panel, demonstrating arbitrary command execution via the IP Addr parameter.

View Repository
371 year agoNot yet reviewed
Share

OS Command Injection in CURO UC300 IP Phone

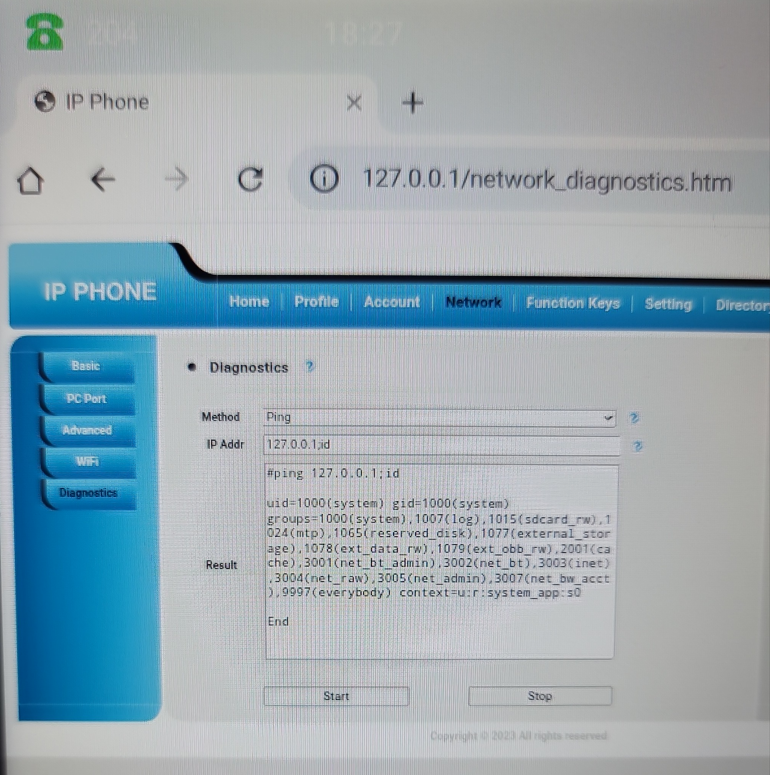
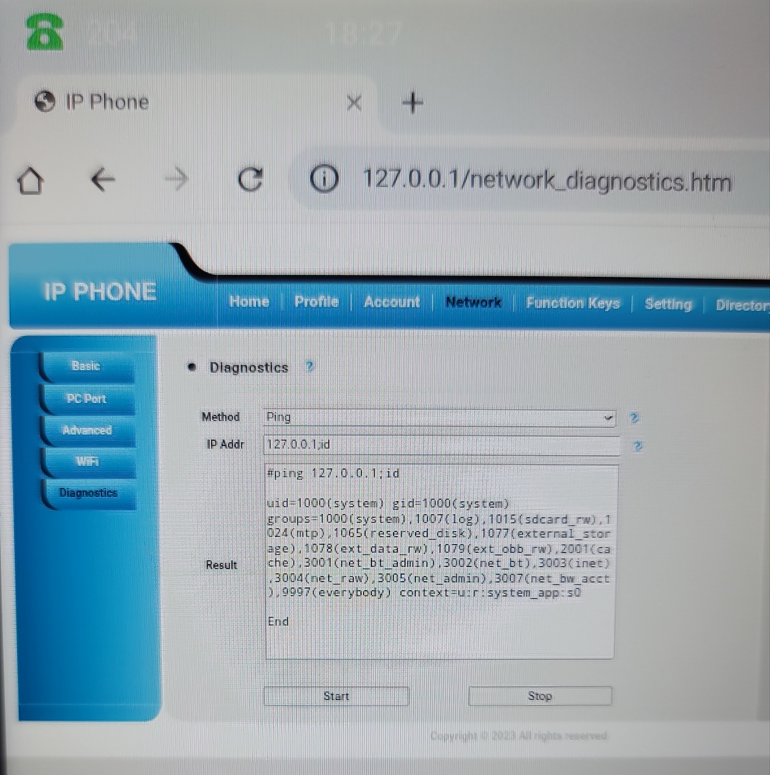
An OS Command Injection vulnerability in the Admin panel in Curo UC300 5.42.1.7.1.63R1 allows local attackers to inject arbitrary OS Commands via the "IP Addr" parameter.
image

PoC: https://github.com/restdone/CVE-2025-57457/blob/main/os_commandinject.mp4

Step

  1. Login to the admin panel of the UC300 (IP of the phone and port 80)
  2. Browse to Network, than Diagnostics
  3. Inject OS Command at IP Addr field.
  4. Click Start and exeucte the Linux Command on the phone.

Timeline

3rd July 2025:

Reported the issue to the vendor. The vendor responded on the same day.

4th July 2025:

The vendor raised the issue internally for furthter investigation and confirmation

19th September 2025:

The vendor confirmed the issue, conducted investigation, developed updated firmware, tested the updated firmware and rolled out to the production of the affected handset.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    509
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    469
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    343
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    310
  • 5

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    306
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    301

Explore all tools

Browse our collection of tools

View all tools →




