
CVE-2026-20841
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
command-and-controlexploitationpayload-development+3
1
hamzamalik3461/cve-2026-20841🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 bishopfox/sliver
Adversary Emulation Framework
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
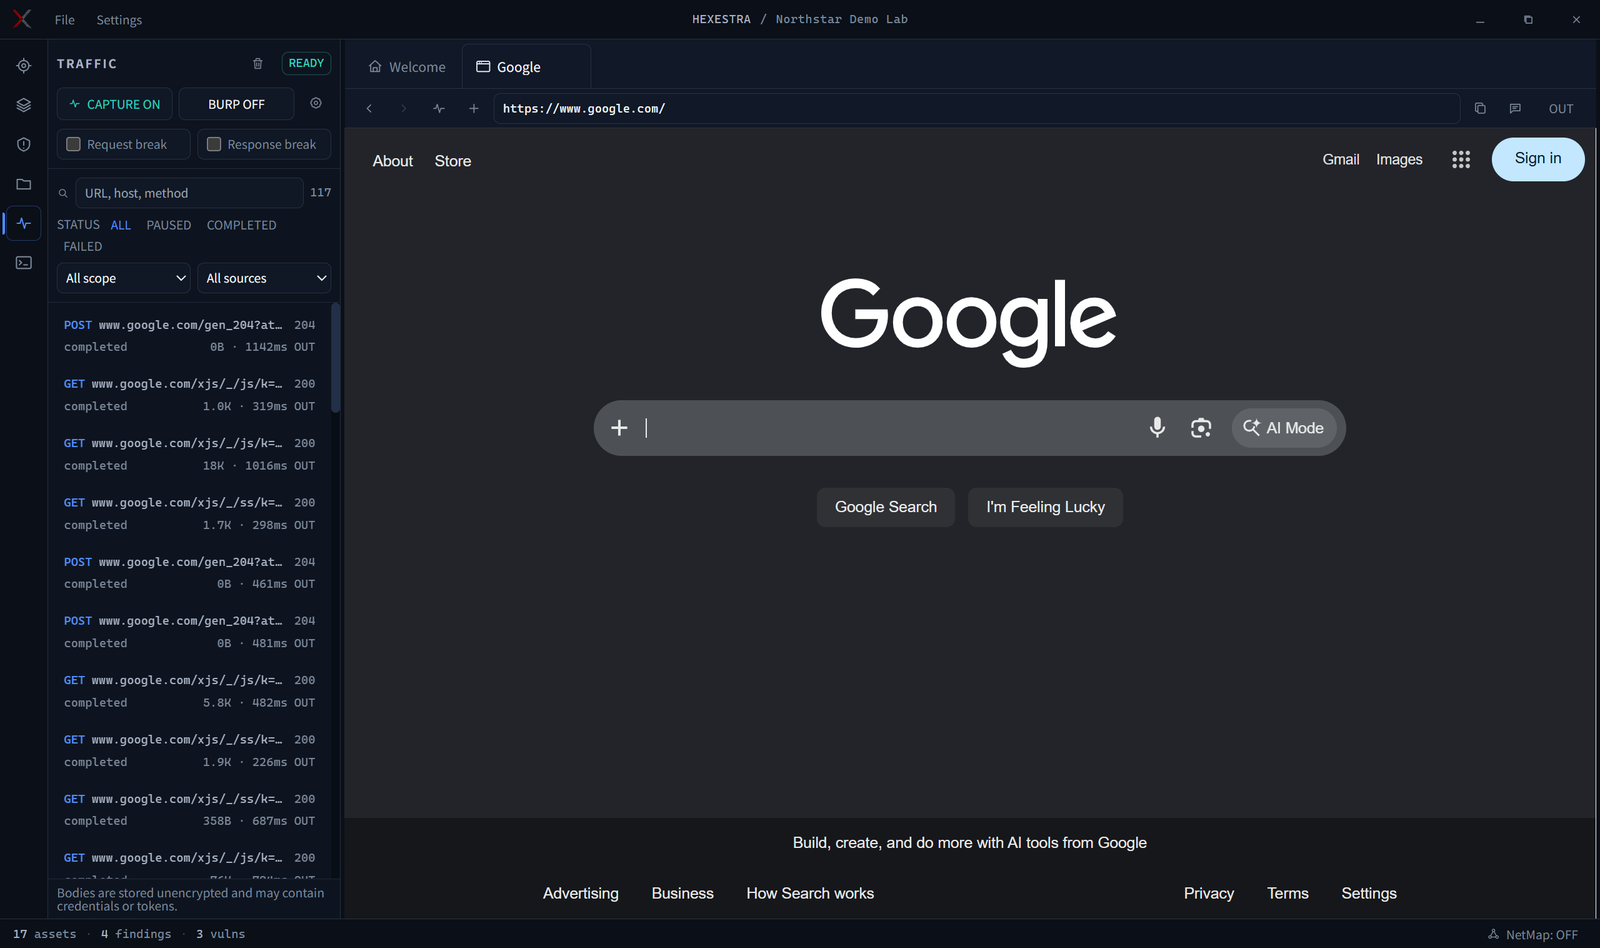 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 k3ystr0k3r/metis
Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 devzero-security/redstackpro
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…
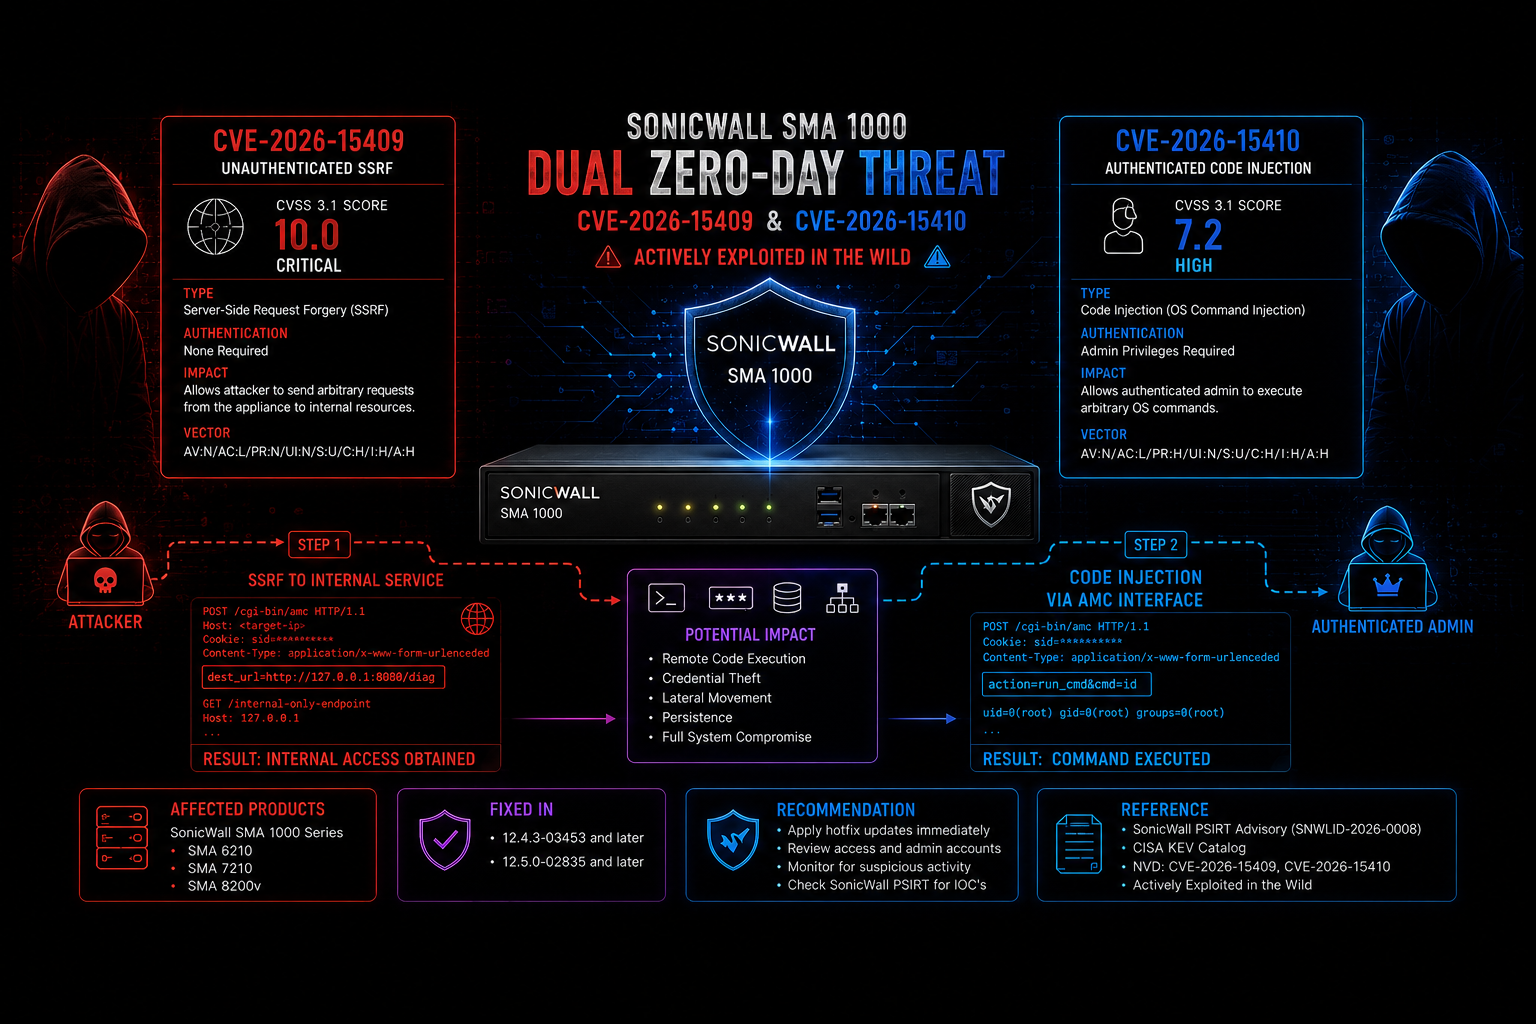 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
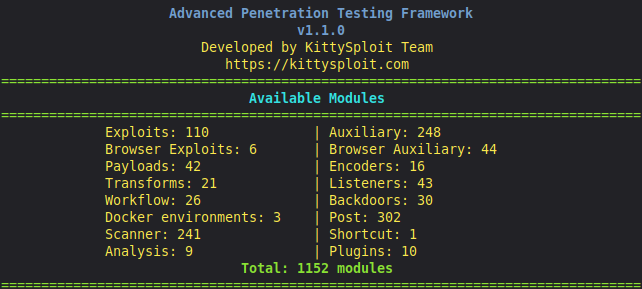 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 dennisdgr/cve-2026-44011-poc
Authenticated Craft CMS RCE PoC for CVE-2026-44011
 nth347/mediawiki-cve-2026-100382
Docker lab reproducing CVE-2026-100382: unauthenticated argument-injection RCE in MediaWiki ExternalData's #get_program_data, with PoC payloads and…