beef
 beefproject/beef
The Browser Exploitation Framework Project
command-and-controlexploitationexploit-frameworks+8
beefproject/beefThe Browser Exploitation Framework Project
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 ghostmanager/ghostwriter
The SpecterOps project management and reporting engine
 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
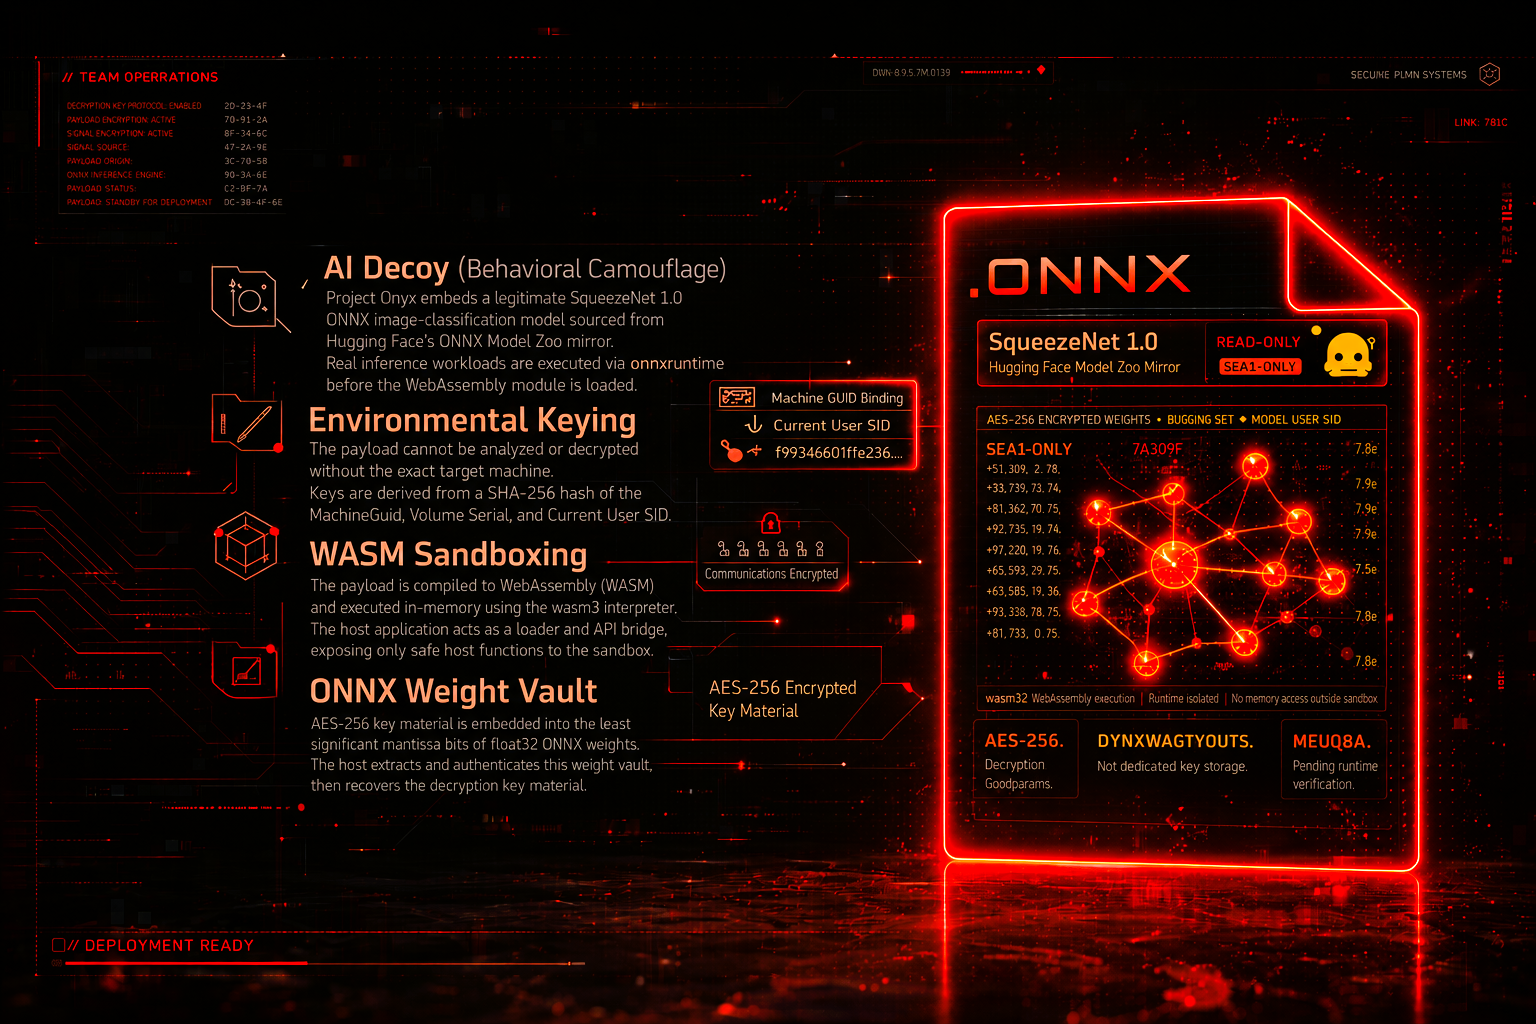 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
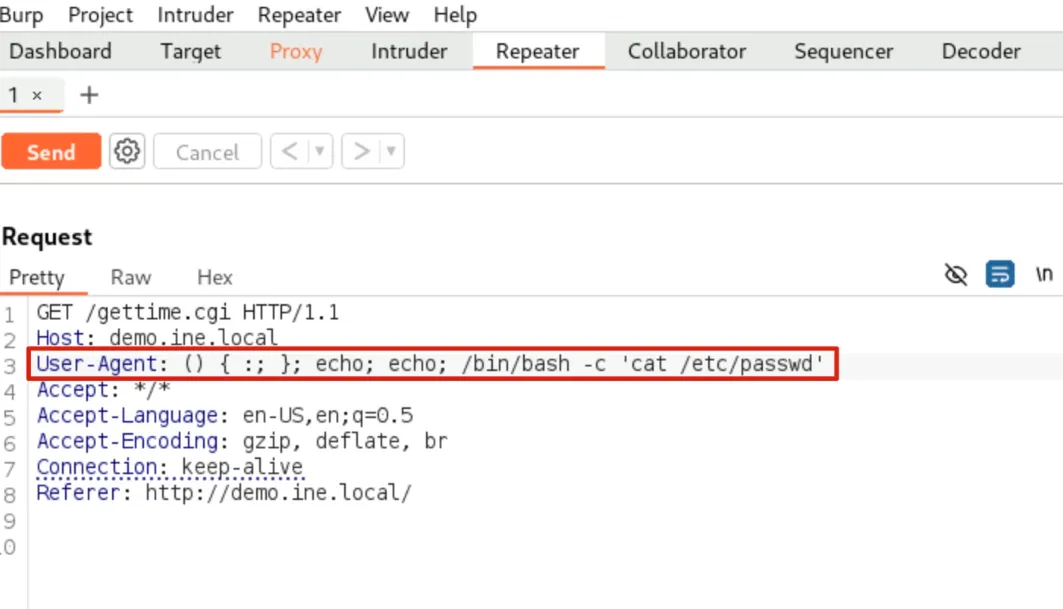 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 cyberbelly/poc-cve-2019-1003030
PoC for jenkins 2.63 CVE-2019-1003030
 synacktiv/livepyre
A tool designed to exploit CVE-2025-54068 and Remote Command Execution if the APP_KEY of the Livewire project is known.
 qmadev/tf-mythic-azure
Automatically deploying Mythic C2 in Azure using Terraform
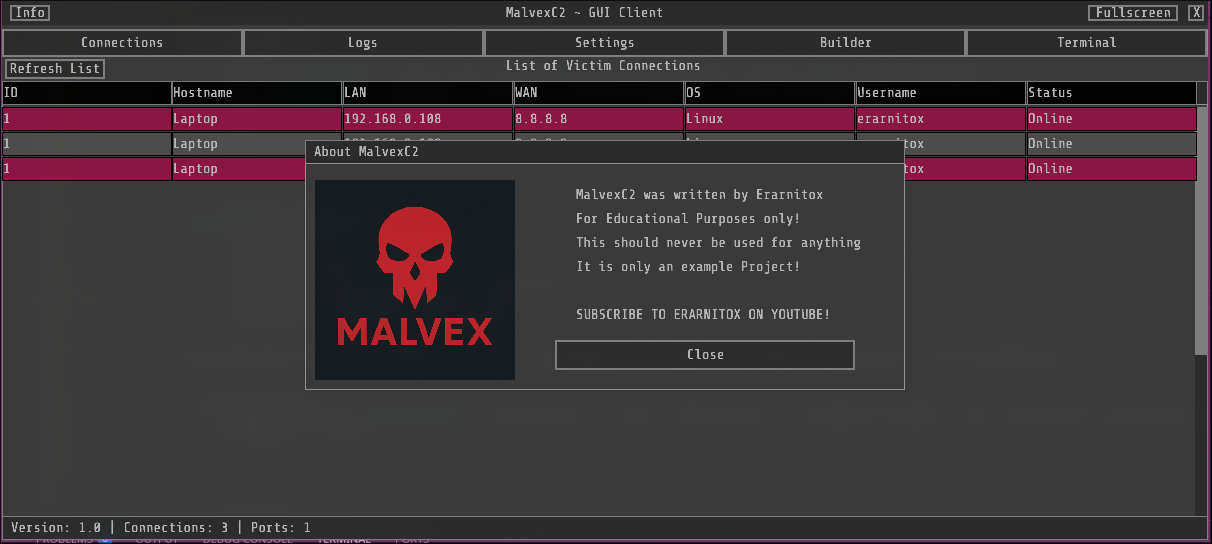 erarnitox/malvexc2
A simple C2 Framework written in modern C++
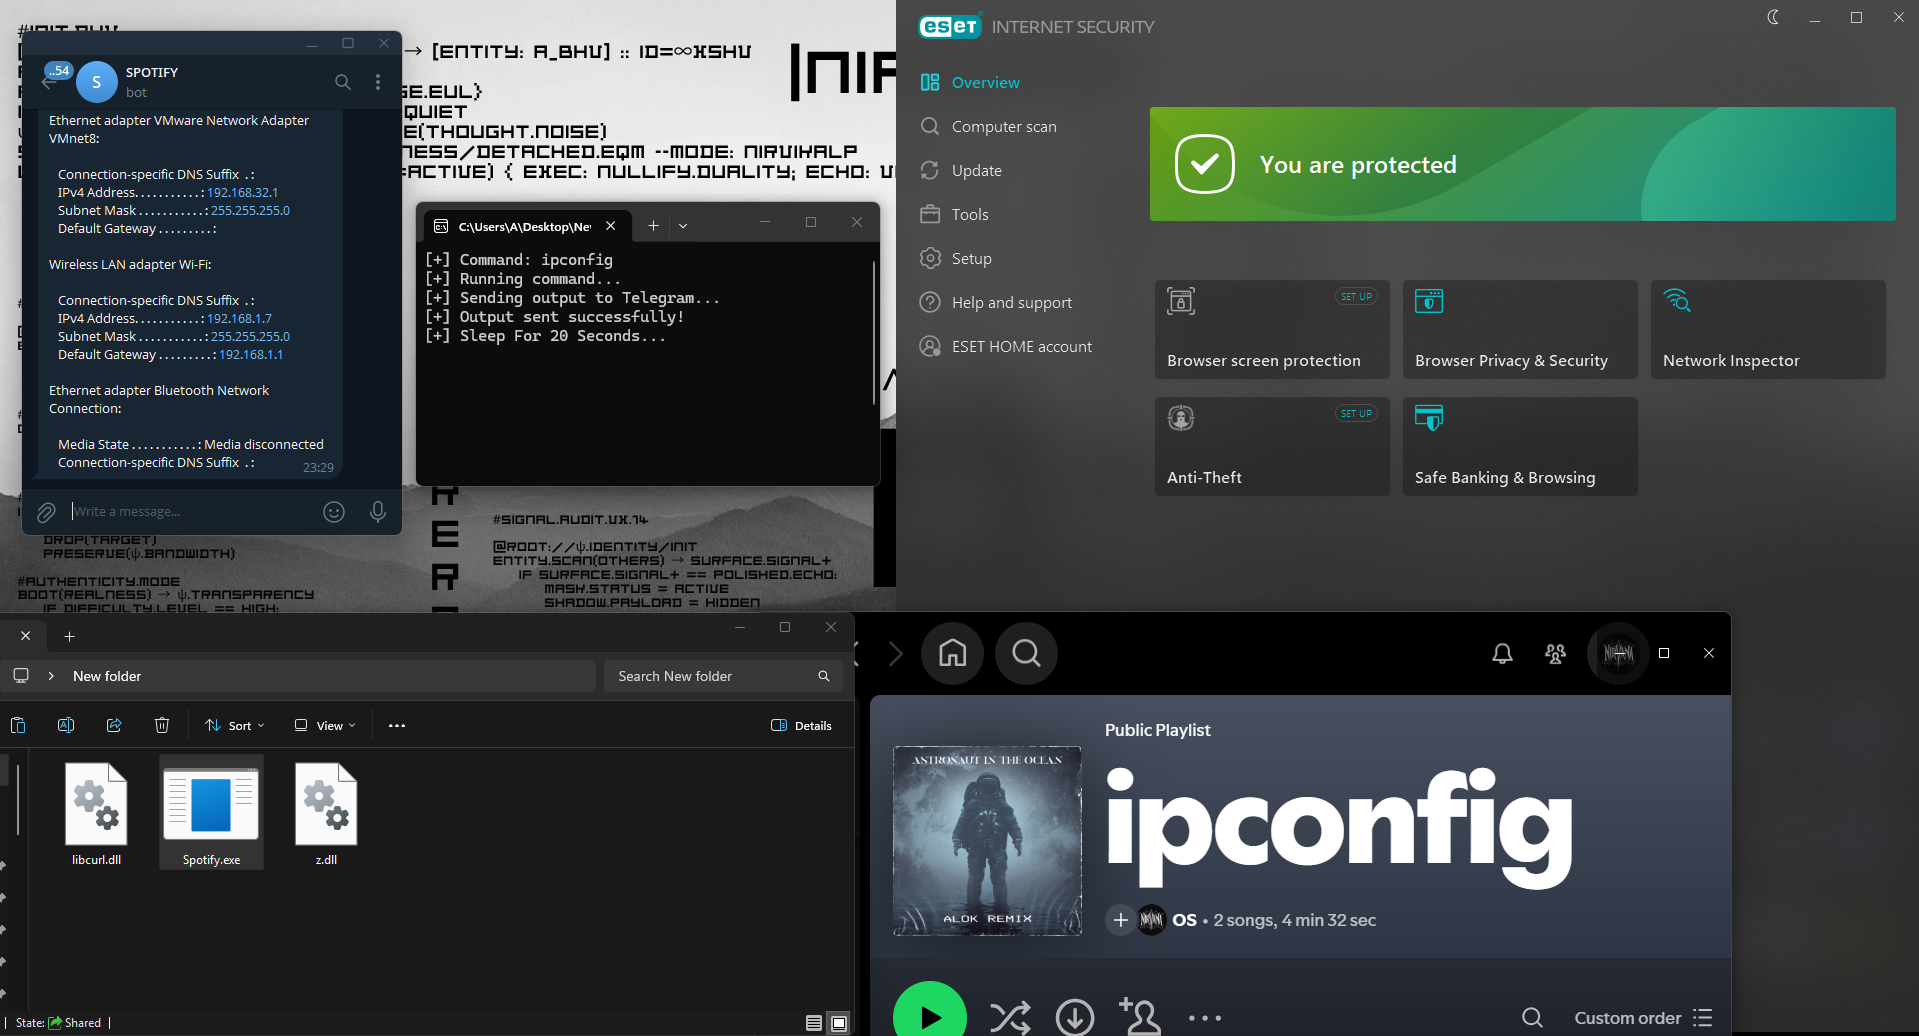 nirvanaon/spotifyc2
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…
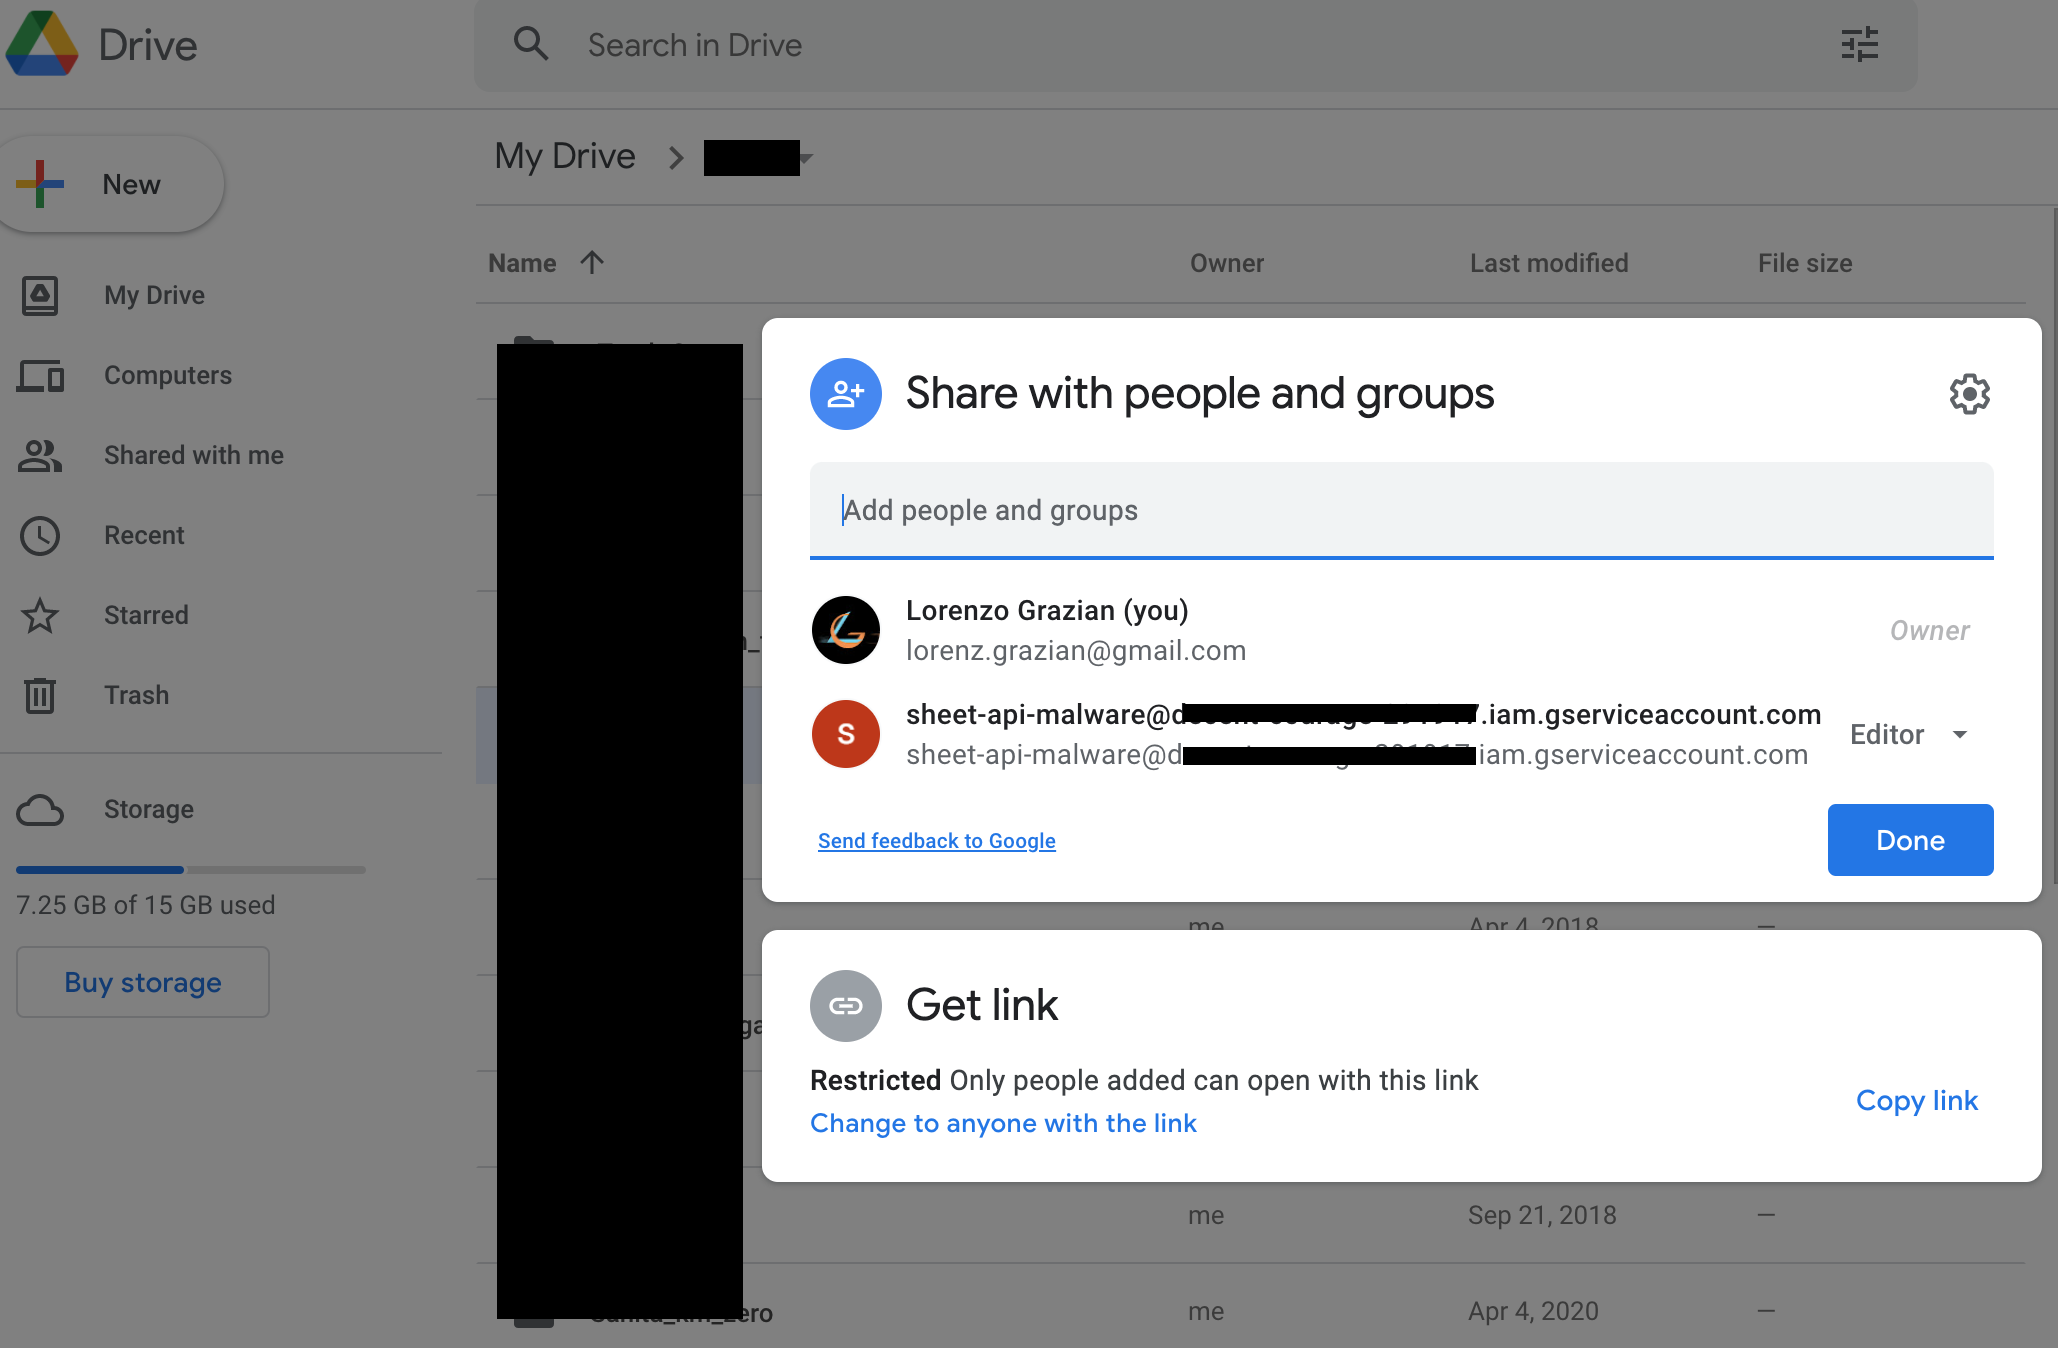 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 gagaltotal/cve-2026-10523-ivanti-sentry
Proof-of-concept detection tool for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520, CVE-2026-10523).…