
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
153 results
CVE-2025-39247 preview

CVE-2025-39247

GitHubsita-technologies/cve-2025-39247

HikCentral Professional - Pre-Auth License ActiveCode Leak
binary-analysiscryptographyexploitation+6
5 months ago
CVE-2022-36163 preview

CVE-2022-36163

GitHubmaherazzouzi/cve-2022-36163

Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…

binary-analysisexploitationfuzzing+2
14 years ago
CVE-2017-8481 preview

CVE-2017-8481

GitHubtamatahyt/cve-2017-8481

Exploit code for CVE-2017-8481, a Windows privilege escalation vulnerability.
binary-analysisexploitationinformation-gathering+2
1 year ago
aaLogger preview

aaLogger

GitHubusscltd/aalogger

CVE-2017-9627 CVE-2017-9629 CVE-2017-9631

binary-analysisexploitationfuzzing+3
5 years ago
CVE-2024-24684 preview

CVE-2024-24684

GitHubspiralbl0ck/cve-2024-24684

Crash File ( Poc for CVE-2024-24684)

binary-analysisexploitationinformation-gathering+2
2 years ago
MANTIS preview

MANTIS

GitHubfareedfauzi/mantis

Multi-Sources Analysis & Threat Intelligence Search

ai-securitybinary-analysisinformation-gathering+7
241 day ago
Detect-It-Easy preview

Detect-It-Easy

GitHubhorsicq/detect-it-easy

Program for determining types of files for Windows, Linux and MacOS.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.3k22h 7m ago
dnSpy preview

dnSpy

GitHubdnspyex/dnspy

Unofficial revival of the well known .NET debugger and assembly editor, dnSpy

ai-assisted-reversingbinary-analysisbinary-exploitation+10
10.9k1 day ago
flare-vm preview

flare-vm

GitHubmandiant/flare-vm

A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
binary-analysisdebuggersdigital-forensics+10
8.9k26 days ago
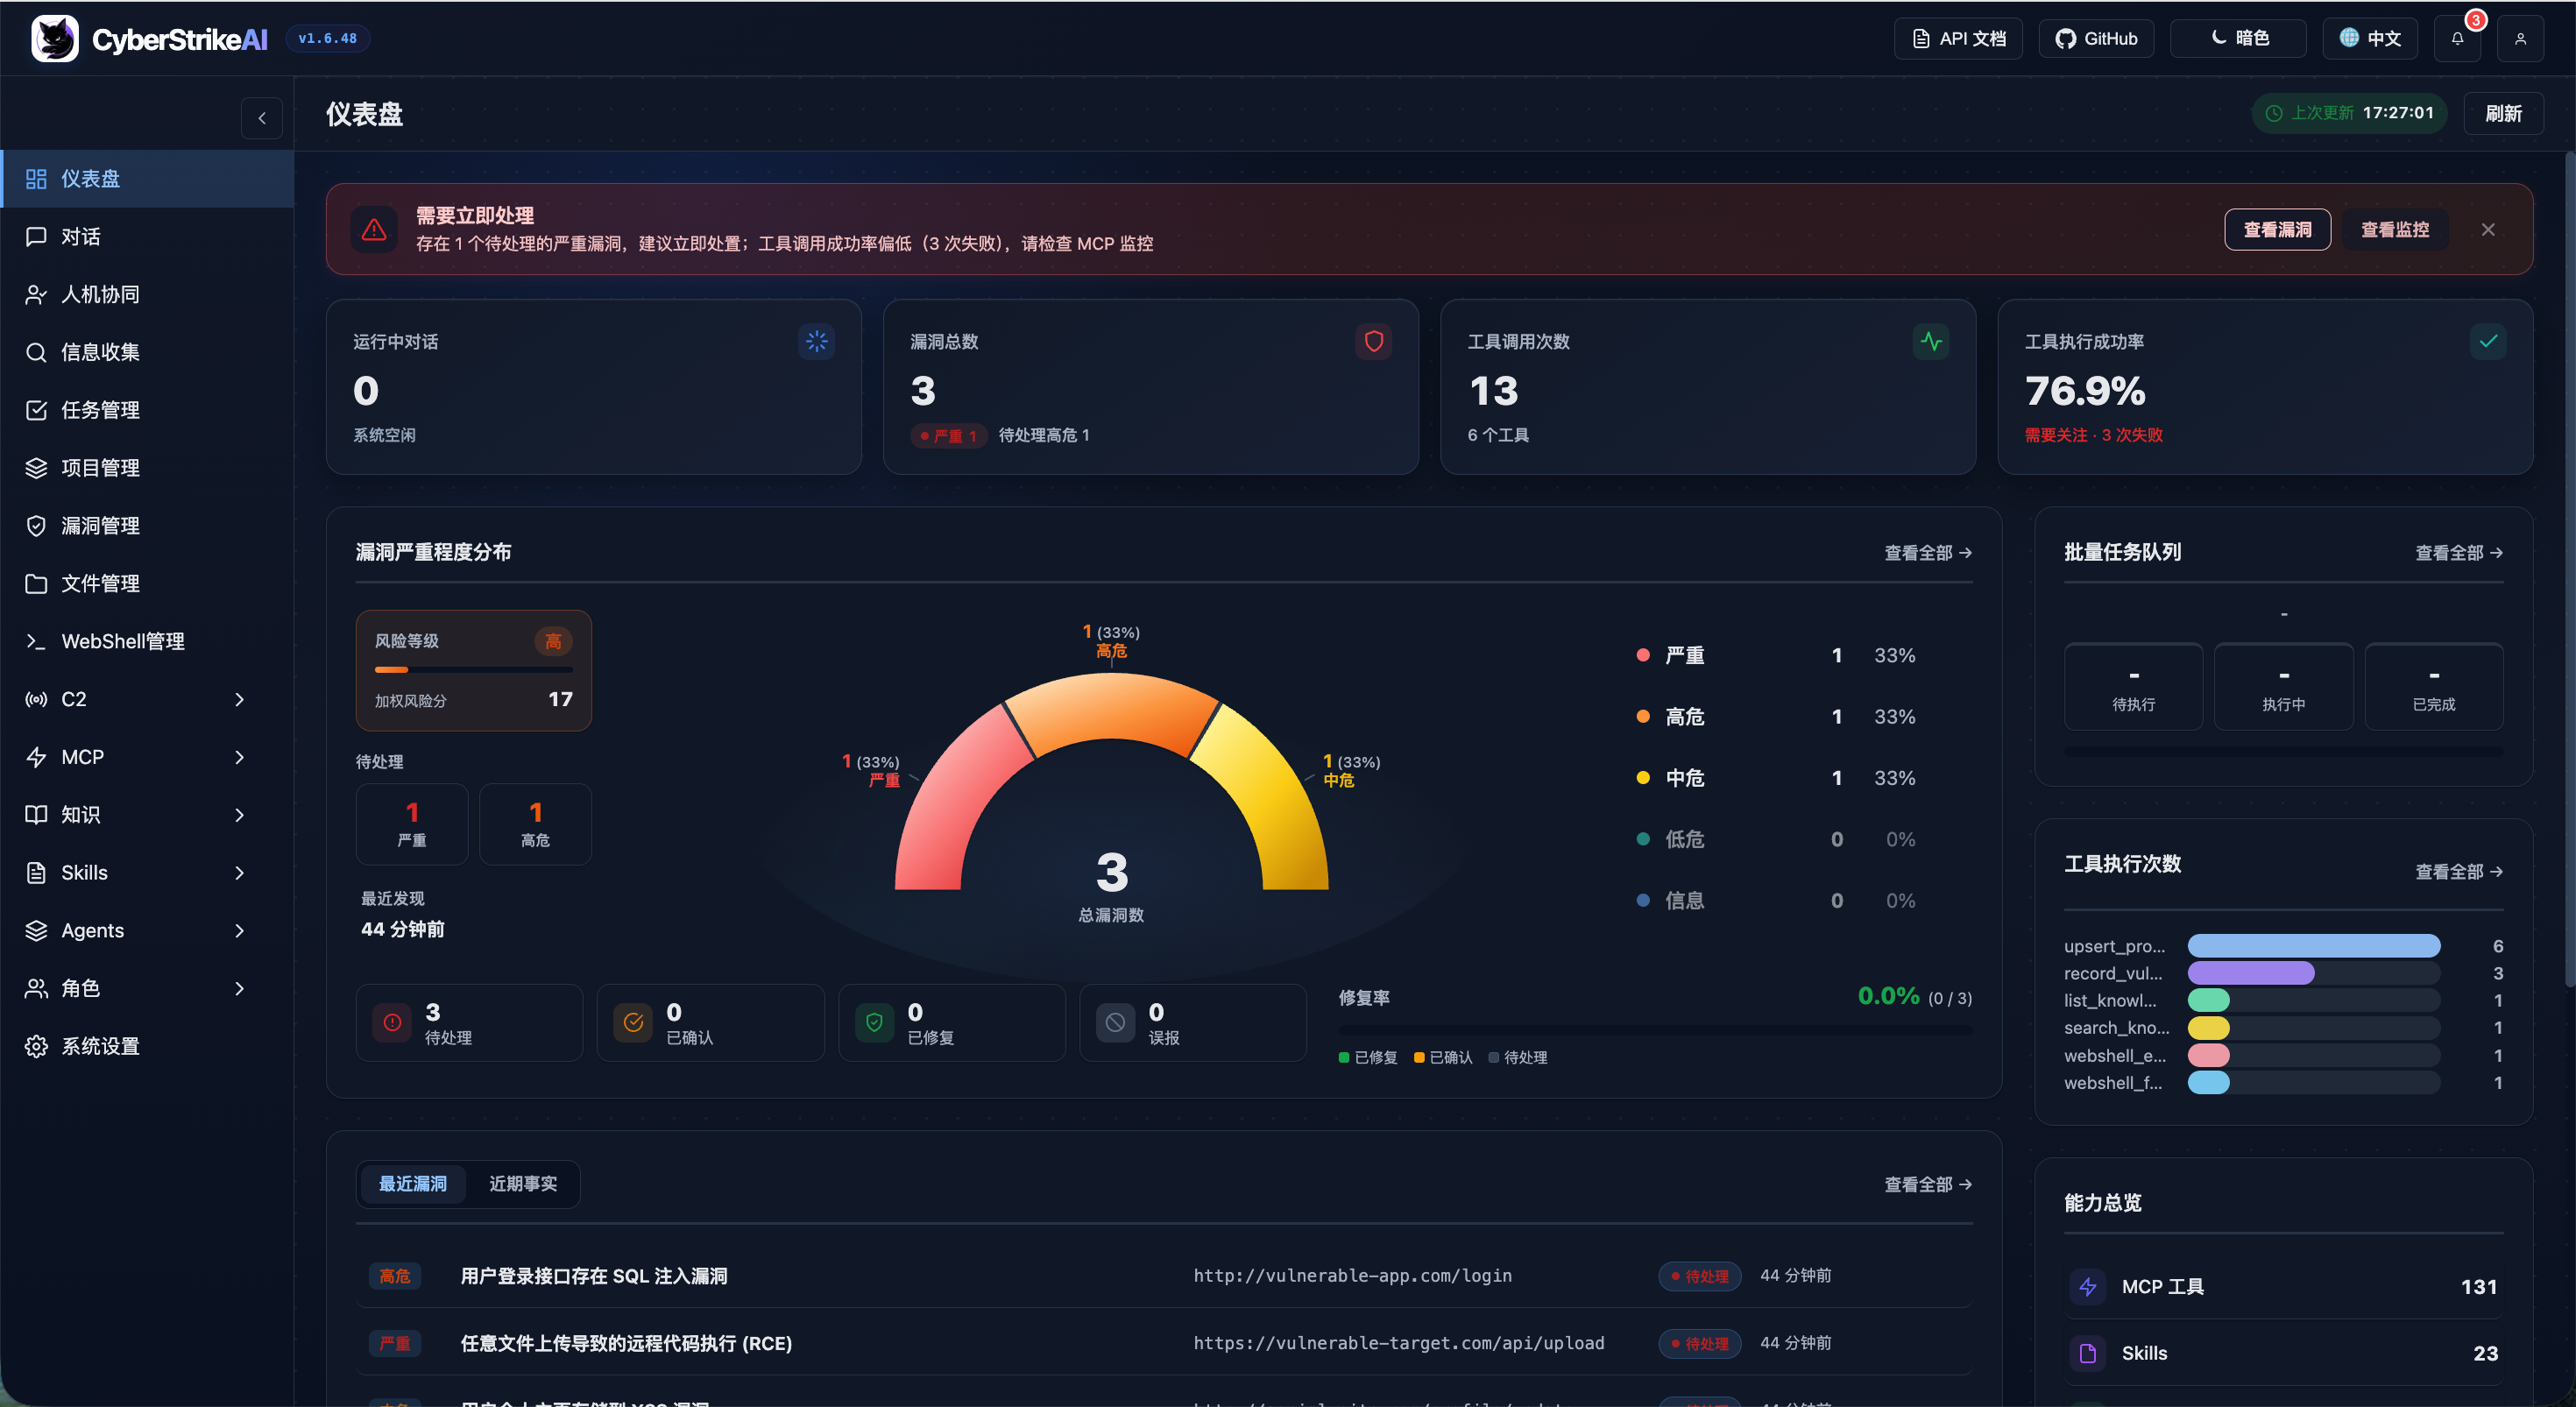
CyberStrikeAI preview

CyberStrikeAI

GitHubed1s0nz/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
5.7k11h 19m ago
CyberStrikeAI preview

CyberStrikeAI

GitHubaipentest/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

ai-securitybinary-analysiscloud-security+8
8.3k11h 19m ago
Awesome-Fuzzing preview

Awesome-Fuzzing

GitHubsecfigo/awesome-fuzzing

A curated list of fuzzing resources ( Books, courses - free and paid, videos, tools, tutorials and vulnerable applications to practice on ) for…
binary-analysiscurated-resourceseducation+6
5.9k3 years ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

binary-analysisforensicsmalware-analysis+2
3.9k4 months ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.2k3 days ago
Malware-analysis-and-Reverse-engineering preview

Malware-analysis-and-Reverse-engineering

GitHubdump-guy/malware-analysis-and-reverse-engineering

Some of my publicly available Malware analysis and Reverse engineering.
binary-analysisctfcurated-resources+8
9602 years ago
KsDumper preview

KsDumper

GitHubequifox/ksdumper

Dumping processes using the power of kernel space !

binary-analysiseducationexploitation+2
1.1k3 years ago
forensictools preview

forensictools

GitHubcristianzsh/forensictools

Collection of forensic tools

binary-analysisdata-recoverydigital-forensics+7
7012 months ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…

binary-analysisdefensive-toolsforensics+3
6789 months ago
Previous1234…9Next