
Archived
cve-2014-2734
 adrienthebo/cve-2014-2734
I think this CVE is full of lies and deceit and very confusing code.
binary-analysisexploitationvulnerability-analysis
1
adrienthebo/cve-2014-2734I think this CVE is full of lies and deceit and very confusing code.
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 mrphrazer/binary-ninja-headless-mcp
Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 zardus/ctf-tools
Some setup scripts for security research tools.
 upx/upx
UPX - the Ultimate Packer for eXecutables
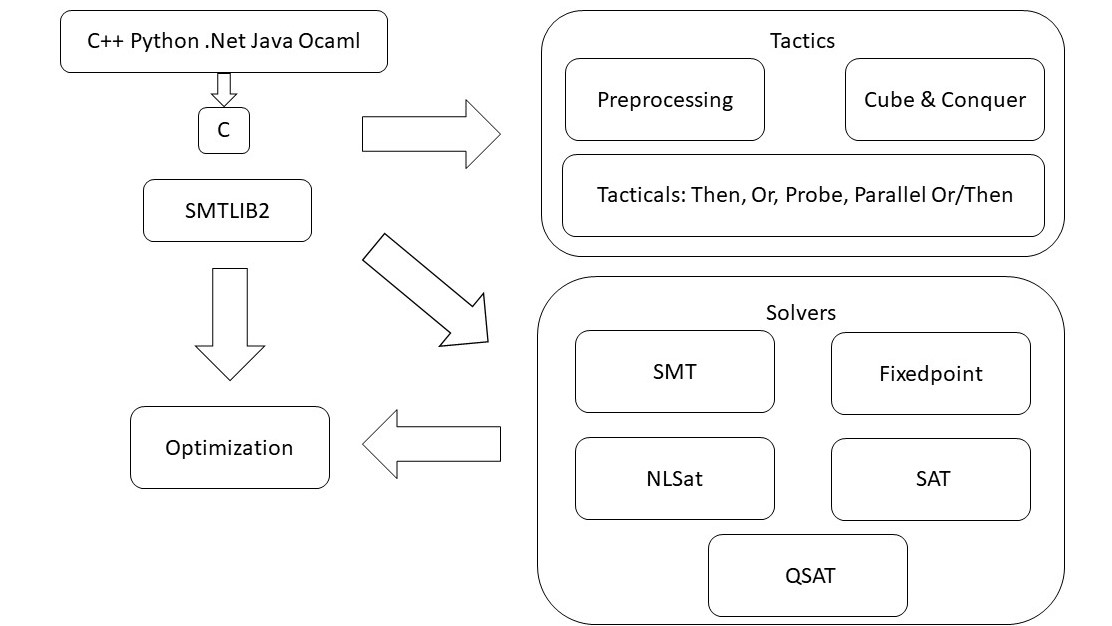 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 lauriewired/ghidramcp
MCP Server for Ghidra
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
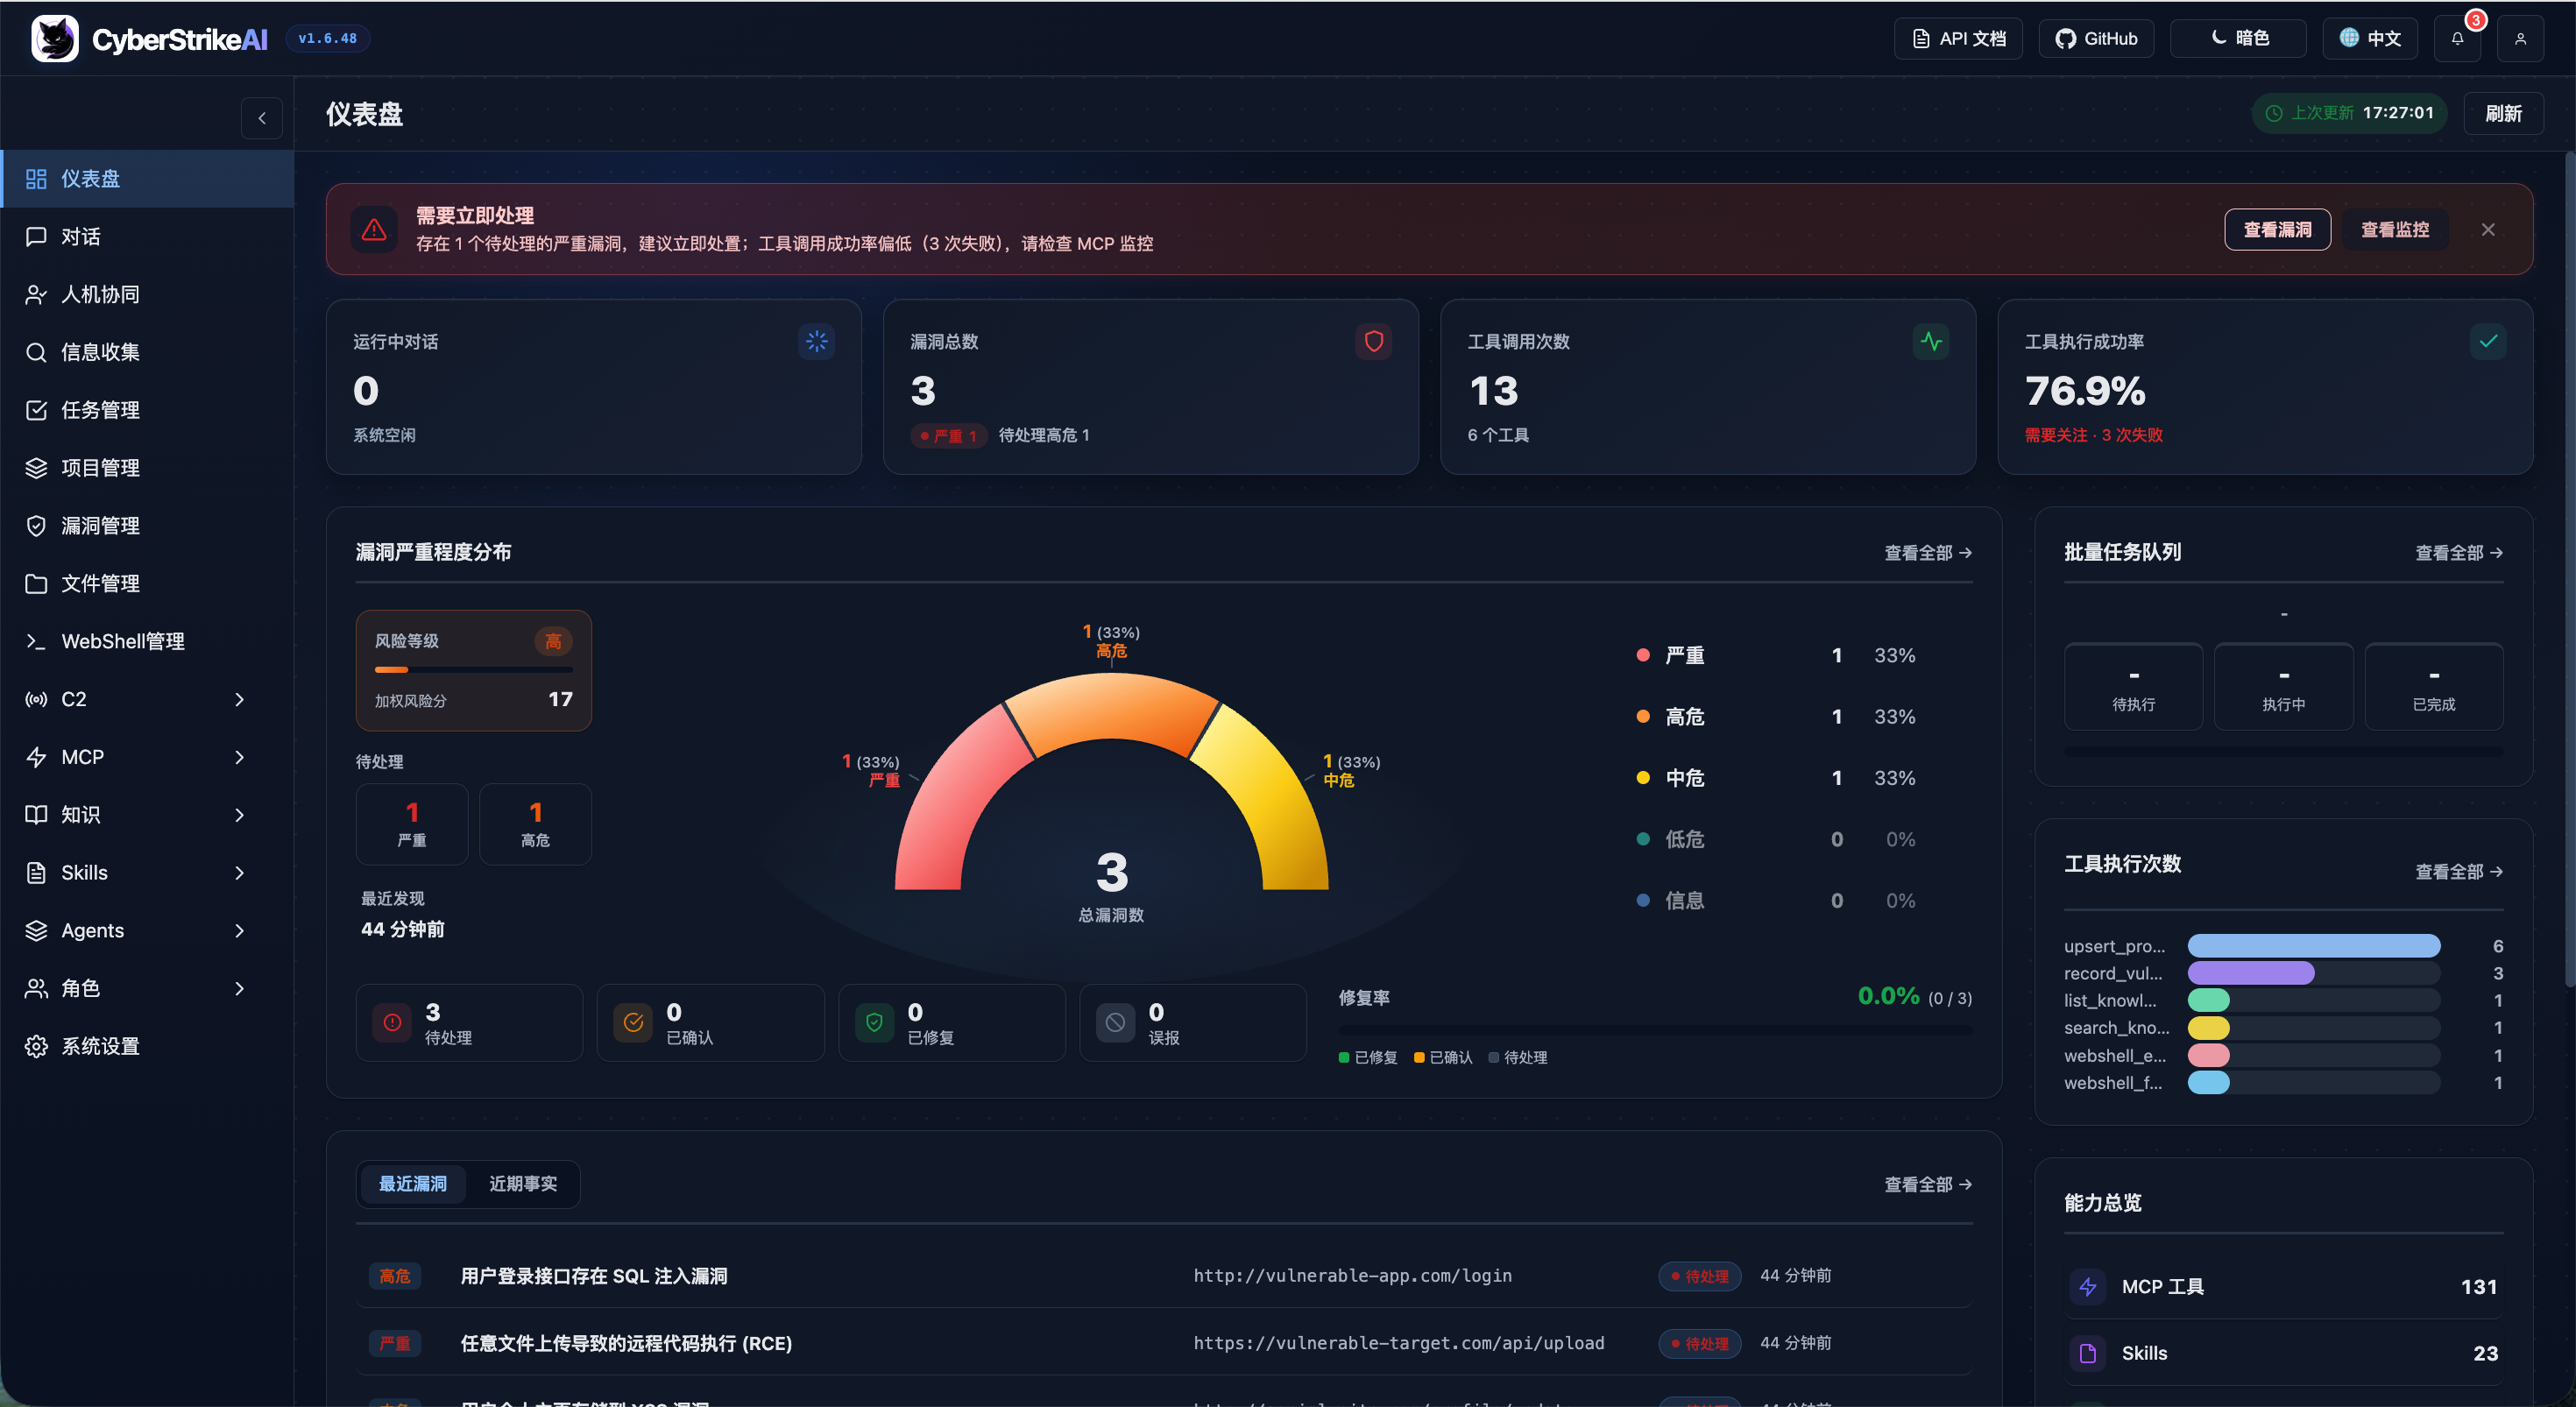 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
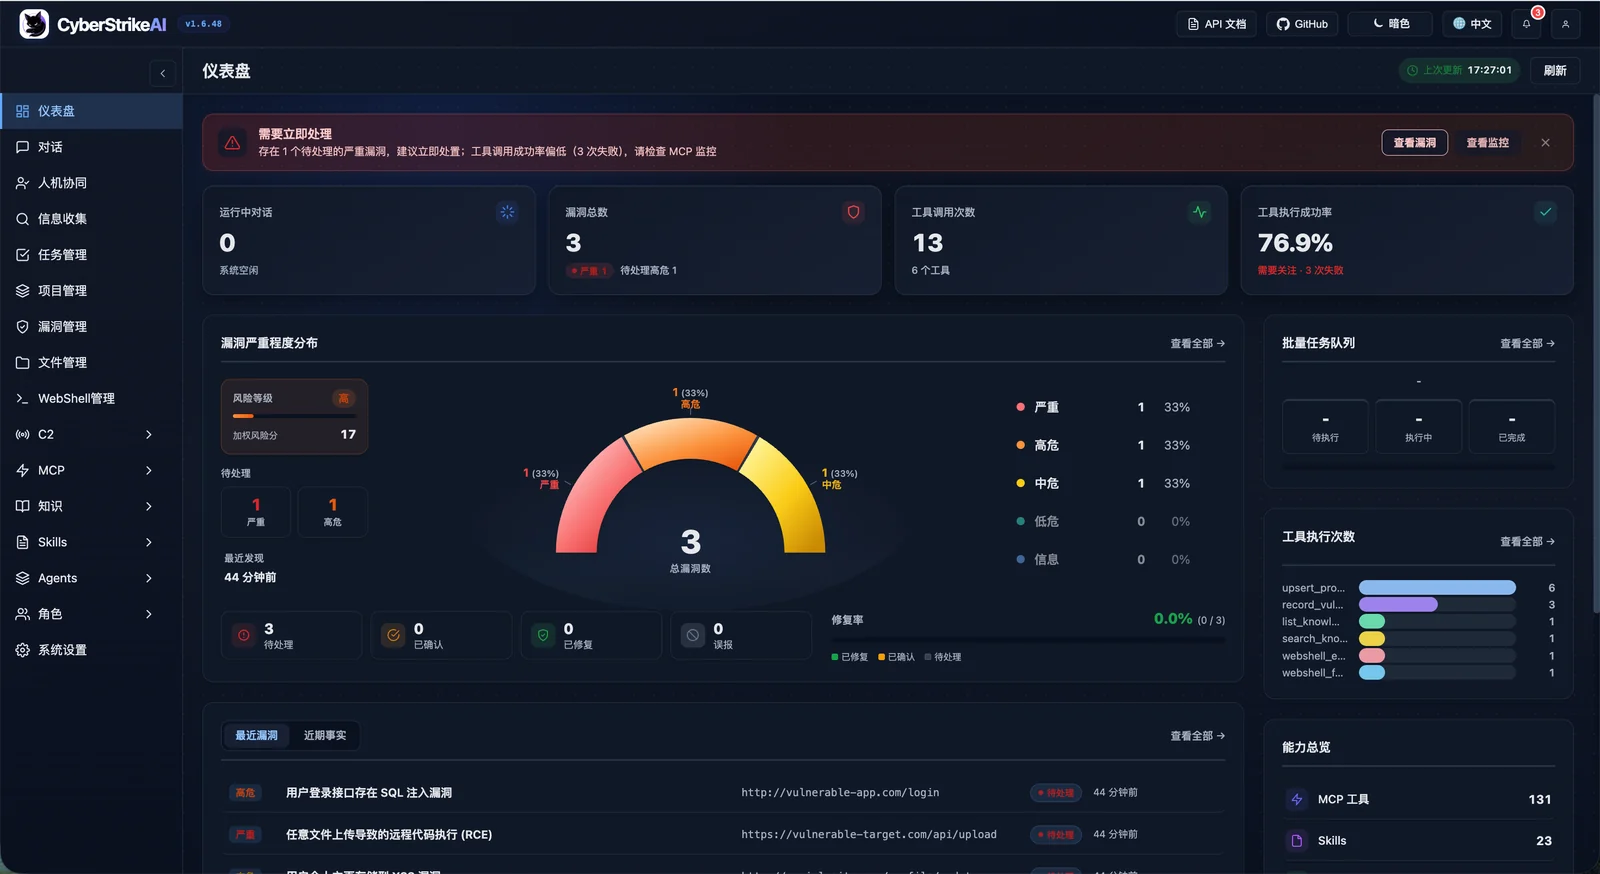 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
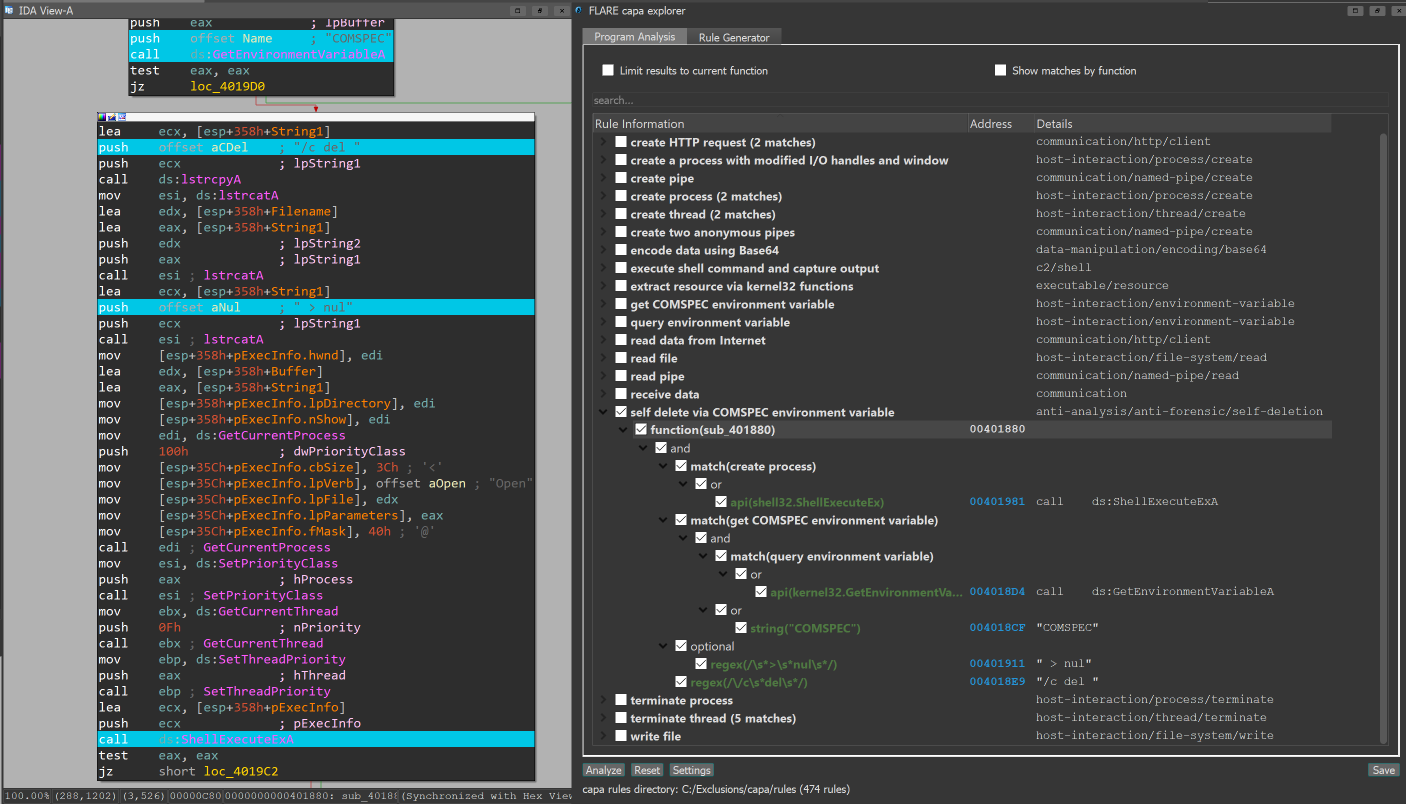 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…