

wpprobe
 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
api-security-testingcrawlerexploitation+5
93124 days ago
chocapikk/wpprobeA fast WordPress plugin enumeration tool
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
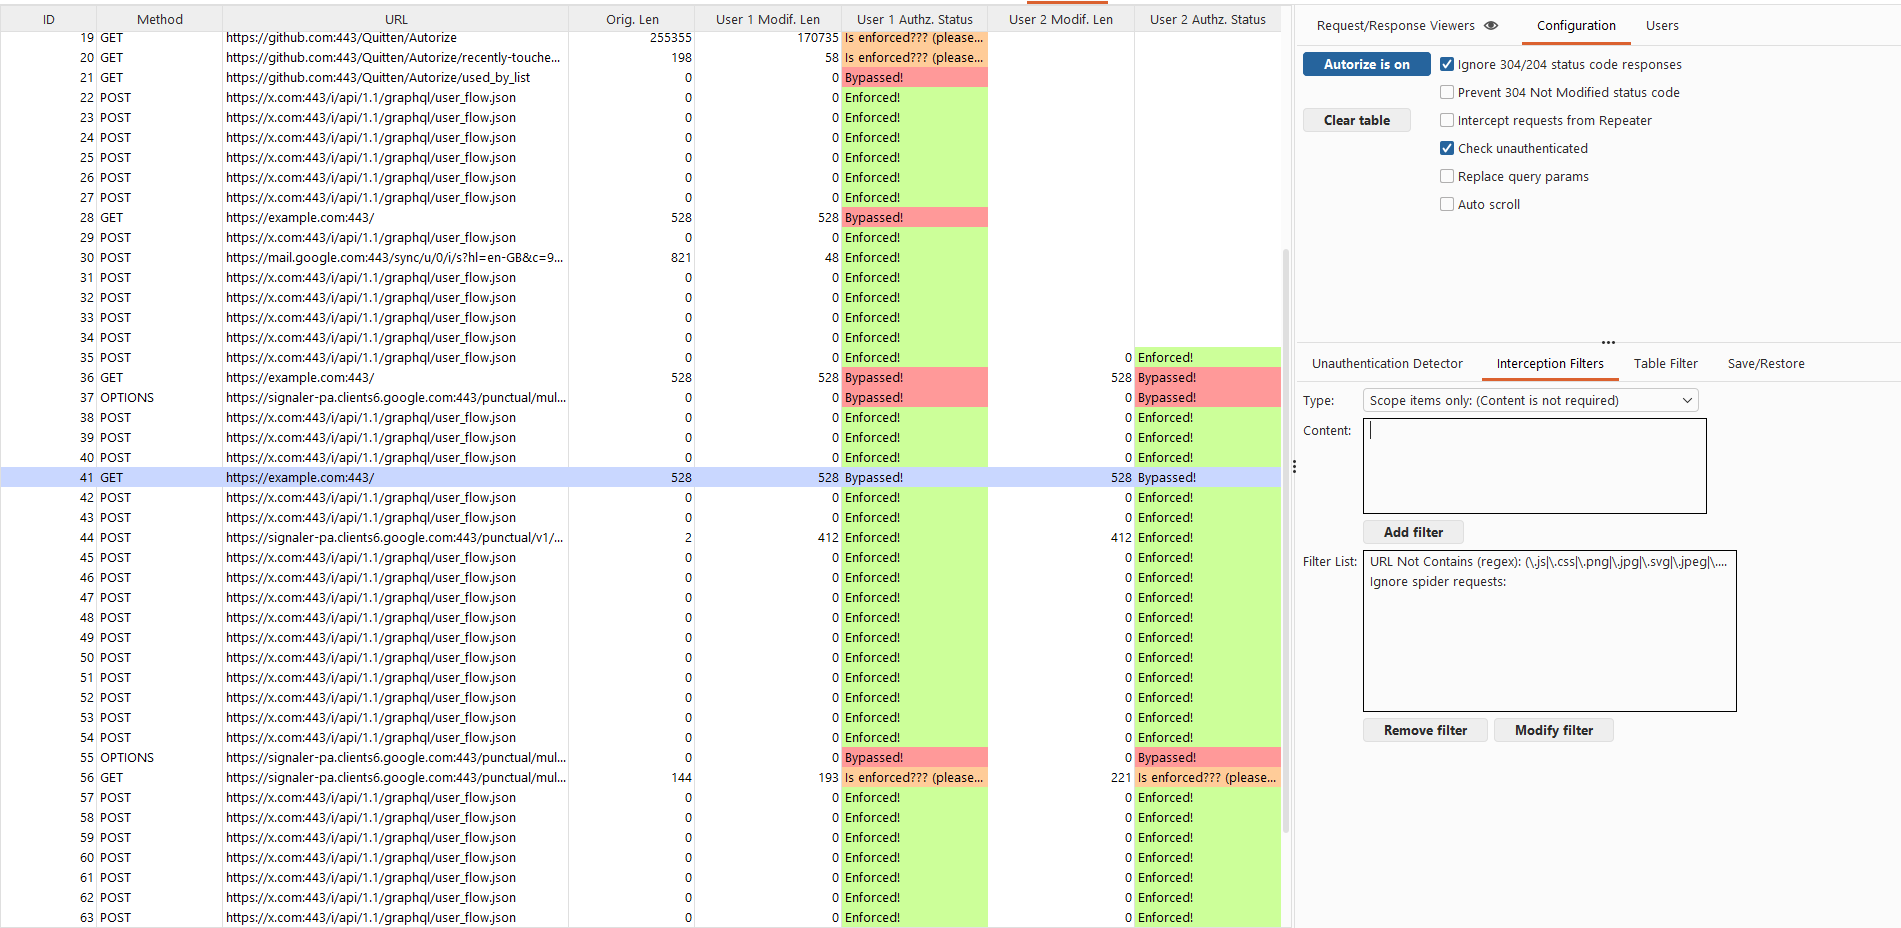 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
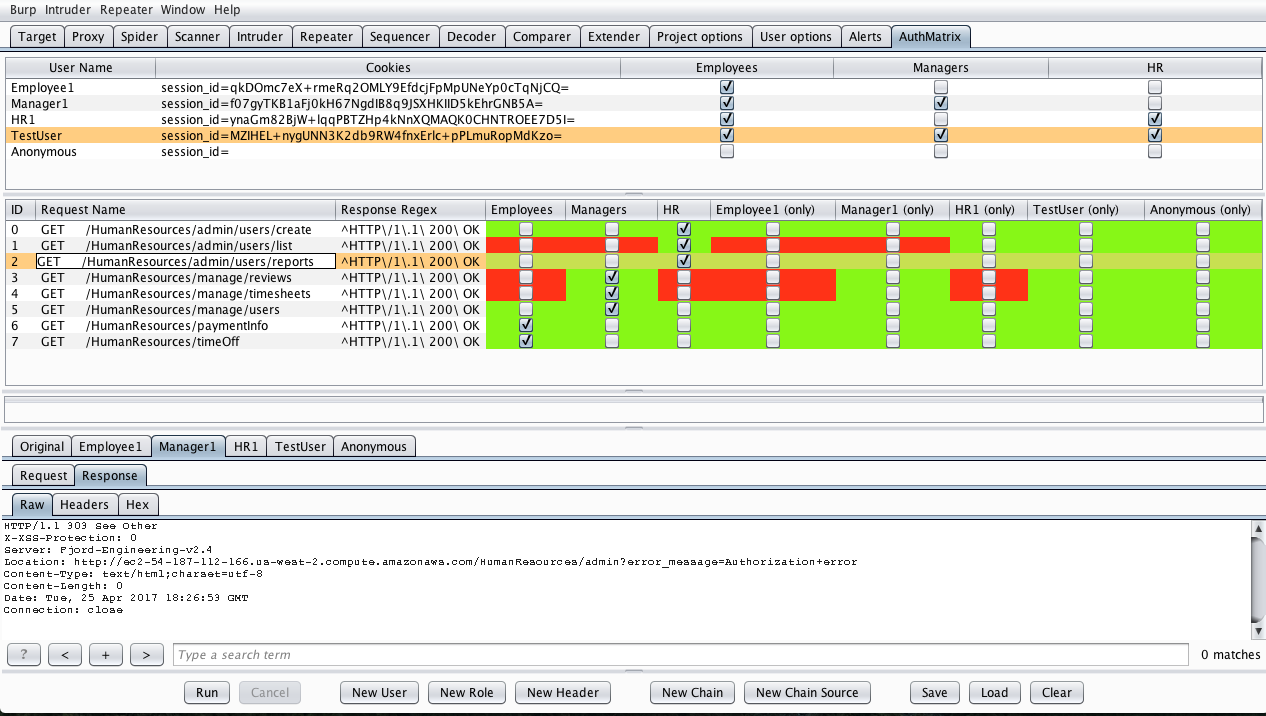 securityinnovation/authmatrix
AuthMatrix is a Burp Suite extension that provides a simple way to test authorization in web applications and web services.
 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
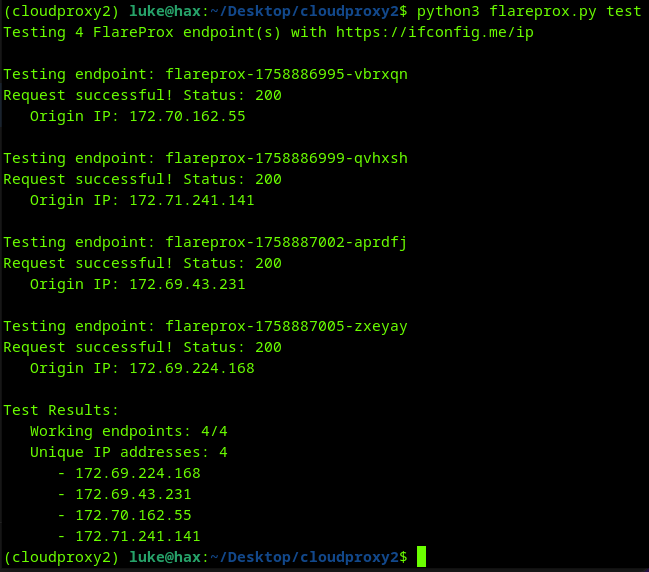 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 papamica/waf-checker
Tests your WAF with +160 payloads
 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 ebryx/aes-killer
Burp Plugin to decrypt AES encrypted traffic on the fly
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…