

akca
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
245
akha-security/akcaEvidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
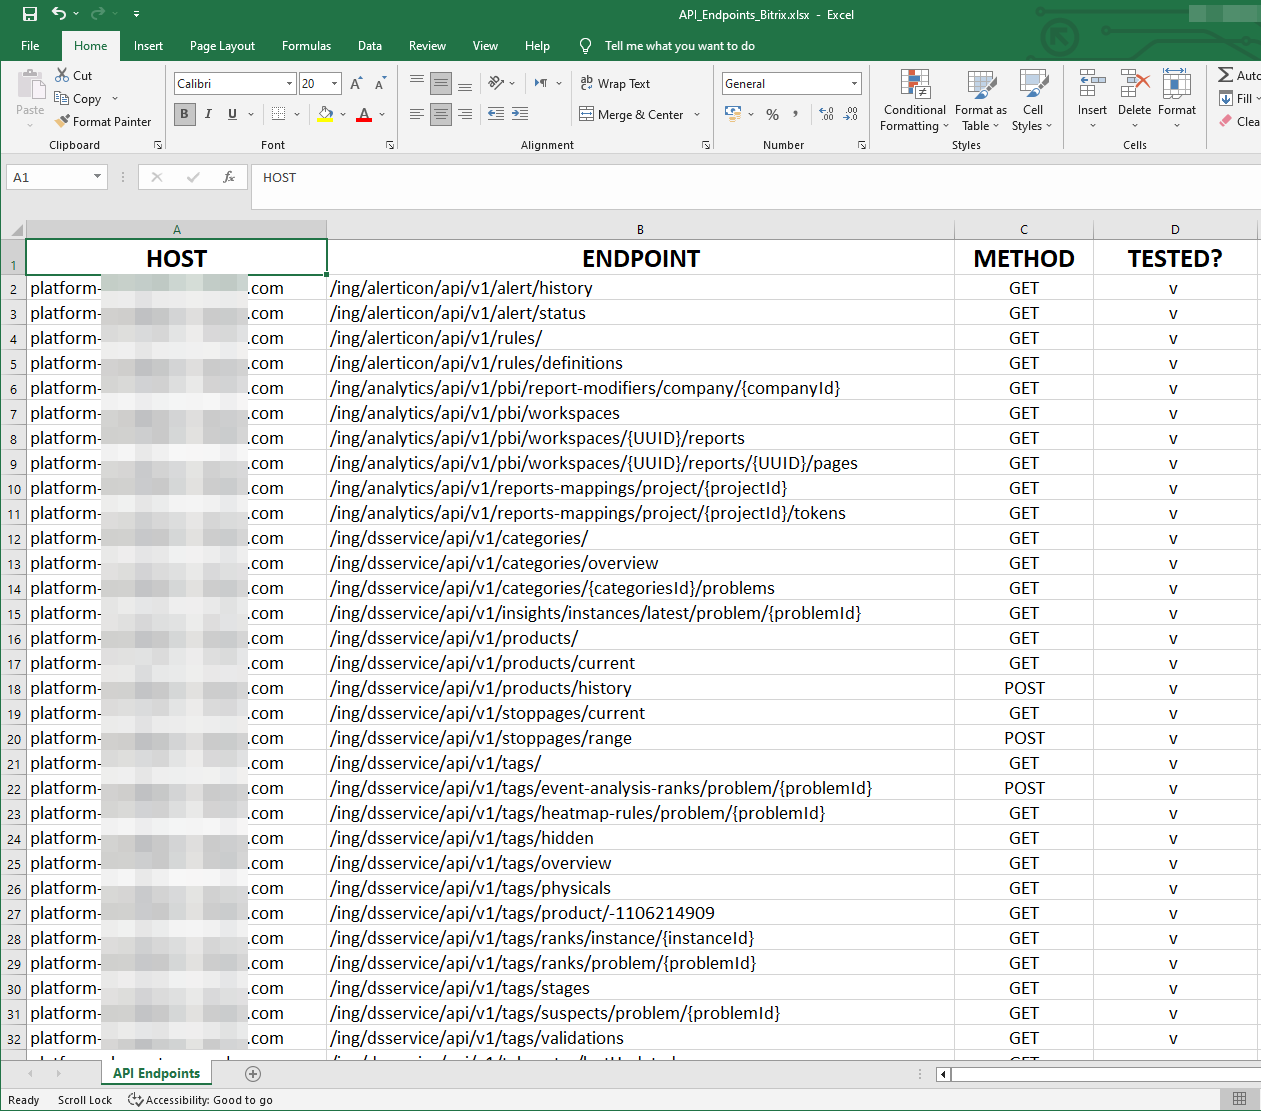 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
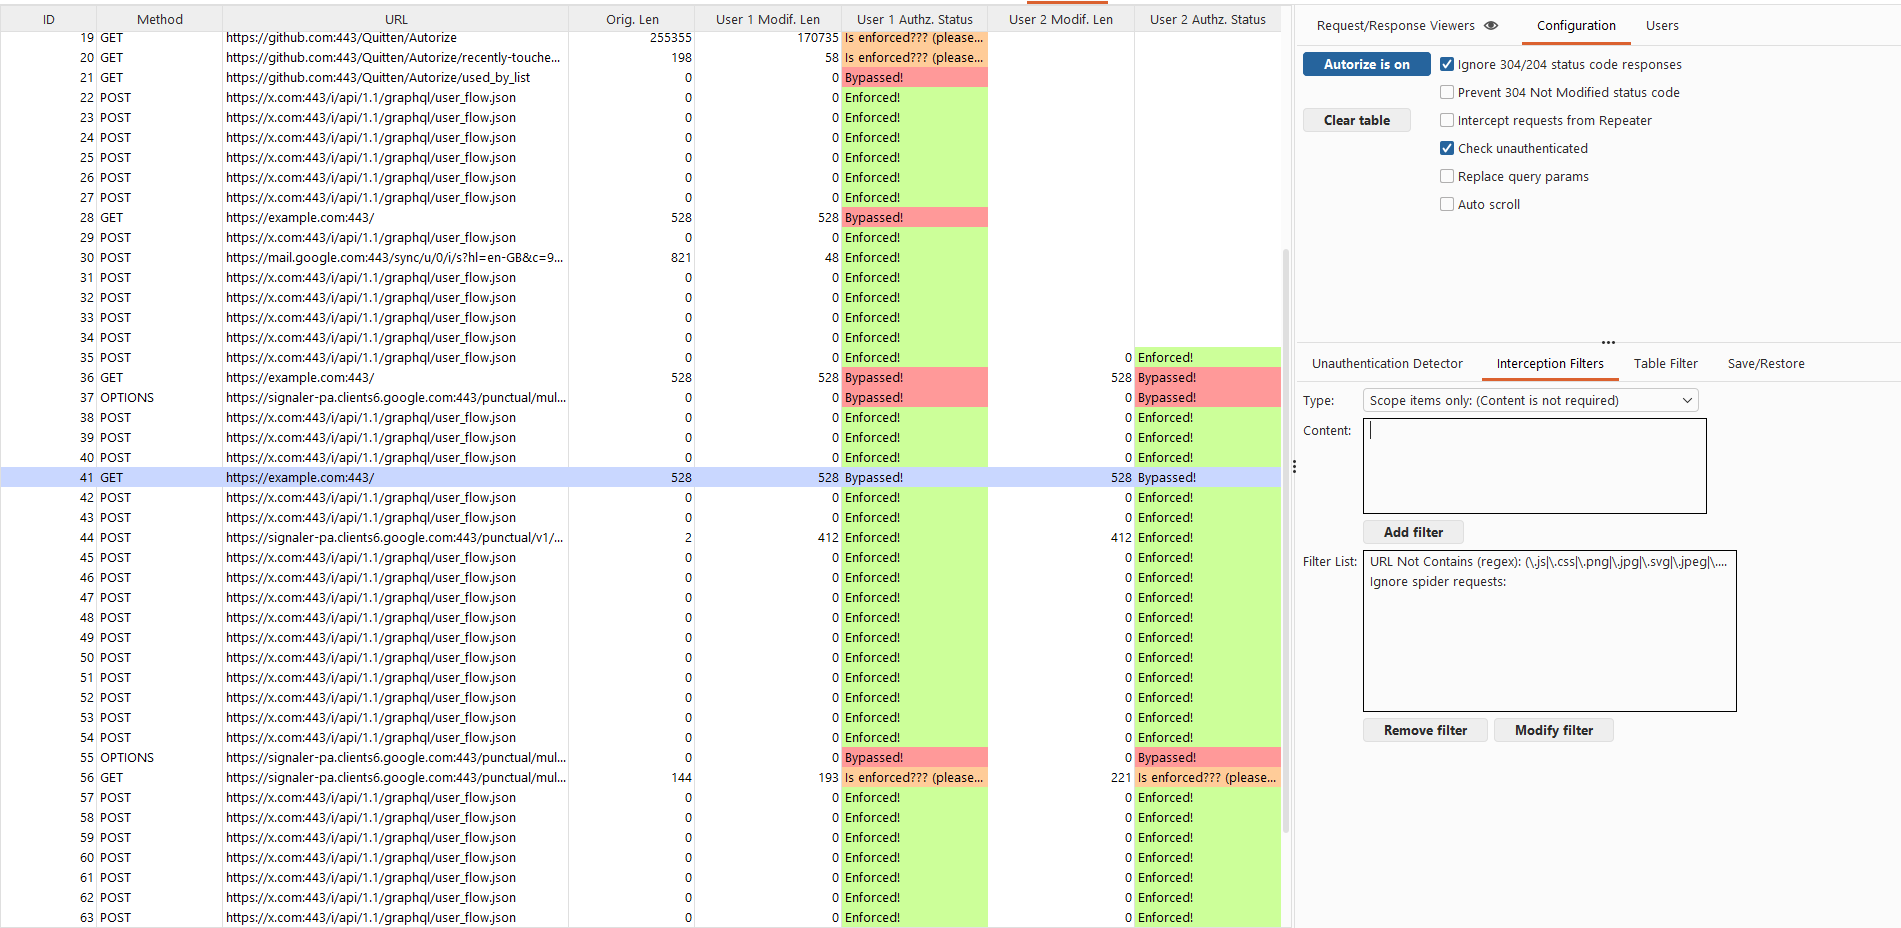 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
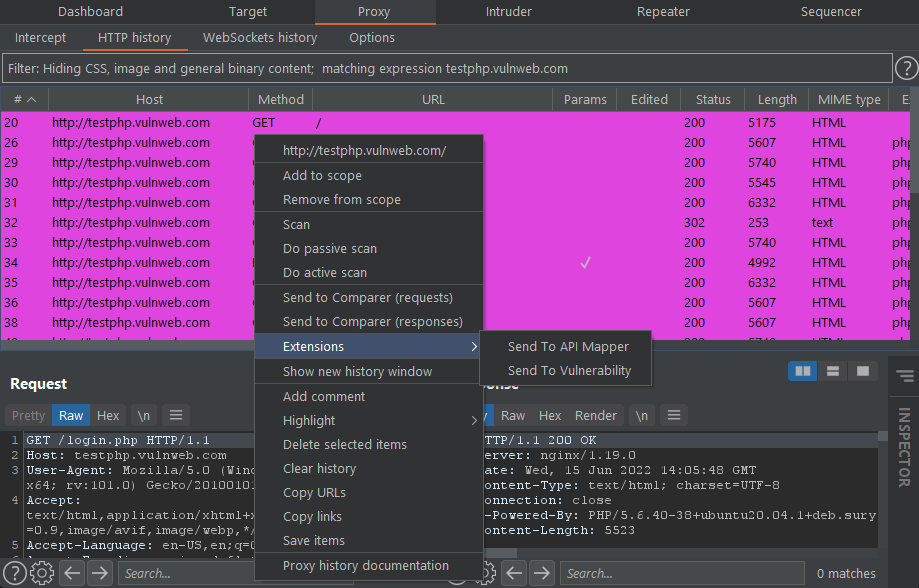 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
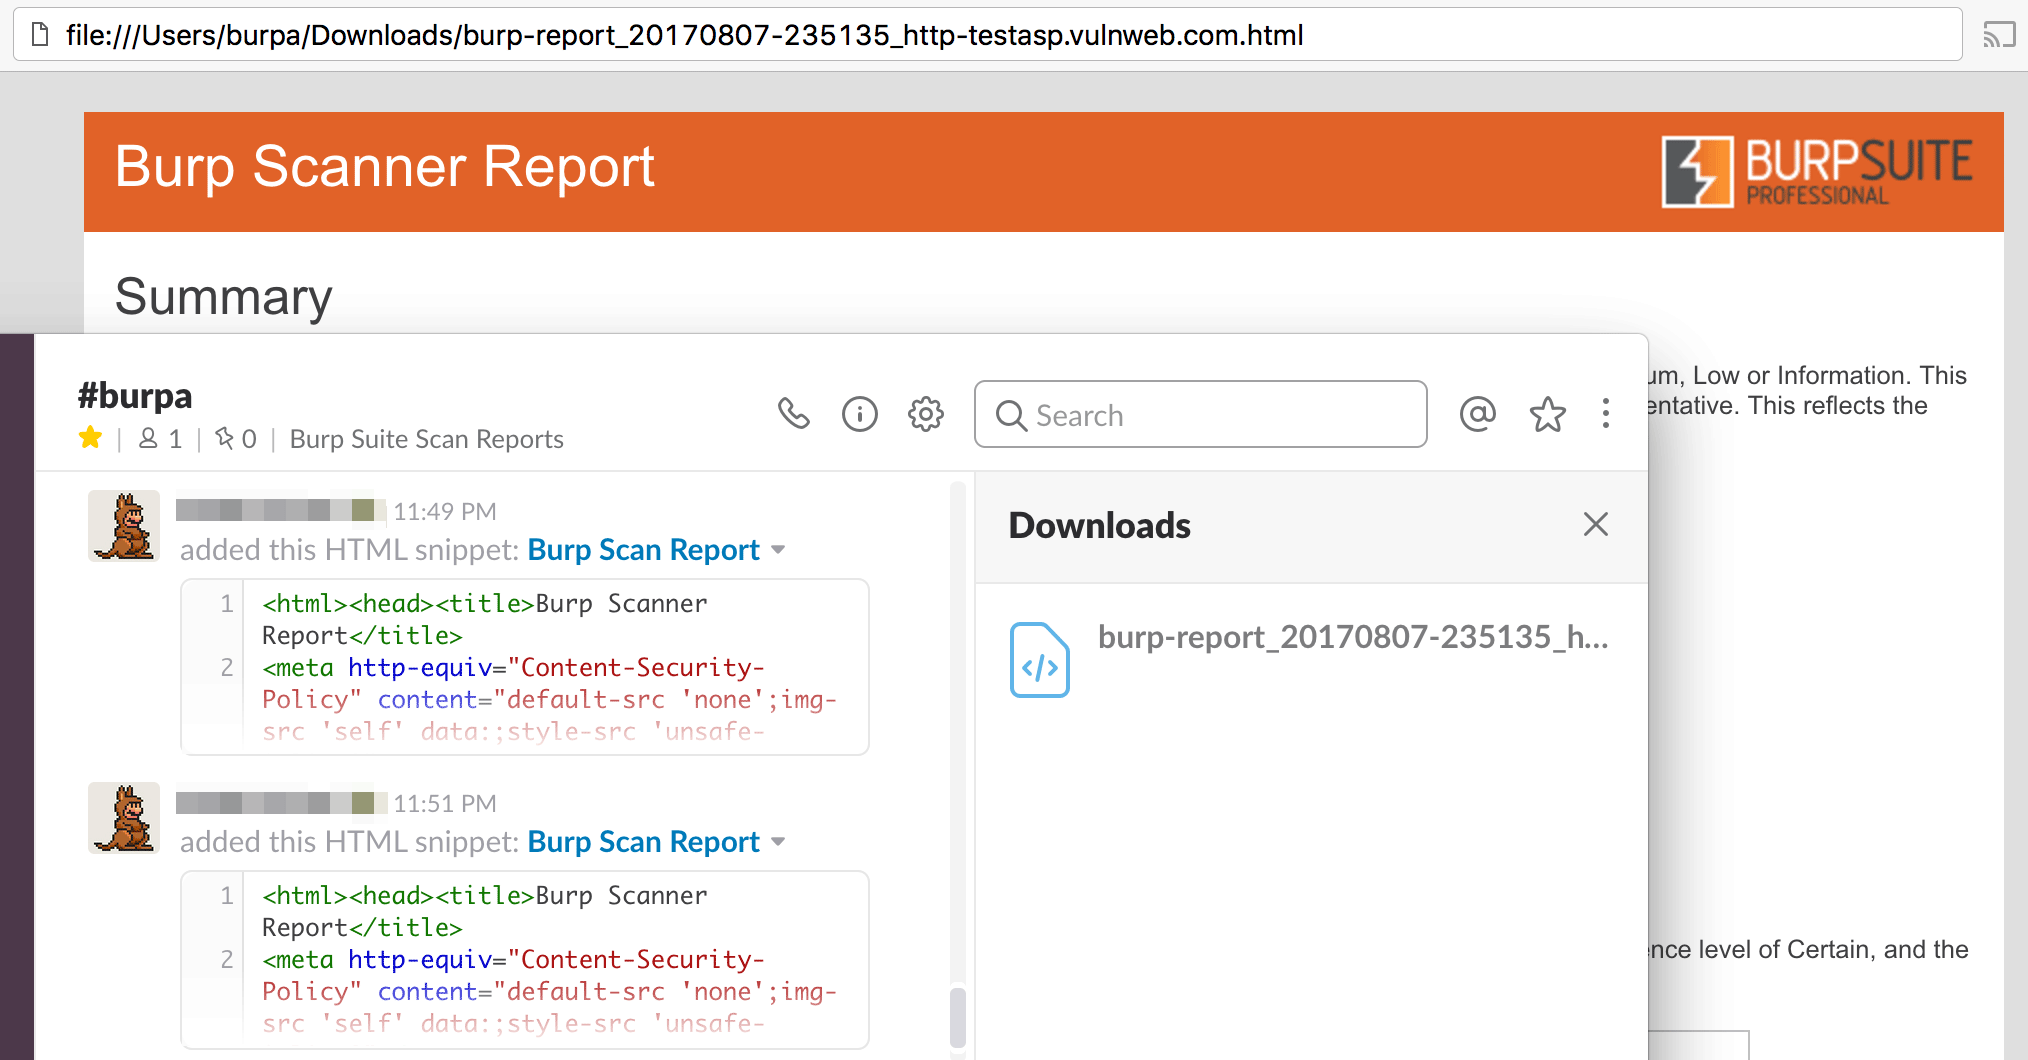 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 papamica/waf-checker
Tests your WAF with +160 payloads
 owasp/dvsa
a Damn Vulnerable Serverless Application