
NetSpecter
 mrhackercharlie/netspecter
Real-time system monitoring tool for detecting process activity and network exposure!
anomaly-detectiondefensive-toolseducation+4
13
mrhackercharlie/netspecterReal-time system monitoring tool for detecting process activity and network exposure!
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
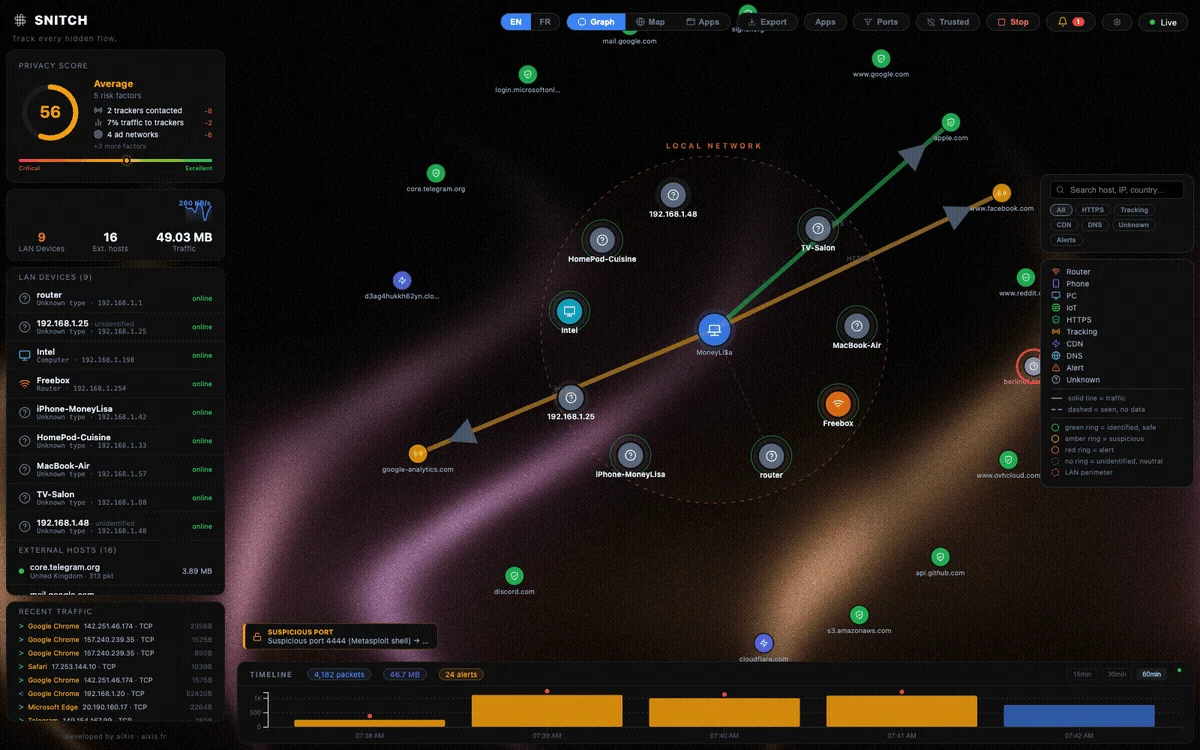 aixisstudio/snitch
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 online-ml/river
Streaming machine learning library for incremental learning on data streams, providing online estimators, drift and anomaly detection, pipelines,…
 0x0allenace/soc-analyst-portfolio
A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 neo23x0/raccine
A Simple Ransomware Vaccine
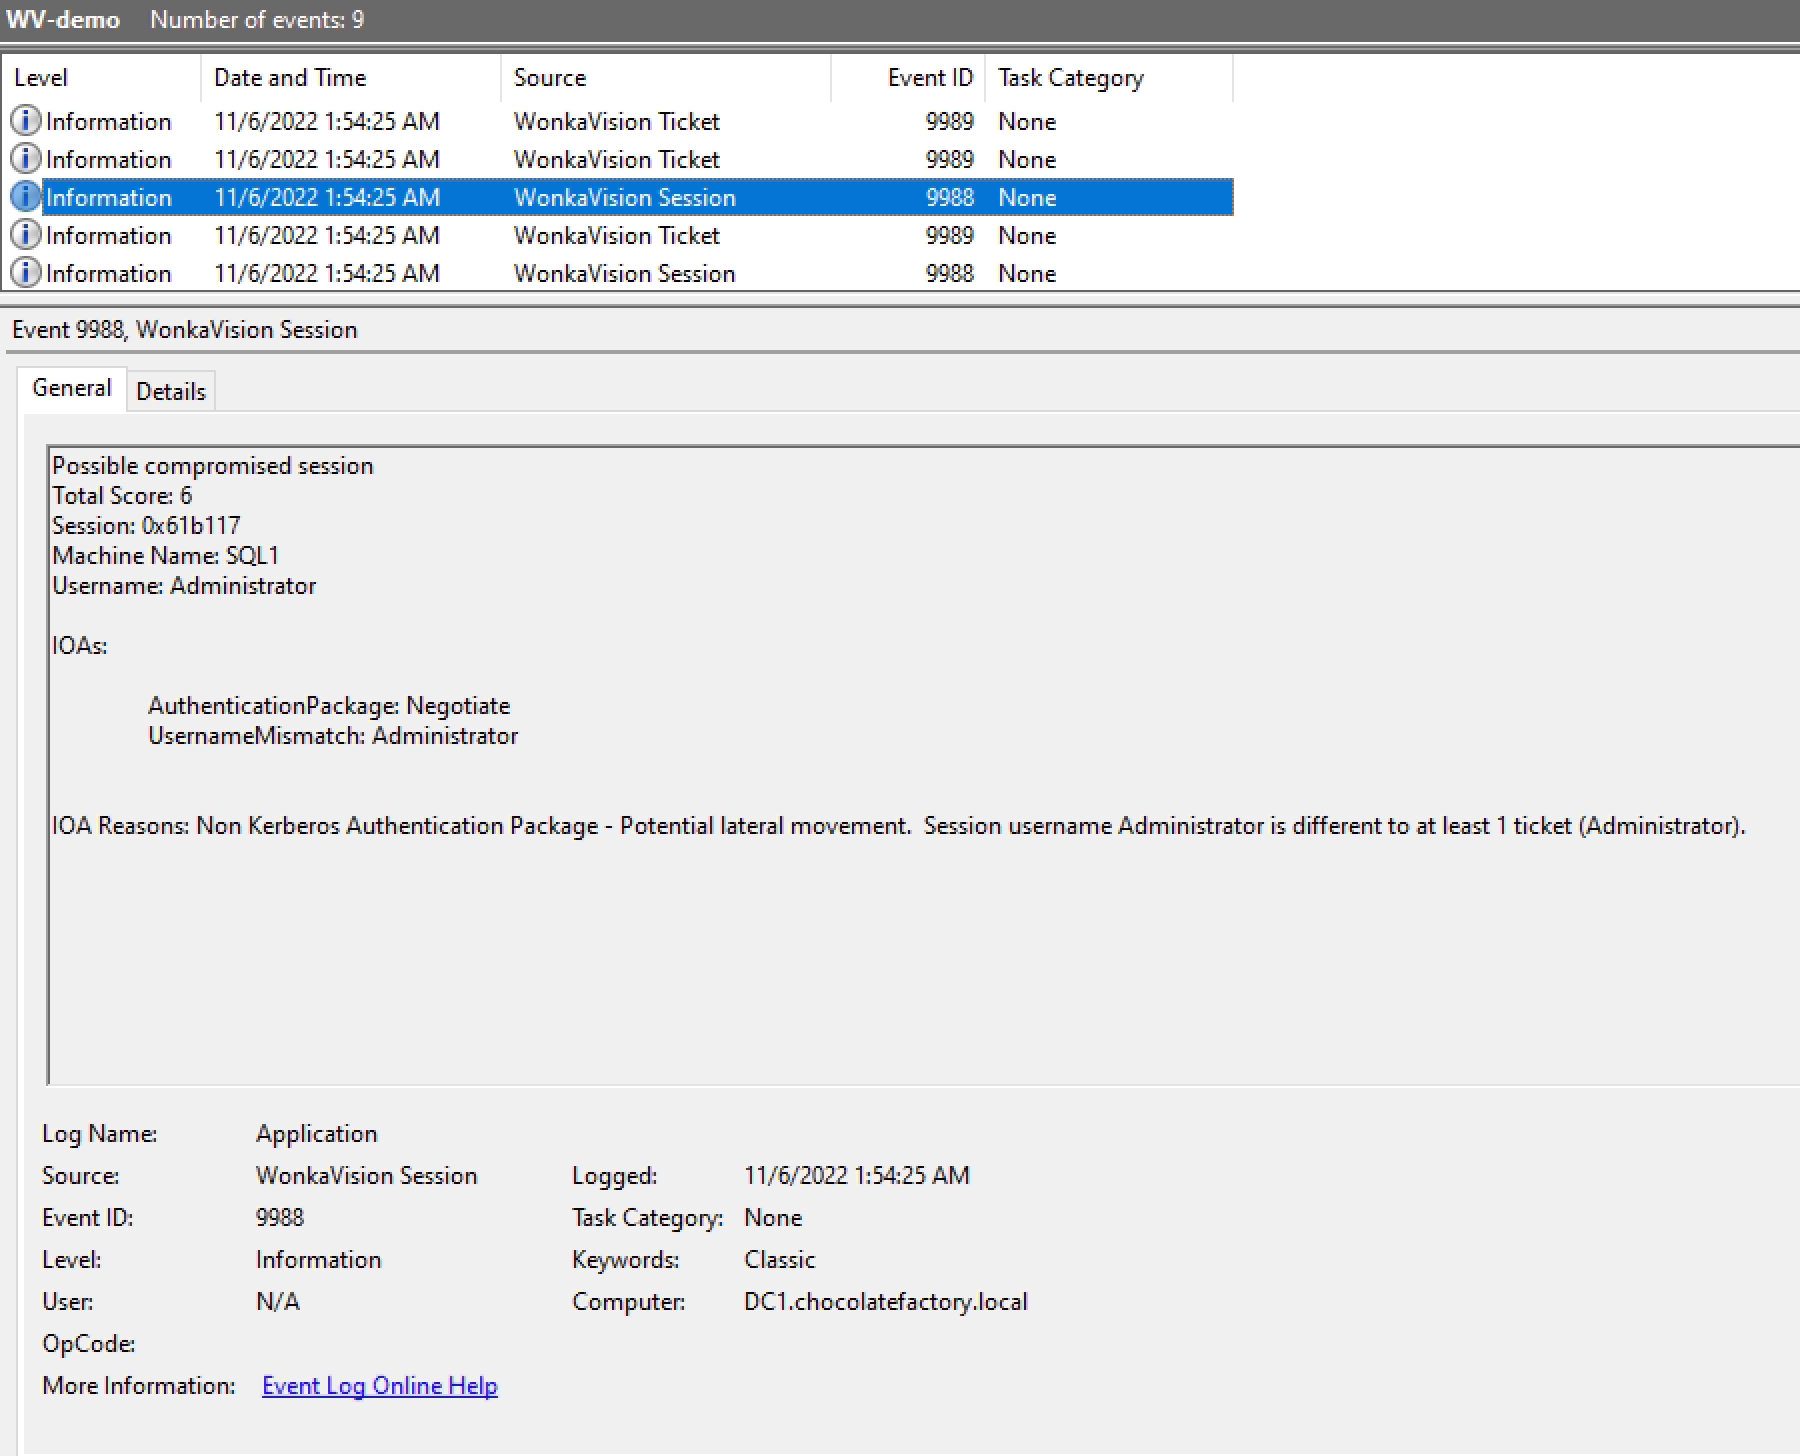 0xe7/wonkavision
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…
 connectedlucy/plague
Default Detections for EDR
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 puniaze/portdog
Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…