

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Hunt-Weird-Syscalls — ETW based POC to identify direct and indirect syscalls | Kitploit

Tools/GitHubGitHub/theflink/hunt-weird-syscalls
Defensive ToolsMalware AnalysisIntrusion DetectionAnomaly Detection
GitHubtheflink/hunt-weird-syscalls

Hunt-Weird-Syscalls

ETW based POC to identify direct and indirect syscalls

View Repository
19524353 years agoReviewed by Kitploit
Share

Hunt-Weird-Syscalls

This is a ETW based POC to monitor for abnormal syscalls.

For now, the syscalls NtOpenThread and NtSetContextThread are monitored to identify IOCs indicating both direct and indirect syscalls.

Description

This project uses ETW, more precisely kernel based ETW providers, to monitor for IOCs.
ETW providers sitting in the kernel can effectively be leveraged, as the calltraces of emitted events contain the usermode address from where the syscall was conducted.

This allows monitoring IOCs indicating direct and indirect syscalls, a technique often leveraged by threat actors:

1: A syscall was conducted from an untrusted module (=direct syscall)
2: The used syscall stub in ntdll does not match the conducted syscall (=indirect syscall)

This project uses the Provider: Microsoft-Windows-Kernel-Audit-API-Calls to monitor for OpenThread and SetContextThread events triggered by the syscalls NtSetContextThread or NtOpenThread respectively.
Calltraces are enabled, using the flag EVENT_ENABLE_PROPERTY_STACK_TRACE.

This is a POC, and only monitors two specific syscalls. It is of course possible to use other kernel based providers to enhance telemetry.

Tests

This project contains two sample programs using direct and indirect syscalls created using the amazing SysWhispers3. They were generated as follows:

python3 syswhispers.py -a x64 -m jumper_randomized --functions NtSetContextThread
python3 syswhispers.py -a x64 -m embedded --functions NtSetContextThread

Upon execution, abnormal syscalls should be identified:
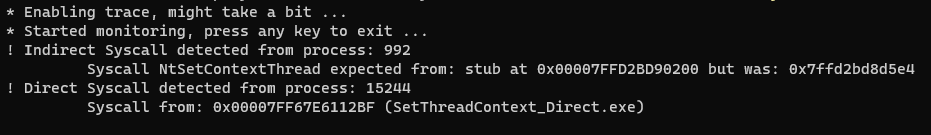
Identification of Abnormal Syscalls

Tested on 10.0.19044.

Credits

  • KrabsETW
  • SysWhispers3
  • etw provider docs by repnz
  • @OutflankNL for IsElevated()
  • @trickster012 for testing and support <3
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →






