
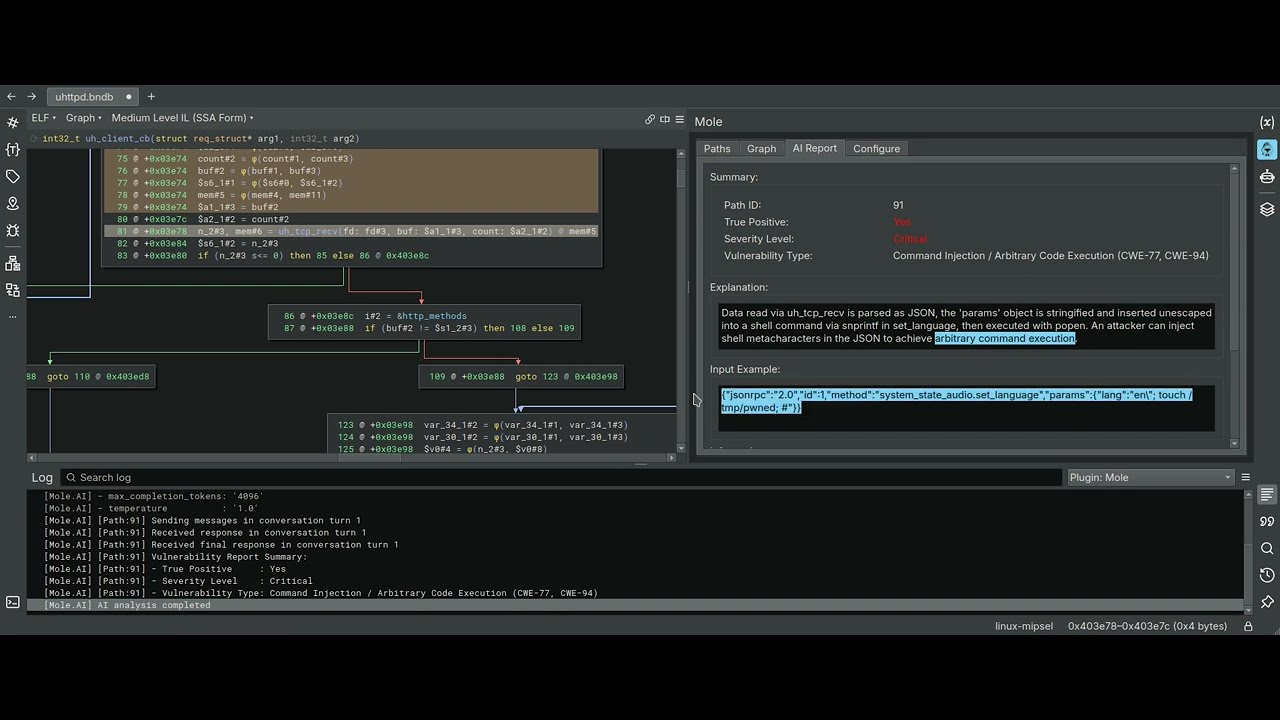
mole
 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
ai-assisted-reversingbinary-analysiscode-analysis+4
85
cyber-defence-campus/moleA Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
 lcfr-eth/cve-2024-14027_slop
Exploits for CVE-2024-14027 creating using AI/Claude as a test.
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
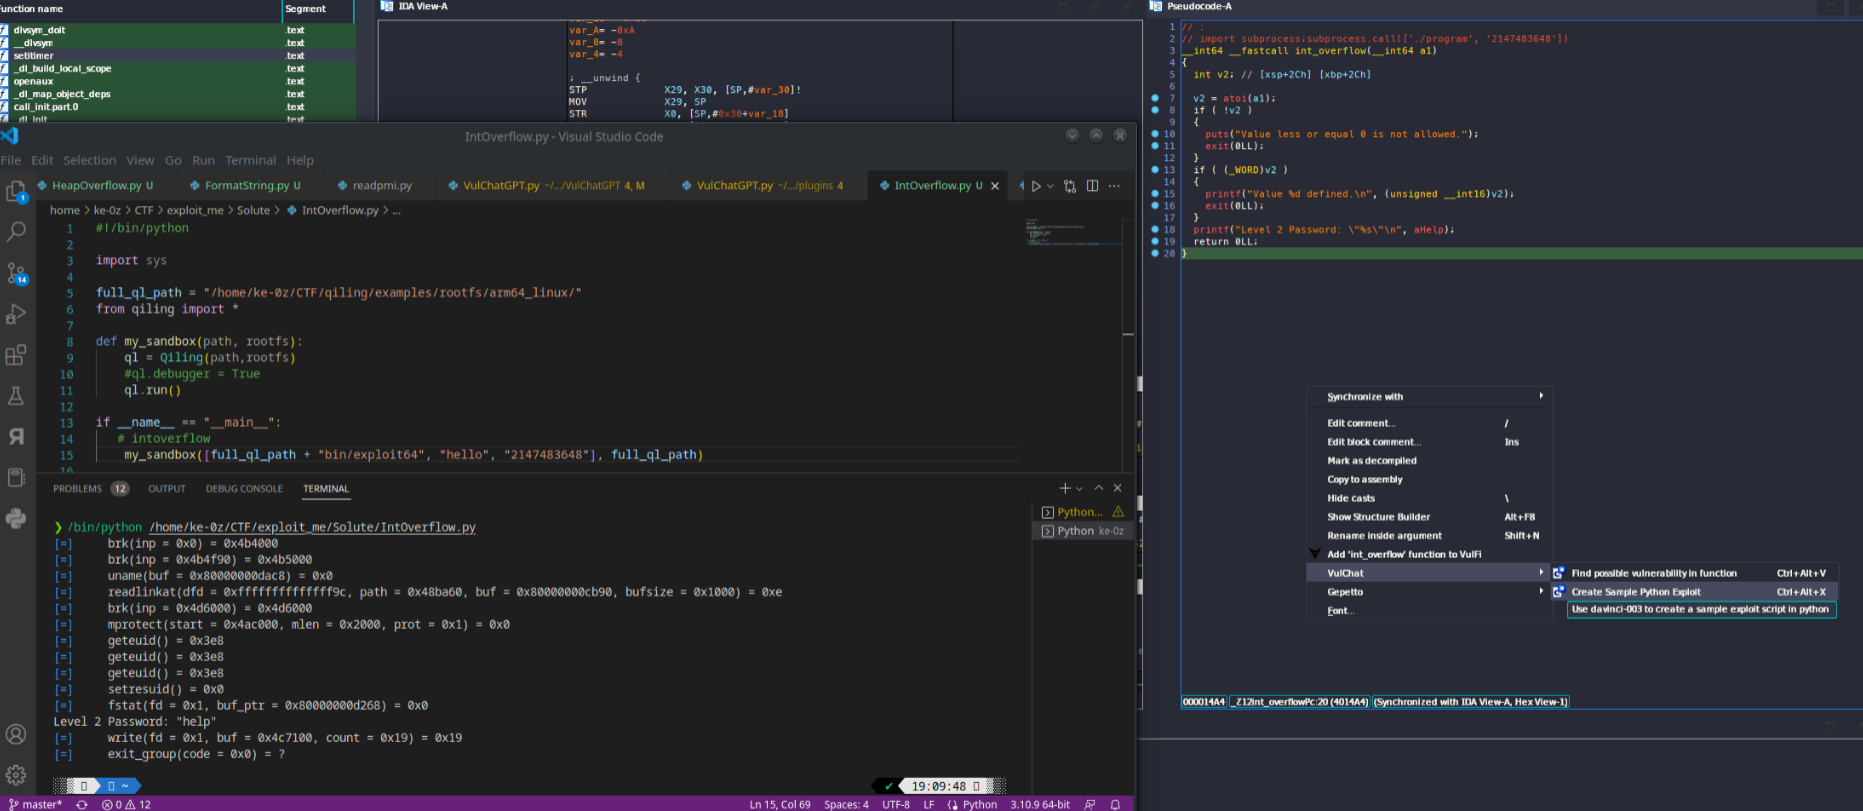 ke0z/binaivulhunter
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 lauriewired/malimite
iOS and macOS Decompiler
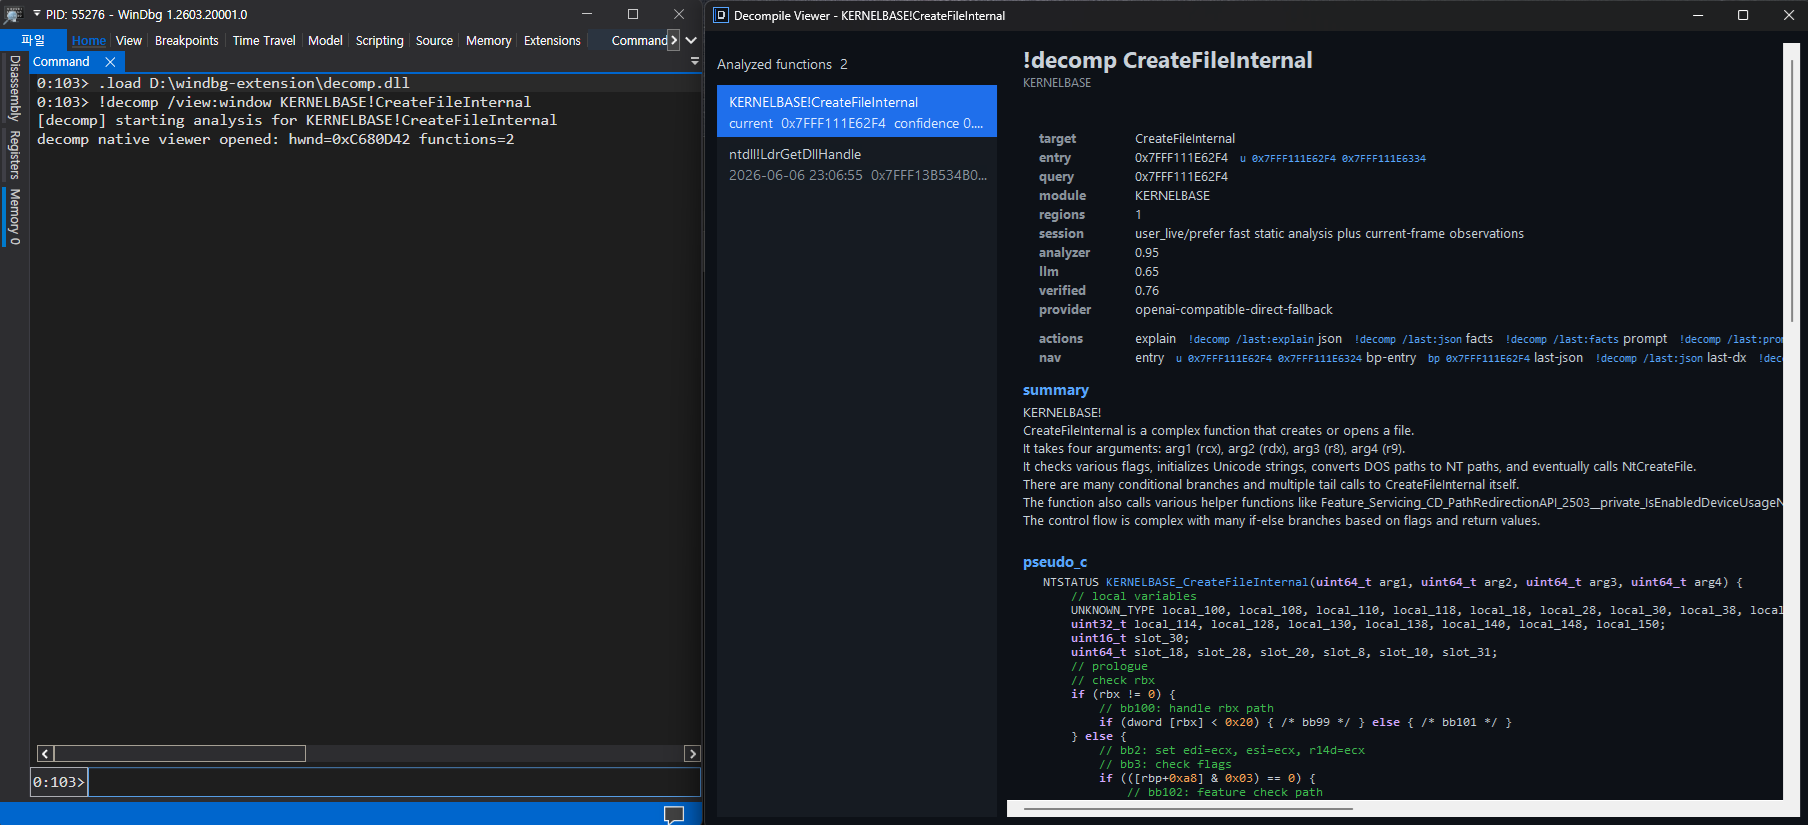 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
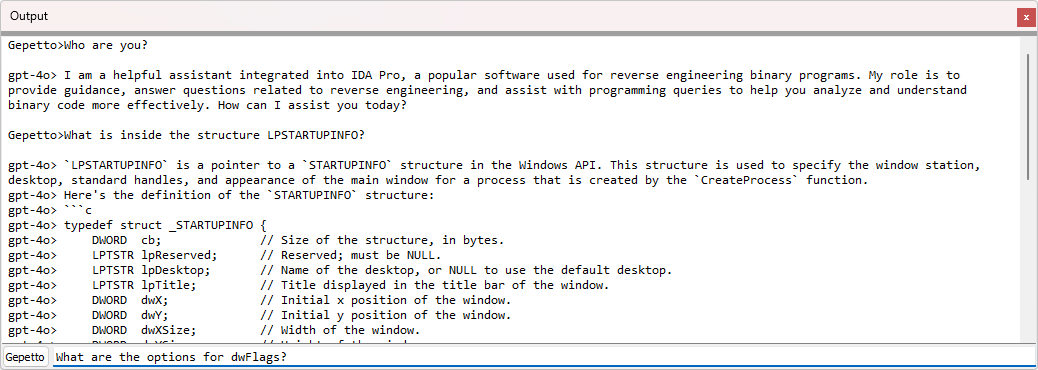 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering