Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Categories

Memory Forensics

Tools for analyzing RAM dumps to find running processes, network connections, and hidden malware.

Kitploit recommended
Top tools

10 selected
volatility3 preview#1

volatility3

GitHubvolatilityfoundation/volatility3
4.3k1 month ago
avml preview#3

avml

GitHubmicrosoft/avml
1.1k11h 8m ago
velociraptor preview#5

velociraptor

GitHubvelocidex/velociraptor
4.2k1 day ago
LiME preview#6

LiME

GitHubjtsylve/lime
2.1k7 months ago
community preview#7

community

GitHubvolatilityfoundation/community
3796 years ago
dwarf2json preview#8

dwarf2json

GitHubvolatilityfoundation/dwarf2json
1632 years ago
dissect preview#9

dissect

GitHubfox-it/dissect
1.1k11 days ago
flare-floss preview#10

flare-floss

GitHubmandiant/flare-floss
4.1k22 days ago
capa preview#11

capa

GitHubmandiant/capa
6.1k2 days ago
yara-x preview#12

yara-x

GitHubvirustotal/yara-x
1.2k1 day ago
NewestRelevanceMost popularRecently updated
775 results
ghidra preview

ghidra

GitHubnationalsecurityagency/ghidra

Ghidra is a software reverse engineering (SRE) framework
android-securityembedded-systems-securitystatic-analysis+17
71.1k2 days ago
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
static-analysisdynamic-analysis-sandboxingmemory-forensics+7
49.1k3 days ago
radare2 preview

radare2

GitHubradareorg/radare2

UNIX-like reverse engineering framework and command-line toolset
android-securityembedded-systems-securitystatic-analysis+16
24.5k3h 48m ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
static-analysismemory-forensicshash-analysis+10
54.4k1 month ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
disk-forensicsmemory-forensicsforensics+9
9.6k1 month ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
general-purpose-utilitiesmemory-forensicsnetwork-mapping+6
15.6k1 day ago
awesome-malware-analysis preview

awesome-malware-analysis

GitHubrshipp/awesome-malware-analysis

Defund the Police.
memory-forensicsvulnerability-analysisreverse-engineering+10
14.1k2 years ago
pwndbg preview

pwndbg

GitHubpwndbg/pwndbg

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
embedded-systems-securitystatic-analysismemory-forensics+12
10.8k1 day ago
angr preview

angr

GitHubangr/angr

A powerful and user-friendly binary analysis platform!
embedded-systems-securitystatic-analysisdynamic-analysis-sandboxing+12
9.0k10h 46m ago
dnSpy preview

dnSpy

GitHubdnspyex/dnspy

Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
static-analysisdynamic-analysis-sandboxingencryption-decryption-tools+10
10.9k3 days ago
objection preview

objection

GitHubsensepost/objection

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
android-securitypenetration-testing-frameworksdynamic-analysis-sandboxing+9
9.3k16 days ago
cheat-engine preview

cheat-engine

GitHubcheat-engine/cheat-engine

Cheat Engine. A development environment focused on modding
general-purpose-utilitiesmemory-forensicsexploitation+3
18.9k1 year ago
CAPEv2 preview

CAPEv2

GitHubkevoreilly/capev2

Malware Configuration And Payload Extraction
dynamic-analysis-sandboxingmemory-forensicsvulnerability-analysis+6
3.4k0 days ago
gef preview

gef

GitHubhugsy/gef

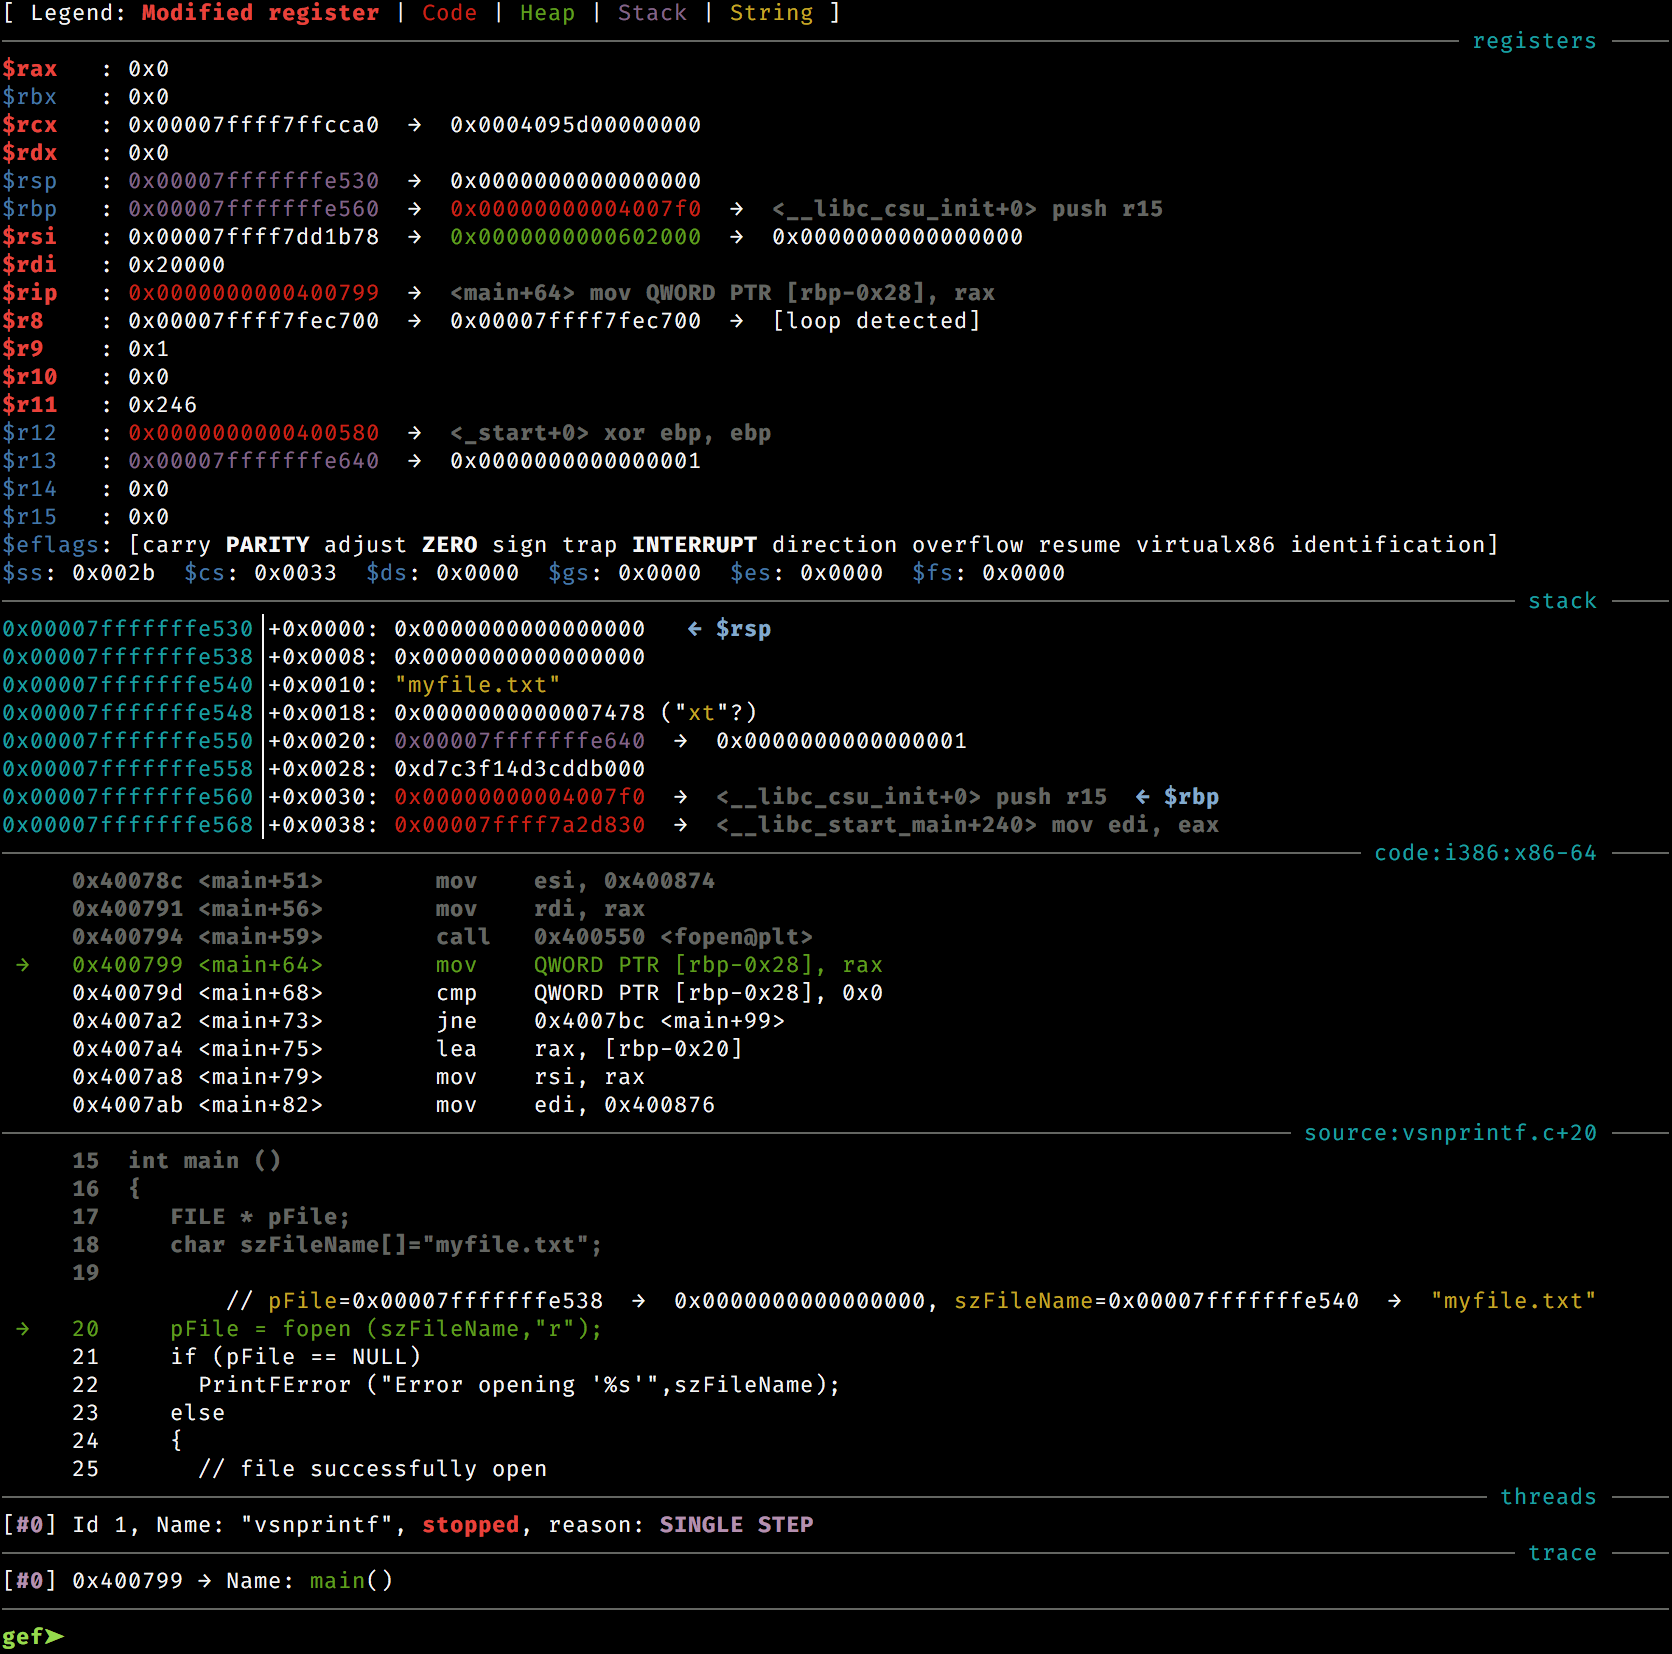
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
static-analysisdynamic-analysis-sandboxingmemory-forensics+10
8.3k1 day ago
capa preview

capa

GitHubmandiant/capa

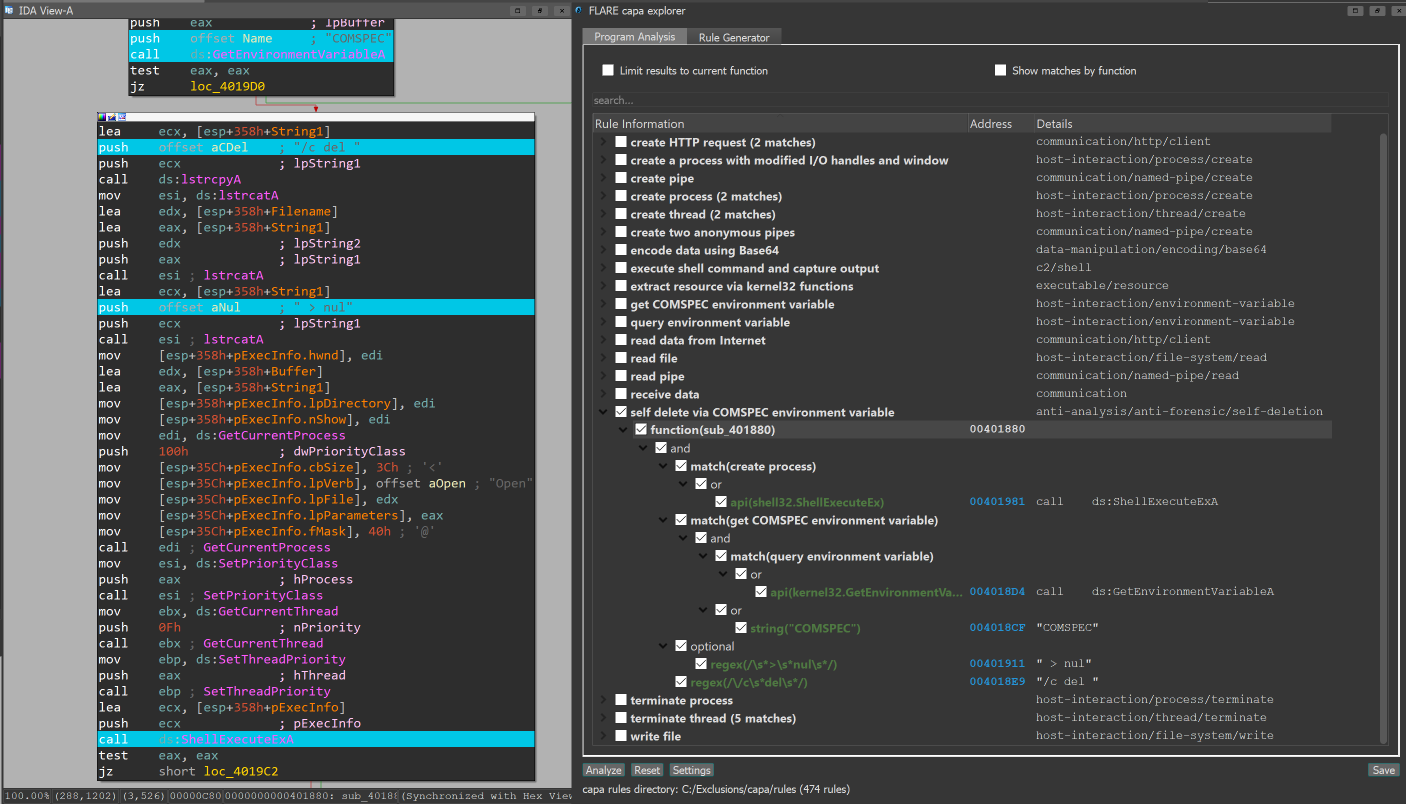
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ioc-managementstatic-analysisdynamic-analysis-sandboxing+10
6.1k2 days ago
flare-vm preview

flare-vm

GitHubmandiant/flare-vm

A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
static-analysisdynamic-analysis-sandboxingmemory-forensics+10
8.9k1 month ago
digital-forensics-lab preview

digital-forensics-lab

GitHubfrankwxu/digital-forensics-lab

Free hands-on digital forensics labs for students and faculty
disk-forensicspassword-crackingmemory-forensics+9
2.9k7 days ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library
privilege-escalationdynamic-analysis-sandboxingmemory-forensics+9
5.5k4 years ago
Previous12…44Next
Memory Forensics | Kitploit