Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Shuffle — Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and hybrid resource sharing for SOC teams. | Kitploit
Tools/GitHubGitHub/shuffle/shuffle
Defensive ToolsIndicator of Compromise (IOC) ManagementScripting & AutomationUtilities & FrameworksThreat IntelligenceIncident ResponseTop in Incident Response #17
GitHubshuffle/shuffle

Shuffle

Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and hybrid resource sharing for SOC teams.

2.5k442981 day agoReviewed by Kitploit
Share
View RepositoryWebsite

Shuffle Logo

Shuffle Automation

Deploy On


Shuffle is an open source automation platform, built for and by the security professionals. Security operations is complex, but it doesn't have to be. Built to work well with MSSP's and other service providers in mind.

Key Features — Community & Support — Get training - Documentation — Getting Started — Development - Set up a demo call

Follow us on Twitter at @shuffleio.
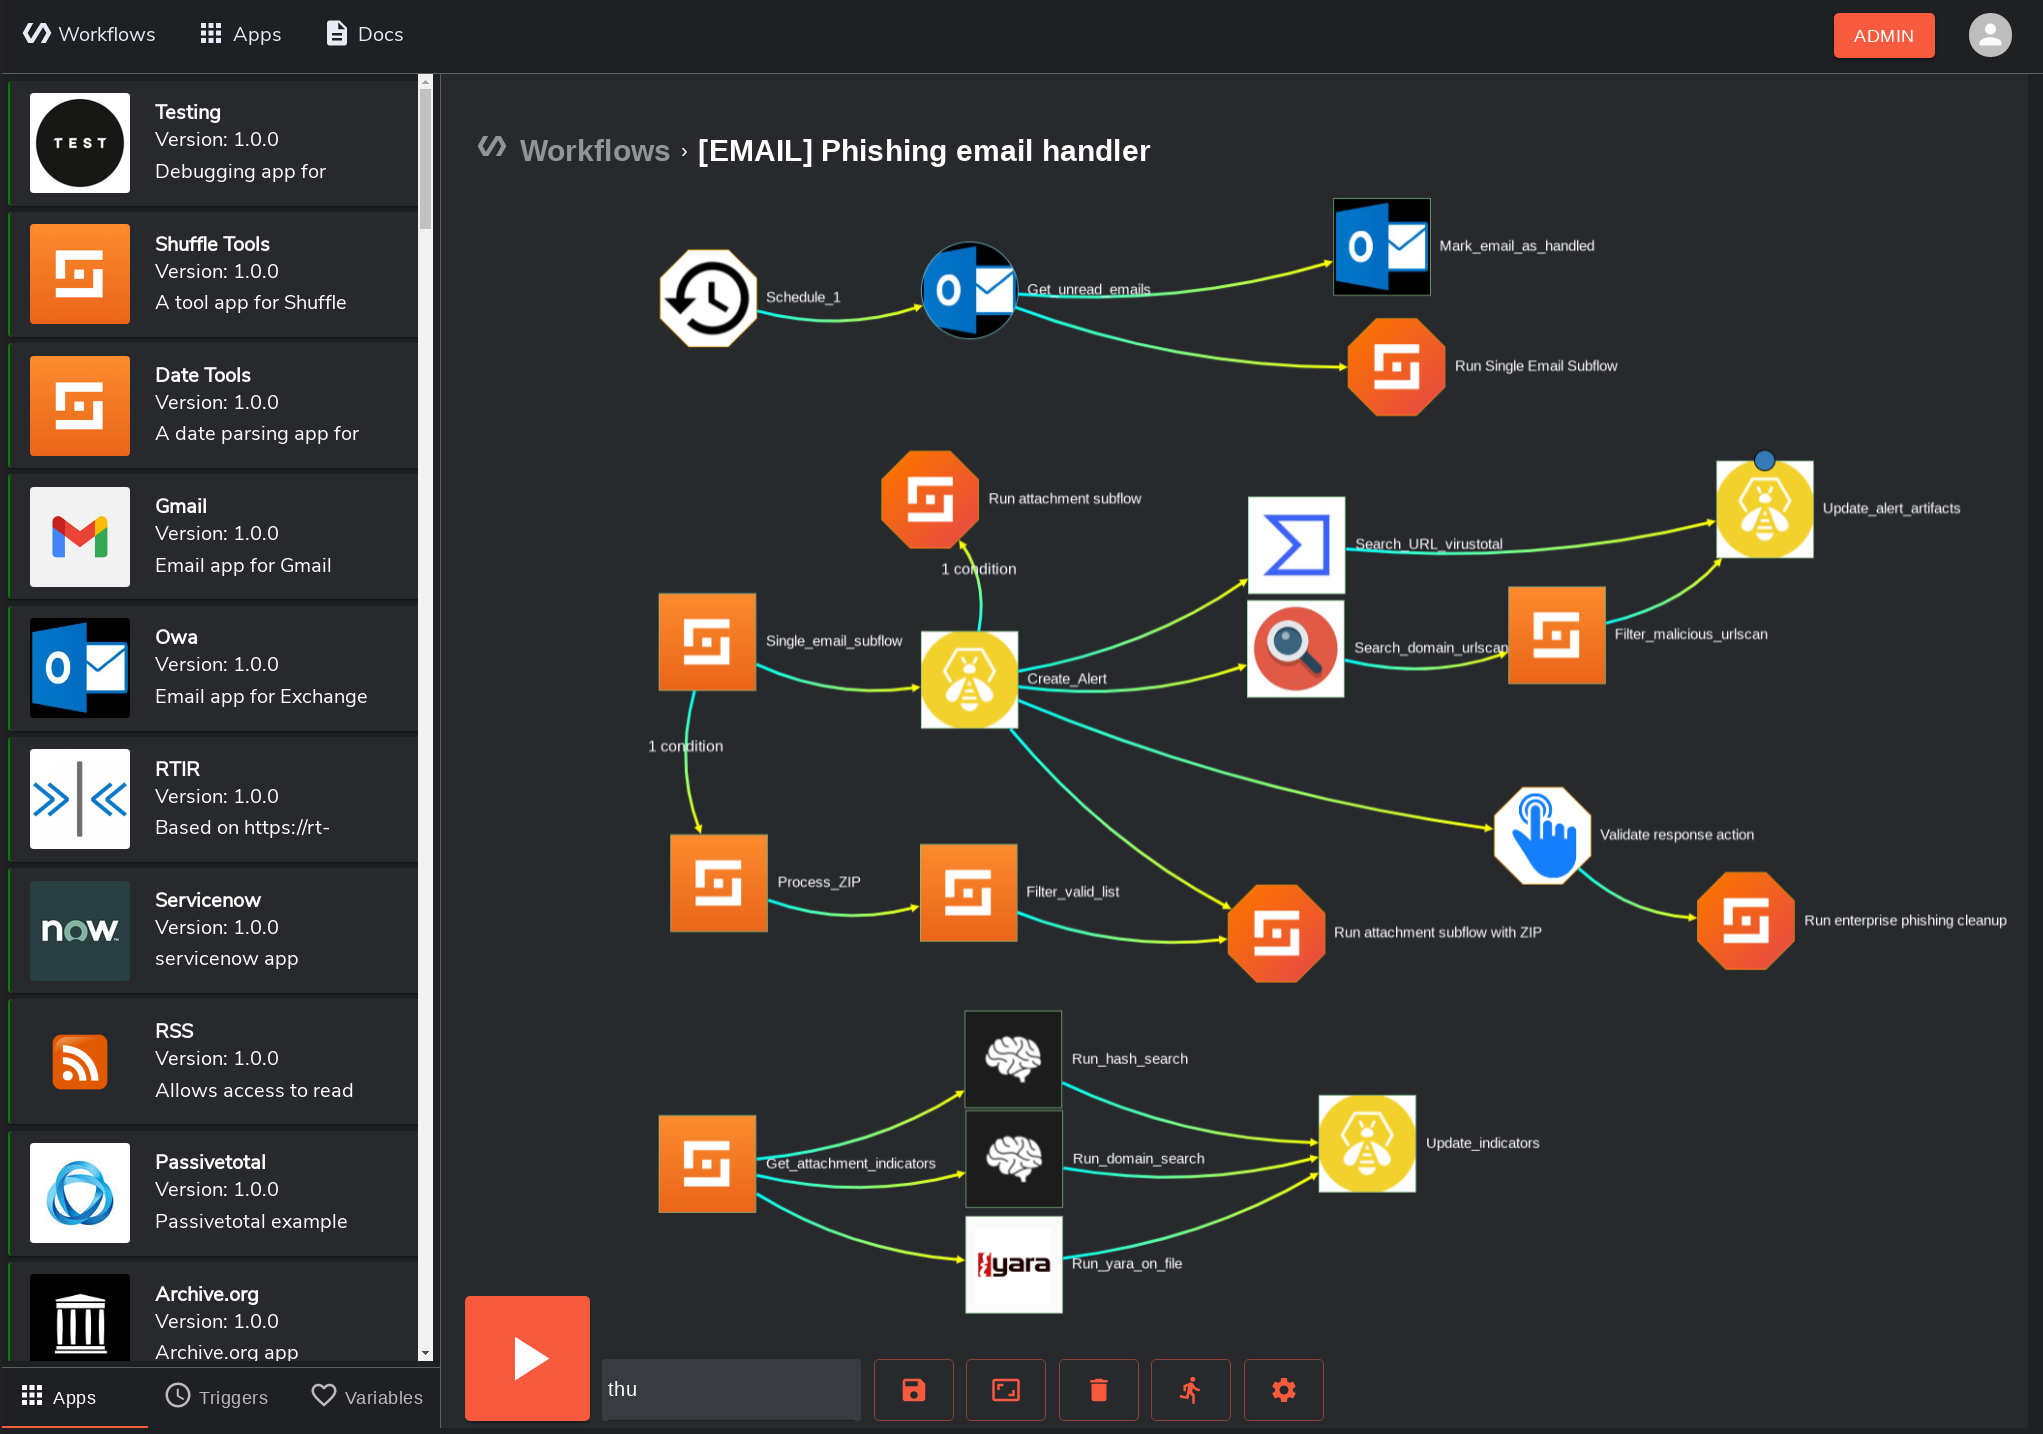
Example Shuffle webhook integration

Try it

  • Self-hosted: Check out the installation guide
  • Local development: see the local development quick start
  • Cloud: Register at https://shuffler.io/register and get cooking

Please consider sponsoring the project if you want to see more rapid development.

Local development

The local development quick start in the install guide covers prerequisites (including the Windows/WSL2 setup), starting the backend and database with Docker, running the frontend, creating your admin account, ports and troubleshooting.

docker compose up -d opensearch backend   # backend + database
cd frontend && npm install && npm start     # frontend on http://localhost:3000

Support

  • Discord
  • Twitter
  • Email
  • Open issue
  • Shuffler.io

Blogposts

  • 1. Introducing Shuffle
  • 2. Getting started with Shuffle
  • 3. Integrating Shuffle with Virustotal and TheHive
  • 4. Real-time executions with TheHive, Cortex and MISP

Documentation

Documentation can be found on https://shuffler.io/docs and is written here: https://github.com/shuffle/shuffle-docs.

Related repositories

  • OpenAPI apps: https://github.com/shuffle/security-openapis
  • Documentation: https://github.com/shuffle/shuffle-docs
  • Workflows: https://github.com/shuffle/shuffle-workflows
  • Python apps: https://github.com/shuffle/shuffle-apps

Features

  • Simple, feature rich workflow editor
  • App creator using OpenAPI
  • Premade apps for your security tools
  • Organization and sub-organization control
  • Hybrid resource sharing with shuffler.io (optional)

Website

https://shuffler.io

Contributing

We want to make the world of cybersecurity more accessible and need all the help we can get. Send an email to [email protected] and we'll make sure to give you any training you may need.

These are the main areas to contribute in:

  • Frontend (ReactJS)
  • Backend (Golang)
  • App Creation (Python & GUI w/OpenAPI)
  • Documentation (Markdown)
  • Workflow creation (GUI & Conceptualizing)
  • Content Creation (Blogs, videos etc)

Contributing guidelines are outlined here.
Contributors

ICPL logo

Shuffle

App magicians

License

All modular information related to Shuffle will be under MIT (anyone can use it for whatever purpose), with Shuffle itself using AGPLv3.

Workflows: MIT Documentation: MIT Shuffle backend: AGPLv3 Apps, specification and App SDK: MIT
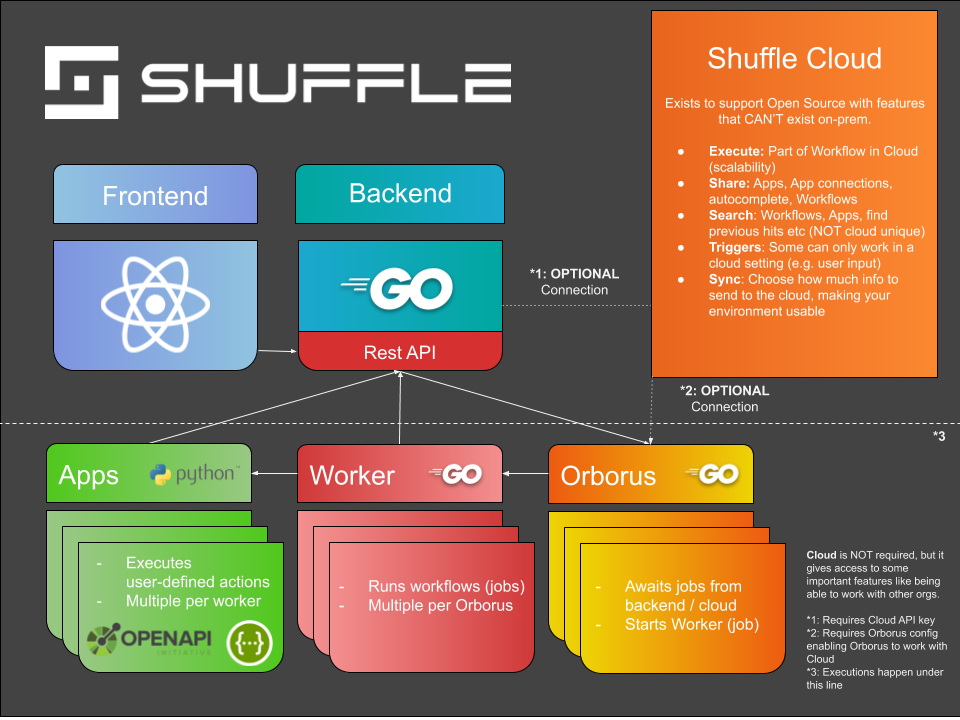
Architecture

Shuffle Architecture

Security Contributors: Hall of Fame

Pushpraj - Reported several issues between July and August 2024

Repository overview

Below is the folder structure with a short explanation

├── README.md				# What you're reading right now
├── backend					# Contains backend related code.
│   ├── go-app 			# The backend golang webserver
│   └── app_sdk			# The SDK used for apps
├── frontend				# Contains frontend code. ReactJS (Vite), Material UI and cytoscape
├── functions				# Has execution and extension resources, such as the Wazuh integration
│   ├── onprem				# Code for onprem solutions
│   │   ├── Orborus 	# Distributes execution locations
│   │   ├── Worker		# Runs a workflow
├── shuffle-apps			# Local app folder (mounted into the backend container)
├── shuffle-database		# OpenSearch data (created/used by docker compose)
├── .env					# Configuration used by docker-compose.yml
└── docker-compose.yml 	# Used for deployments

Get in touch, send a mail to [email protected] or poke me on twitter @frikkylikeme

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →