
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring, quarantine, and multi-channel alerting

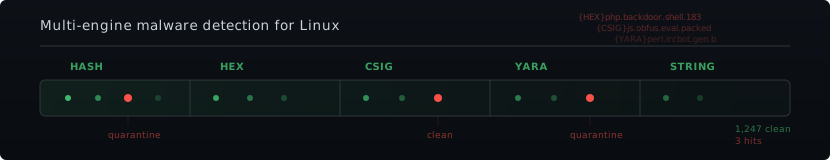


Malware scanner for Linux — multi-stage threat detection (MD5, SHA-256, HEX, YARA, statistical analysis), ClamAV integration, real-time inotify monitoring, quarantine/clean/restore operations, and multi-channel alerting (email, Slack, Telegram, Discord).
(C) 2002-2026, R-fx Networks <[email protected]>
(C) 2026, Ryan MacDonald <[email protected]>
Licensed under GNU GPL v2
43x faster native scan engine — the native scanning pipeline has been completely rewritten with batch parallel processing. Real-world benchmark on ~10,000 files:
| Version | Runtime | Files | Hits |
|---|---|---|---|
| v1.6.6 | 1,217s | 9,931 | 35 |
| v2.0.1 | 28s | 9,931 | 35 |
MD5 and HEX signature matching now use batch grep with Aho-Corasick parallel workers,
eliminating per-file pattern compilation overhead and ~500,000 subprocess forks per scan.
Configure parallel worker count with scan_workers (default: auto).
Other highlights: scan lifecycle management (--kill, --pause, --stop/--continue,
-L), SHA-256 hash scanning with CPU hardware auto-detection (scan_hashtype),
native YARA scanning (scan_yara=1), Discord webhook alerting, Slack/Telegram alerting
fixes, ClamAV hex wildcard support in the native engine, and 200+ bug fixes across the
codebase.
See CHANGELOG for full details.
# Install to /usr/local/maldetect
./install.sh

# Scan all files under a path
maldet -a /home/?/public_html

# Scan files modified in the last 2 days
maldet -r /home/?/public_html 2

# Enable YARA scanning at runtime
maldet -co scan_yara=1 -a /home/?/public_html

# Quarantine all hits from a scan
maldet -q SCANID

# Start real-time inotify monitoring
maldet -m users

# Update signatures
maldet -u
LMD's architecture, detection stages, and supported platforms.
Linux Malware Detect (LMD) is a malware scanner for Linux released under the GNU GPLv2 license, designed around the threats faced in shared hosted environments. It uses threat data from network edge intrusion detection systems to extract malware that is actively being used in attacks and generates signatures for detection. In addition, threat data is derived from user submissions with the LMD checkout feature and from malware community resources.
LMD focuses on the malware classes that traditional AV products frequently miss: PHP shells, JavaScript injectors, base64-encoded backdoors, IRC bots, and other web-application-layer threats that target shared hosting user accounts rather than operating system internals.
Detection Stages
Scanning & Monitoring
inspectFile hookQuarantine & Response
Alerting & Reporting
alert/custom.d/ overridesInfrastructure
LMD runs on any Linux distribution with bash and standard GNU utilities. Tested platforms:
| Platform | Init System | Package Config Path |
|---|---|---|
| RHEL / Rocky / AlmaLinux 8, 9, 10 | systemd | /etc/sysconfig/maldet |
| CentOS 6, 7 | SysV / systemd | /etc/sysconfig/maldet |
| Debian 10, 11, 12 | systemd | /etc/default/maldet |
| Ubuntu 20.04, 22.04, 24.04 | systemd | /etc/default/maldet |
| Gentoo | OpenRC | — |
| Slackware | SysV | — |
| FreeBSD | — | — (partial; no inotify) |
Installing, upgrading, and removing LMD from a system.
The included install.sh script handles all installation tasks. Previous installations are automatically backed up.
./install.sh
