El script hace una revisión de tu Linux frente a esa vulnerabilidad, sin tocar nada por defecto: osea mira tu kernel — lee tu versión real de Linux (uname -r) y la compara con la lista de versiones donde ya está arreglado el fallo.

Check whether your Linux machine is vulnerable to CVE-2026-98432 (use-after-free in the kernel's IPv4/TCP).
by Prf@fEsOr X
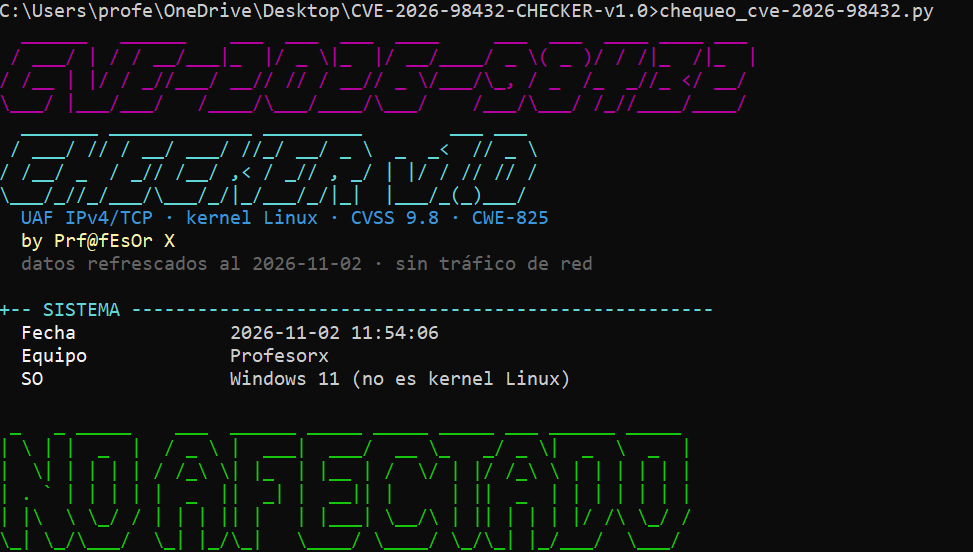
pip install colorama pyfiglet
# Check THIS machine
python3 CVE_2026_98432_Checker_1h.py

# Analyze the kernel version of ANOTHER machine (its uname -r)
python3 CVE_2026_98432_Checker_1h.py --kernel 5.15.0-203-generic

# No colors (for logs or screenshots)
python3 CVE_2026_98432_Checker_1h.py --no-color

# View the status of temporary mitigations (without changing anything)
python3 CVE_2026_98432_Checker_1h.py --endurecer

# APPLY the temporary mitigations (requires root)
sudo CVE_2026_98432_Checker_1h.py --endurecer --aplicar
| Flag | What it does |
|---|---|
| (none) | Check of this machine (kernel + distro + exposure) |
--kernel X.Y.Z[-something] | Analyzes that kernel version instead of the local one |
--endurecer | Verifies the temporary mitigations (read-only mode) |
--endurecer --aplicar | Applies the mitigations: tcp_migrate_req=0, MPTCP off and Red Hat nftables rule |
--no-color | Output without colors |
--version | Script version |
| Code | Meaning |
|---|---|
0 | Not affected |
1 | VULNERABLE |
2 | Requires review |
3 | Missing dependencies (pip install colorama pyfiglet) |
4 | --aplicar run without root |
Example for automation:
python3 CVE_2026_98432_Checker_1h.py --no-color
if [ $? -eq 1 ]; then echo "ALERT: vulnerable kernel"; fi
human.py: the same checker without comments and with prof_x_* variables; same functionality and same exit codes.--endurecer --aplicar are temporary: the kernel patch is the only complete fix. After updating, reboot and run the script again.python3 chequeo_cve-2026-98432.py -h.by Prf@fEsOr X · CVE-2026-98432 CHECKER v1.0








